
BRC4-BOF-Artillery
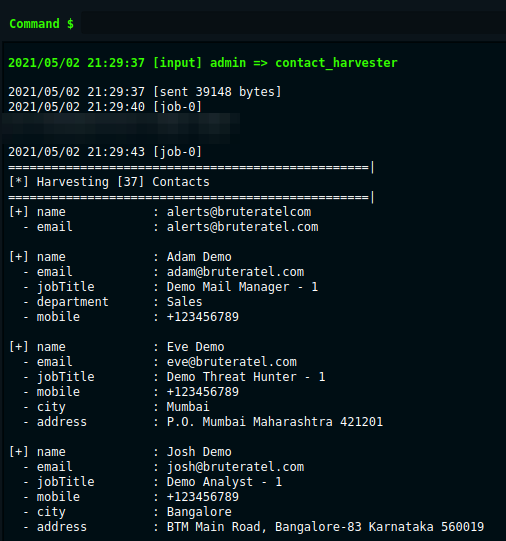
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…

A tool for simplifying the process of researching IOCs.

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.

The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis

Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…

A small utility to deal with malware embedded hashes.

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…


Browser-based Merkle tree demo — build a tree, generate inclusion proofs, recompute the root hash by hash, and replay the RFC 6962 second-preimage…

RSA attack tool (mainly for ctf) - retrieve private key from weak public key and/or uncipher data

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

YARA signature and IOC database for my scanners and tools

A self-contained cryptographic library for Python

A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…

A tool for automating cracking methodologies through Hashcat from the TrustedSec team.