
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
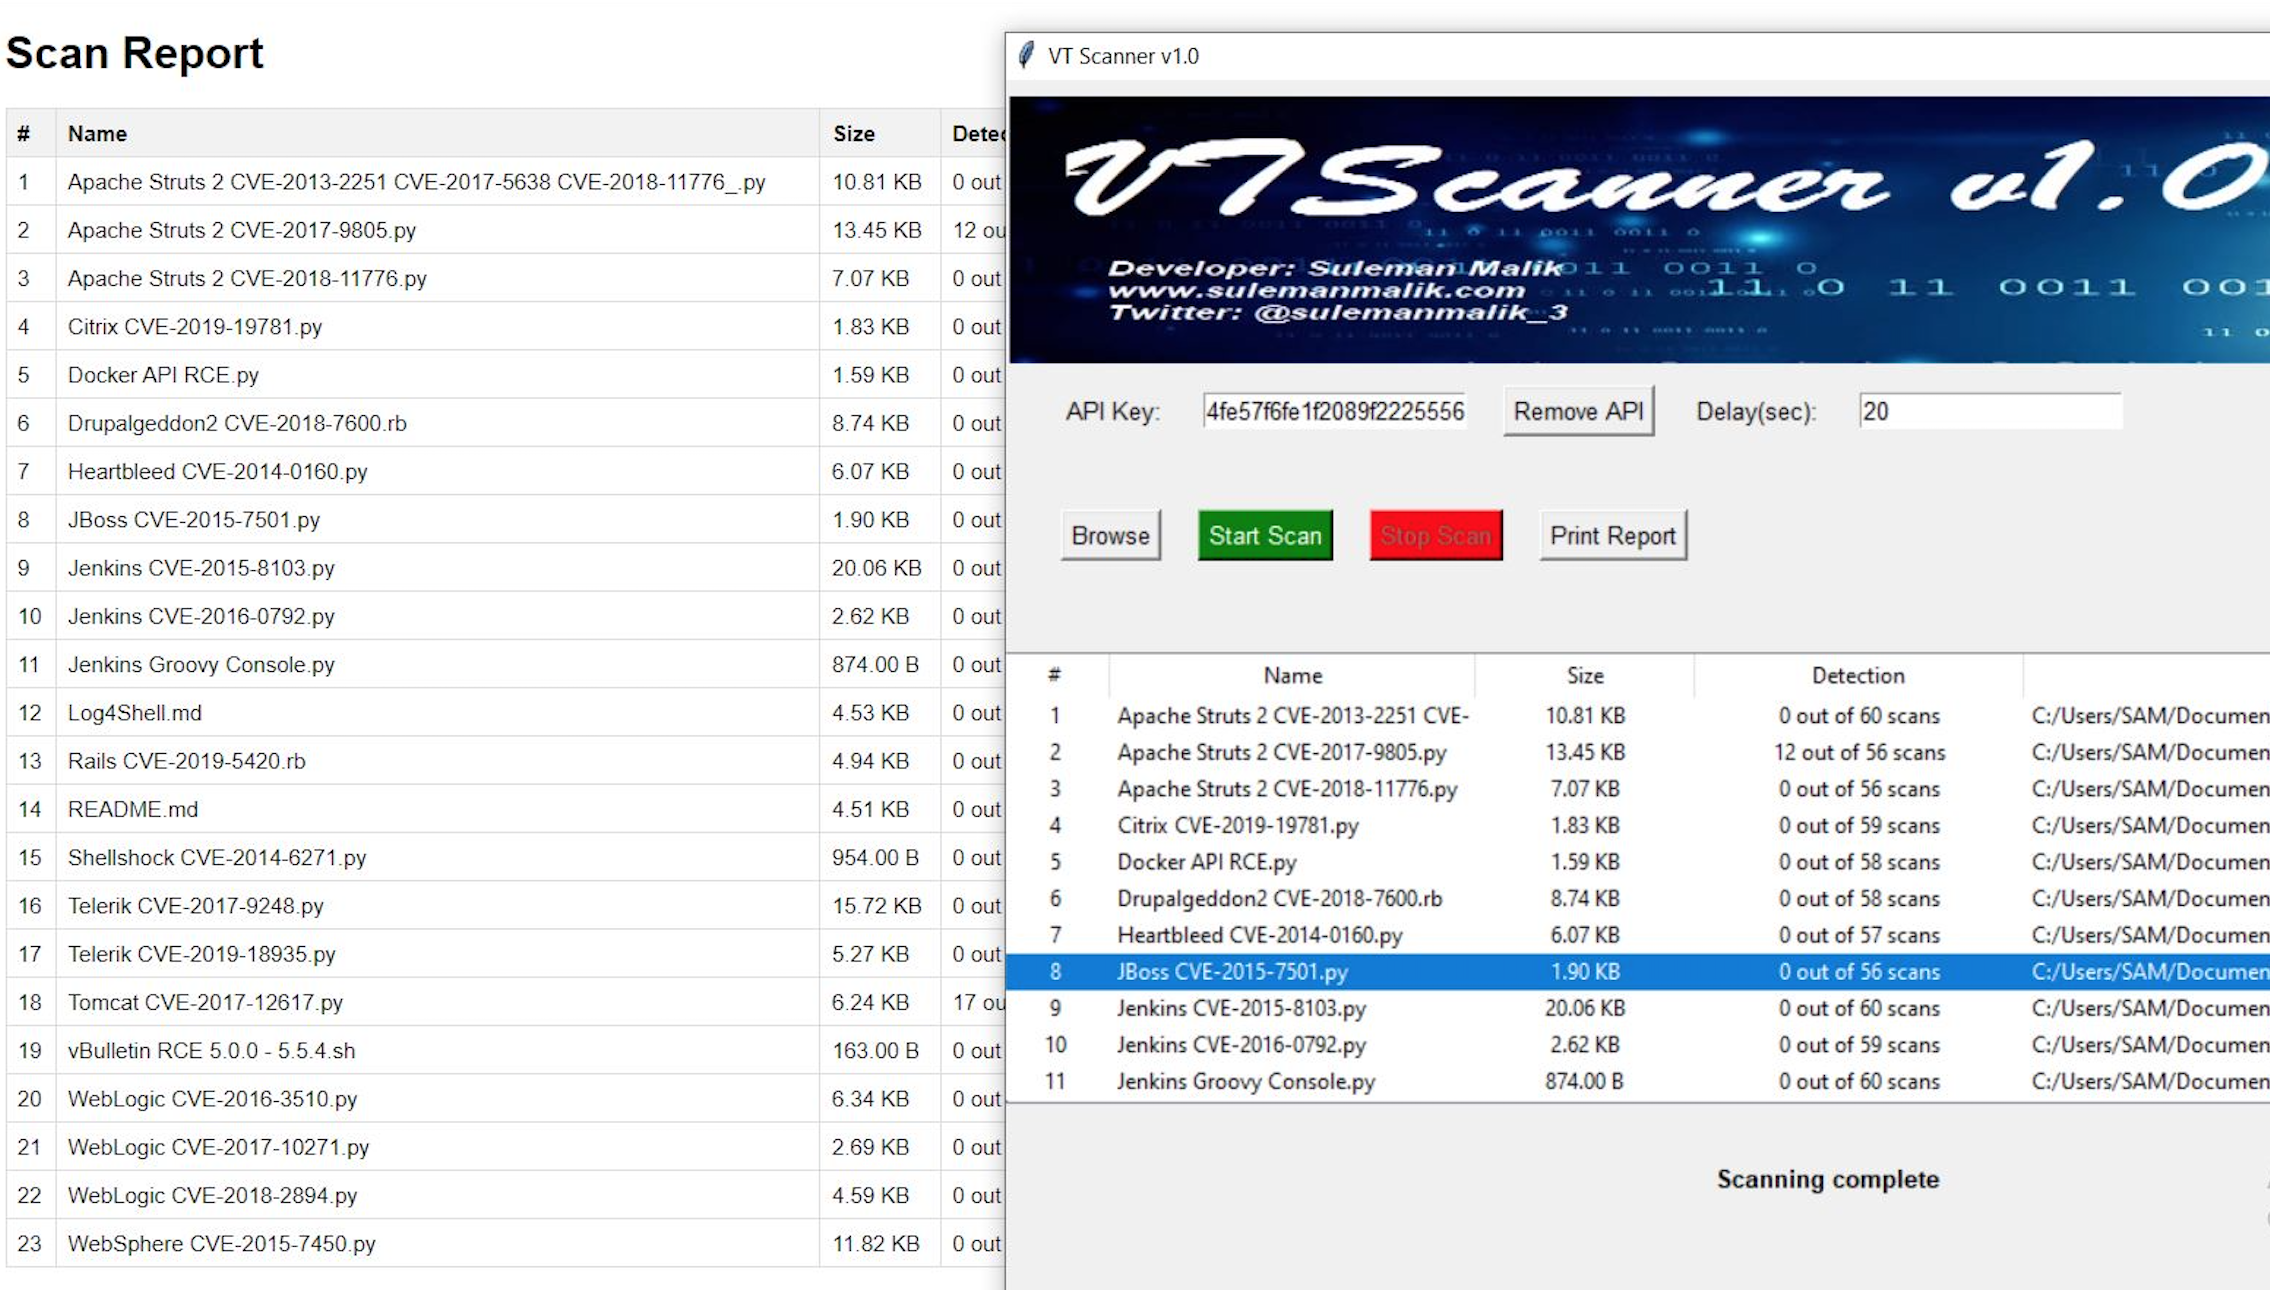
VTScanner preview

VTScanner

GitHubsamhaxr/vtscanner

A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
hash-analysisinformation-gatheringmalware-analysis+1
112
3 years ago
fileintel preview

fileintel

GitHubkeithjjones/fileintel

A modular Python application to pull intelligence about malicious files
hash-analysisinformation-gatheringmalware-analysis+2
1235 years ago
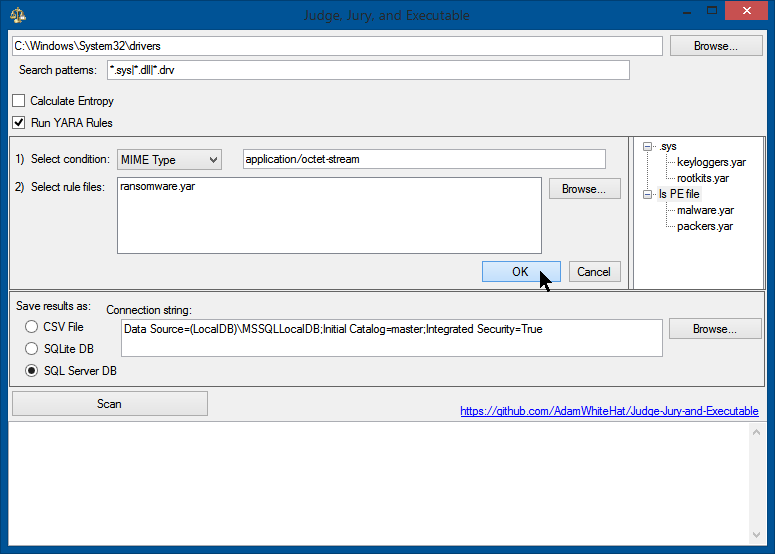
Judge-Jury-and-Executable preview

Judge-Jury-and-Executable

GitHubadamwhitehat/judge-jury-and-executable

A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

database-securitydigital-forensicsdisk-forensics+8
855 months ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
2.9k1 month ago
shaha preview

shaha

GitHuboritwoen/shaha

Hash database builder and reverse lookup tool — SHA256, RIPEMD160, Keccak256, BLAKE3 and more
cryptographyctfdata-recovery+5
56 months ago
ForensiX preview

ForensiX

GitHubtheevidencehunter/forensix

Digital Forensics Intelligence Framework
digital-forensicsdisk-forensicsforensics+4
5 months ago
FileWatchTower preview

FileWatchTower

GitHubiomoath/filewatchtower

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
digital-forensicsforensicshash-analysis+4
292 years ago
naive-hashcat preview

naive-hashcat

GitHubbrannondorsey/naive-hashcat

Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
hash-analysispassword-attackspassword-cracking
1.4k4 years ago
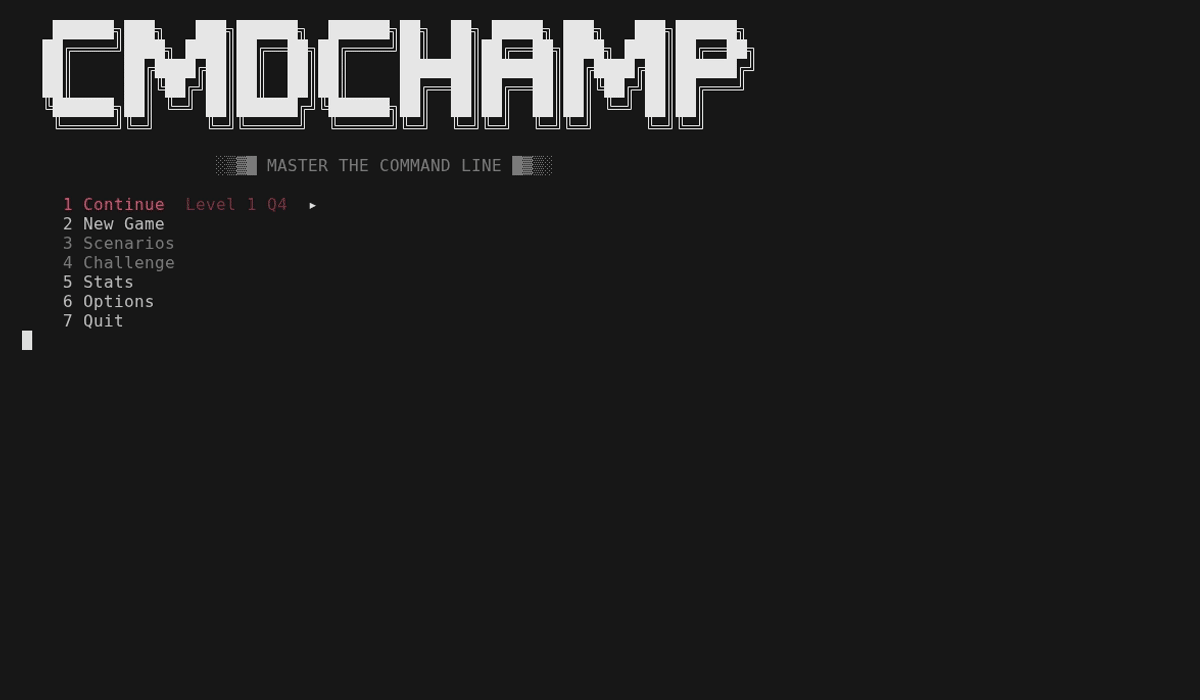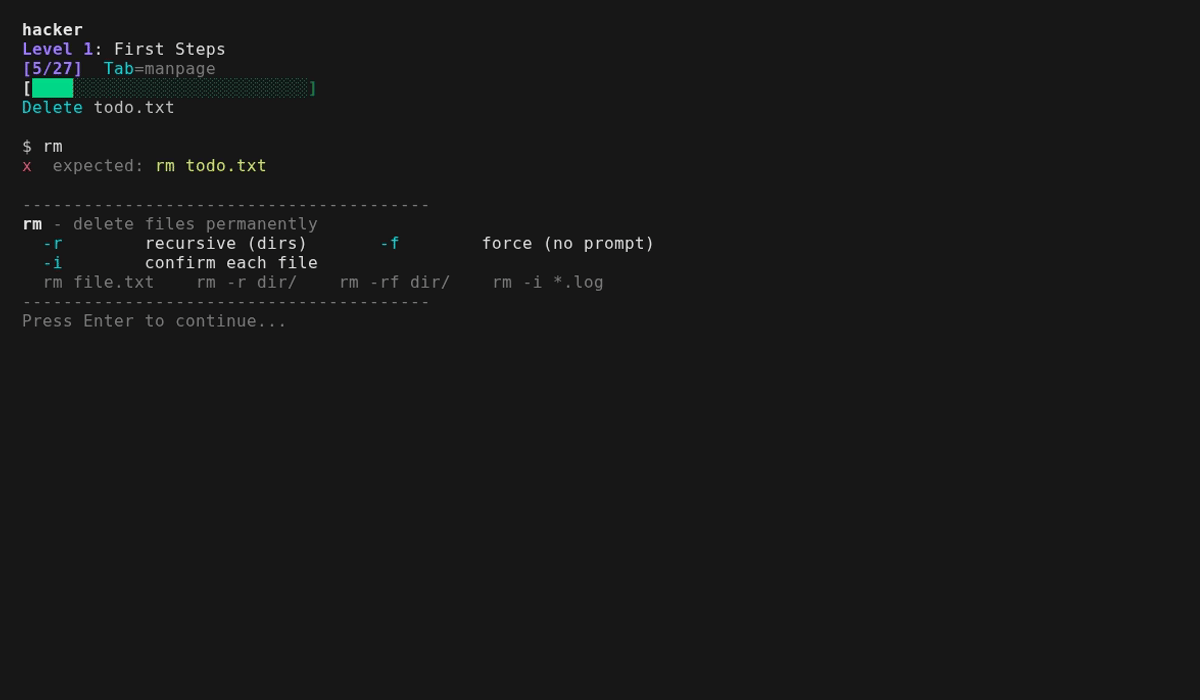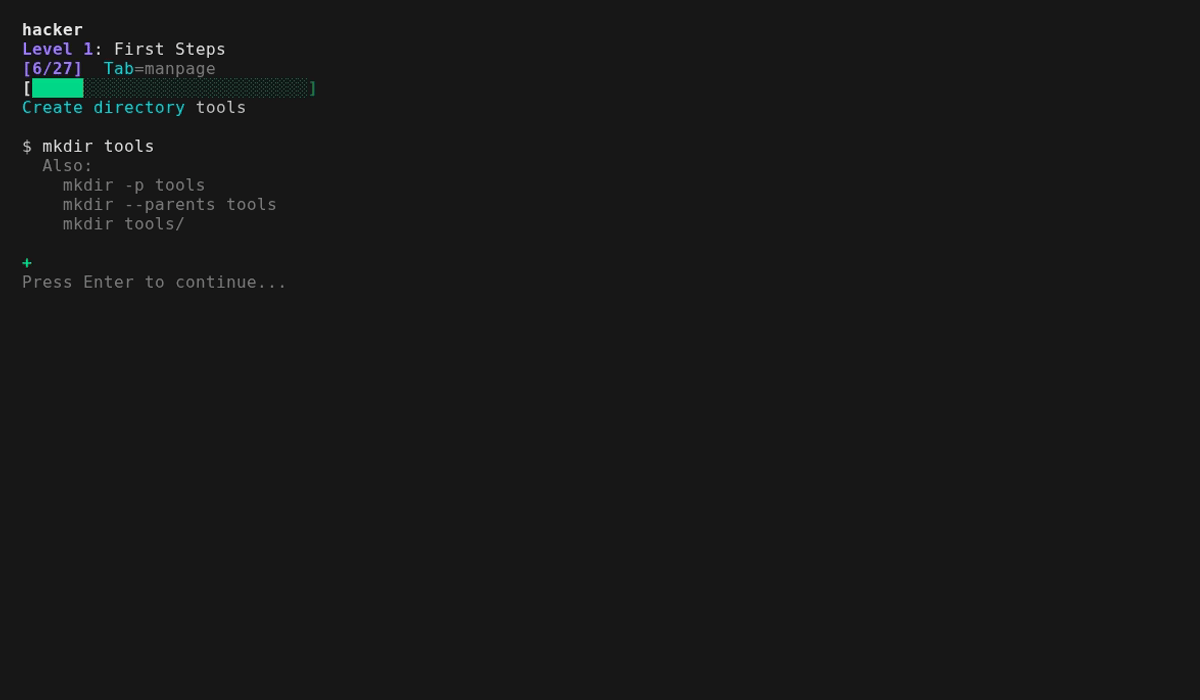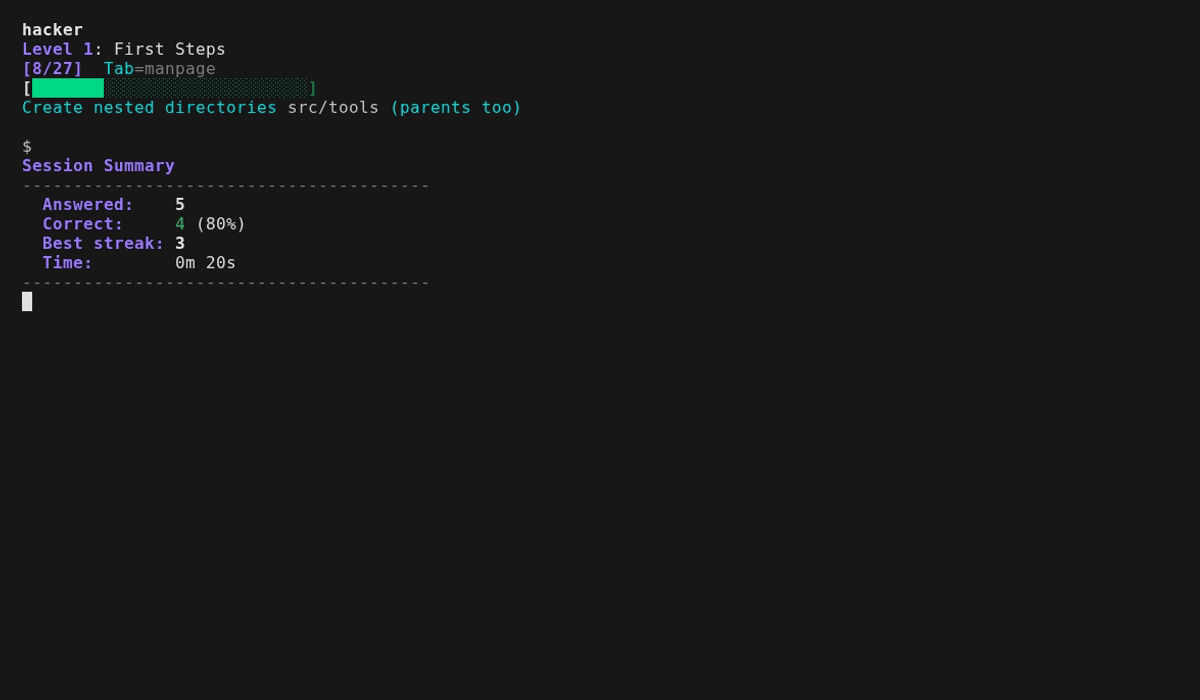
cmdchamp preview

cmdchamp

GitHubmellen9999/cmdchamp

bash CLI trainer — 30 levels from ls to privilege escalation

ctfeducationforensics+8
1222 days ago
Windows-SignedBinary preview

Windows-SignedBinary

GitHubmr-un1k0d3r/windows-signedbinary

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
adversarial-attackbinary-analysishash-analysis+4
2617 years ago
ioccheck preview
Archived

ioccheck

GitHubranguli/ioccheck

A tool for simplifying the process of researching IOCs.
defensive-toolshash-analysisinformation-gathering+3
254 years ago
vt-py-scanner preview

vt-py-scanner

GitHubneorai/vt-py-scanner

Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
forensicshash-analysisinformation-gathering+3
59 months ago
hashdeep preview

hashdeep

GitHubjessek/hashdeep

Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
data-recoverydigital-forensicsforensics+1
7889 years ago
diario-commandline-tools preview

diario-commandline-tools

GitHubelevenpaths/diario-commandline-tools

CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…
api-securityhash-analysisinformation-gathering+3
46 years ago
sleuthkit preview

sleuthkit

GitHubsleuthkit/sleuthkit

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

data-recoverydigital-forensicsdisk-forensics+3
3.1k7h 28m ago
Loki preview

Loki

GitHubneo23x0/loki

IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
anomaly-detectiondigital-forensicsdisk-forensics+11
3.8k8 months ago
hashr preview

hashr

GitHubgoogle/hashr

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…

digital-forensicsdisk-forensicsforensics+2
1316 months ago
binwally preview

binwally

GitHubbmaia/binwally

Binary and Directory tree comparison tool using Fuzzy Hashing

binary-analysisdata-recoverydigital-forensics+3
8411 years ago
Previous12Next