
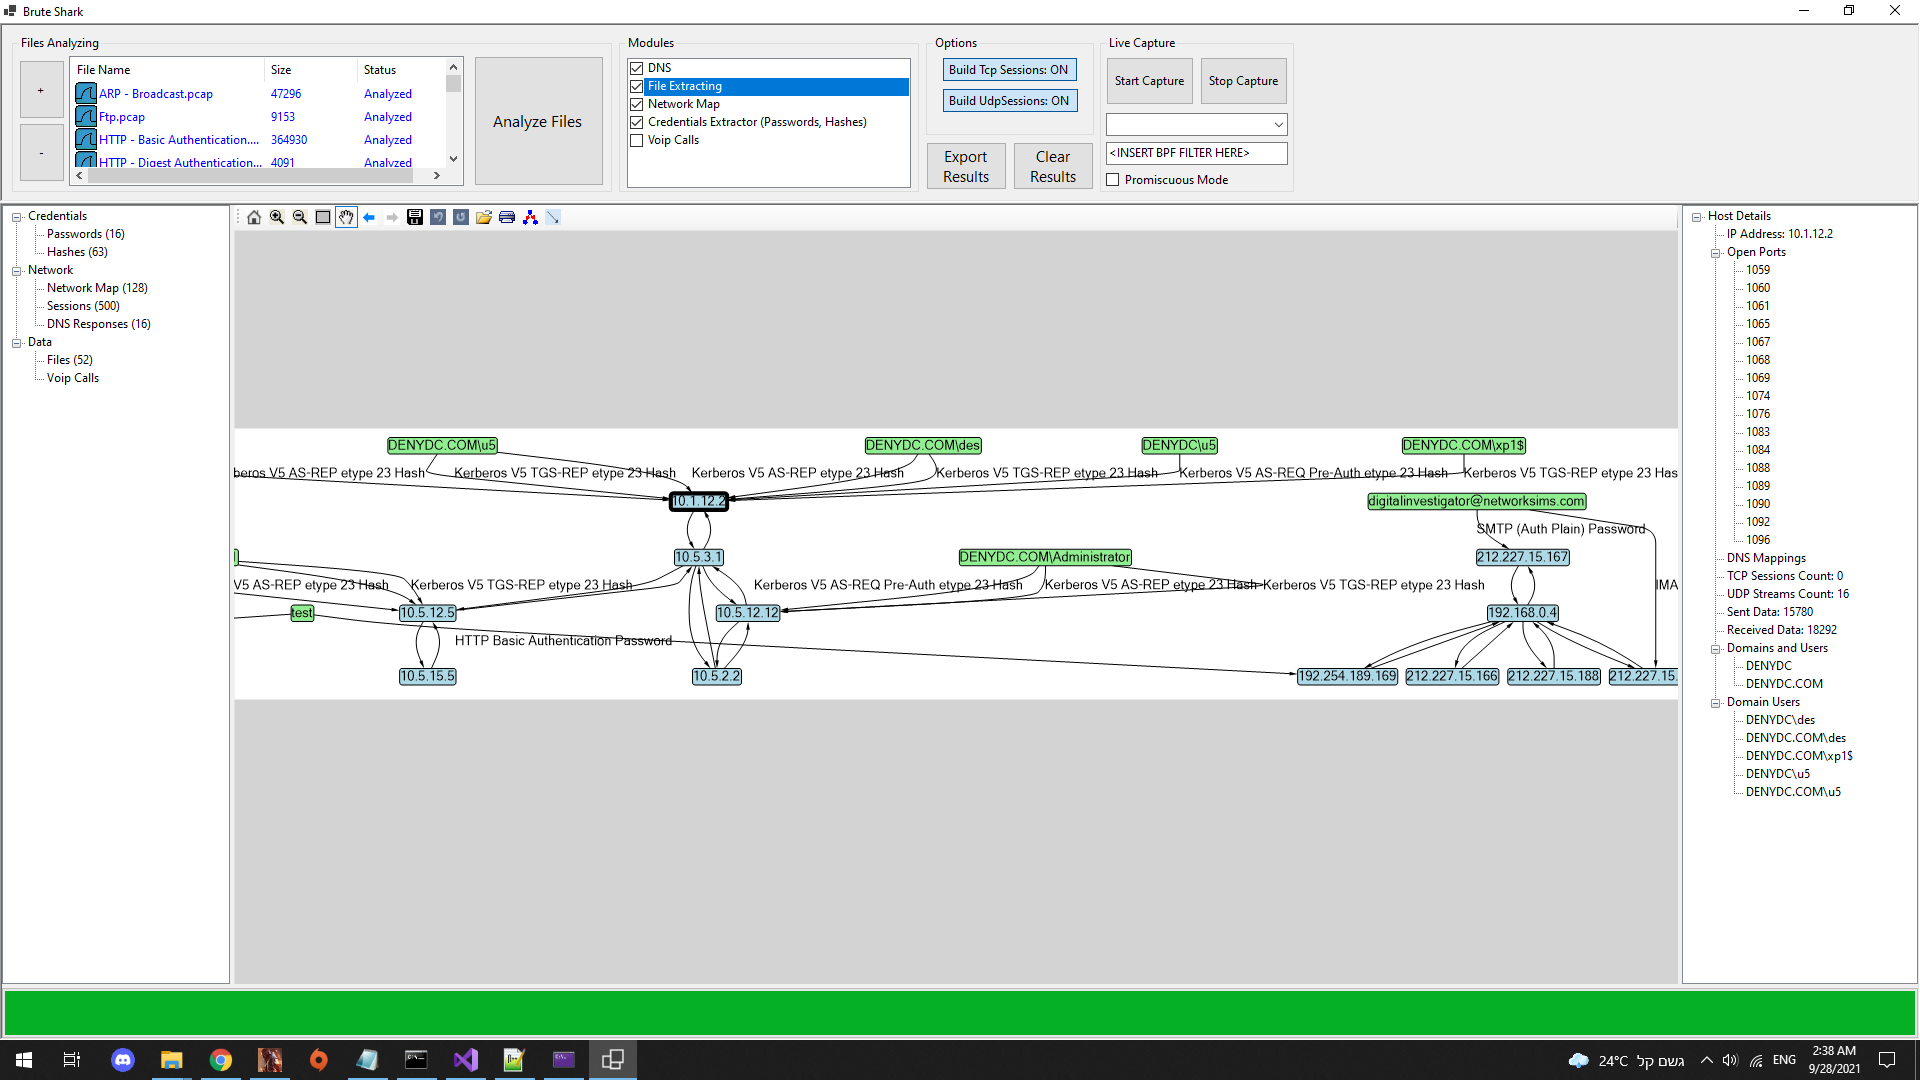

 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
 theevidencehunter/forensix
Digital Forensics Intelligence Framework
 gchq/cyberchef
The Cyber Swiss Army Knife - a web app for encryption, encoding, compression and data analysis
 rsactftool/rsactftool
RSA attack tool (mainly for ctf) - retrieve private key from weak public key and/or uncipher data
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 legrandin/pycryptodome
A self-contained cryptographic library for Python
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 trustedsec/hate_crack
A tool for automating cracking methodologies through Hashcat from the TrustedSec team.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
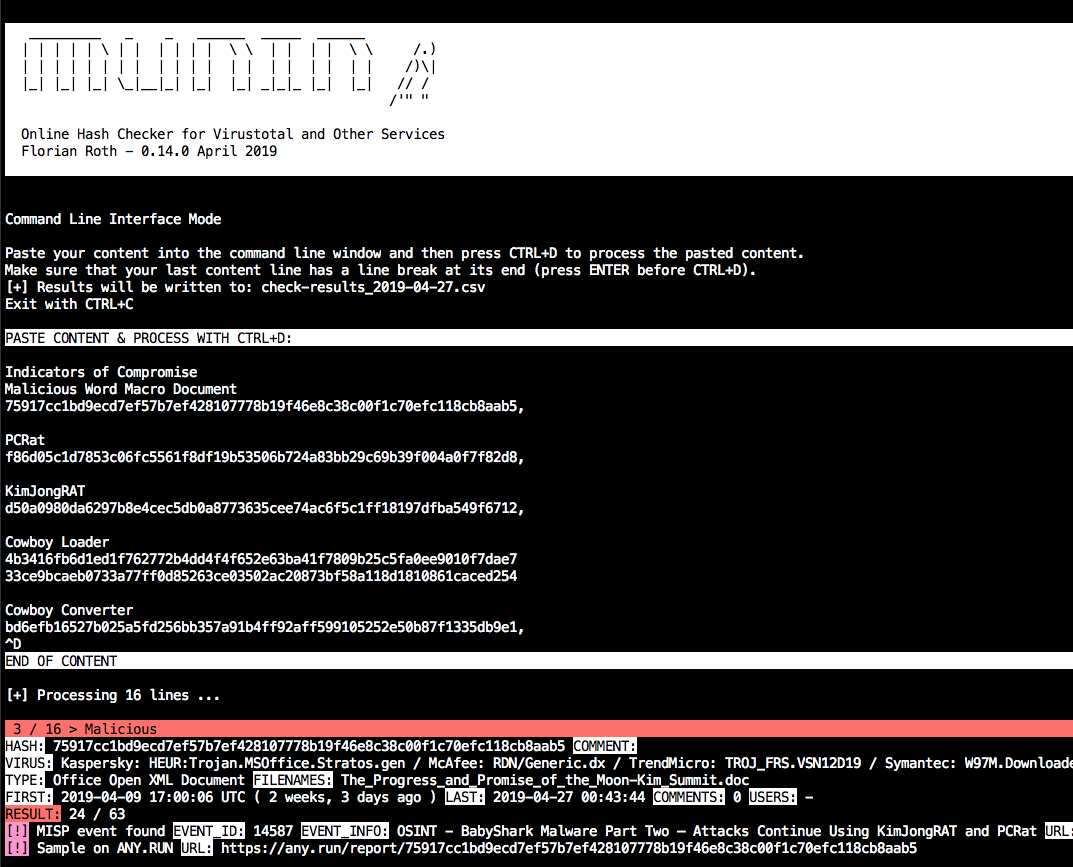 neo23x0/munin
Online hash checker for Virustotal and other services
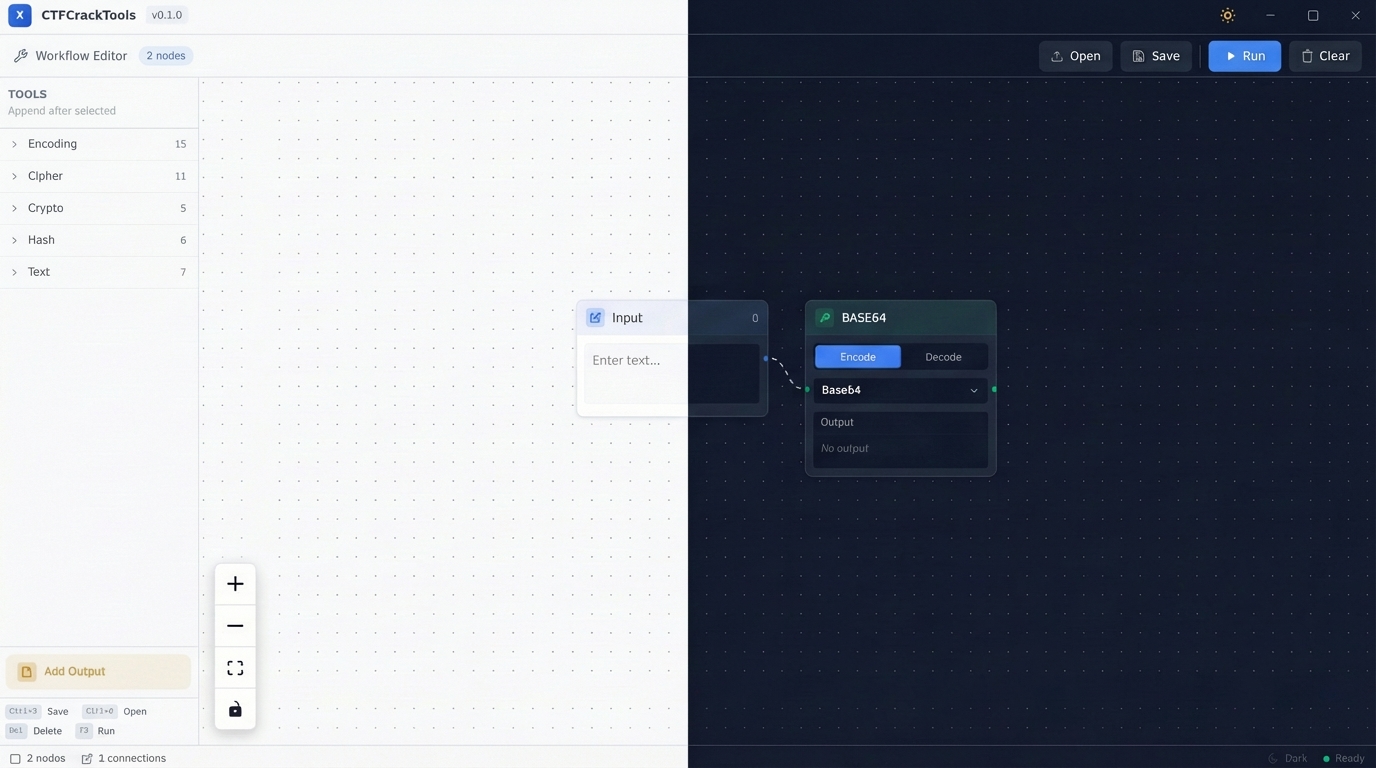 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…