sleuthkit
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
data-recoverydigital-forensicsdisk-forensics+3
3.2k
sleuthkit/sleuthkitForensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 blake3-team/blake3
Fast cryptographic hash function with PRF, MAC, KDF, and XOF modes. Supports verified streaming, incremental updates, and parallelized hashing via…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 neo23x0/signature-base
YARA signature and IOC database for my scanners and tools
 legrandin/pycryptodome
A self-contained cryptographic library for Python
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 rustcrypto/hashes
Collection of cryptographic hash functions written in pure Rust
 hashcat/hashcat-utils
Small utilities that are useful in advanced password cracking
 lanjelot/patator
Patator is a multi-purpose brute-forcer, with a modular design and a flexible usage.
 neo23x0/loki
IOC and YARA-based scanner for detecting indicators of compromise via file name regex, YARA signatures, hash matching, and C2 back-connect checks on…
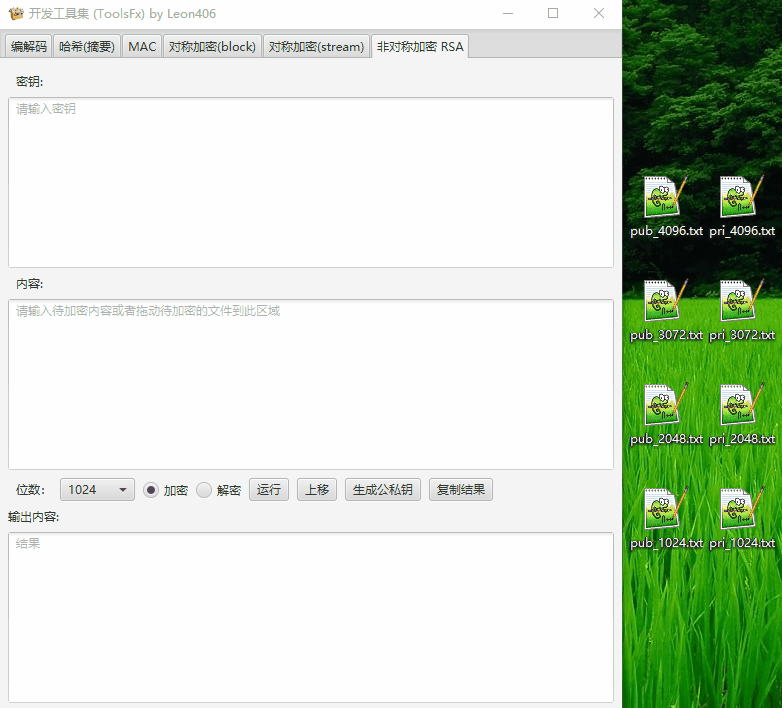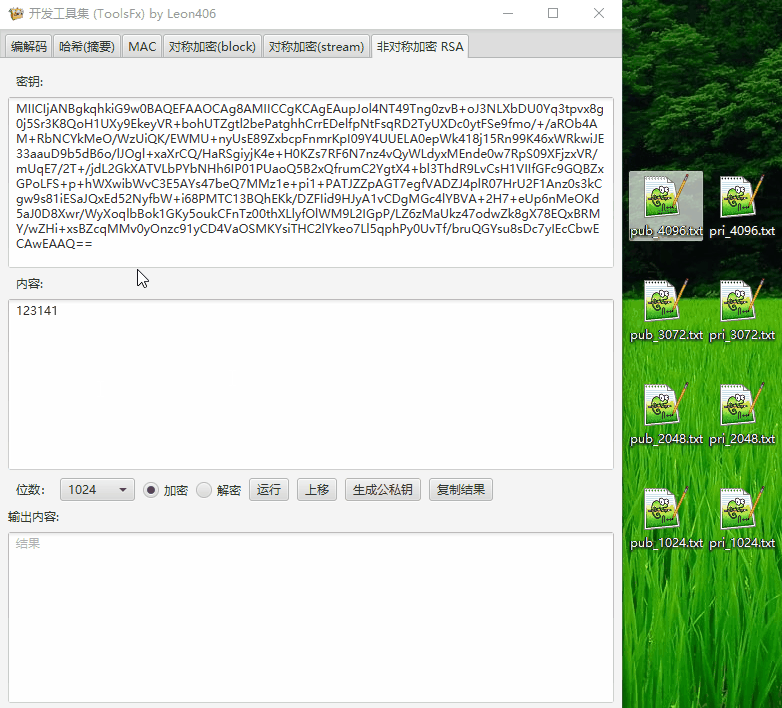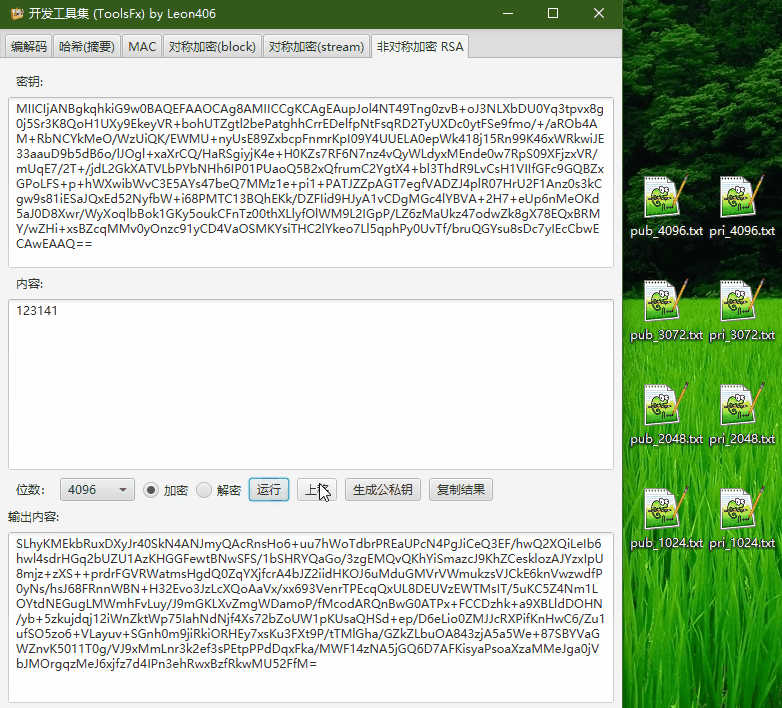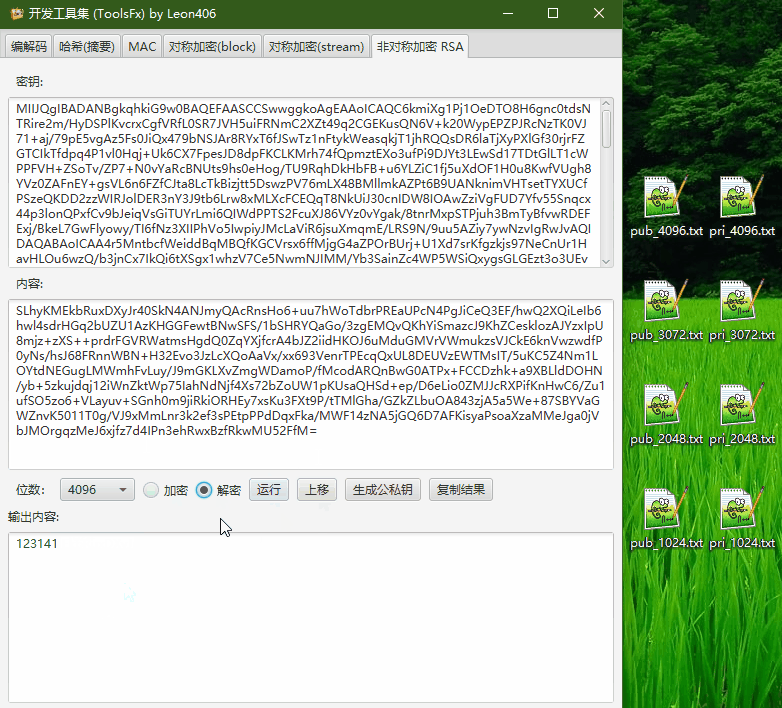 leon406/toolsfx
跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
 trustedsec/hate_crack
A tool for automating cracking methodologies through Hashcat from the TrustedSec team.
 n0kovo/awesome-password-cracking
A curated list of awesome tools, research, papers and other projects related to password cracking and password security.
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
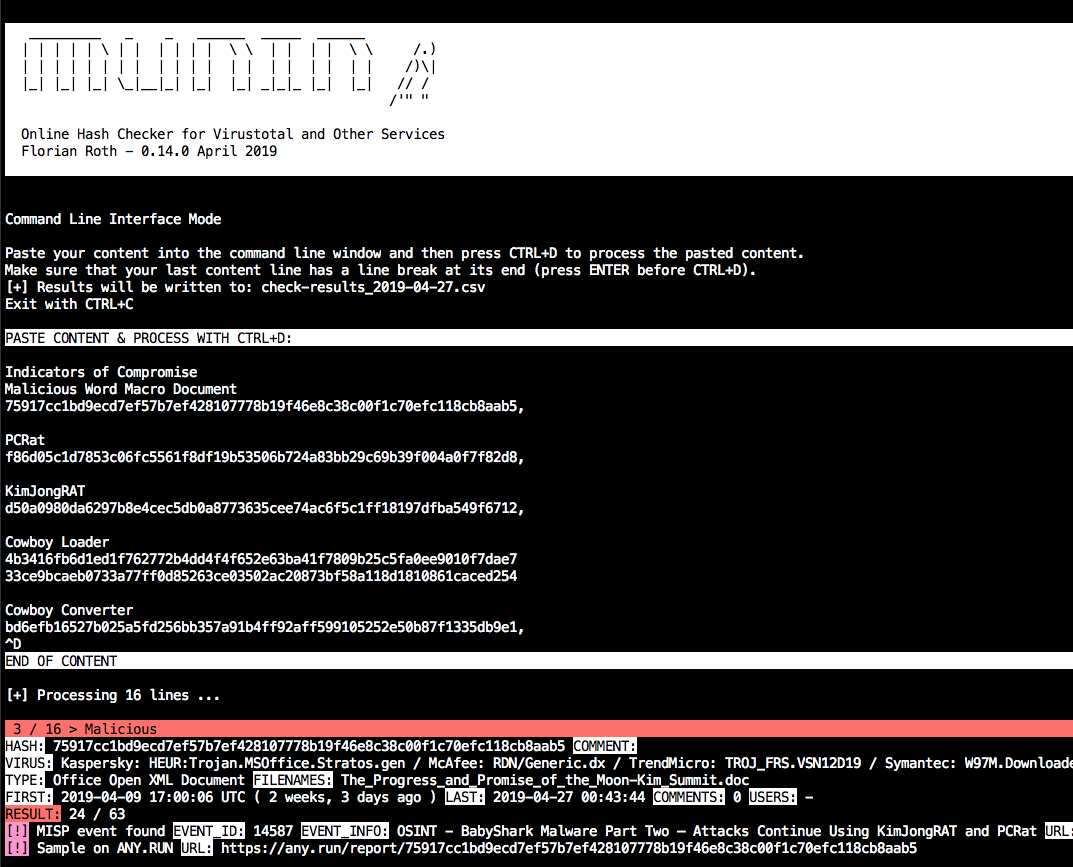 neo23x0/munin
Online hash checker for Virustotal and other services