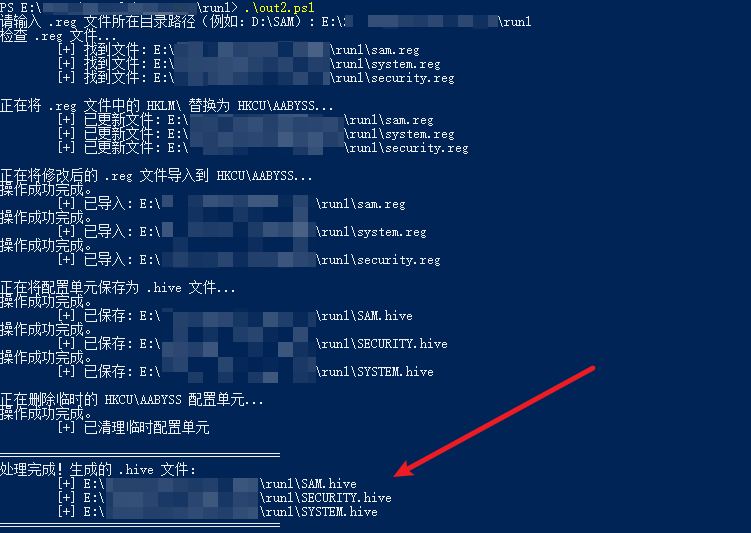
HashDump-BypassEDR
 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
hash-analysisids-ips-evasionpassword-attacks+3
2663 months ago
aabysszg/hashdump-bypassedrWindows绕过EDR实现DumpHash
 coalfire-research/doozer
Password cracking utility
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
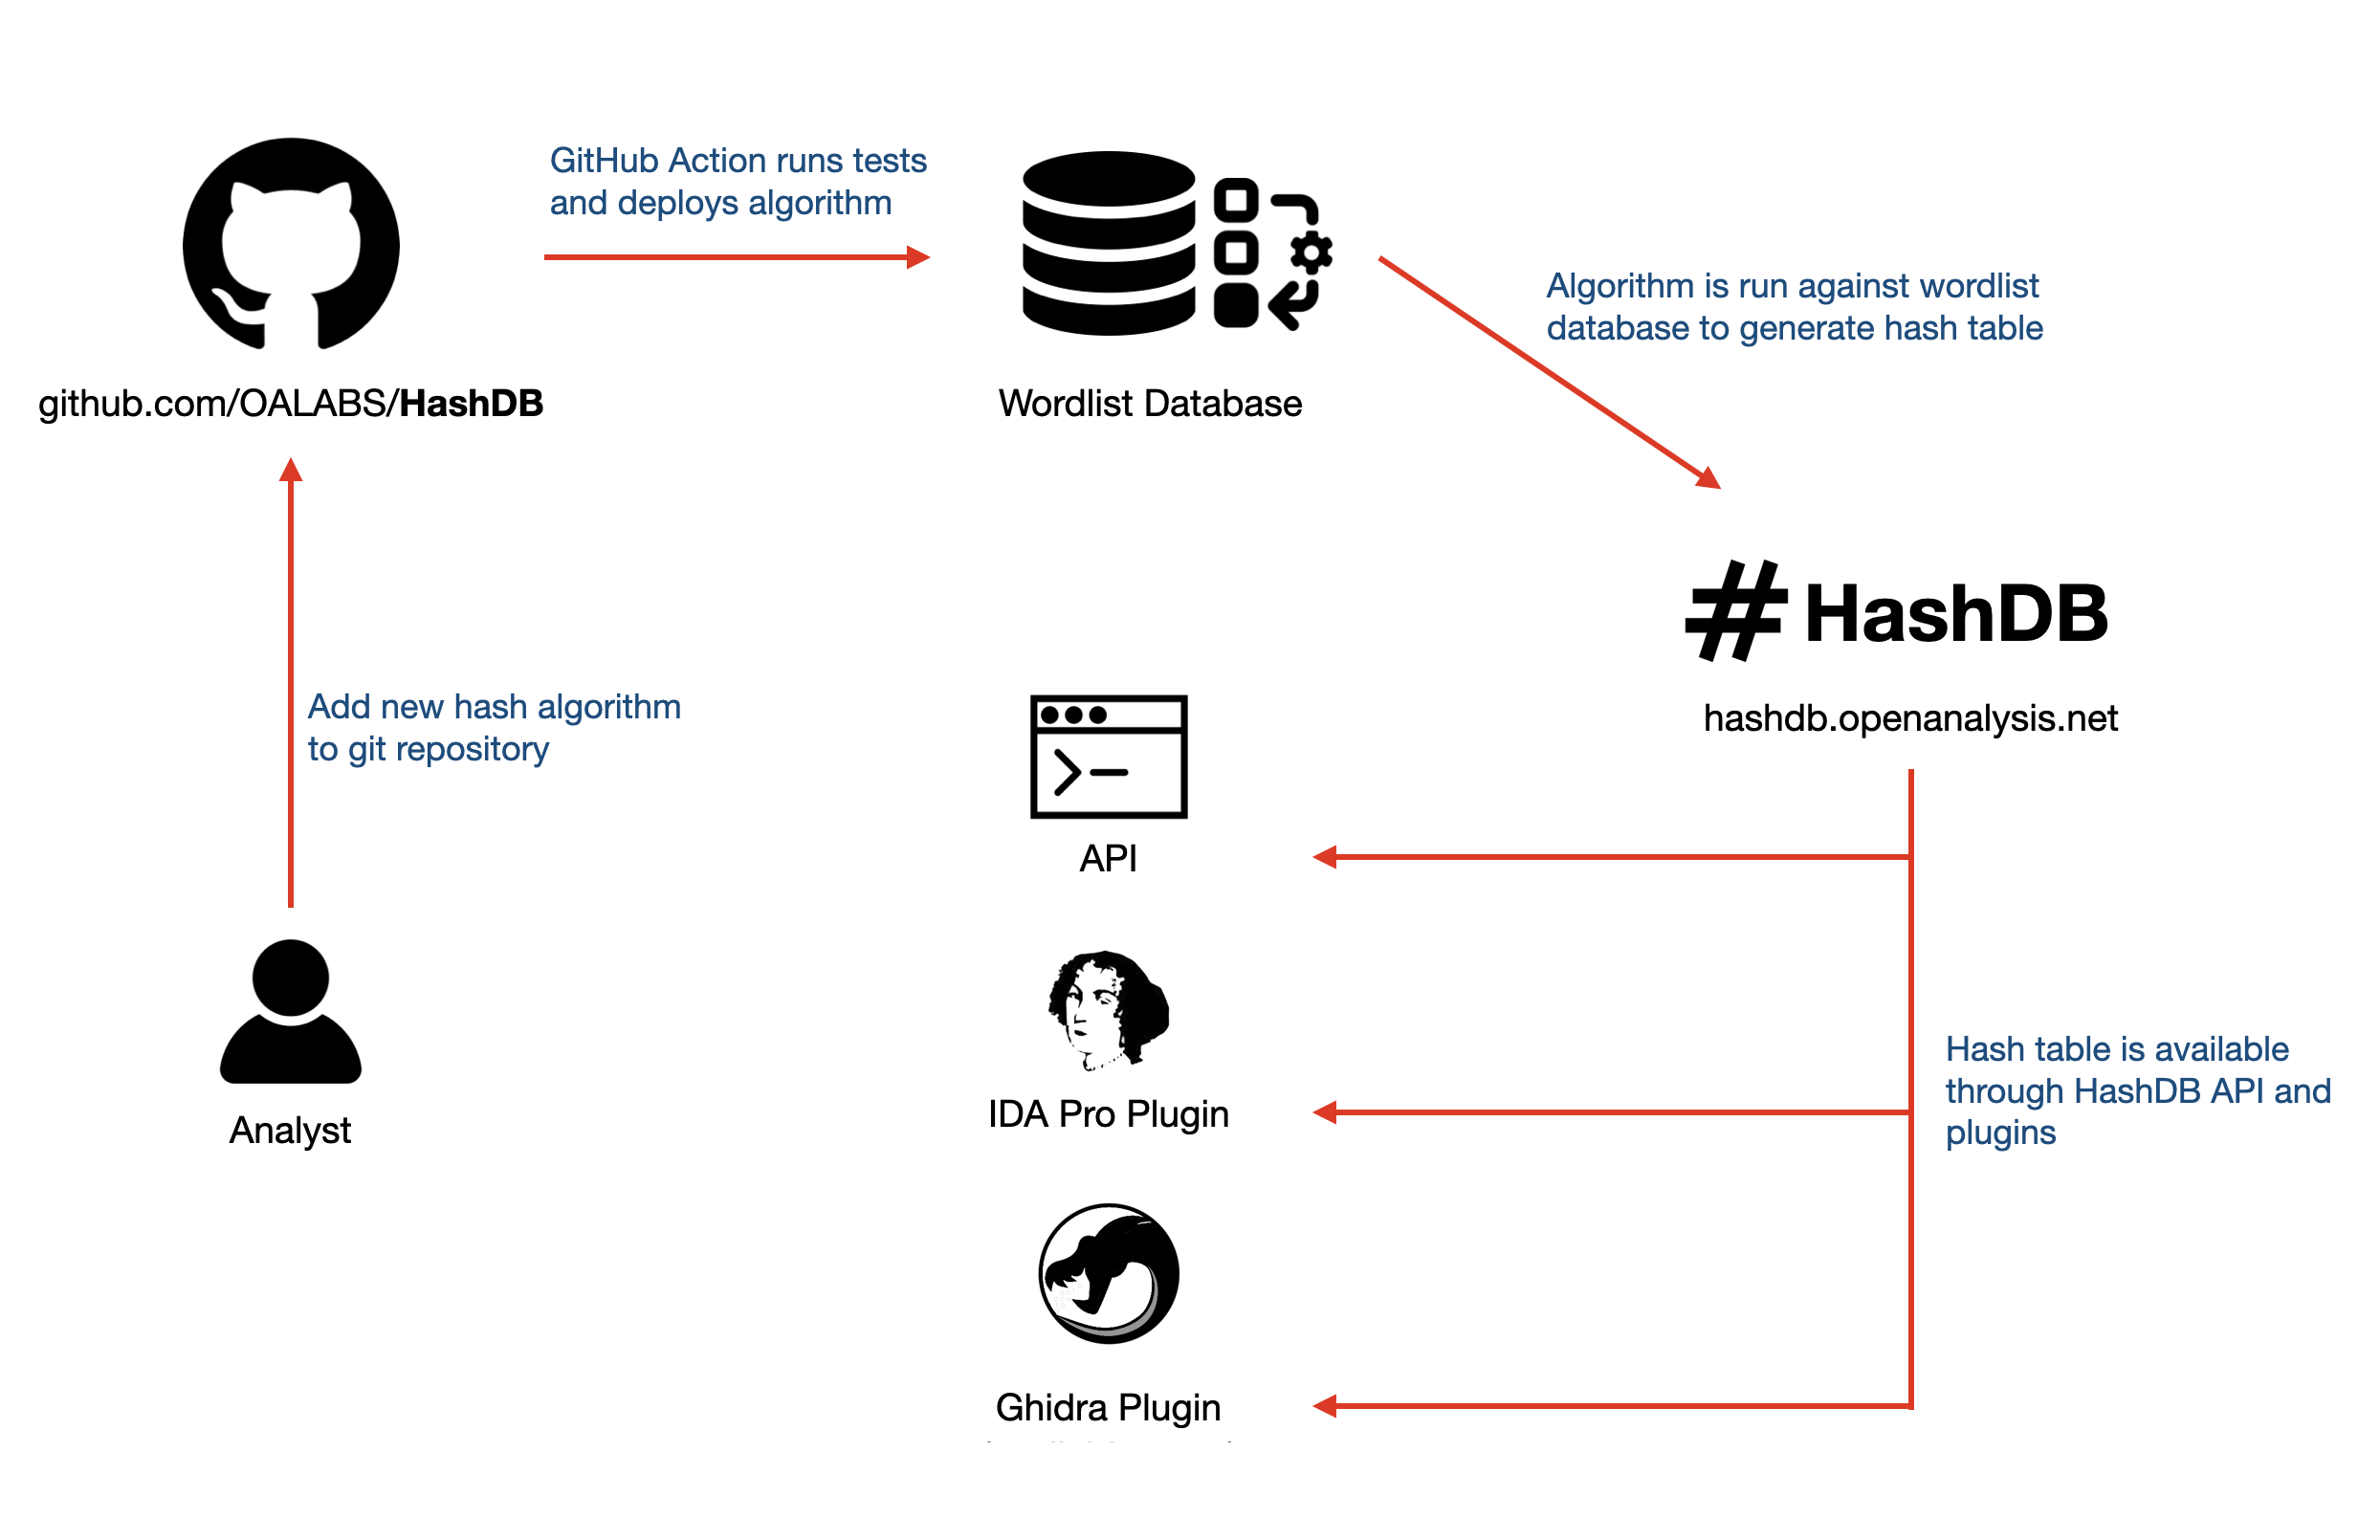 oalabs/hashdb
Assortment of hashing algorithms used in malware
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
 dave_m/clamtk
An easy to use, light-weight, on-demand virus scanner for Linux systems. For additional help, see the <a…
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
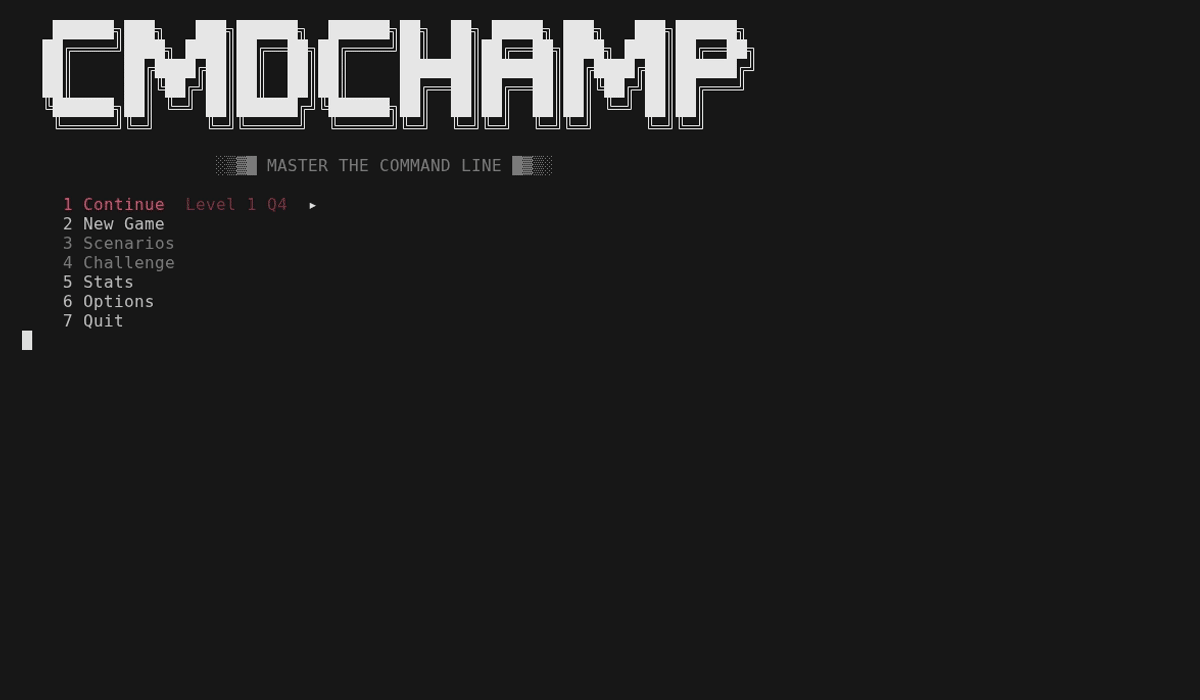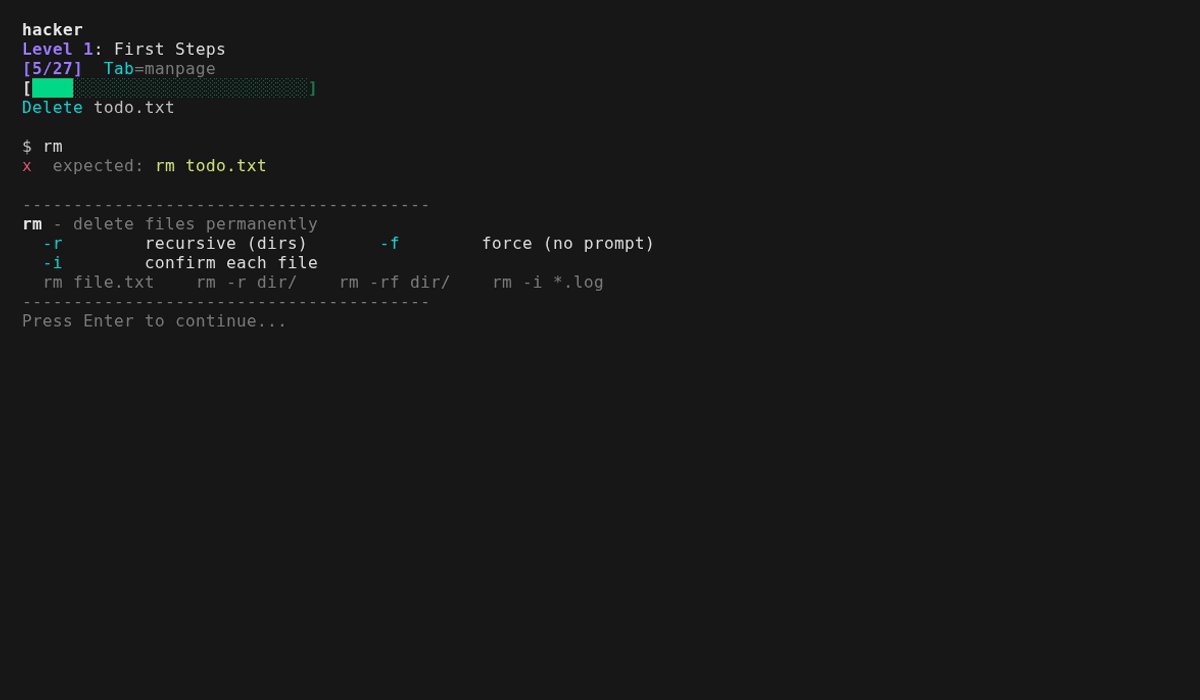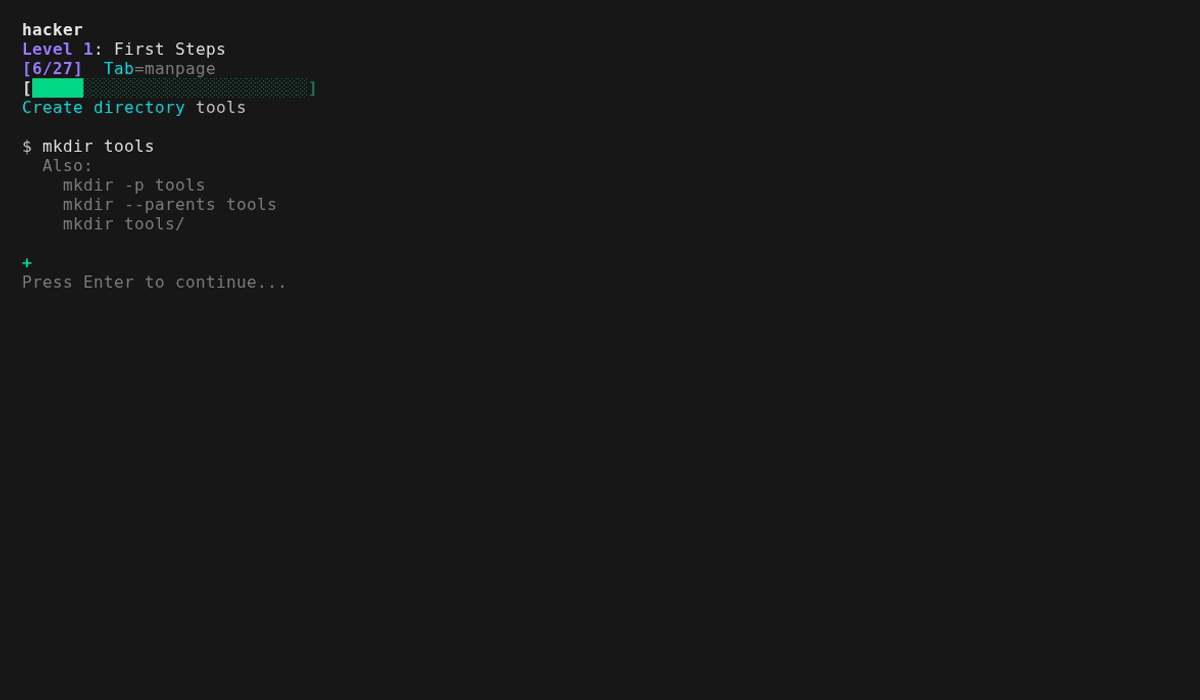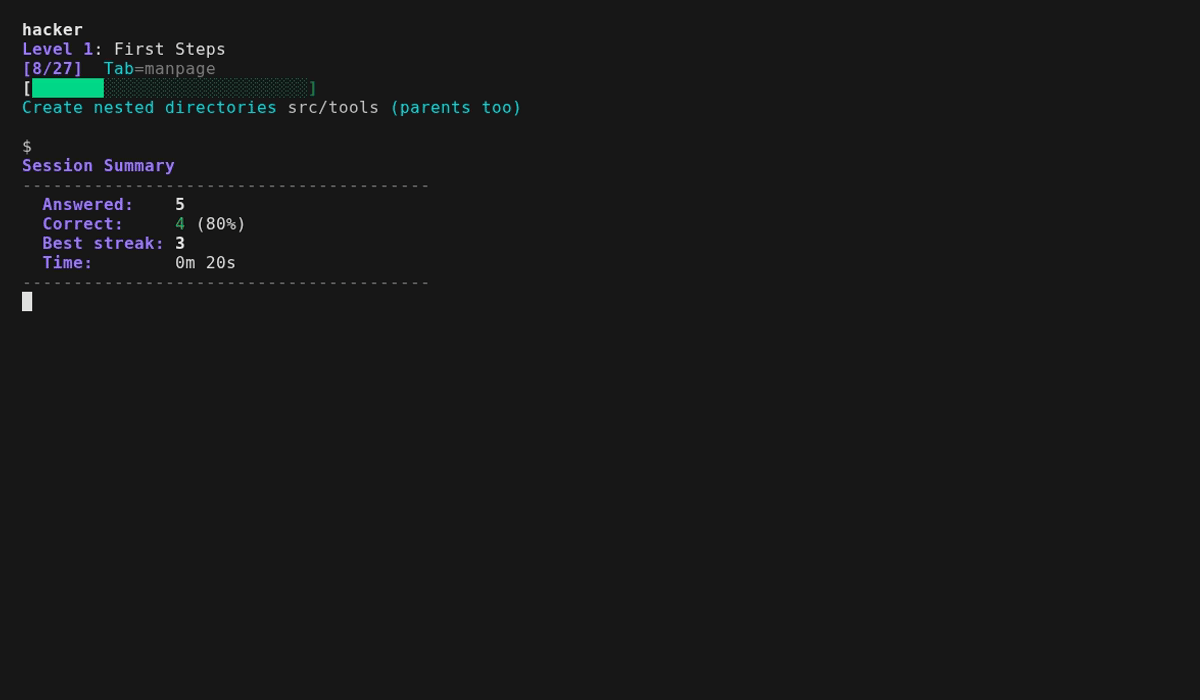 mellen9999/cmdchamp
bash CLI trainer — 30 levels from ls to privilege escalation
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 george0papasotiriou/cve-2026-22016-ipfs-cid-spoofing-via-multihash-length-extension
Python proof-of-concept demonstrating IPFS CID spoofing via multihash length extension, highlighting content-addressing verification flaws that can…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.