
TekDefense-Automater
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
hash-analysisinformation-gatheringosint+1
557
1an0rmus/tekdefense-automaterAutomater - IP URL and MD5 OSINT Analysis
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 netspooky/inhale
A malware analysis and classification tool.
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
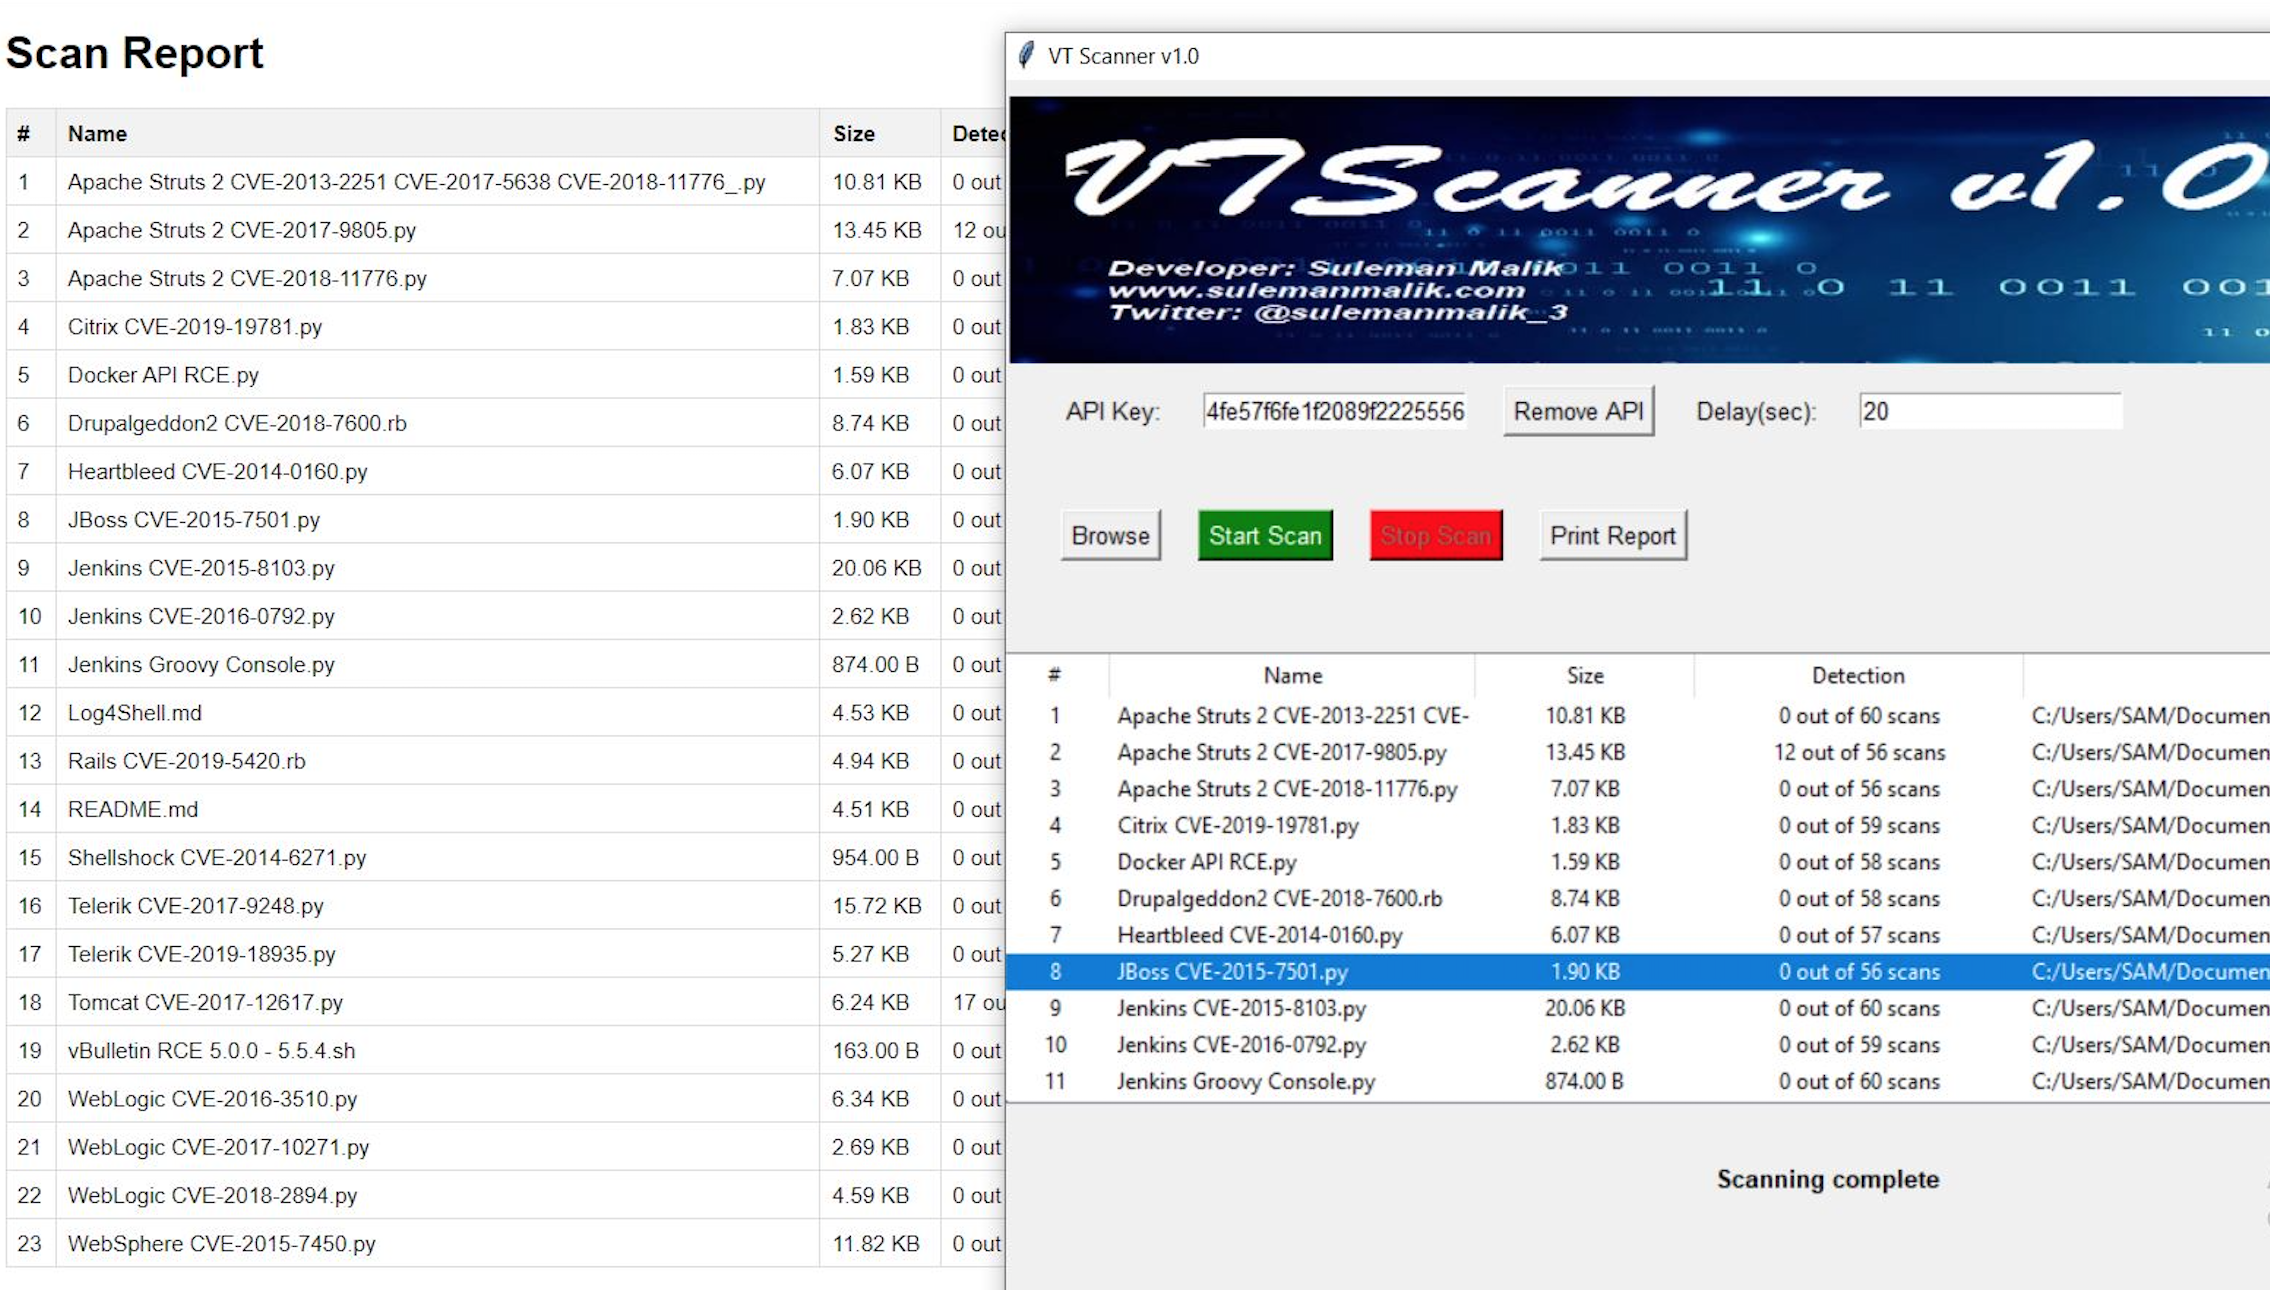 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
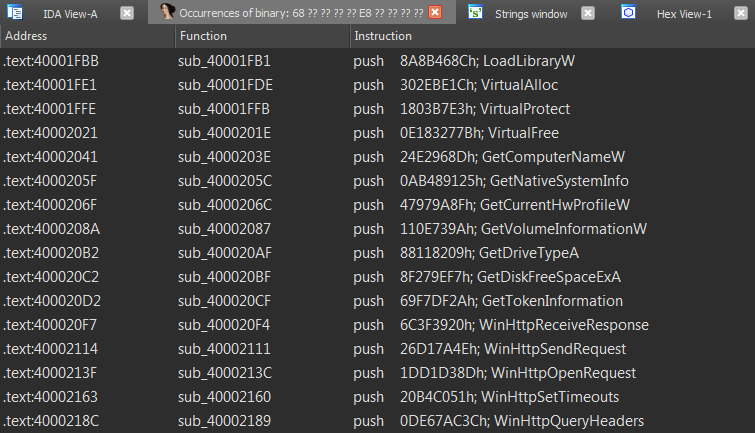 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 occamsec/log4j-checker
Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.
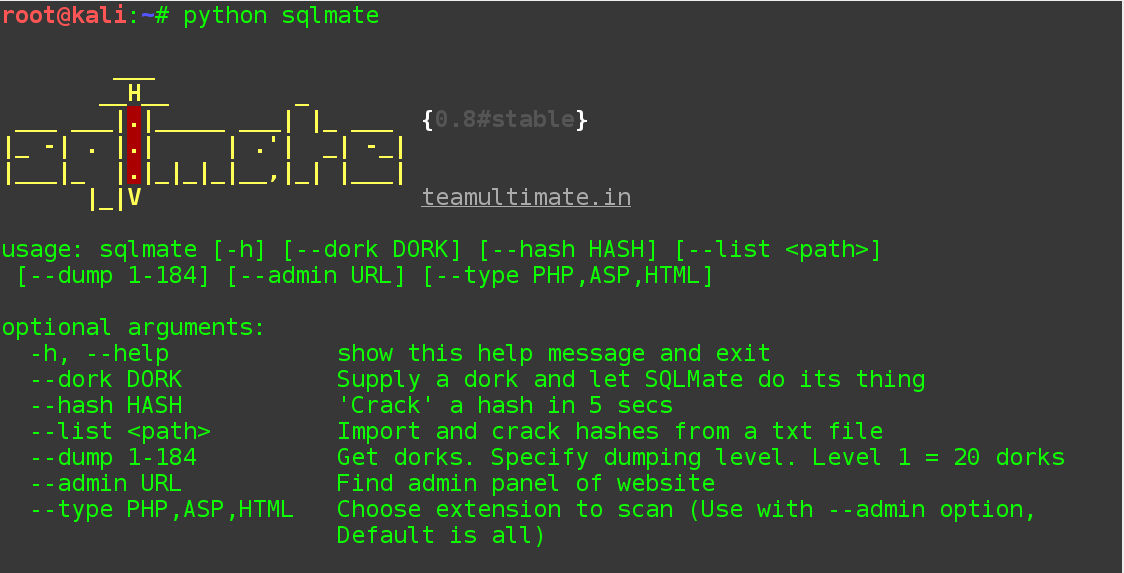 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 joshuamart/pwnedpasswordschecker
Search (offline) if your password (NTLM or SHA1 format) has been leaked (HIBP passwords list v8)
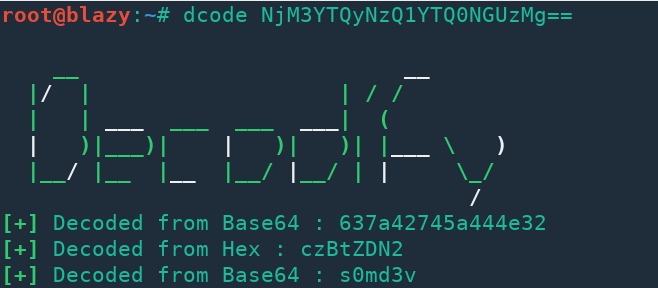 s0md3v/decodify
Detect and decode encoded strings, recursively.
 evilsocket/fang
A multi service threaded MD5 cracker