

IPED
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
data-recoverydigital-forensicsdisk-forensics+9
3.0k
sepinf-inc/ipedIPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
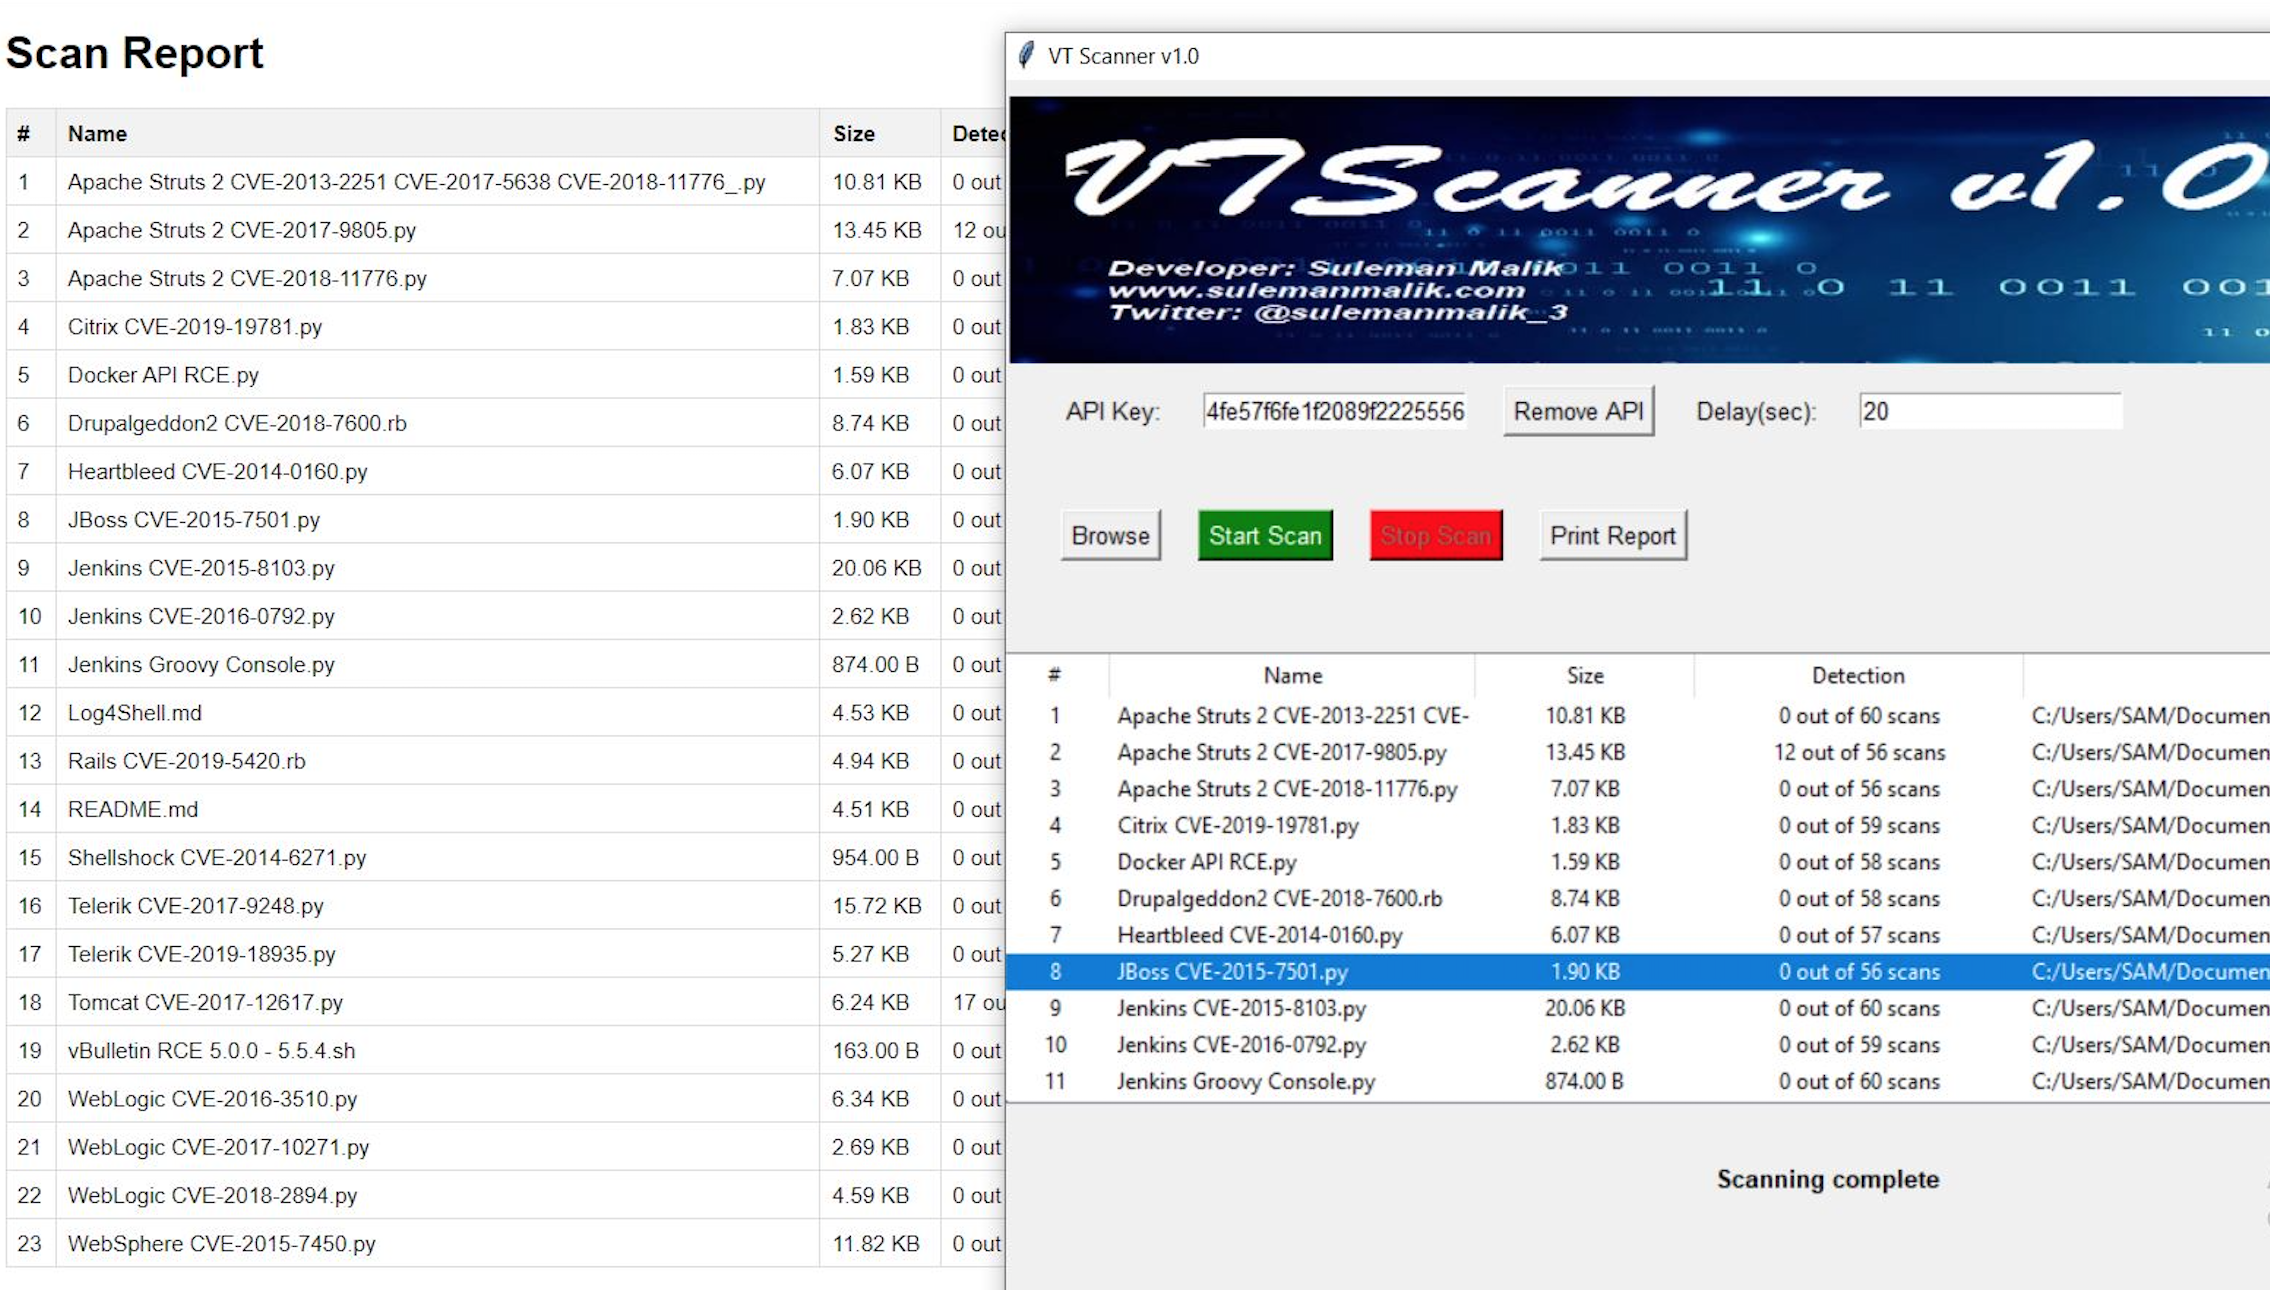 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…