

Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
984 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 bandrel/hashcatrosetta
Hashcat rule analyzer and interpreter - A Rosetta Stone for decoding hashcat rule syntax
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.
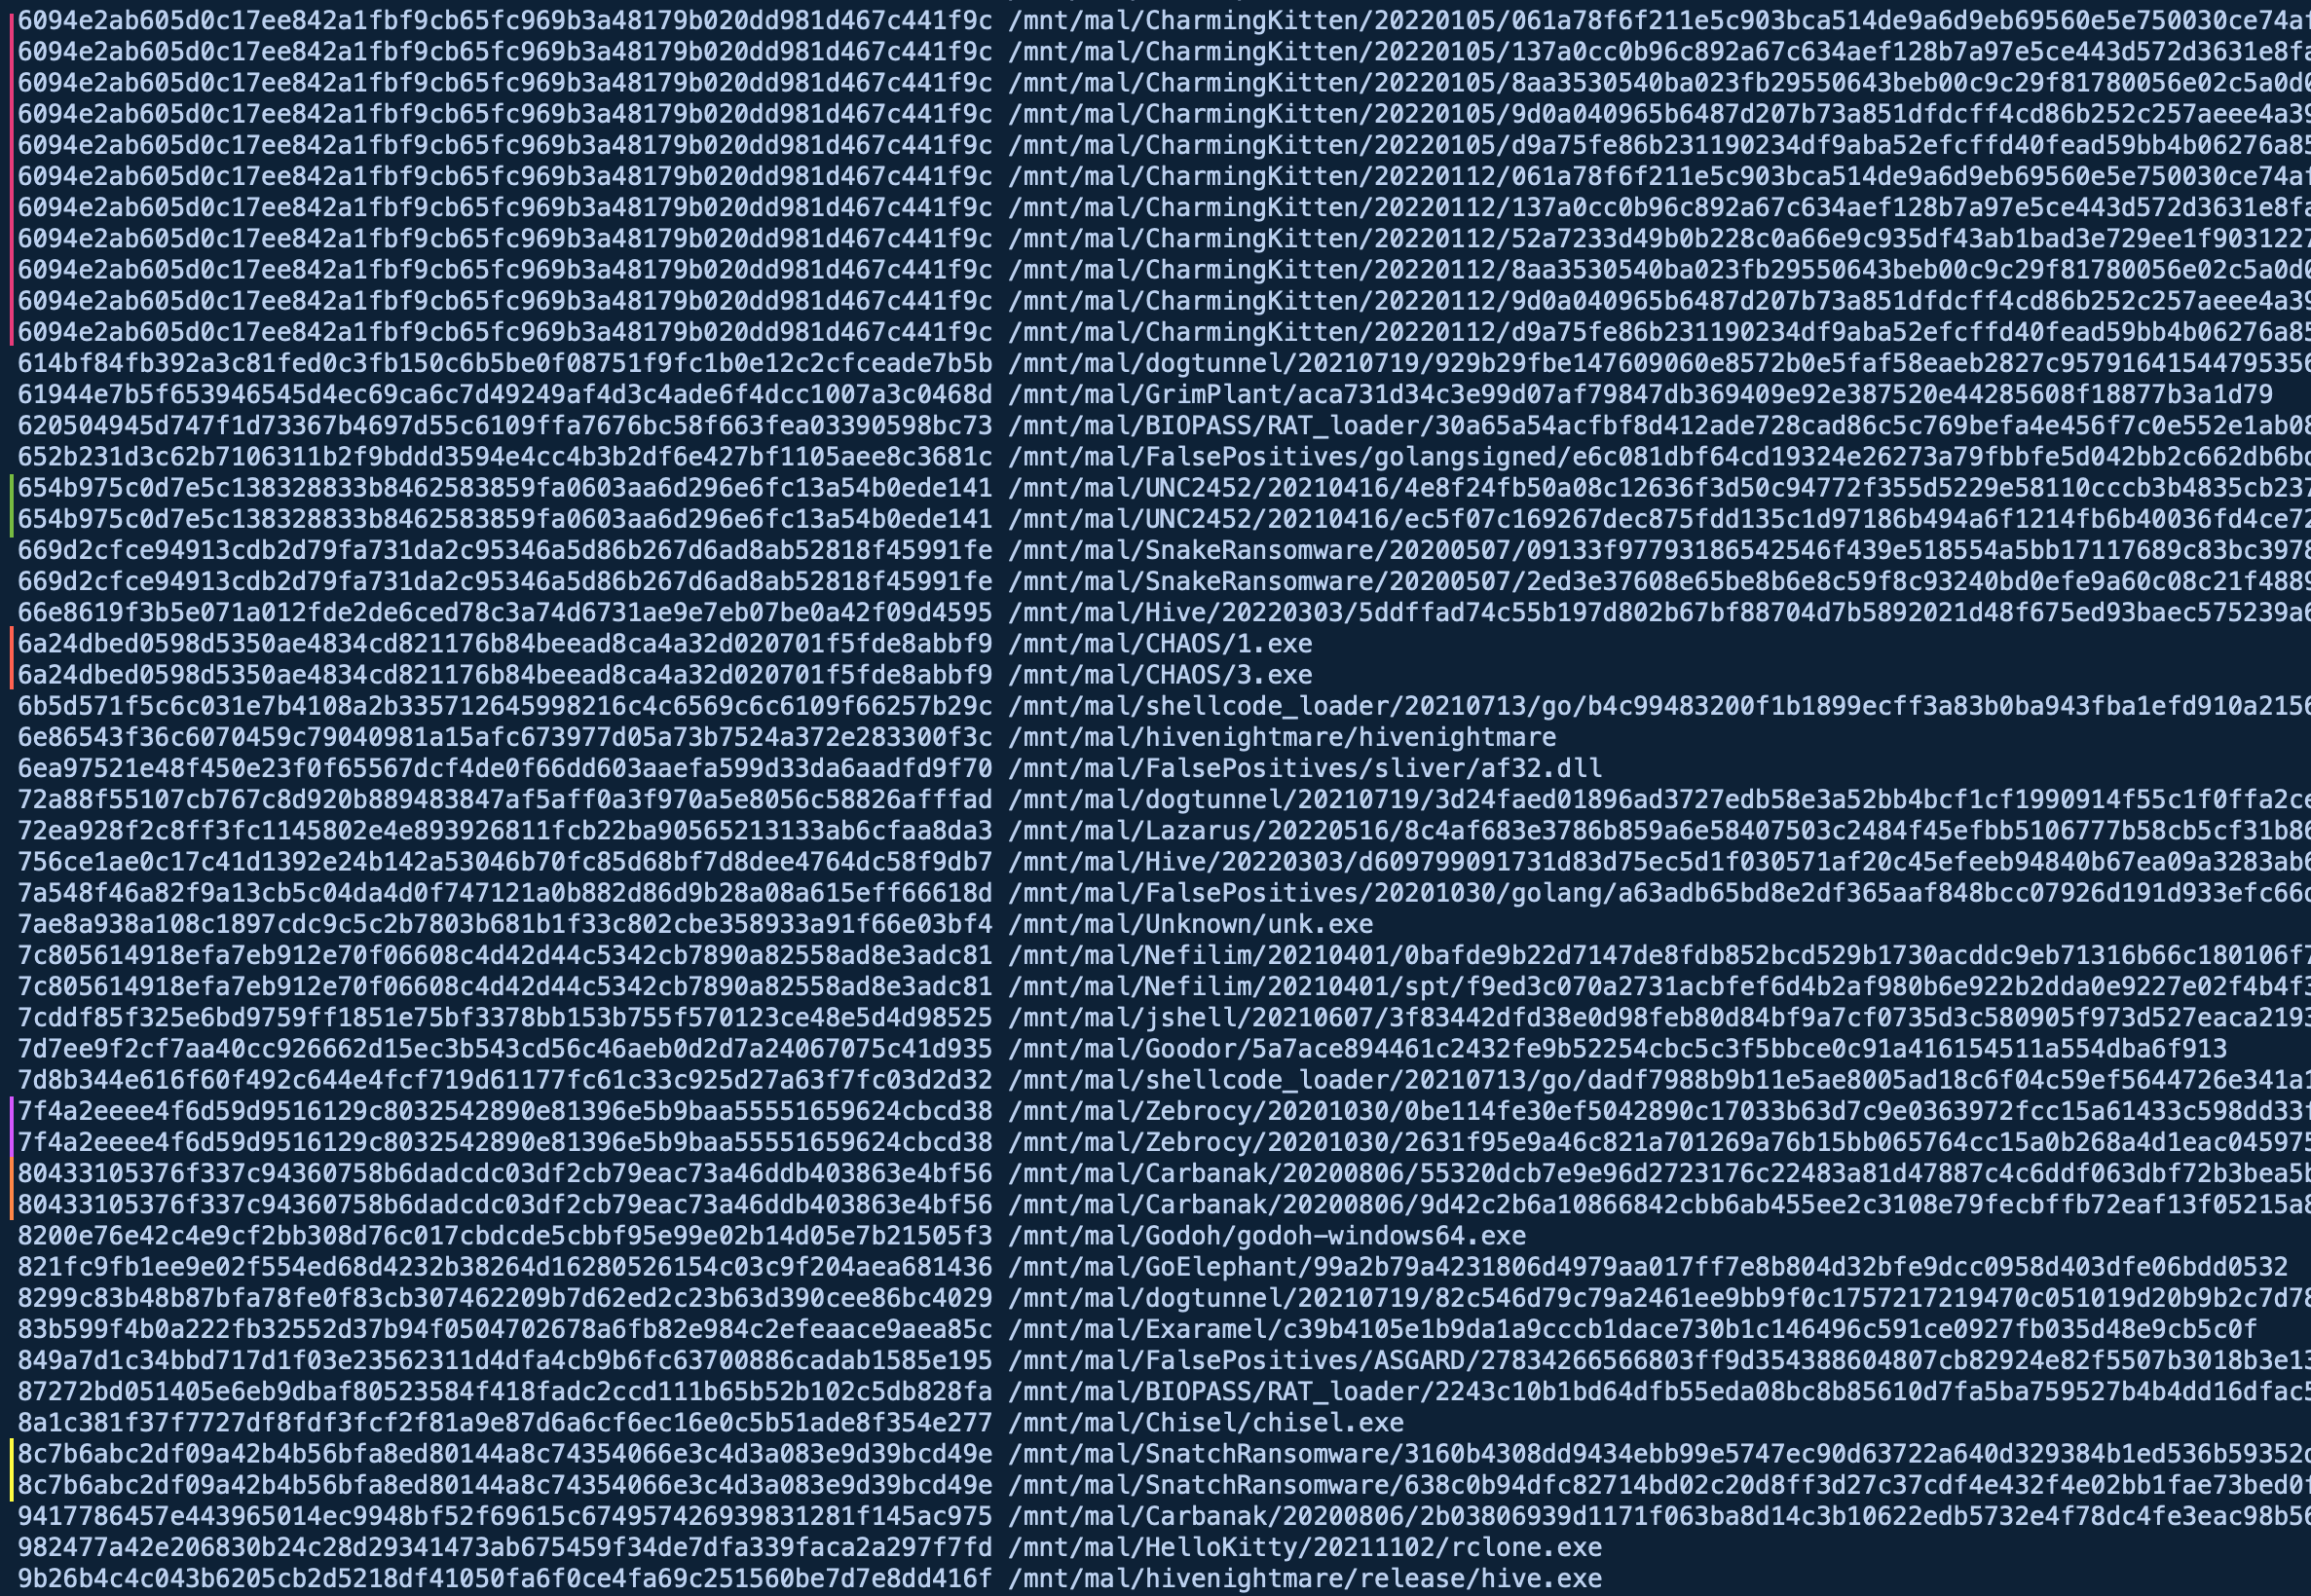 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
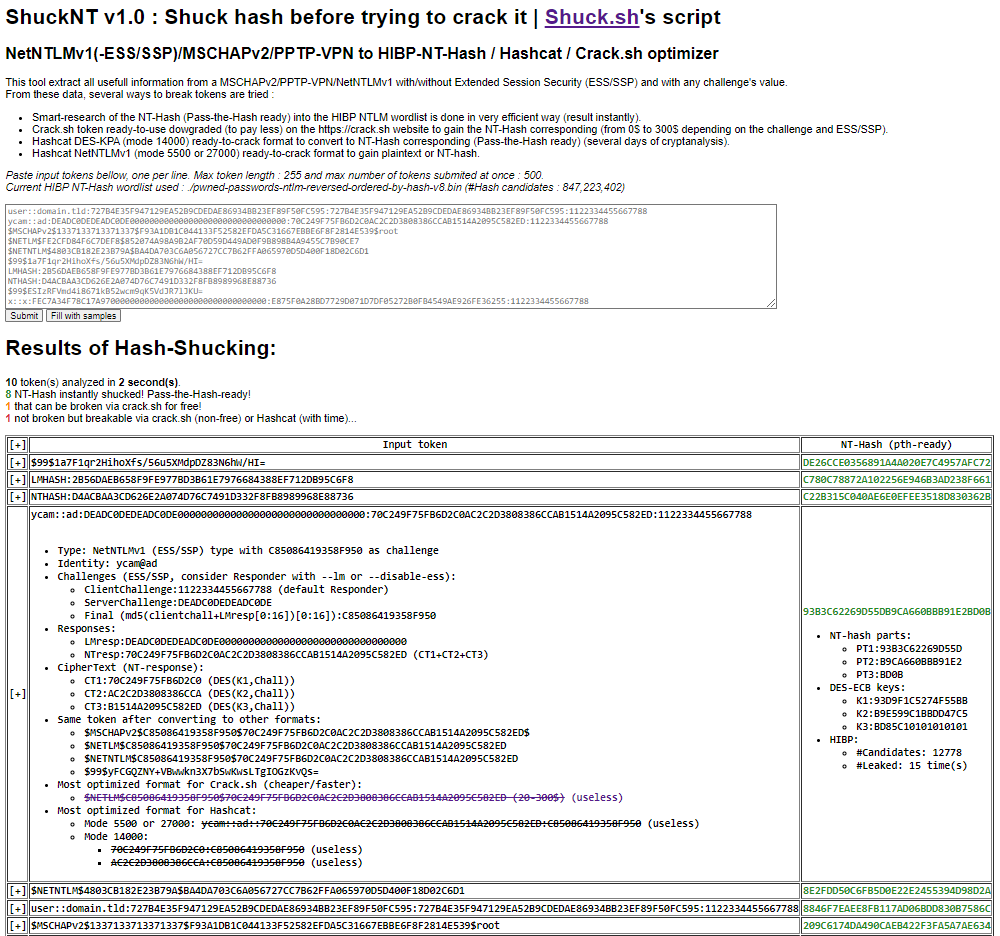 yanncam/shucknt
ShuckNT is the script of Shuck.sh online service for on-premise use. It is design to dowgrade, convert, dissect and shuck authentication token based…