
Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
974 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
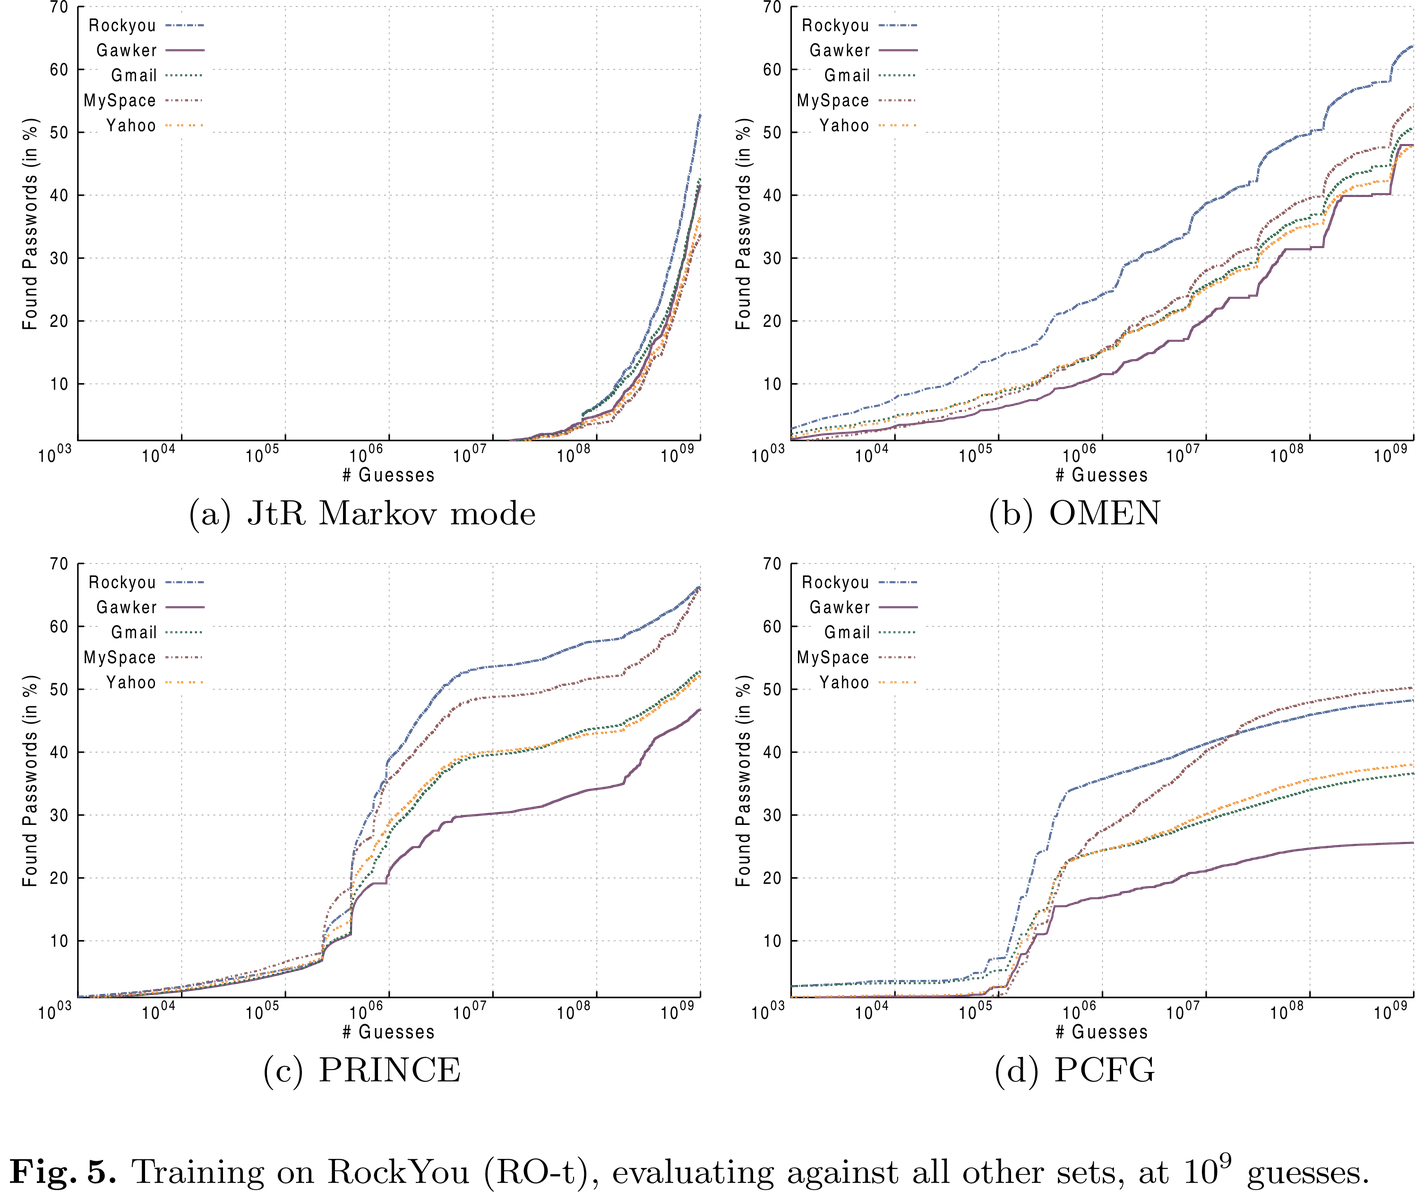 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
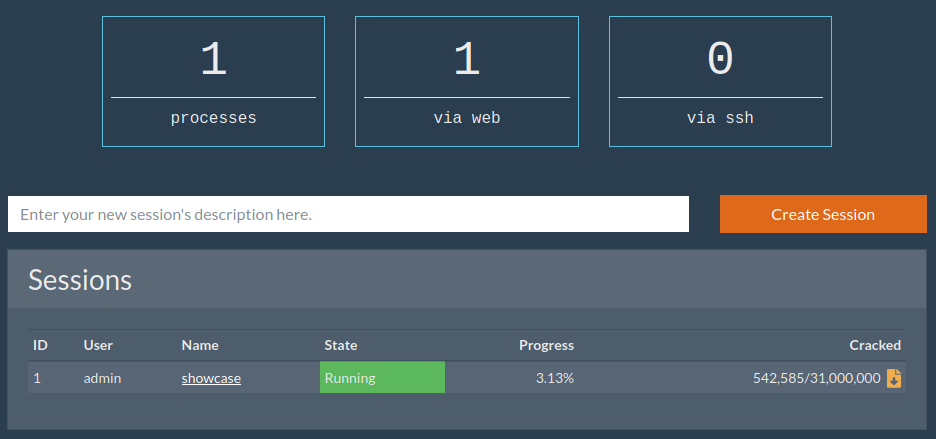 sadreck/crackerjack
Web-based GUI for Hashcat that simplifies password cracking with session management, mask generation, wordlist support, and multi-user access.
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 rustcrypto/hashes
Collection of cryptographic hash functions written in pure Rust
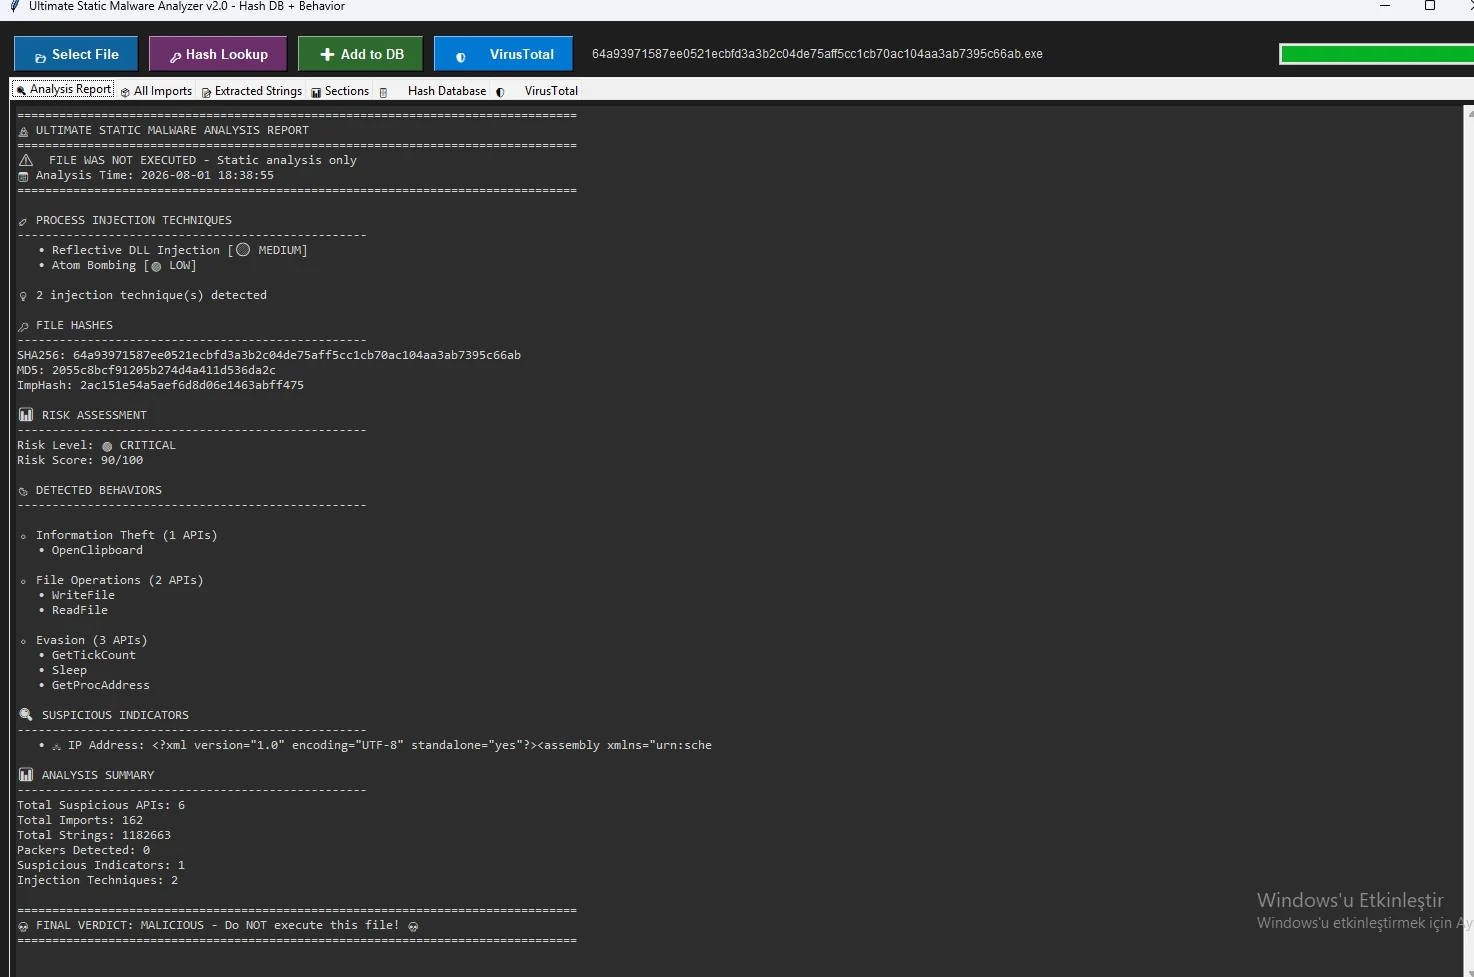 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 facebook/threatexchange
Trust & Safety tools for working together to fight digital harms.

 wattocyber/custom-oscp-tooling
OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…
 abusech/yaraify
Open YARA scan- and search engine
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 nextronsystems/gimphash
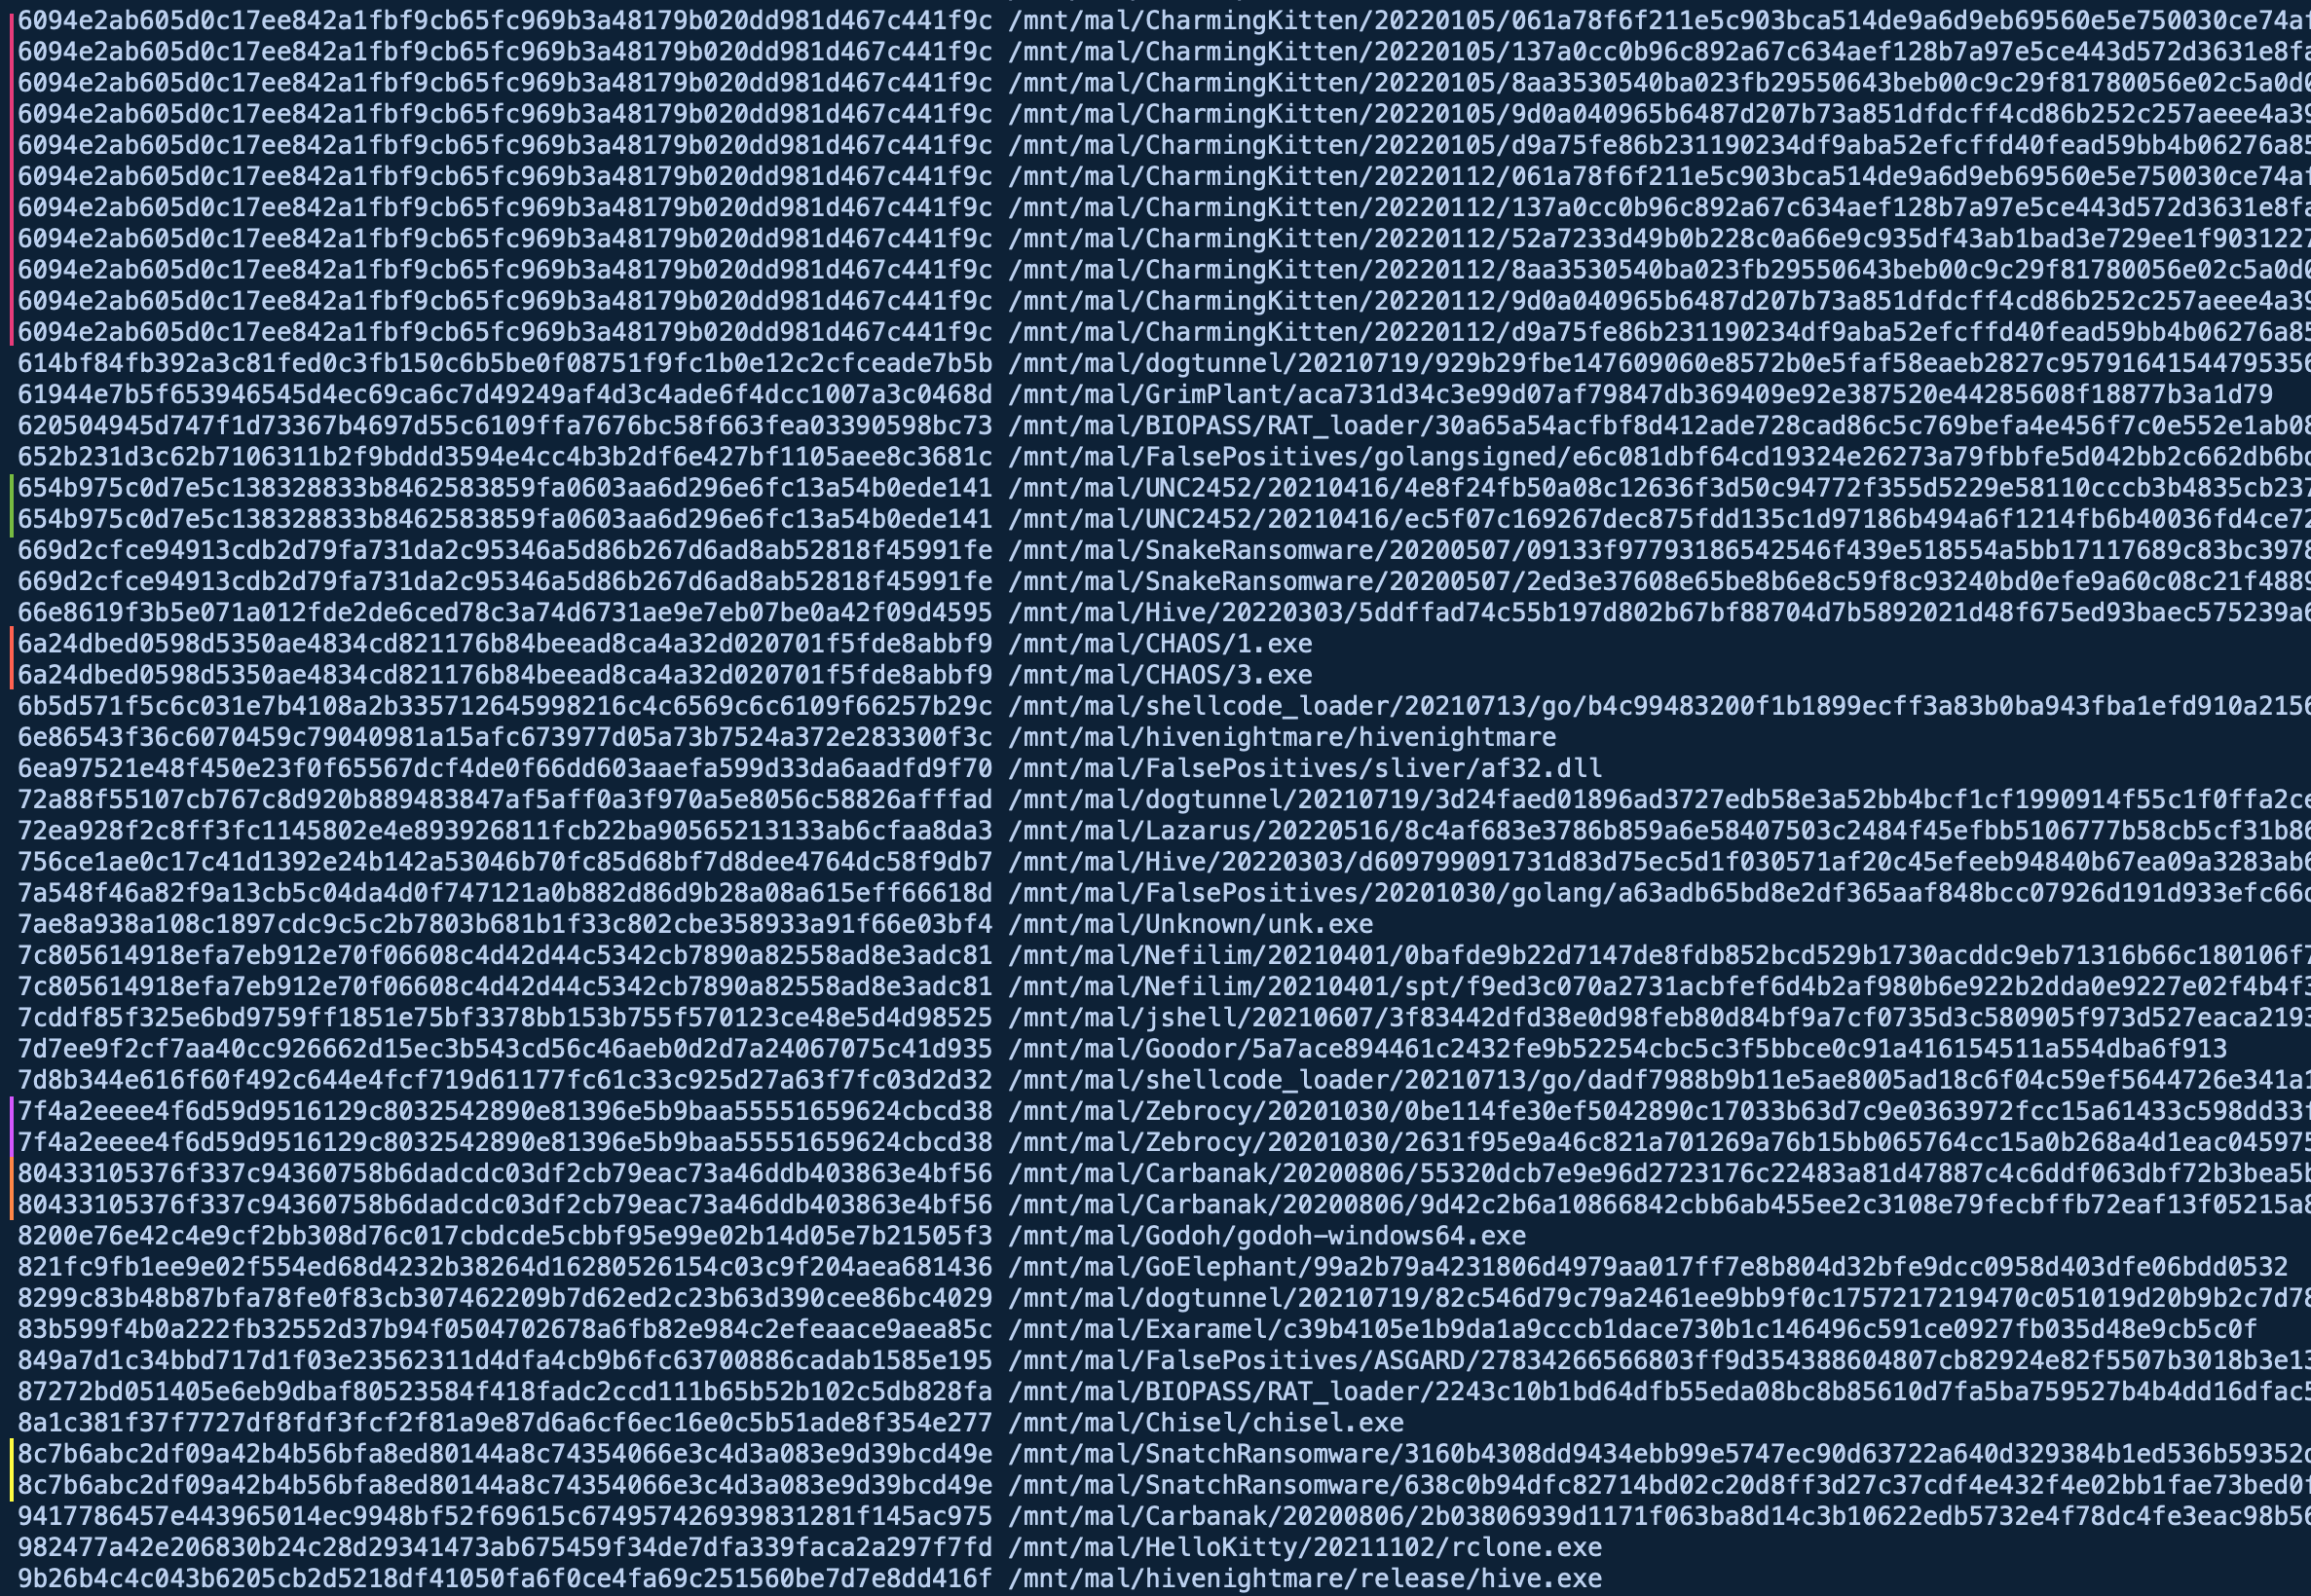
Imphash-like calculation on Golang binaries
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 inquest/python-inquestlabs
A Pythonic interface and command line tool for interacting with the InQuest Labs API.