GateX
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
1
abraxas/gatexFortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
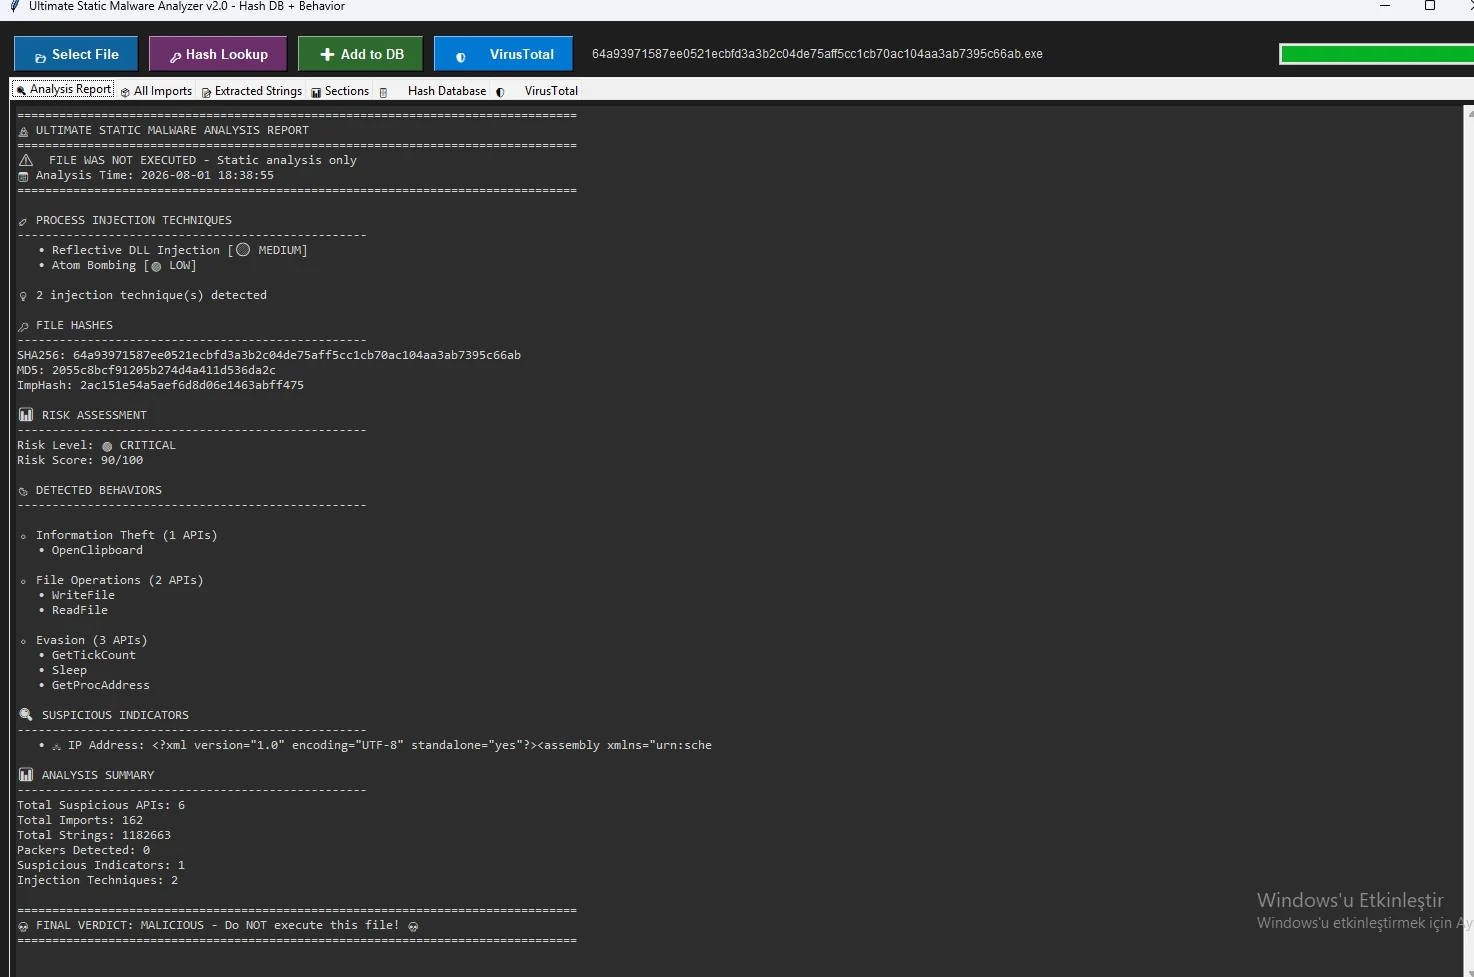 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 decalage2/collisions
Hash collisions and their exploitations
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 google/permhash
Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
 cvonkleist/vxworks_hash
code to reverse vxworks 5.x password hashes
 nccgroup/pip3line
The Swiss army knife of byte manipulation
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
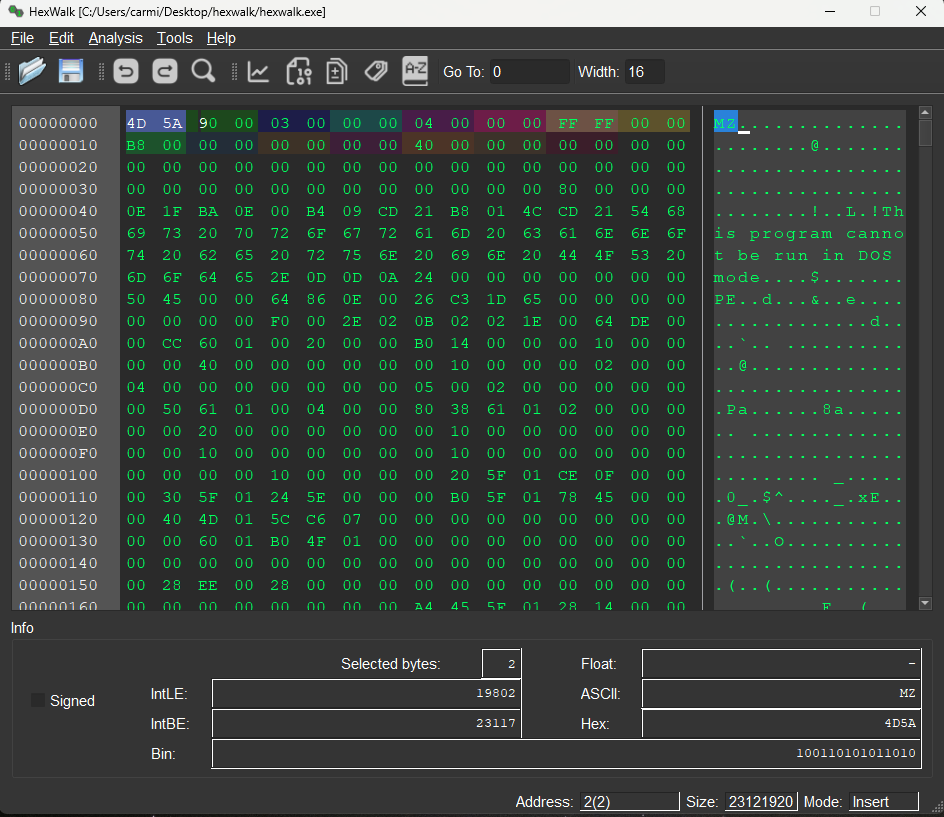 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 polllogamer/sha-256-backdoor-discovery-engine
Detects potential backdoors in SHA-256 hashes using cryptographic analysis and pattern recognition. Designed for malware analysis and security…