MalwareForge---Advanced-Static-Malware-Analyzer

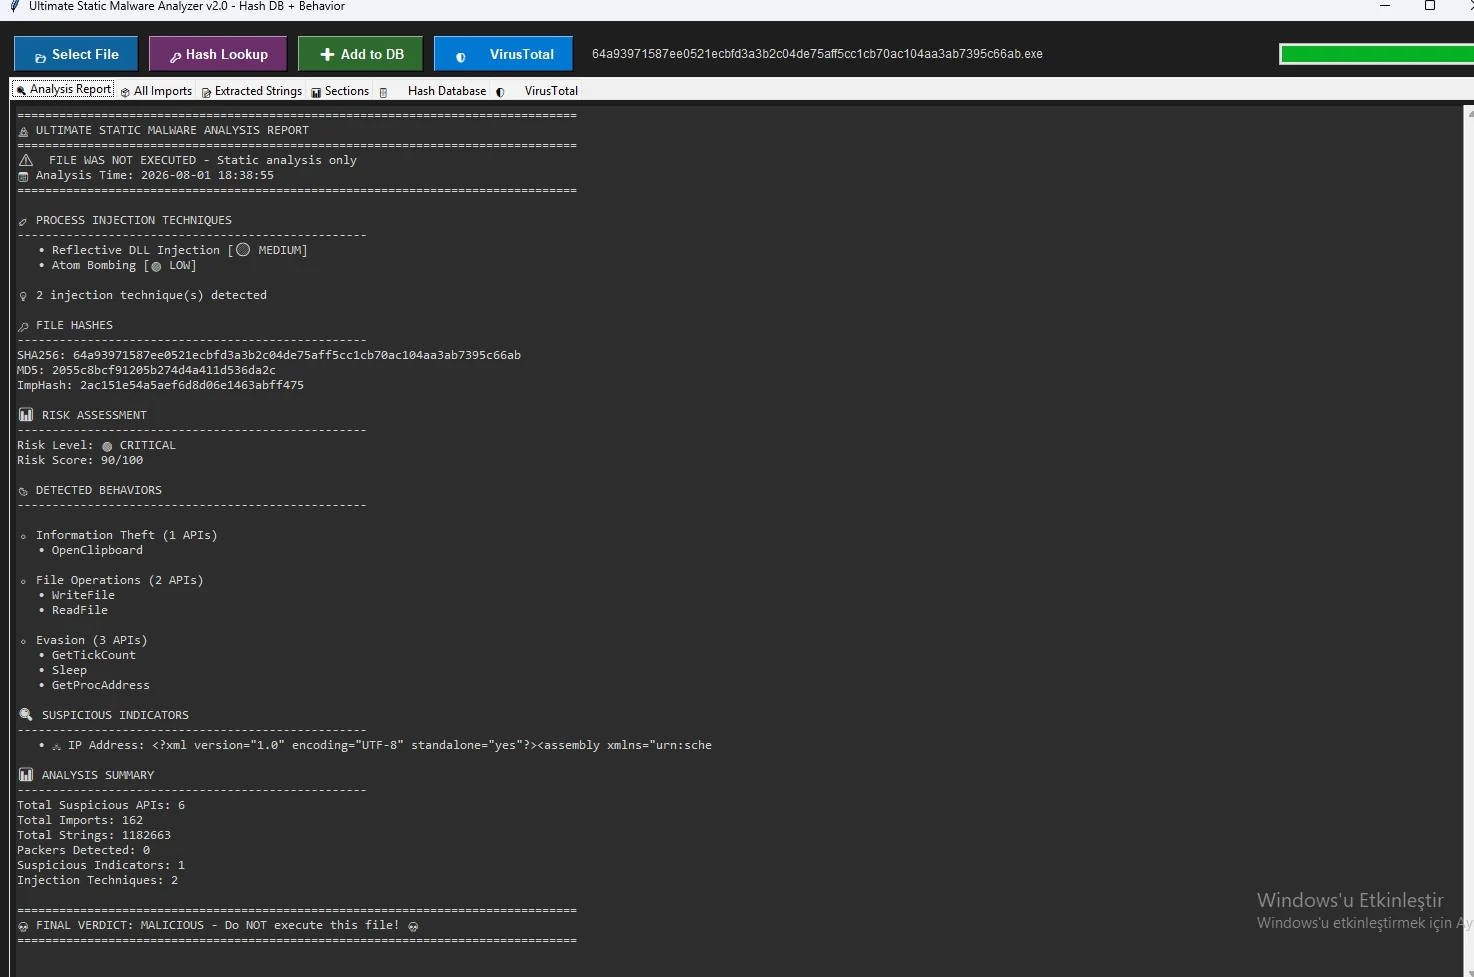
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Open YARA scan- and search engine

Assortment of hashing algorithms used in malware

Imphash-like calculation on Golang binaries

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

Framework for hashing declared permissions in Chromium extensions and APKs, enabling clustering, hunting, and pivoting across potentially malicious…

A Binary Genetic Traits Lexer Framework

A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.

Digital Forensics Intelligence Framework

The Swiss army knife of byte manipulation

Binary and Directory tree comparison tool using Fuzzy Hashing


CLI client for bulk DIARIO API consumption: upload PDF/Office documents, query file hashes, and automate malware analysis workflows via command-line…

FWT is a security analysis and file monitoring tool that utilizes Sysmon events.

Bash and PowerShell scripts to scan a local filesystem for Log4j .jar files which could be vulnerable to CVE-2021-44228 aka Log4Shell.

A set of functions to increase productivity while hacking with Bash