

Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
974 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 abusech/yaraify
Open YARA scan- and search engine
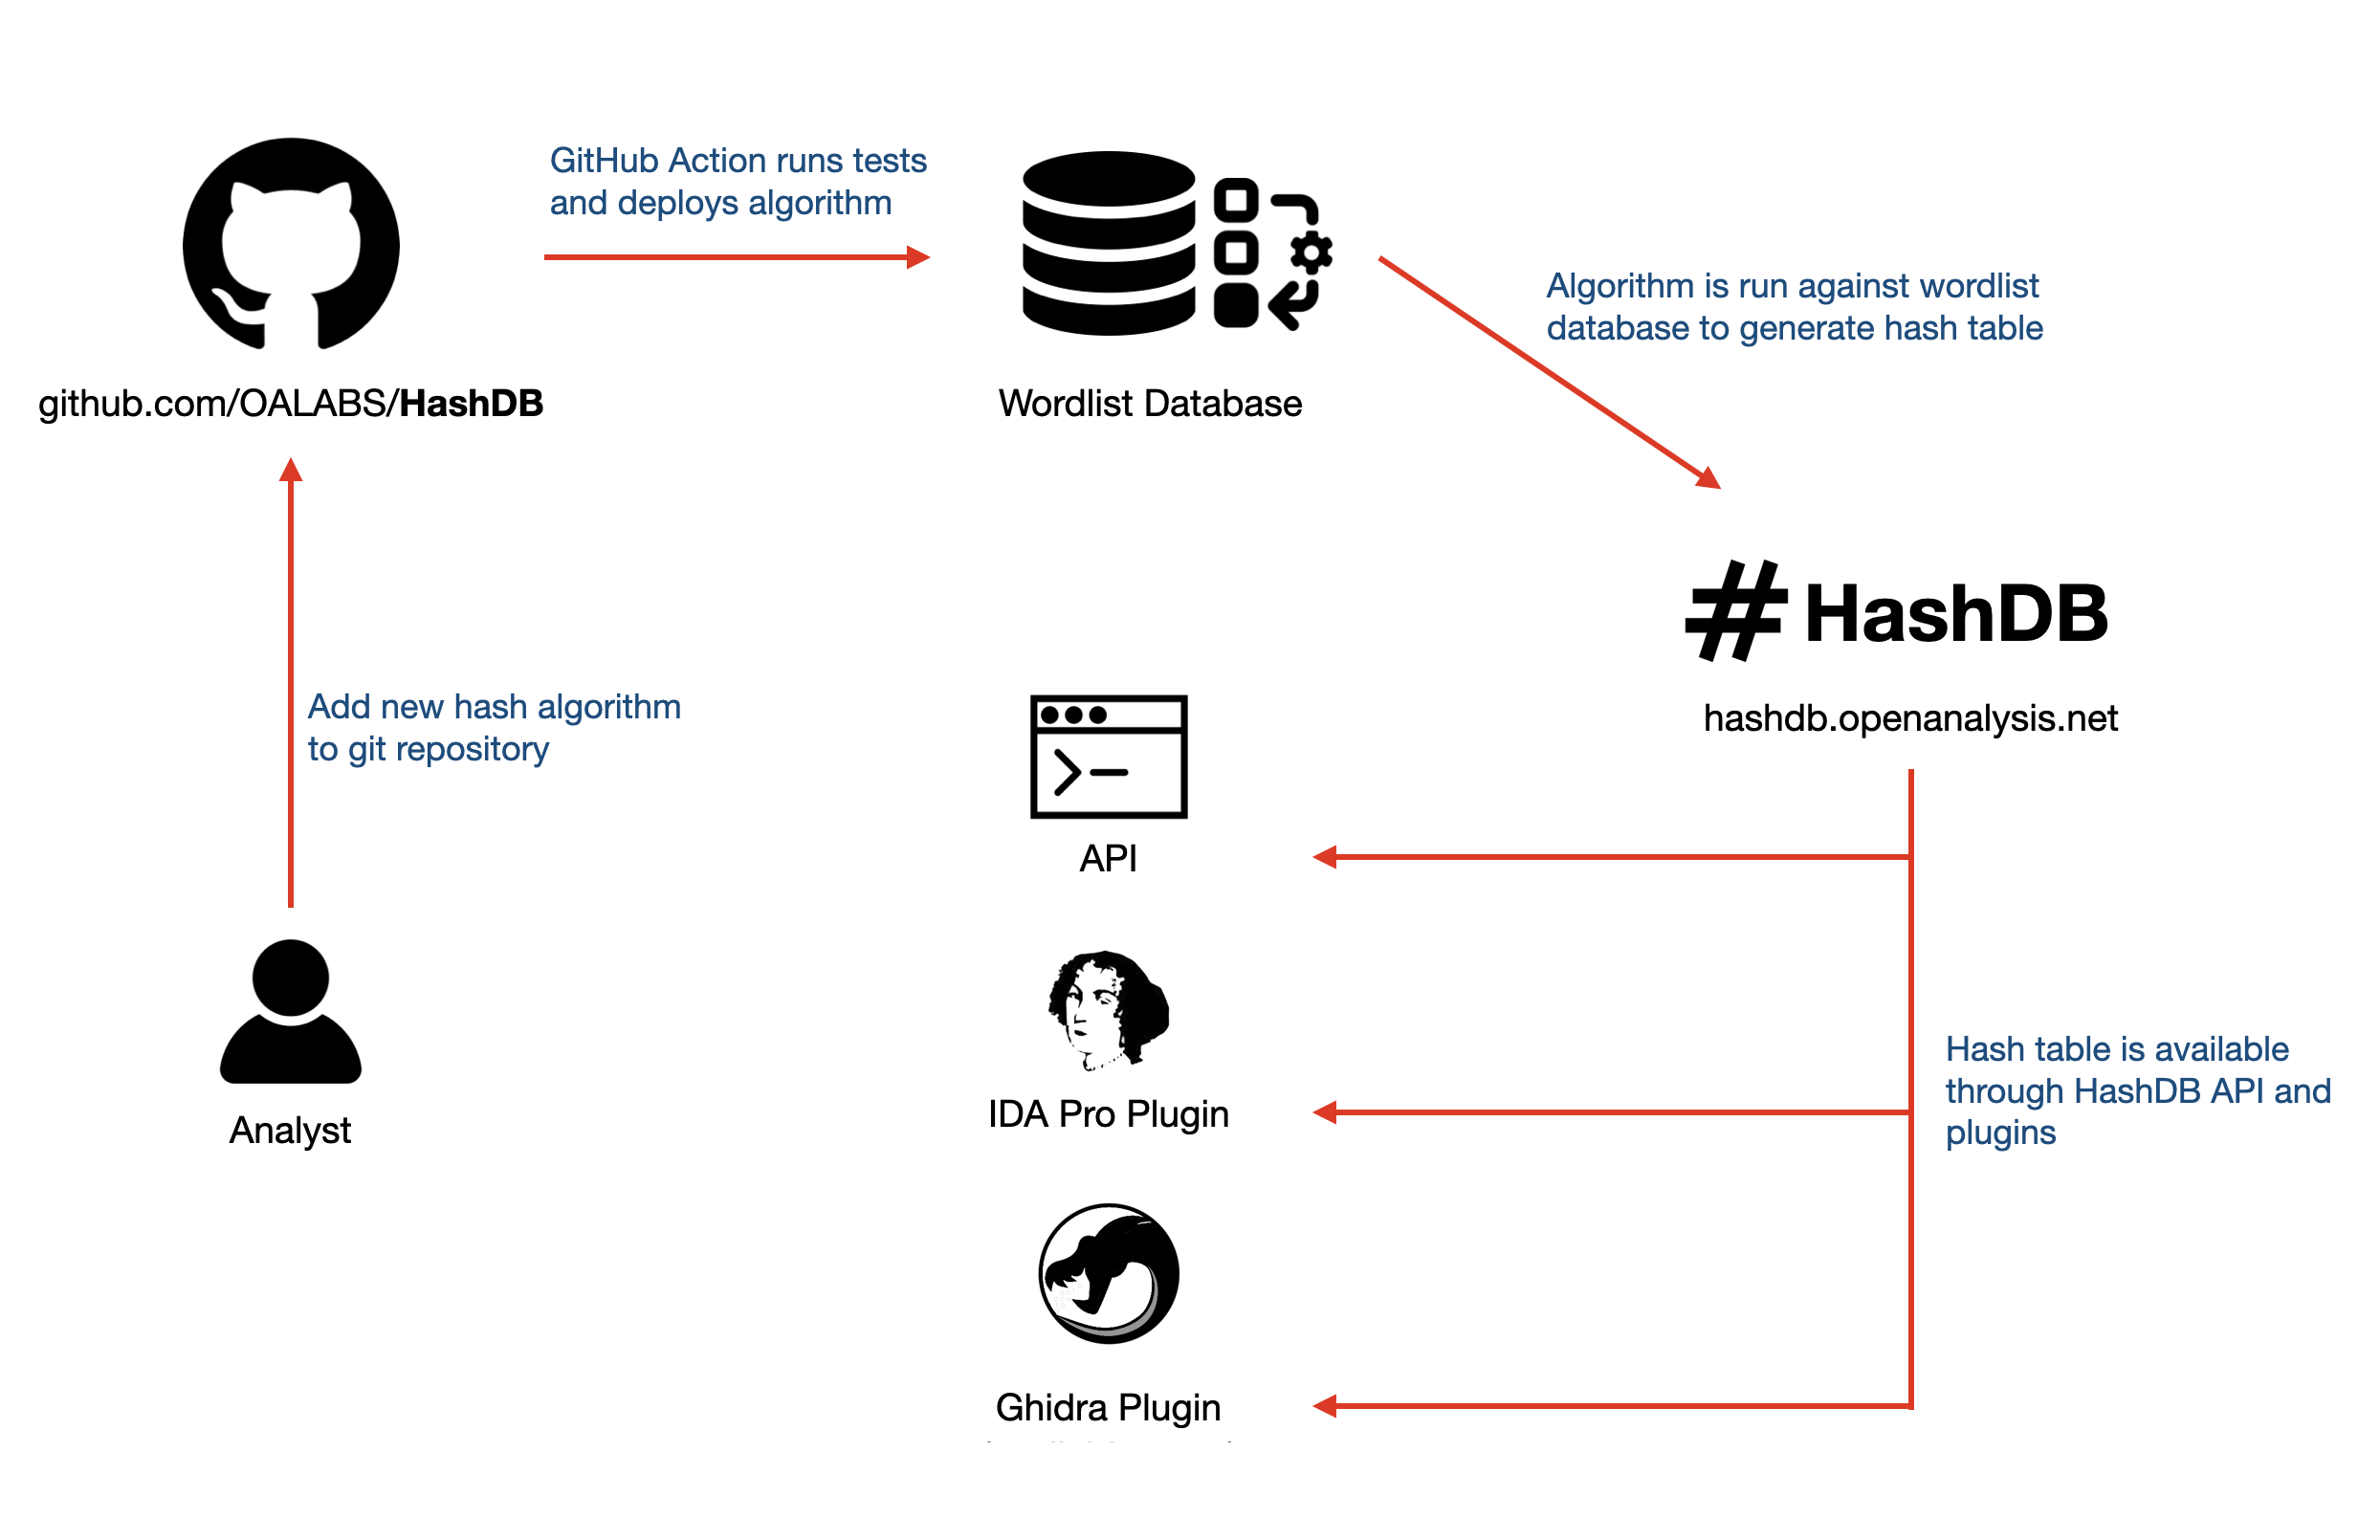 oalabs/hashdb
Assortment of hashing algorithms used in malware
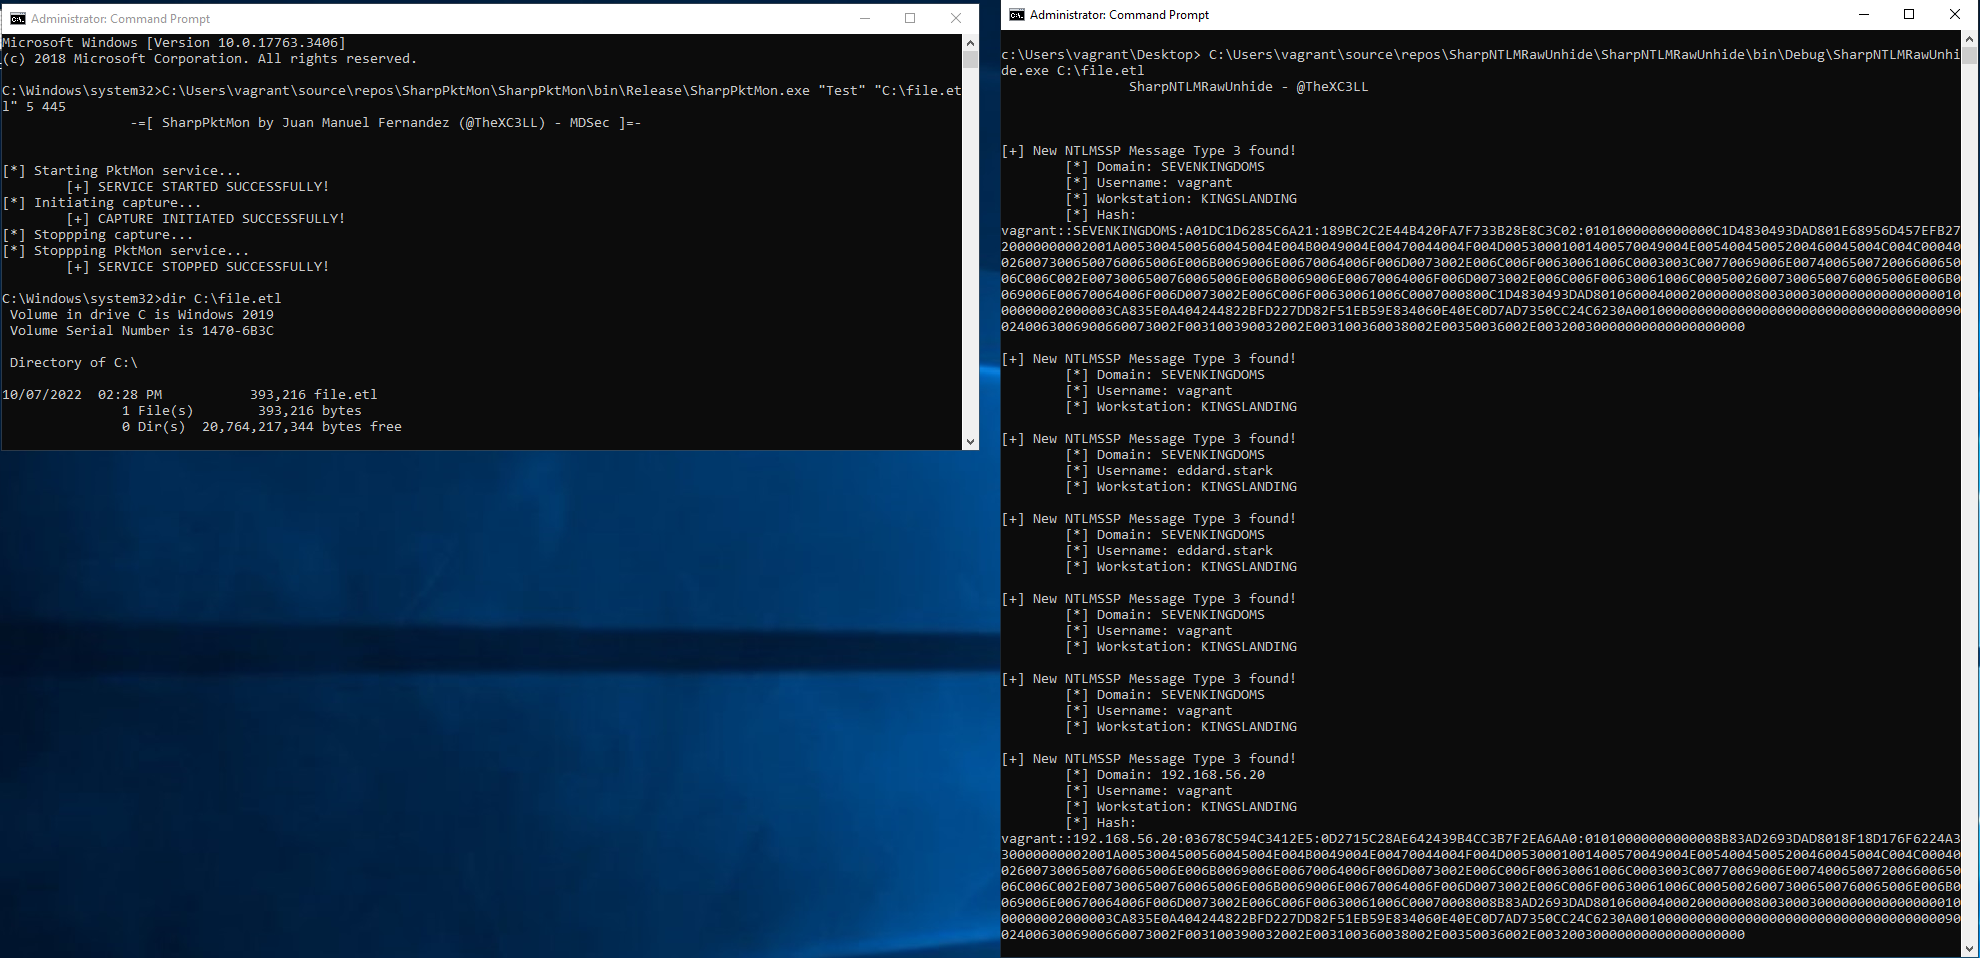 x-c3ll/sharpntlmrawunhide
C# version of NTLMRawUnHide
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 leftp/dpapisnoop
A C# tool to output crackable DPAPI hashes from user MasterKeys
 squiblydoo/certreport
A tool to support the reporting of Authenticode Certificates by reducing the effort on individuals to report.
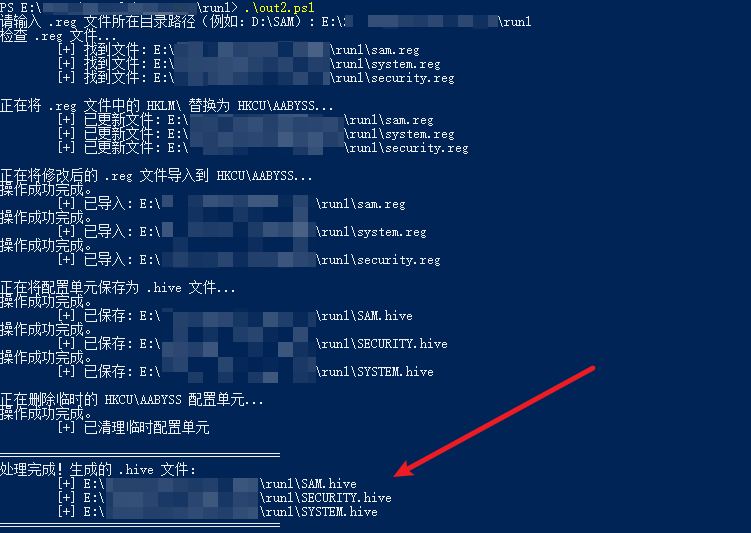 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
 mbadanoiu/artemis2hashcat
Python3 implementation for converting Artemis PBKDF2WithHmacSHA1 hashes to hashcat format
 nccgroup/hashcrack
Guesses hash types, picks some sensible dictionaries and rules for hashcat
 1an0rmus/tekdefense-automater
Automater - IP URL and MD5 OSINT Analysis
 coalfire-research/doozer
Password cracking utility
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 trustedsec/hate_crack
A tool for automating cracking methodologies through Hashcat from the TrustedSec team.