
BLAKE3
 blake3-team/blake3
Fast cryptographic hash function with PRF, MAC, KDF, and XOF modes. Supports verified streaming, incremental updates, and parallelized hashing via…
cryptographyencryption-decryption-toolshash-analysis
6.4k10 days ago
blake3-team/blake3Fast cryptographic hash function with PRF, MAC, KDF, and XOF modes. Supports verified streaming, incremental updates, and parallelized hashing via…
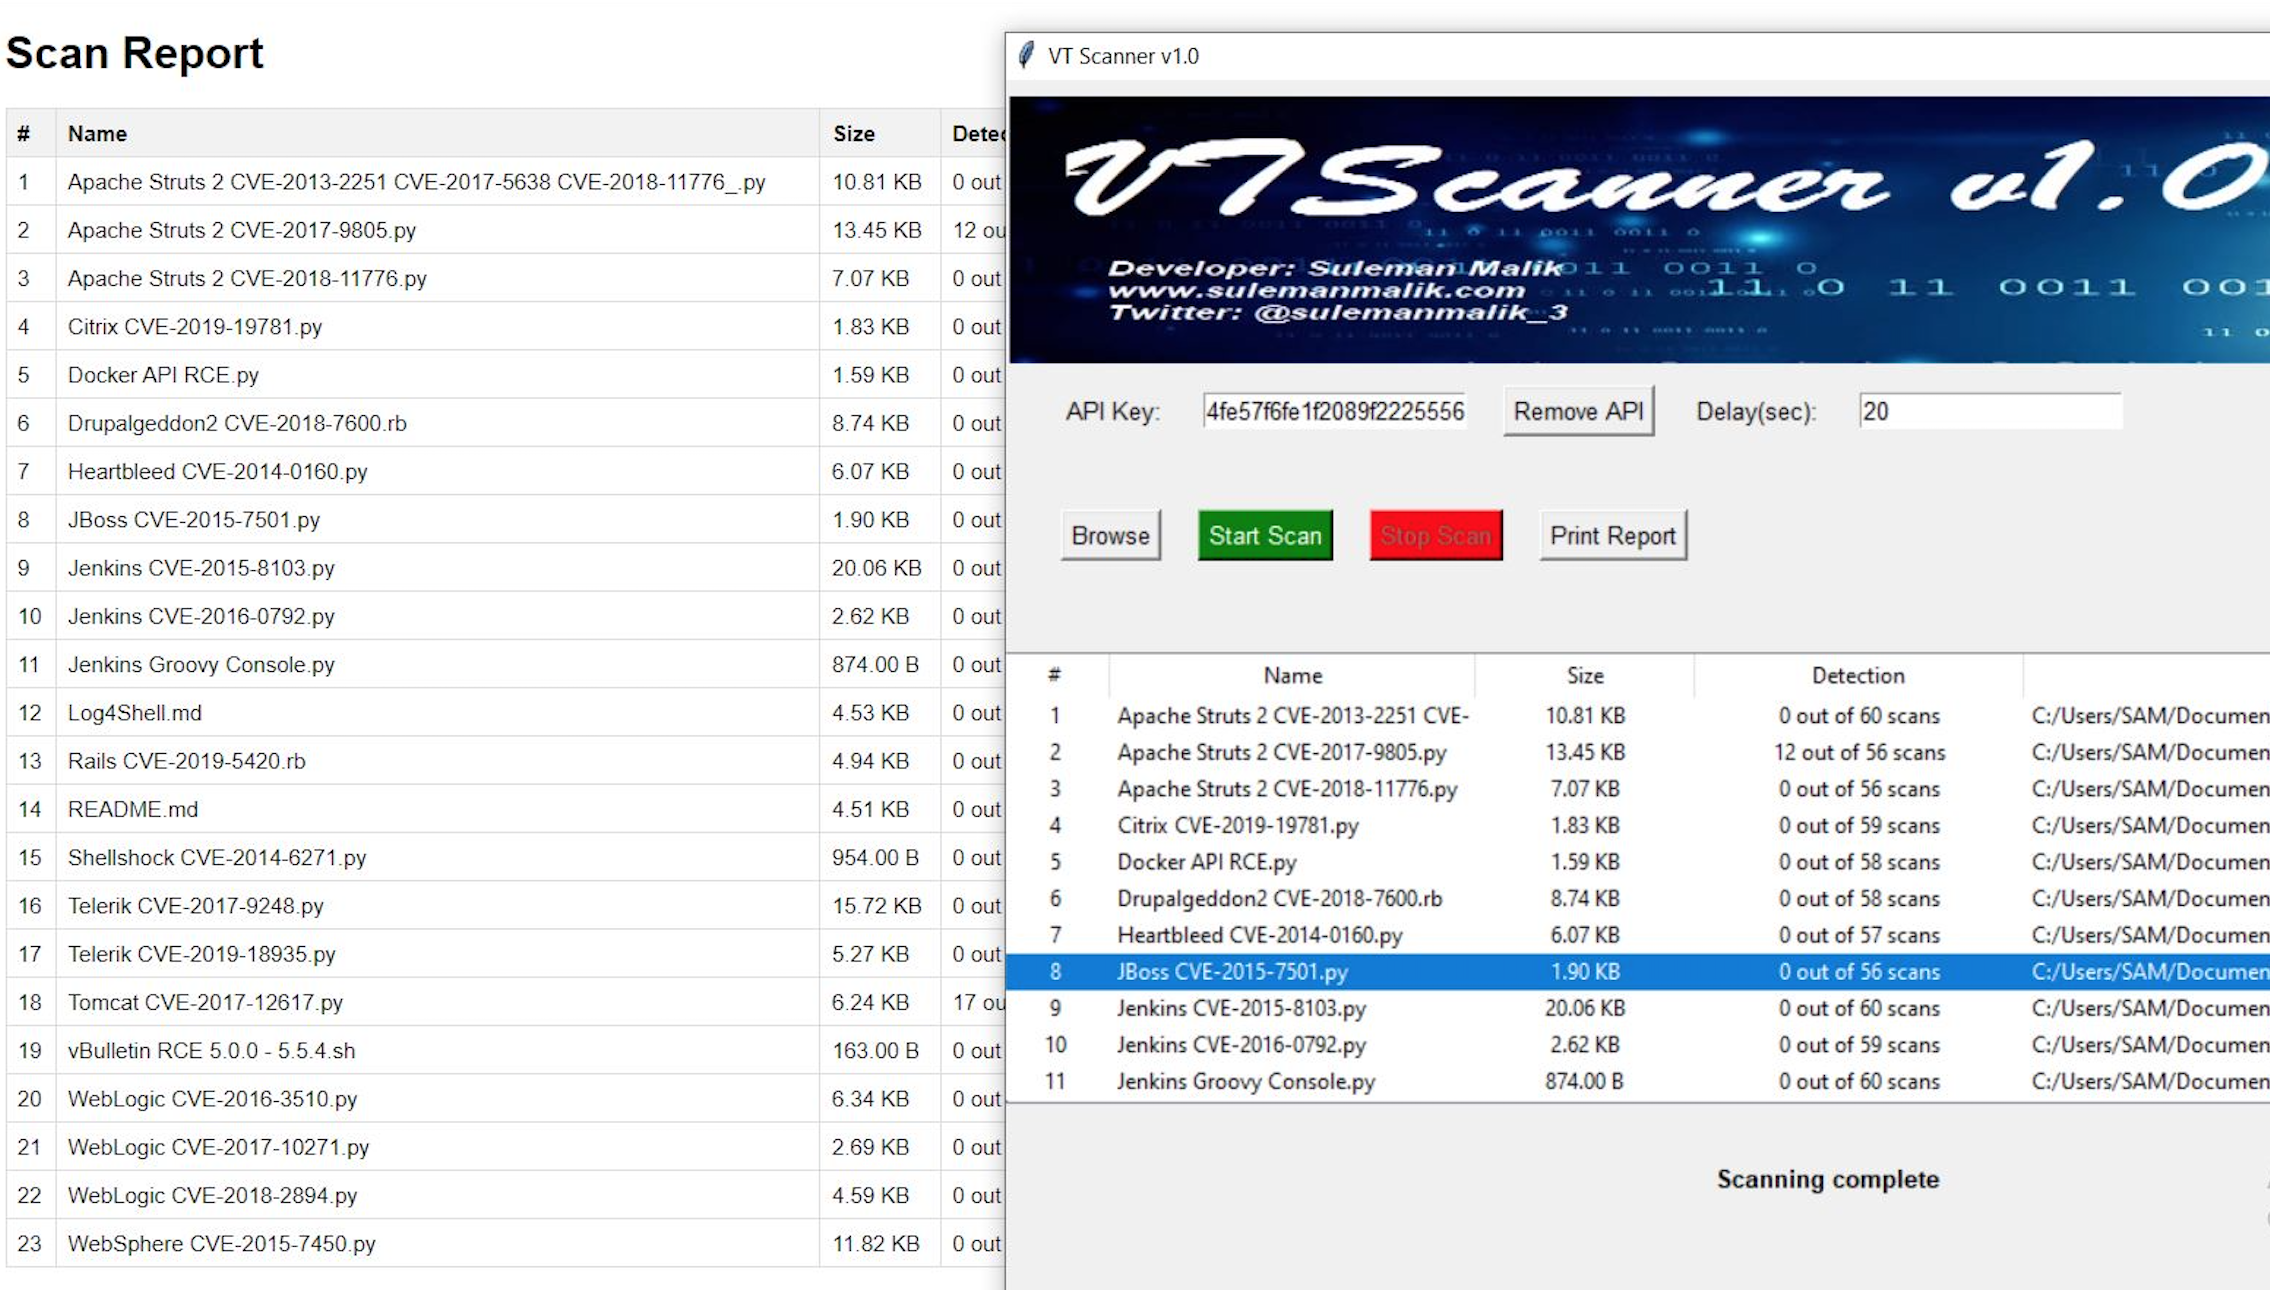 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
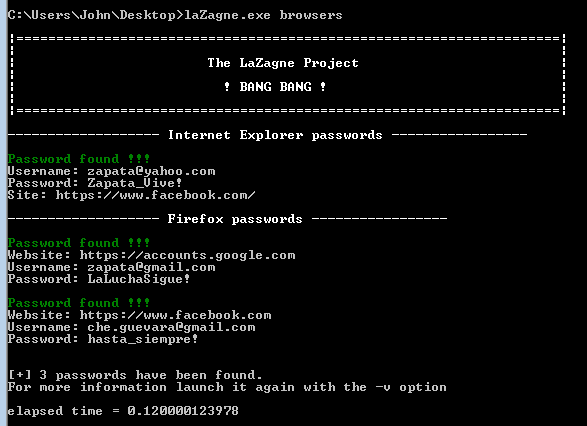 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
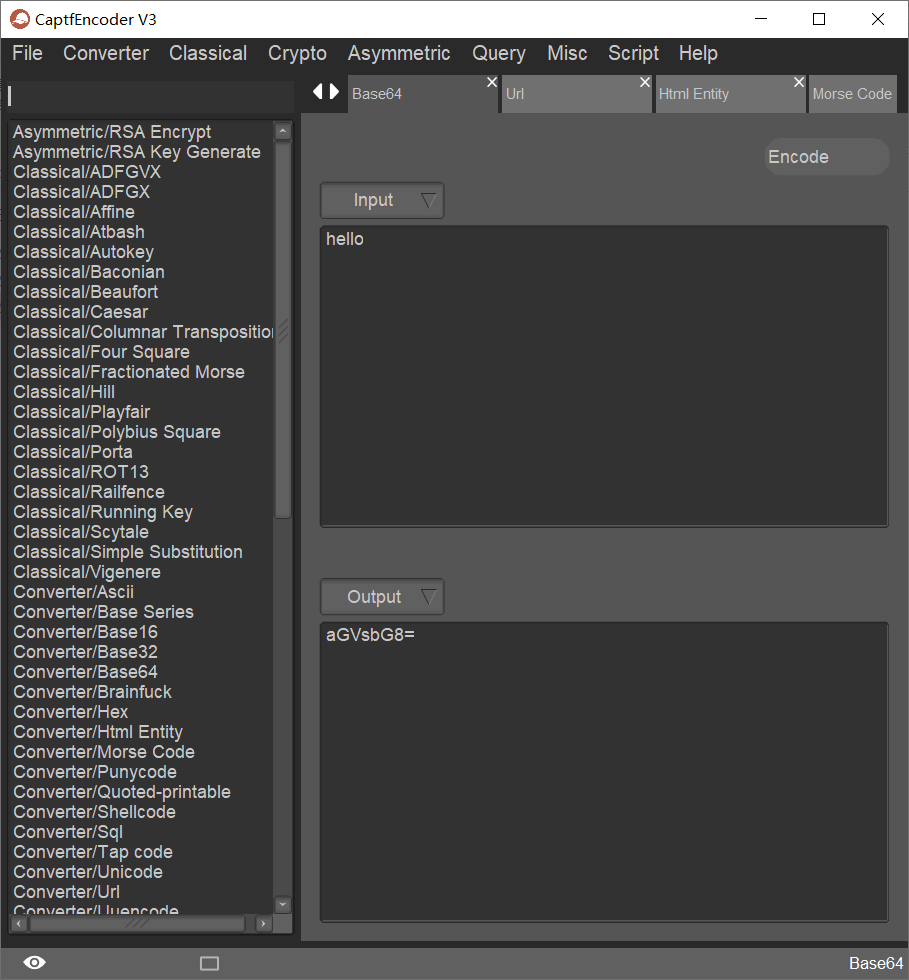 guyoung/captfencoder
Cross-platform security toolkit for encoding, classical and modern cryptography, hash computation, and online reconnaissance queries, designed for…
 hashcat/hashcat
World's fastest and most advanced password recovery utility
 badkeys/badkeys
Tool to find common vulnerabilities in cryptographic public keys
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 0chencc/ctfcracktools
The next-generation CTF Swiss Army Knife powered by Rust & Tauri. Features a visual node-based workflow and local AI intelligence for extreme…
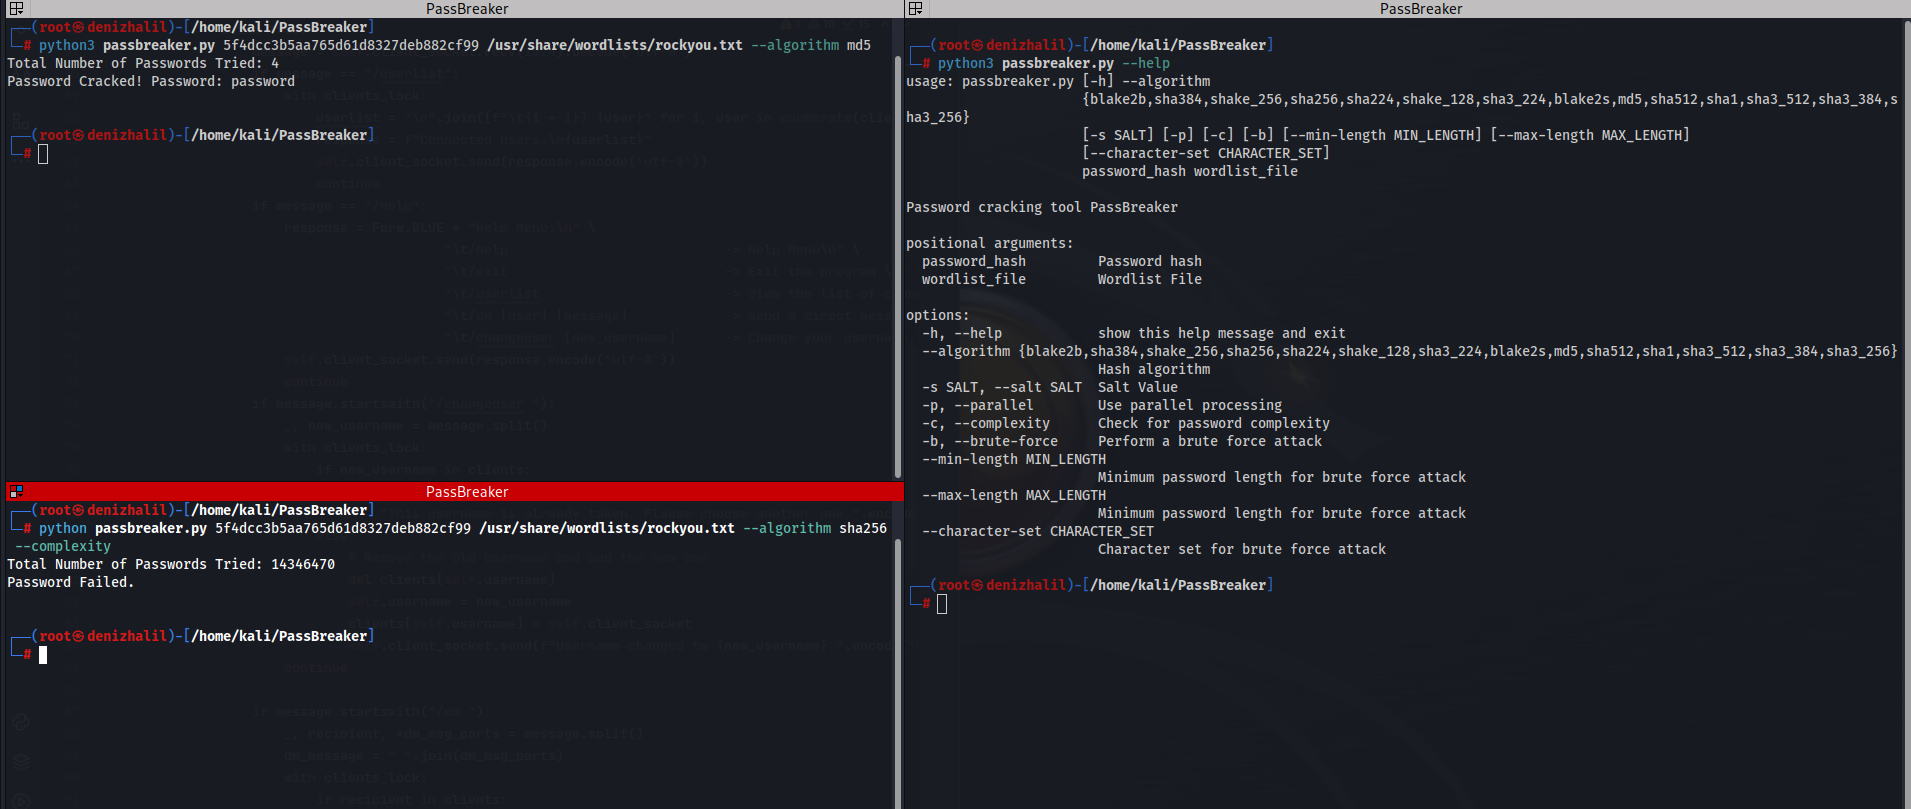 halildeniz/passbreaker
Python-based password cracker supporting wordlist and brute-force attacks with multiple hash algorithms, salt, parallel processing, and password…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
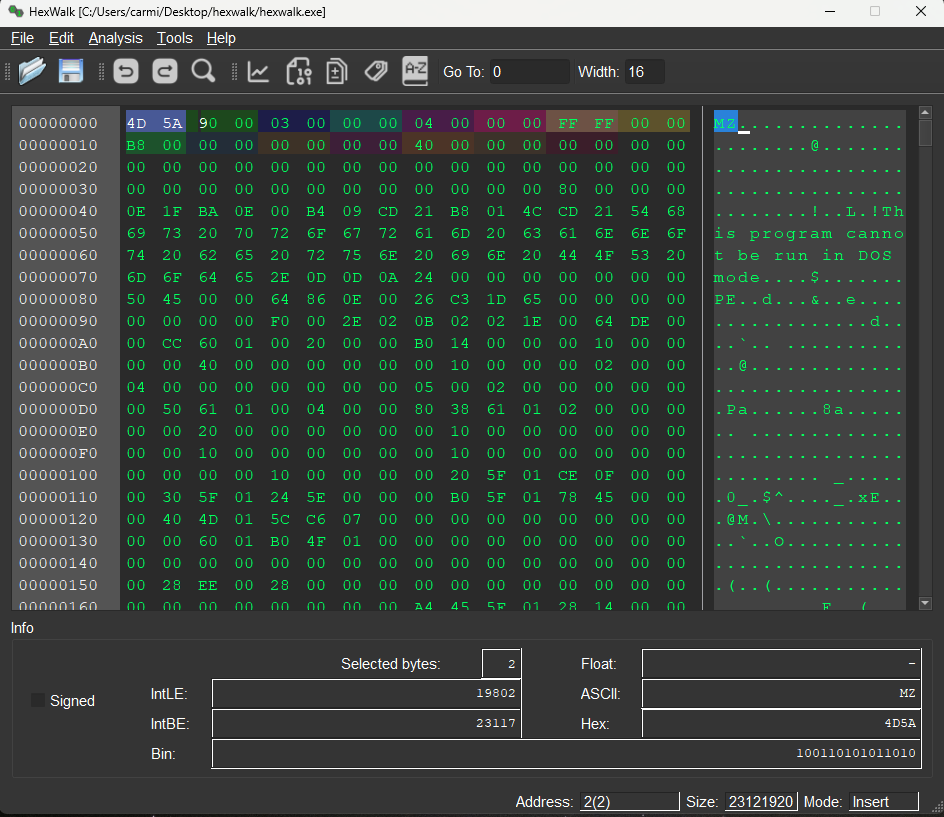 gcarmix/hexwalk
Hex Viewer/Editor/Analyzer compatible with Linux/Windows/MacOS
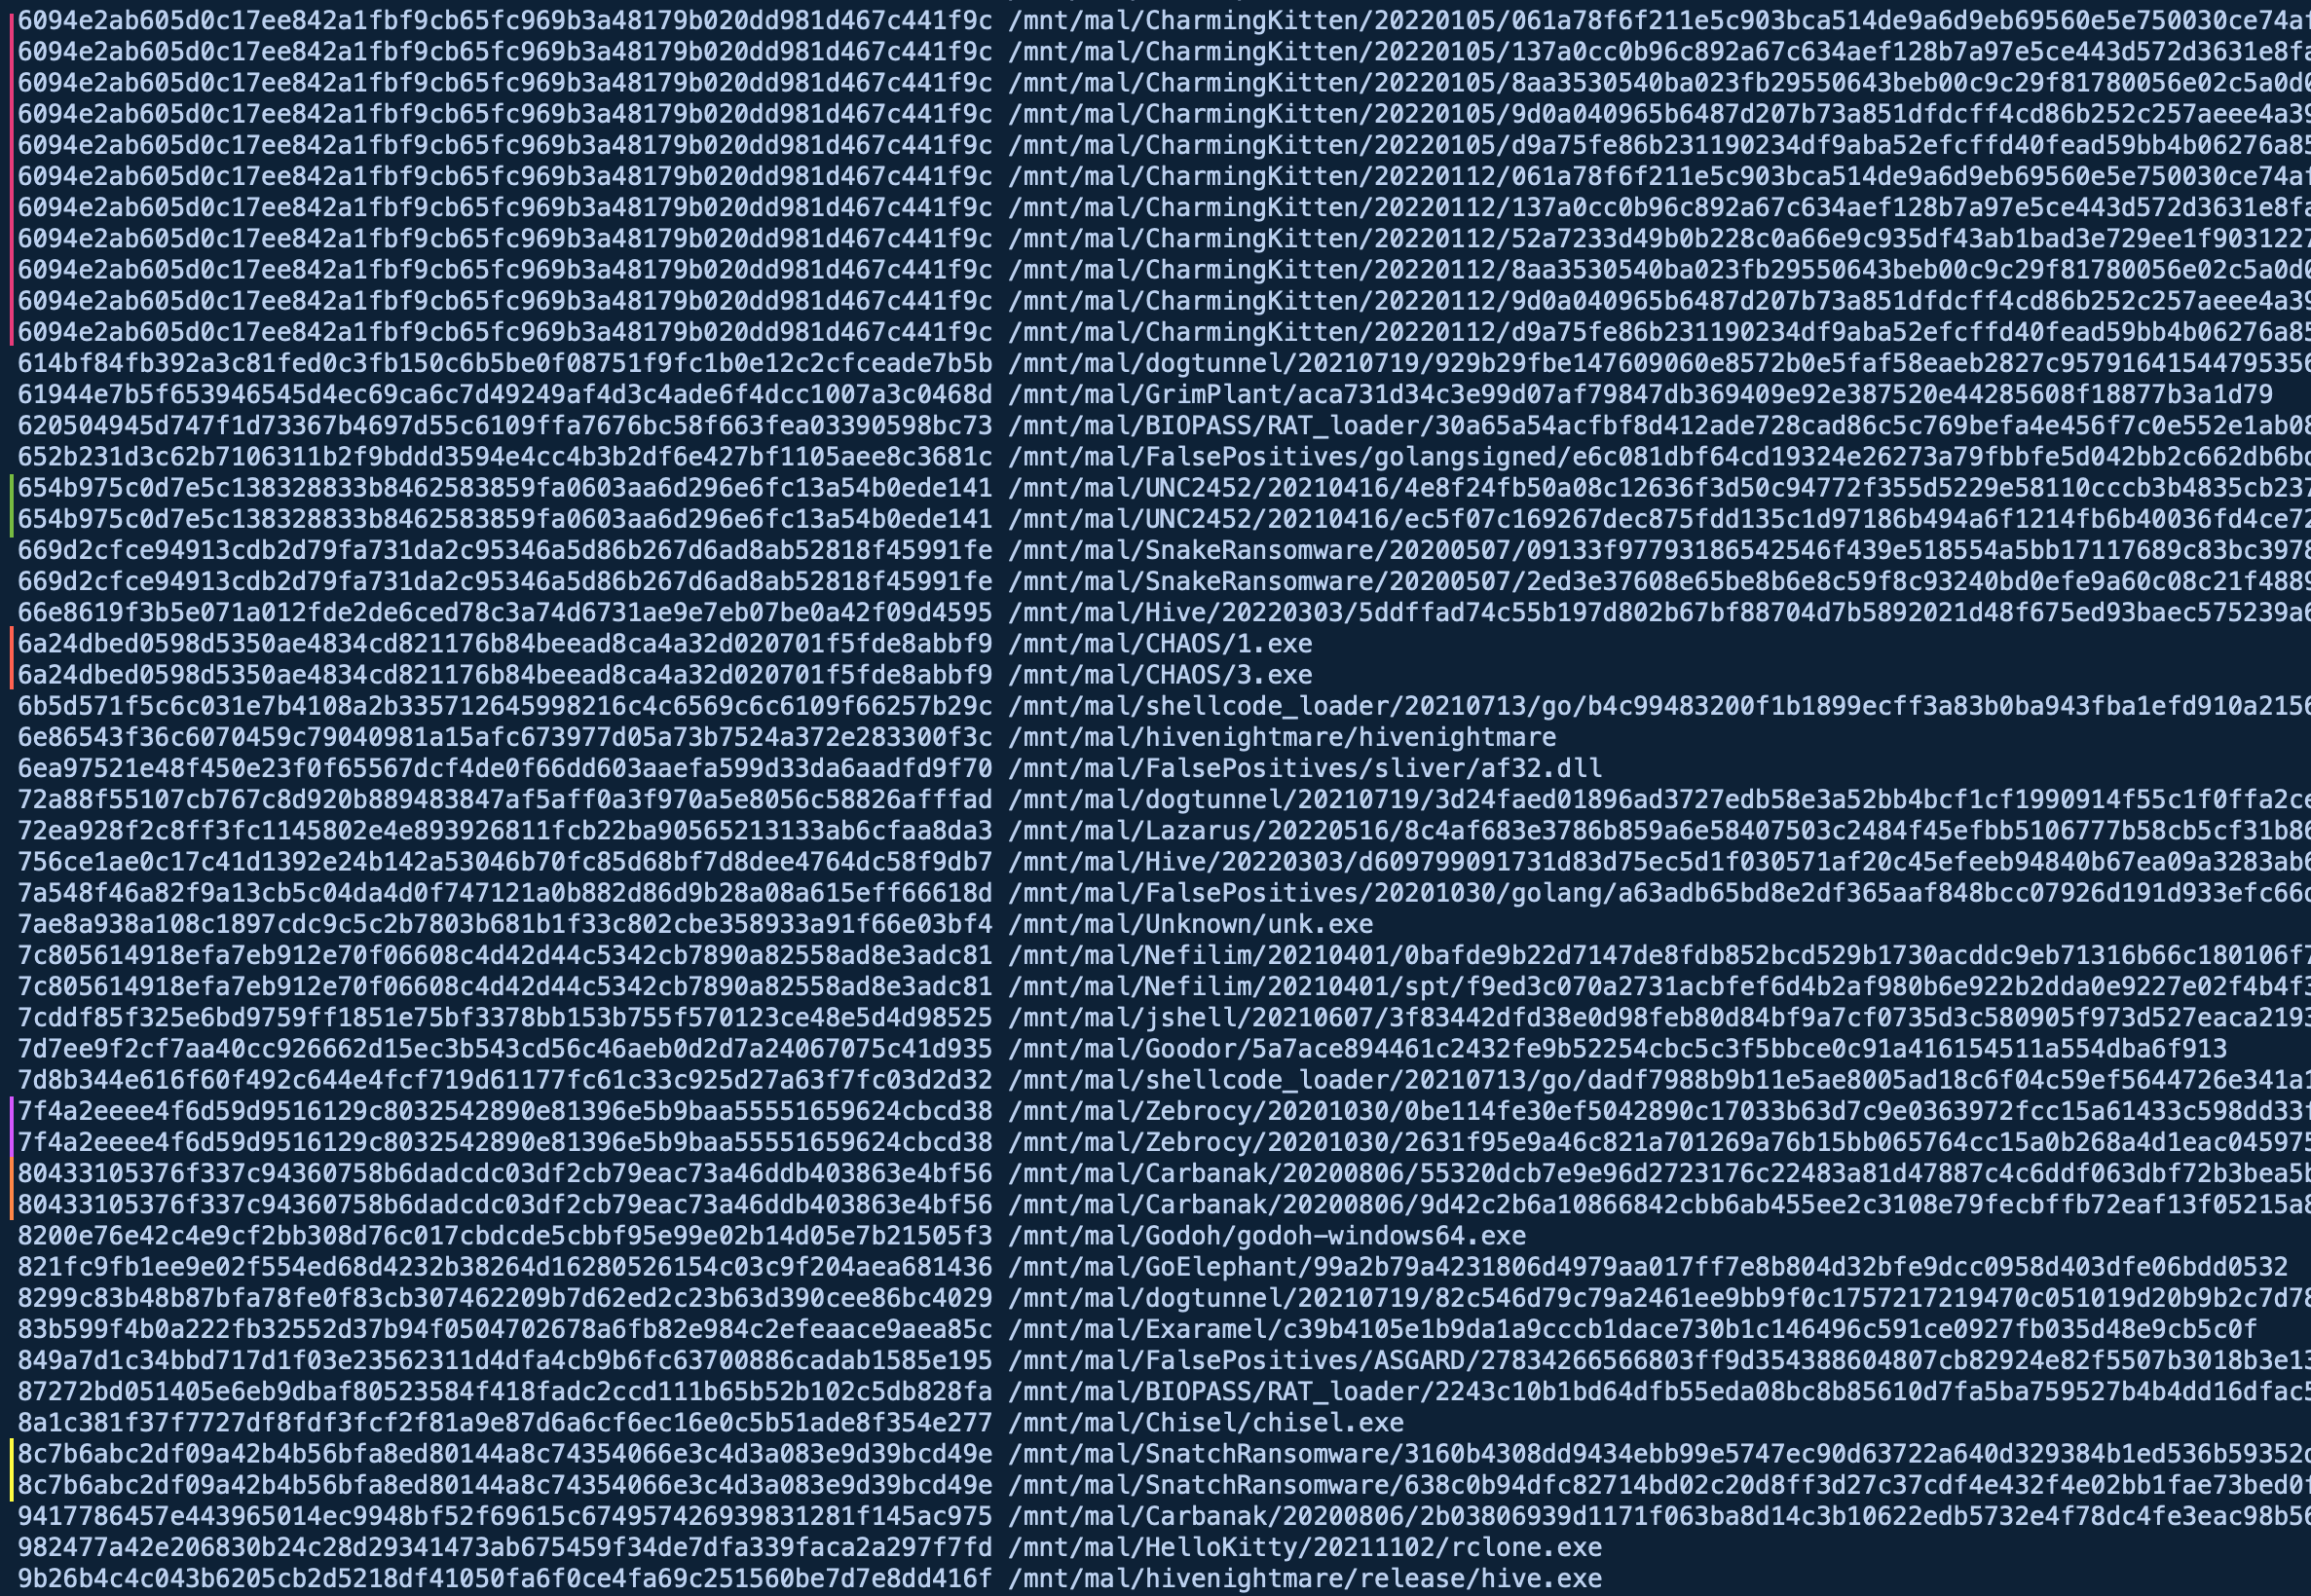 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 luisgg/ophcrack
Windows password cracker using time-memory trade-off with rainbow tables. Supports LM and NT hashes via GUI on Windows, macOS, and Linux.
 helich0pper/karkinos
Penetration Testing and Hacking CTF's Swiss Army Knife with: Reverse Shell Handling - Encoding/Decoding - Encryption/Decryption - Cracking Hashes /…