

DeadMatter
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
data-recoverydigital-forensicsforensics+7
qsecure-labs/deadmatterOffset Independent Credential Extraction Tool
 psypanda/hashid
Software to identify the different types of hashes -
 adamwhitehat/judge-jury-and-executable
A file system forensics analysis scanner and threat hunting tool. Scans file systems at the MFT and OS level and stores data in SQL, SQLite or CSV.…

 password123456/malwarescanner
Hash-based malware scanner for incident response. Scans files recursively using known malware hashes, supports multithreading, extension filtering,…
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
 netspooky/inhale
A malware analysis and classification tool.
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
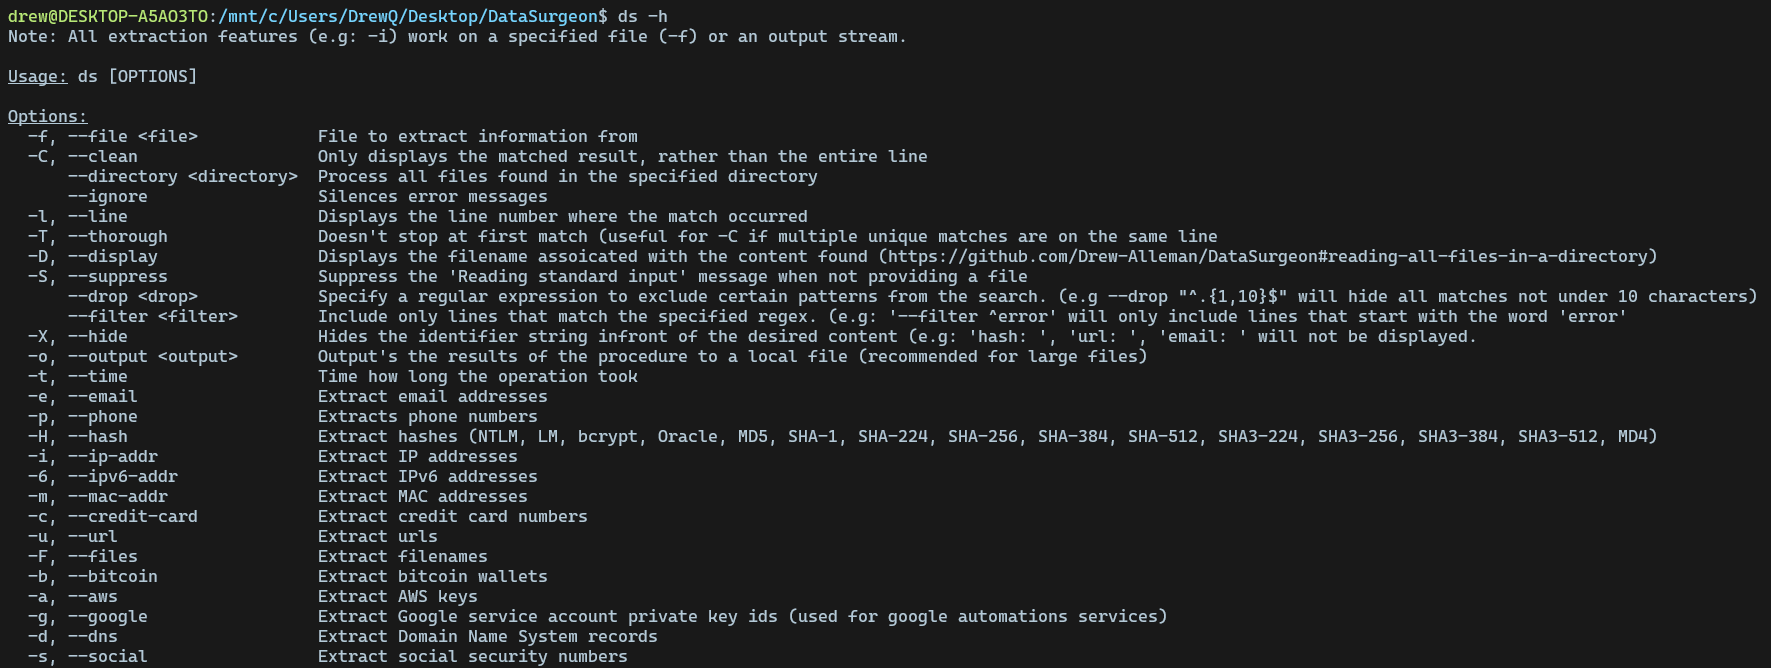 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
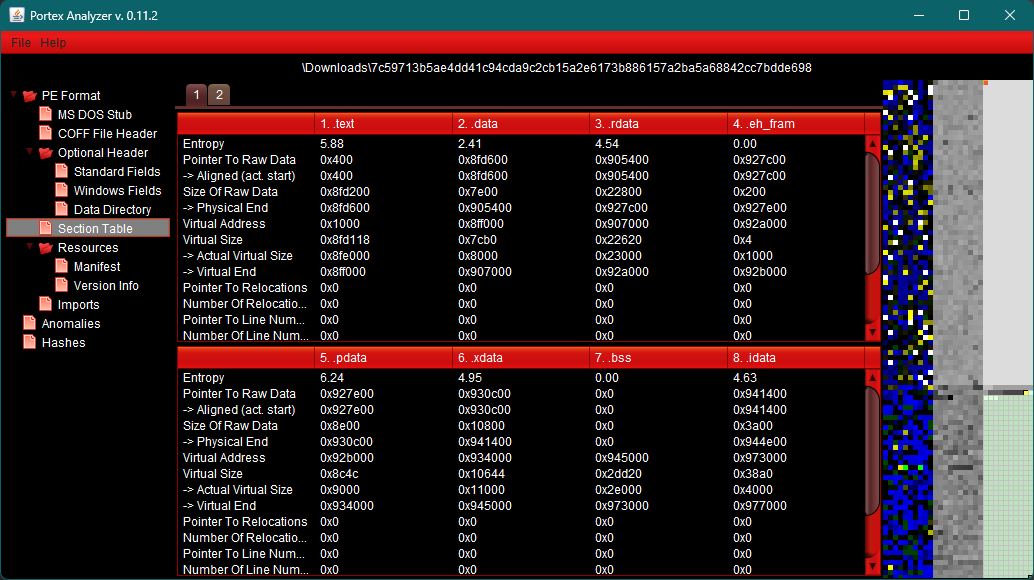 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.