
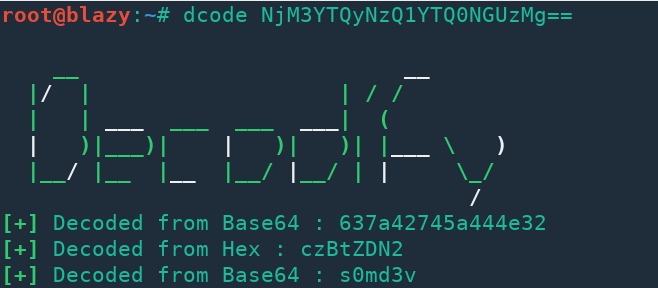
Decodify
 s0md3v/decodify
Detect and decode encoded strings, recursively.
cryptographygeneral-purpose-utilitieshash-analysis
s0md3v/decodifyDetect and decode encoded strings, recursively.
 brannondorsey/naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…
 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
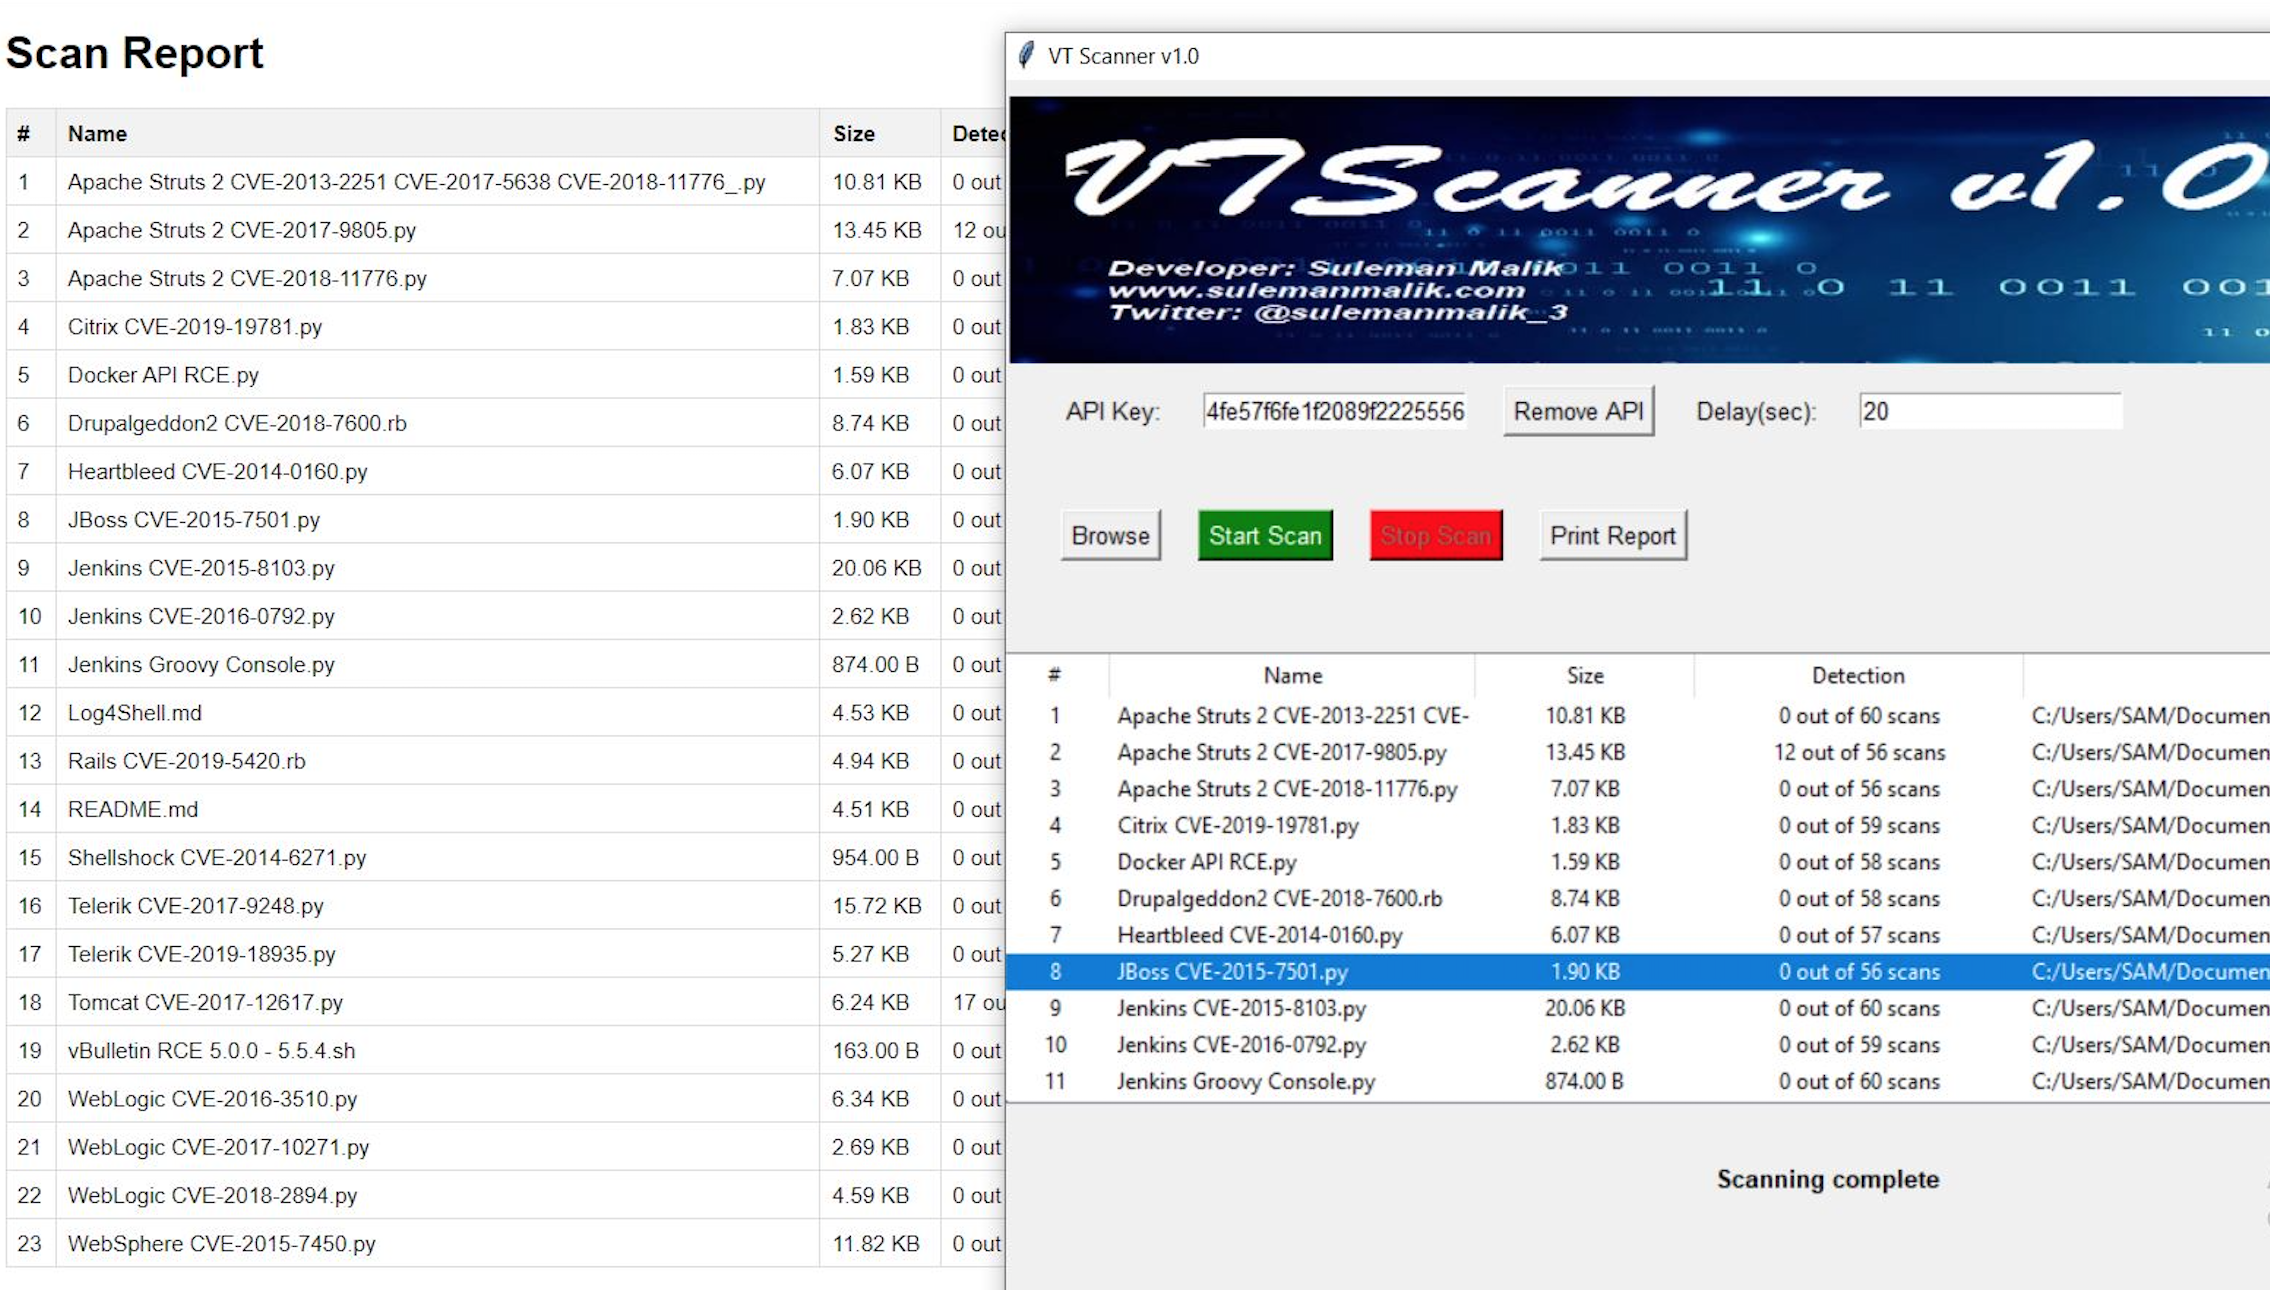 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 jedisct1/libsodium
A modern, portable, easy to use crypto library.
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
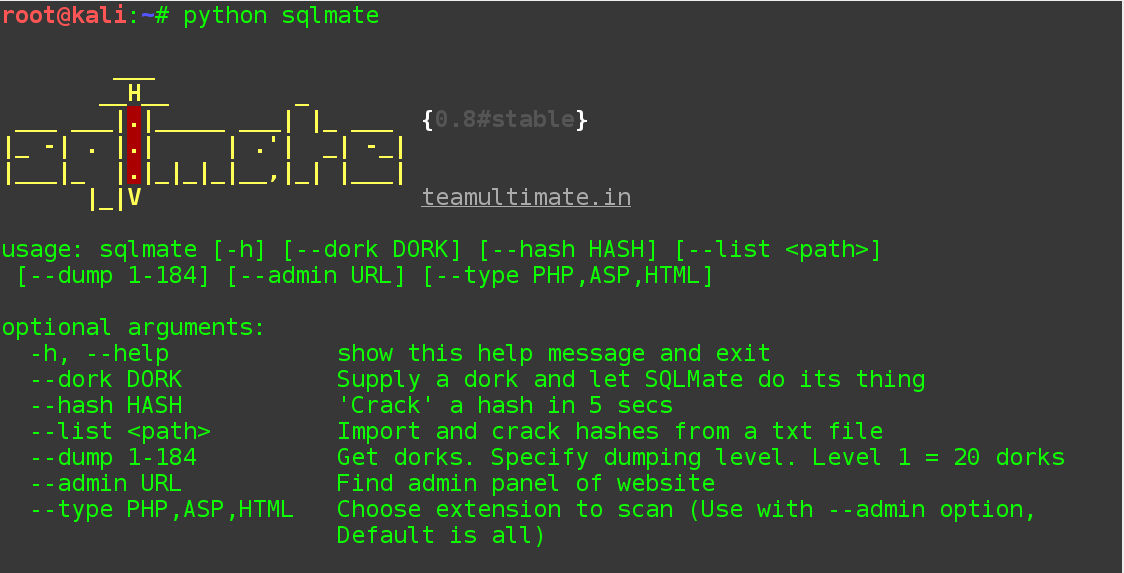 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
 heroku/terrier
Terrier is a Image and Container analysis tool that can be used to scan Images and Containers to identify and verify the presence of specific files…
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
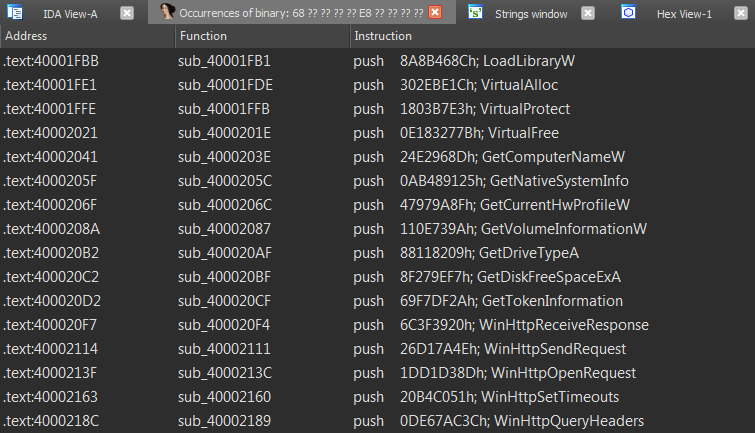 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 aide/aide
File integrity monitoring tool that detects unauthorized changes to monitored files and directories using attribute checks, multiple hash algorithms,…
 hashcat/hashcat-utils
Small utilities that are useful in advanced password cracking
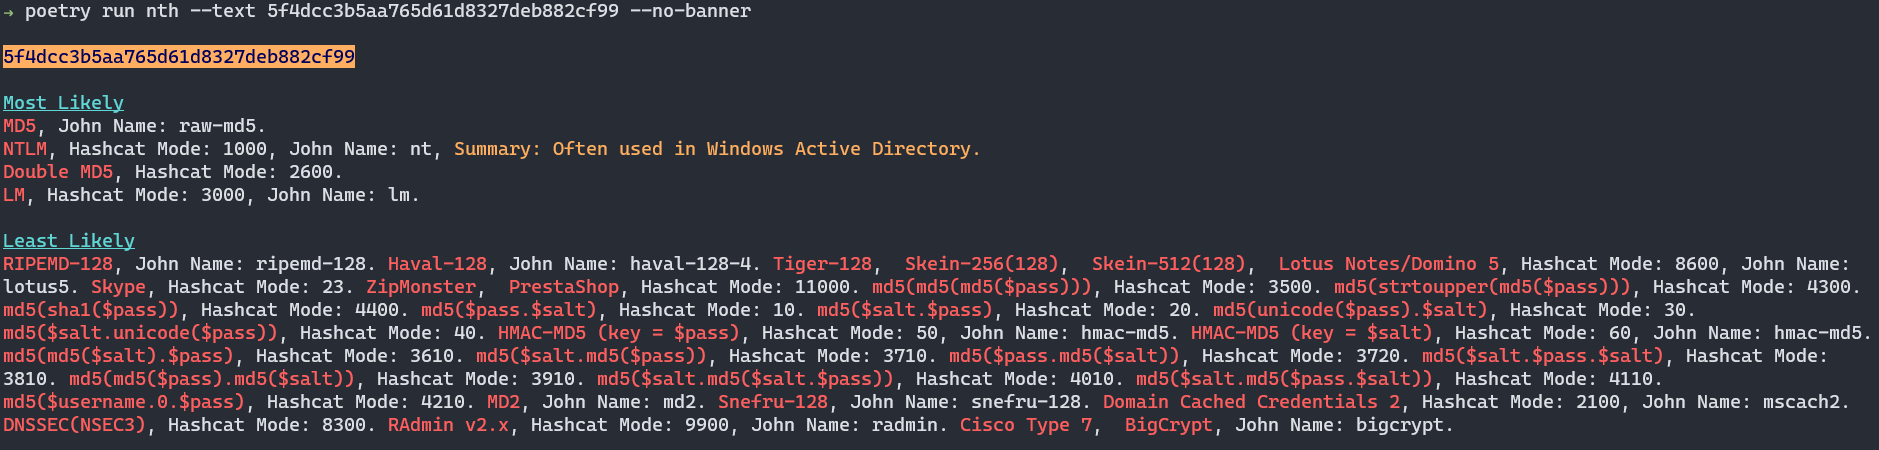 bee-san/name-that-hash
Identify 300+ hash types instantly via CLI or web app. Prioritizes popular hashes, provides summaries, and integrates with HashCat and John the…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 netspooky/inhale
A malware analysis and classification tool.