

 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 umbertodellamonica/linksys-wrt54gl-exploitation
From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)
 infobyte/nec_aterm_tools
Extracts hardware random keys from NEC Aterm router firmware images and QR codes to generate valid passwords for gaining shell access.
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 chrisl0tus/cve-2023-34924
Proof-of-concept exploit for a buffer overflow vulnerability in H3C Magic B1STW router's SetAPInfoById function, causing web service crash and…
 alexoslabs/ipmitest
Shell script for testing the IPMI cipher type zero authentication bypass vulnerability (CVE-2013-4784)
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
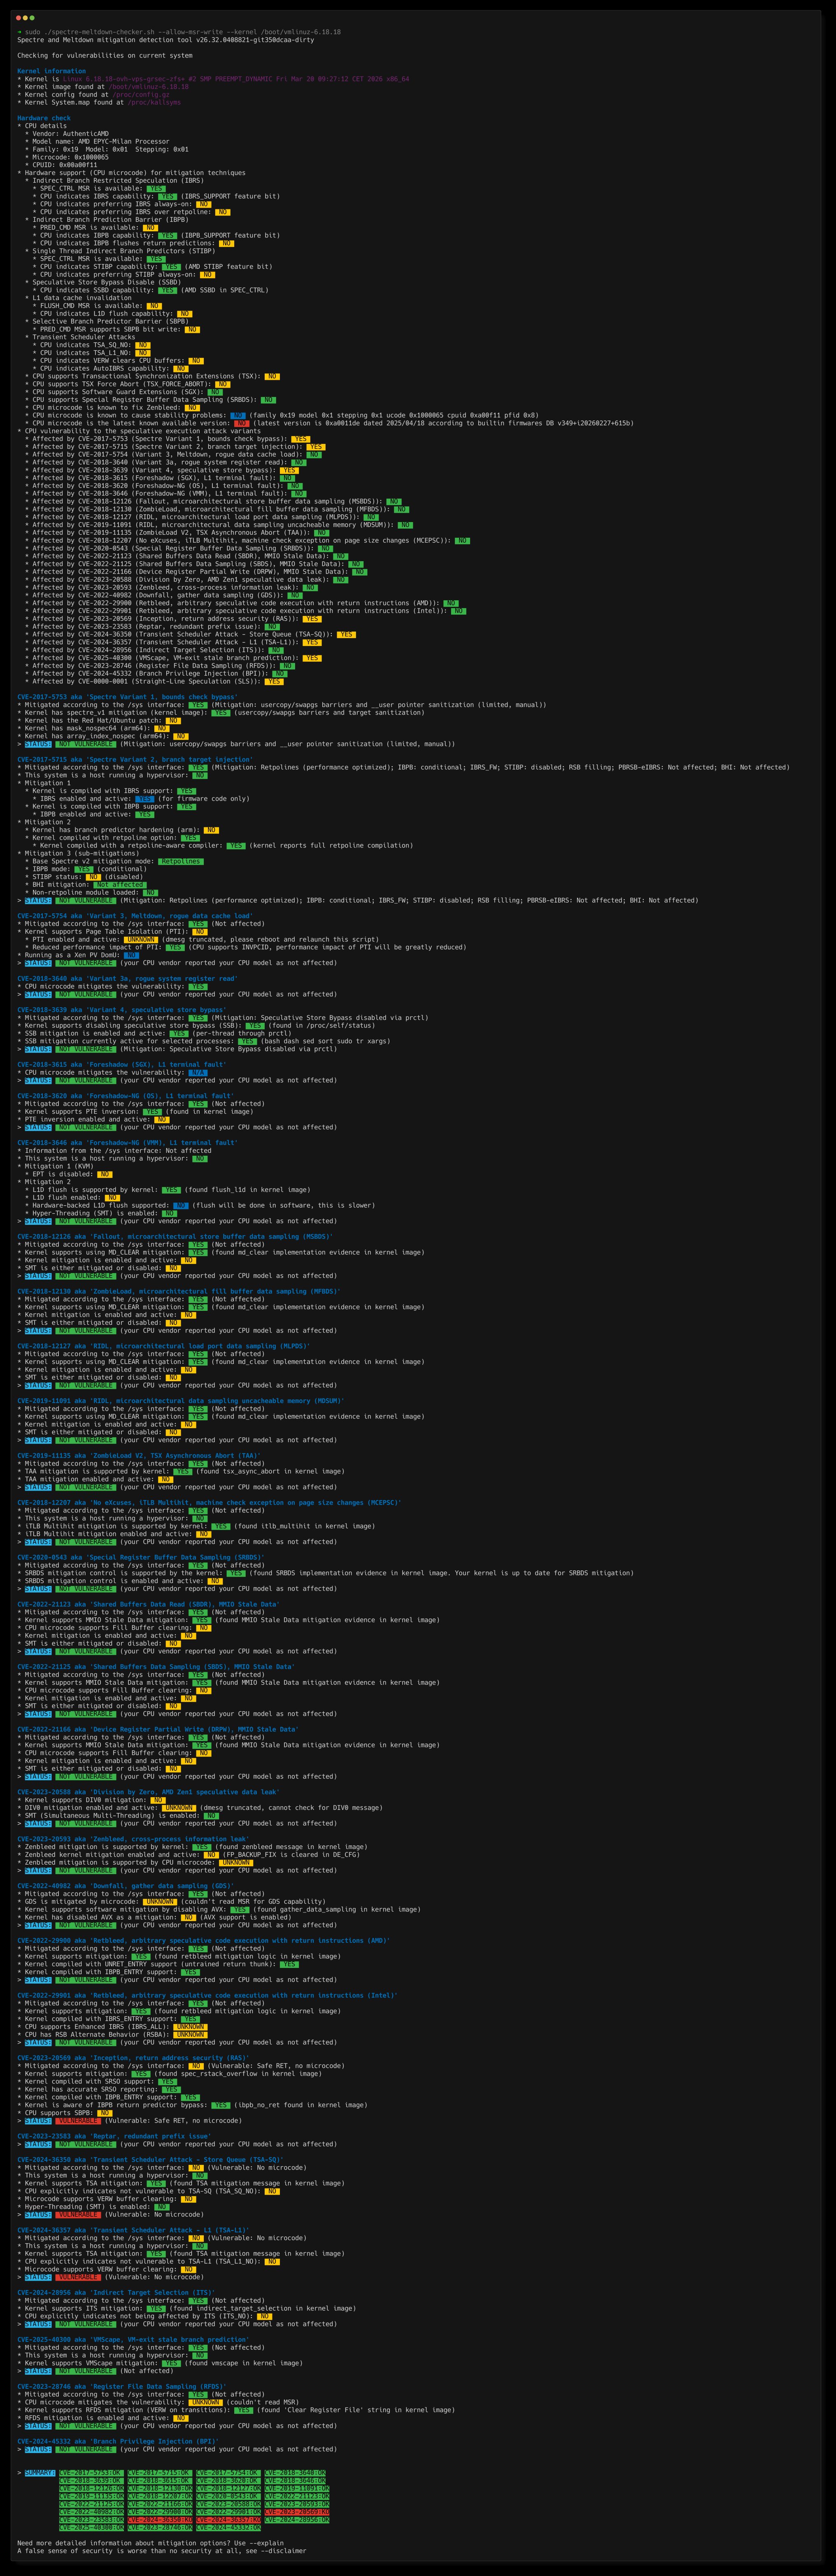 speed47/spectre-meltdown-checker
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
 cyberaz0r/gl.inet-multiple-vulnerabilities
Exploits for GL.iNet CVE-2023-46454, CVE-2023-46455 and CVE-2023-46456