

Driver-HWID-btbd-modified
 gmh5225/driver-hwid-btbd-modified
Modified btbd HWID spoofer kernel driver that can be manually mapped to evade anti-cheat detection on Windows 1909.
anti-botfingerprint-spoofinghardware-security
35 years ago
gmh5225/driver-hwid-btbd-modifiedModified btbd HWID spoofer kernel driver that can be manually mapped to evade anti-cheat detection on Windows 1909.
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
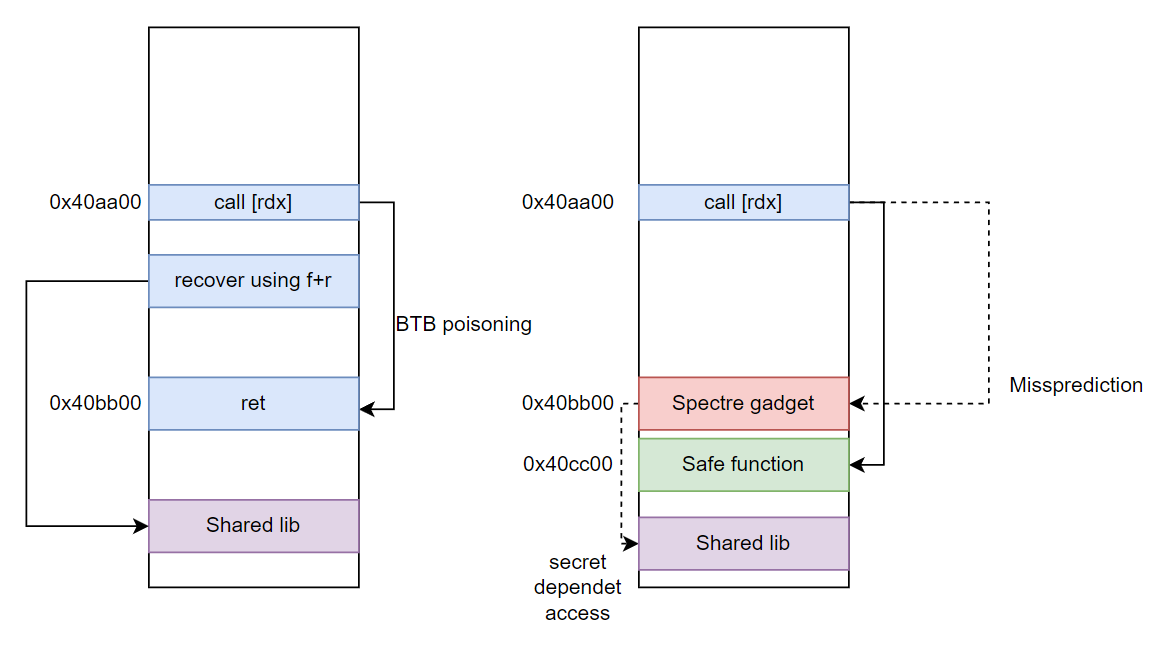 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
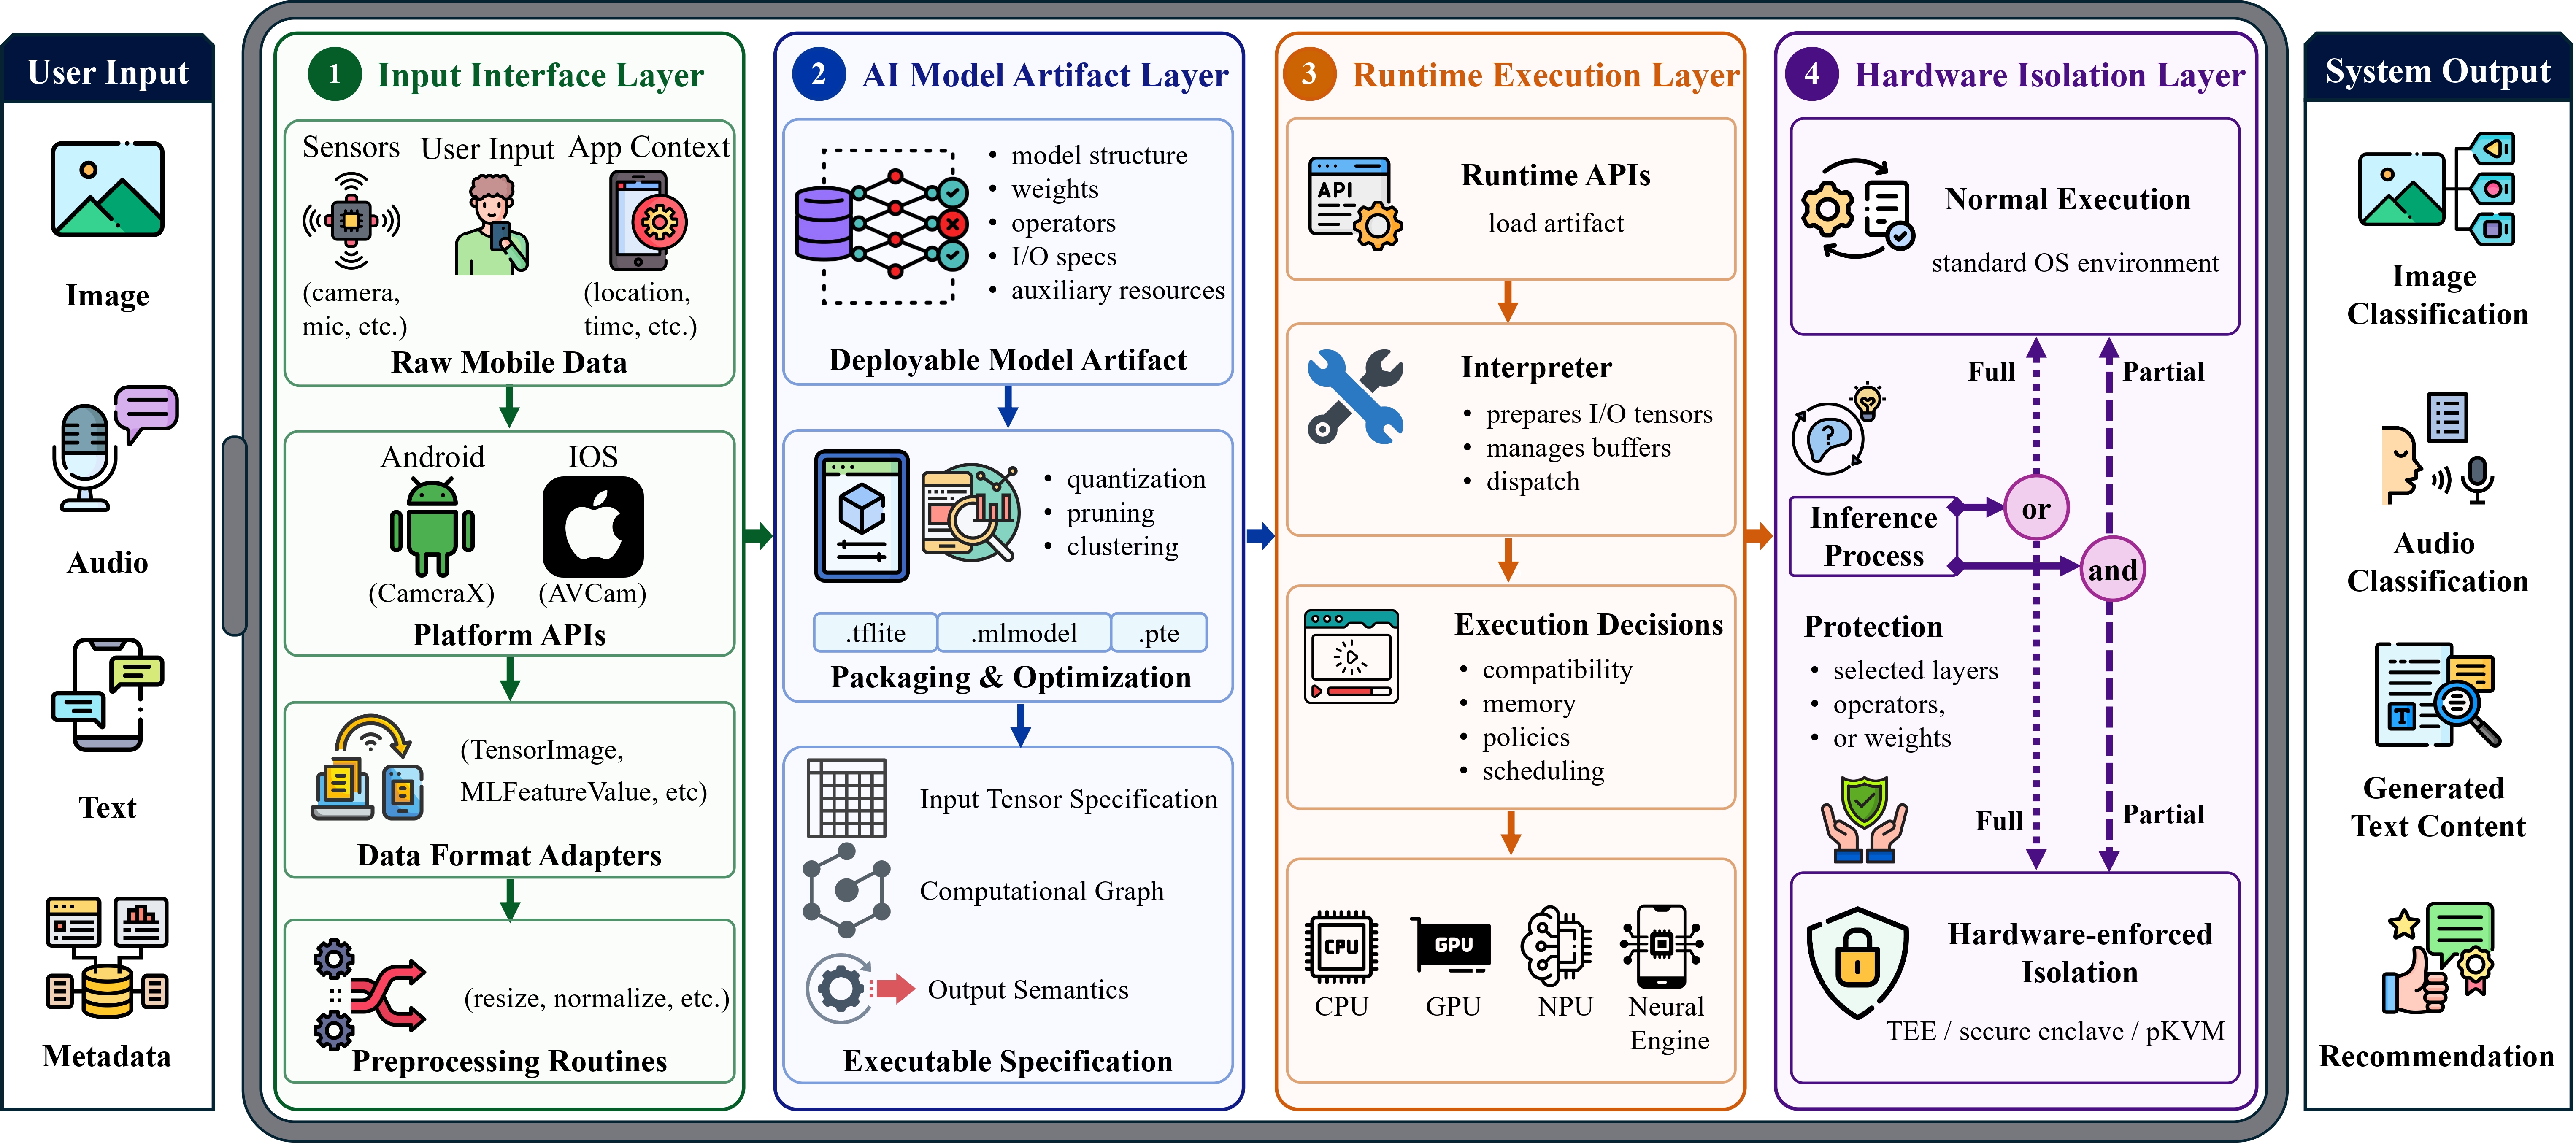 jinxhy/awesome-moai-security
Curated reading list and taxonomy of attack and defense research for mobile on-device AI systems, covering adversarial, backdoor, model stealing, and…
 spiralbl0ck/rowhammer-exploit
RowHammer Based-Exploit
 pmsosa/duckhunt
:dart: Prevent RubberDucky (or other keystroke injection) attacks
 valdikss/super-uefiinsecureboot-disk
Super UEFIinSecureBoot Disk: Boot any OS or .efi file without disabling UEFI Secure Boot
 idov31/novahypervisor
Windows hypervisor for Intel x64: defensive host hypervisor for Windows designed to mitigate kernel-level attacks including BYOVD, compatible with…
 antisurveillanceagency/shadownet
ShadowNet is an anonymous routing protocol that forces all connections (system-wide) to go through Tor while implementing Mixnet-like…