
CVE-2020-14974
 aterror2be/cve-2020-14974
A simple POC that demonstrates A vulnerability found in IObitUnlocker 1.1.2 that leverages IOCTL codes found it its vulnerable driver…
binary-exploitationexploitationhardware-security+2
7
aterror2be/cve-2020-14974A simple POC that demonstrates A vulnerability found in IObitUnlocker 1.1.2 that leverages IOCTL codes found it its vulnerable driver…
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
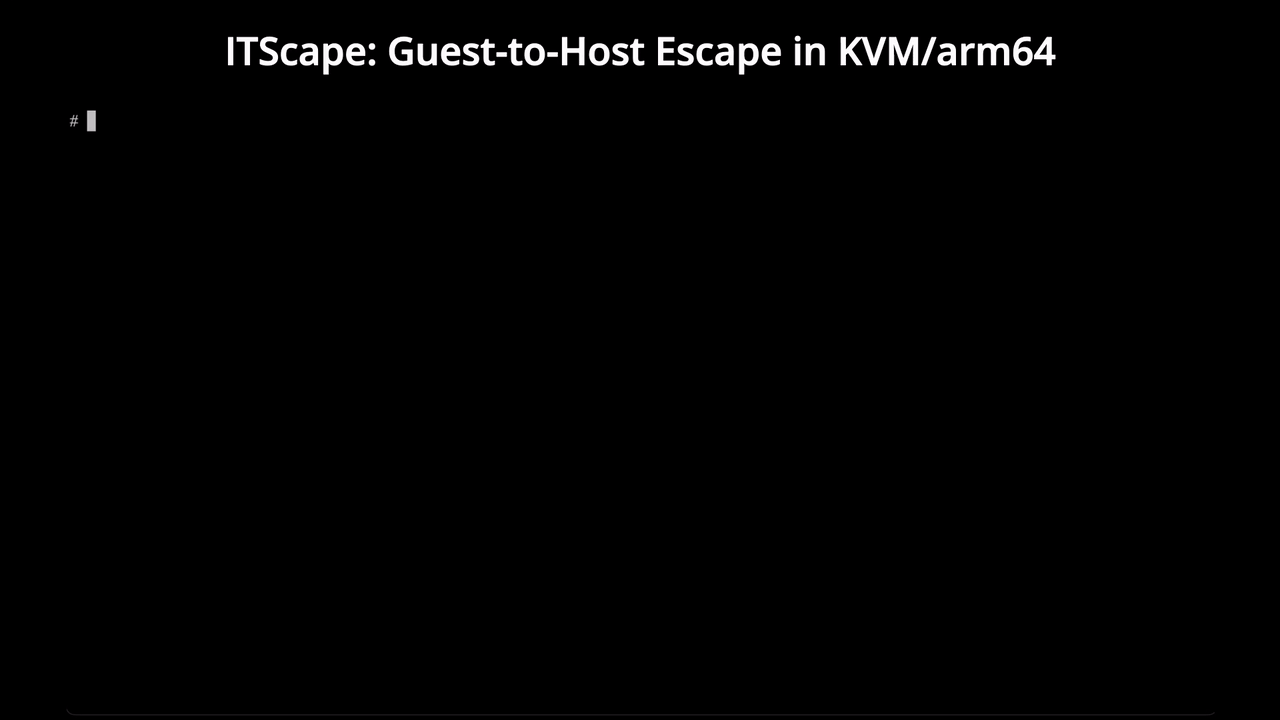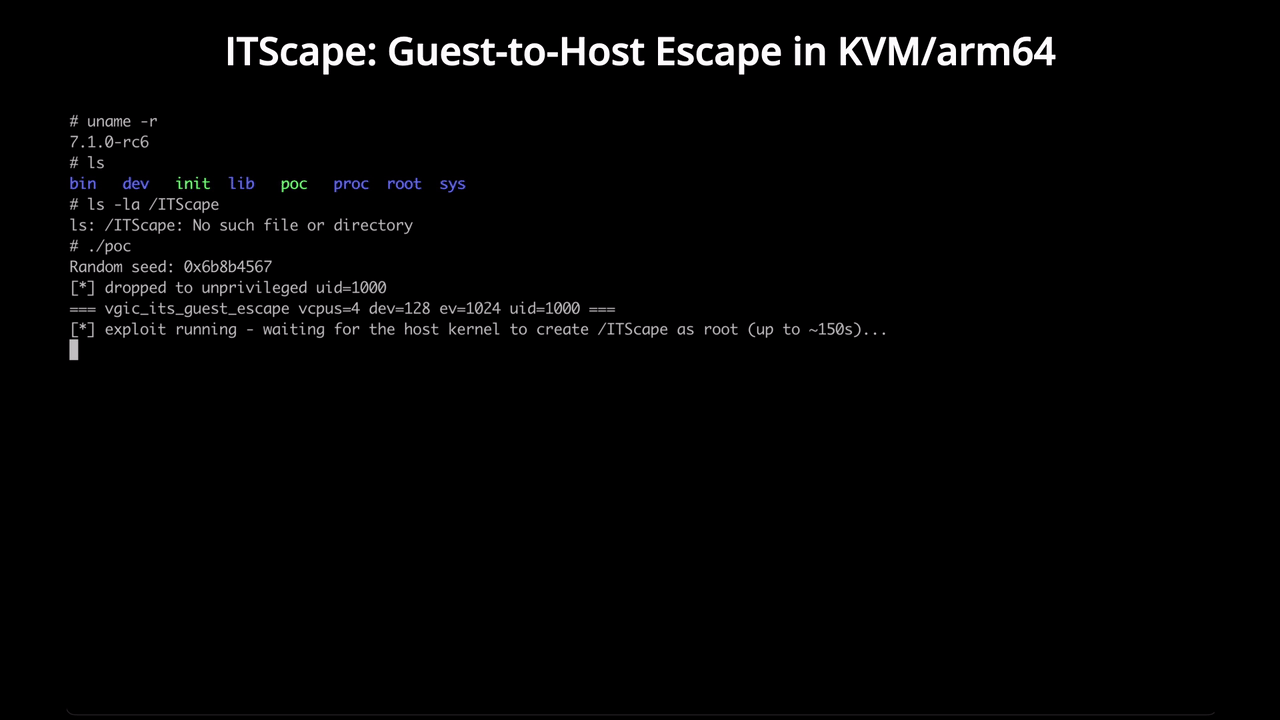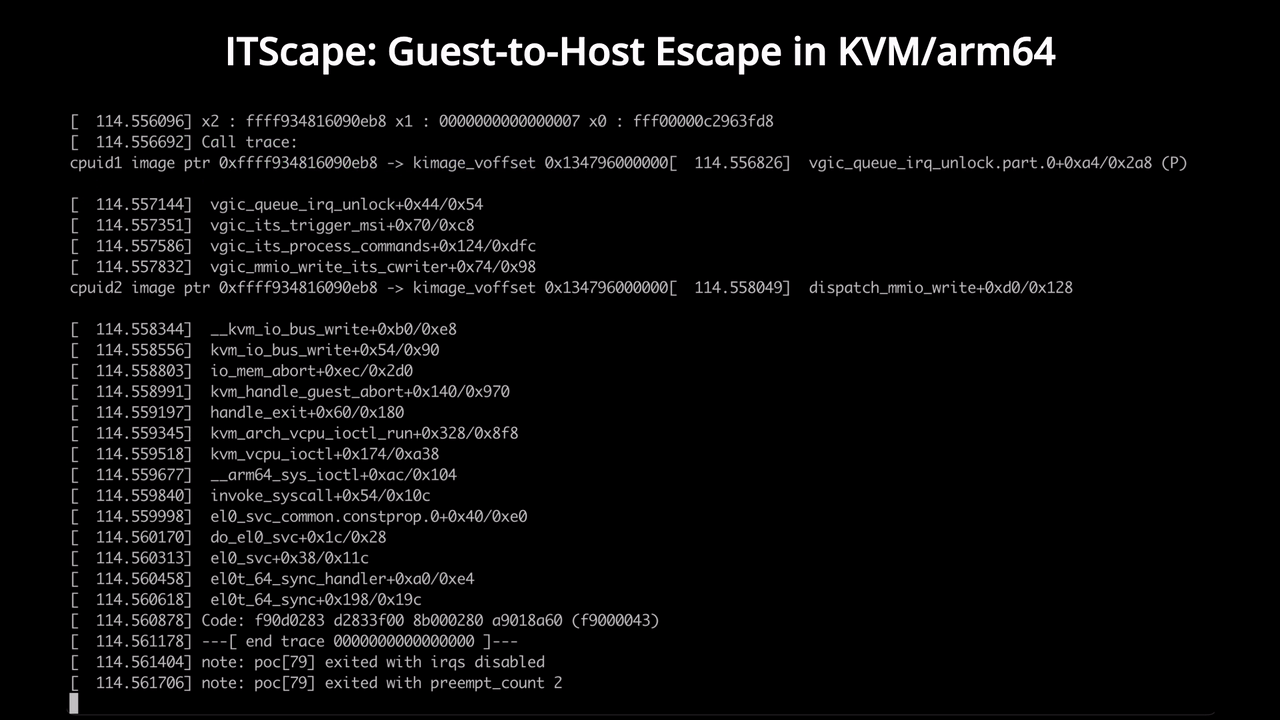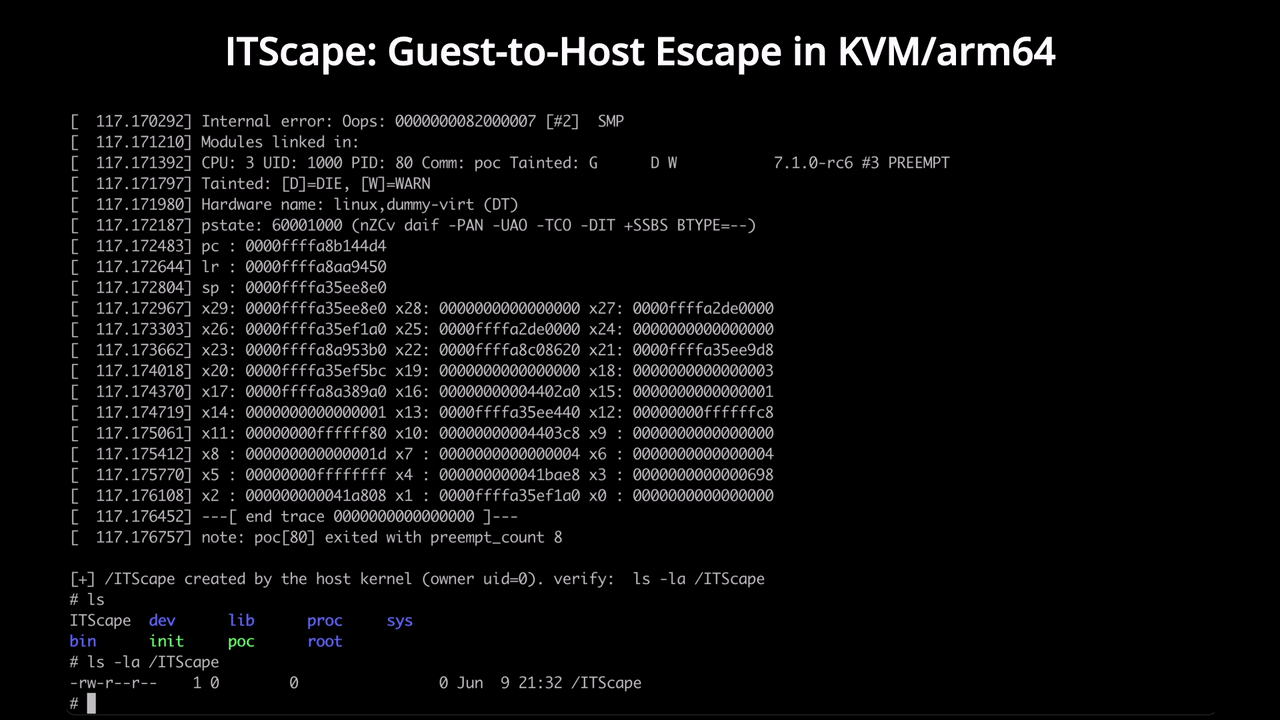 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 renorobert/virtualbox-cve-2018-2844
C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…
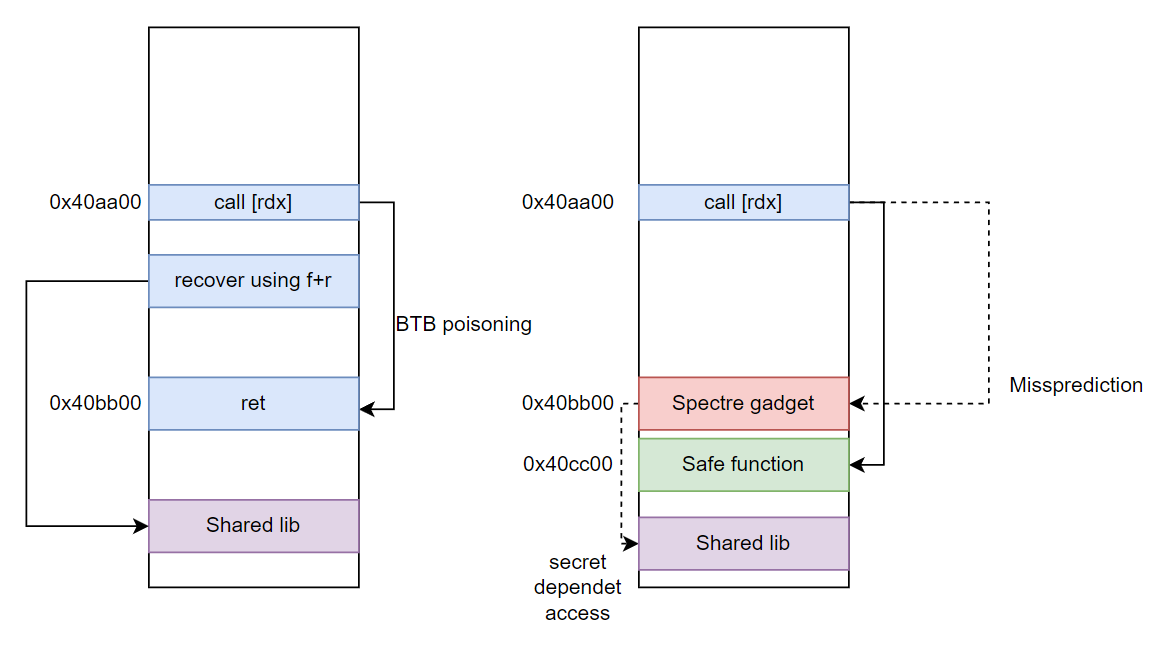 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 ch3rn0byl/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551 targeting Dell's dbutil_2_3 driver to achieve code execution on systems with HVCI disabled.
 shurikgo/cve-2026-25262-sm8450-research
CVE-2026-25262 applicability to Snapdragon 8 Gen 1 — experimental results
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…
 wzy114514sb/pwnage24mtk
Cert exploit for MTK devices.There is a logic flaw in MTK cert verification process.Similar to CVE-2023-20696.
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 jeromeyoung/cve-2021-40154
POC to test the BootROM vulnerability found in LPC55S69 and K82 Series
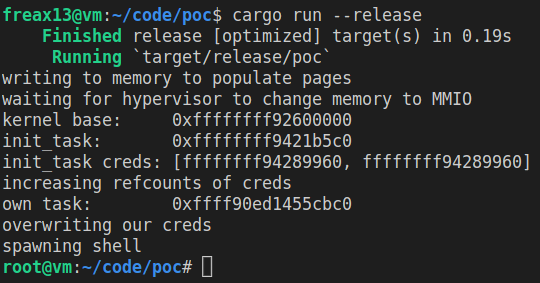 freax13/cve-2023-46813-poc
Proof-of-concept exploit for CVE-2023-46813 targeting AMD SEV-SNP. Escalates privileges by manipulating hypervisor memory type changes to swap task…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 retr0reg/tenda-ac8v4-rop
Exploits for Tenda Ac8v4 stack-based overflow to Remote-Code Execution via Mipsel Ropping (CVE-2023-33669 - CVE-2023-33675)
 0xcyberstan/cve-2026-53360-poc
PoC for CVE-2026-53360: guest-triggered heap out-of-bounds read/write in KVM SEV-SNP Page State Change (PSC) handling.
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
 killvxk/cve-2021-3972
Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.