
CVE-2024-53375
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
command-and-controlexploitationhardware-security+4
22
thottysploity/cve-2024-53375TP-Link Archer AXE75 Authenticated Command Injection
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 s-hamann/cve-2023-40289
Exploit for CVE-2023-40289, a command injection vulnerability in several Baseband Management Controllers (BMC) by with firmware by ATEN
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 yt2w/cve-2025-9961
Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 jackdoan/tp-link-archerc5-rce
CVE-2018-19537
 bertoldvdb/pcanexploit
CVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways
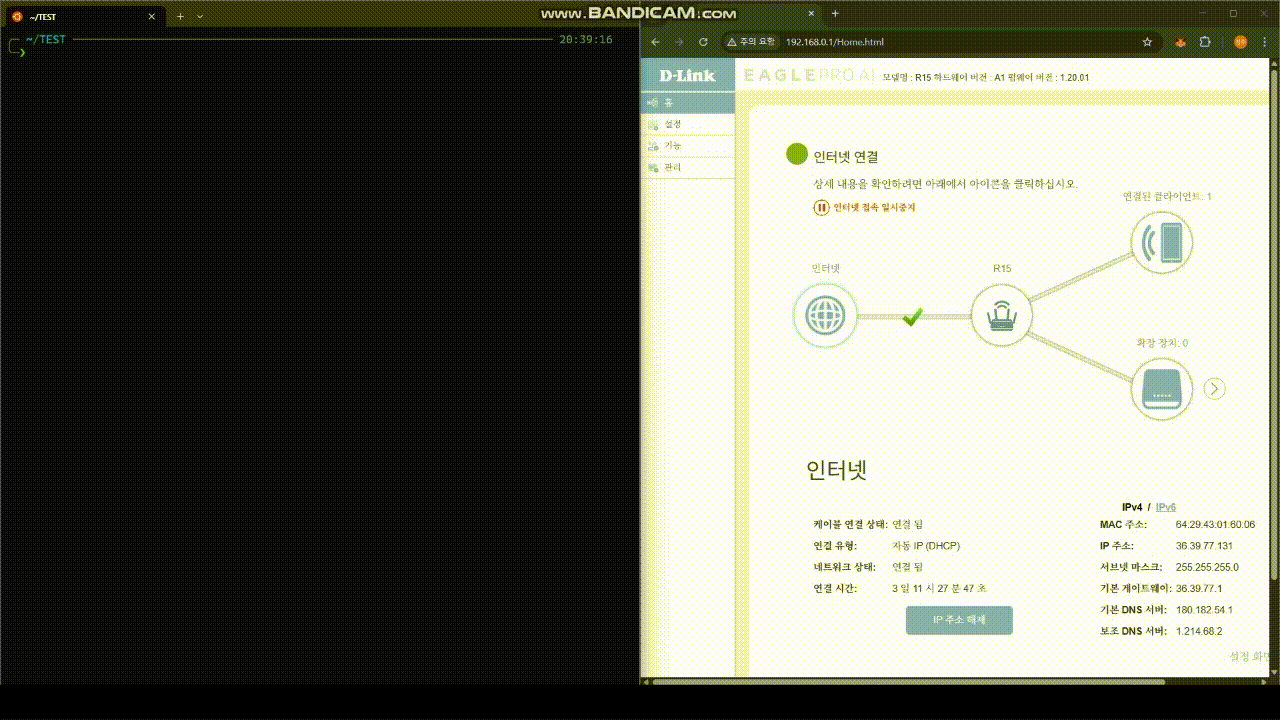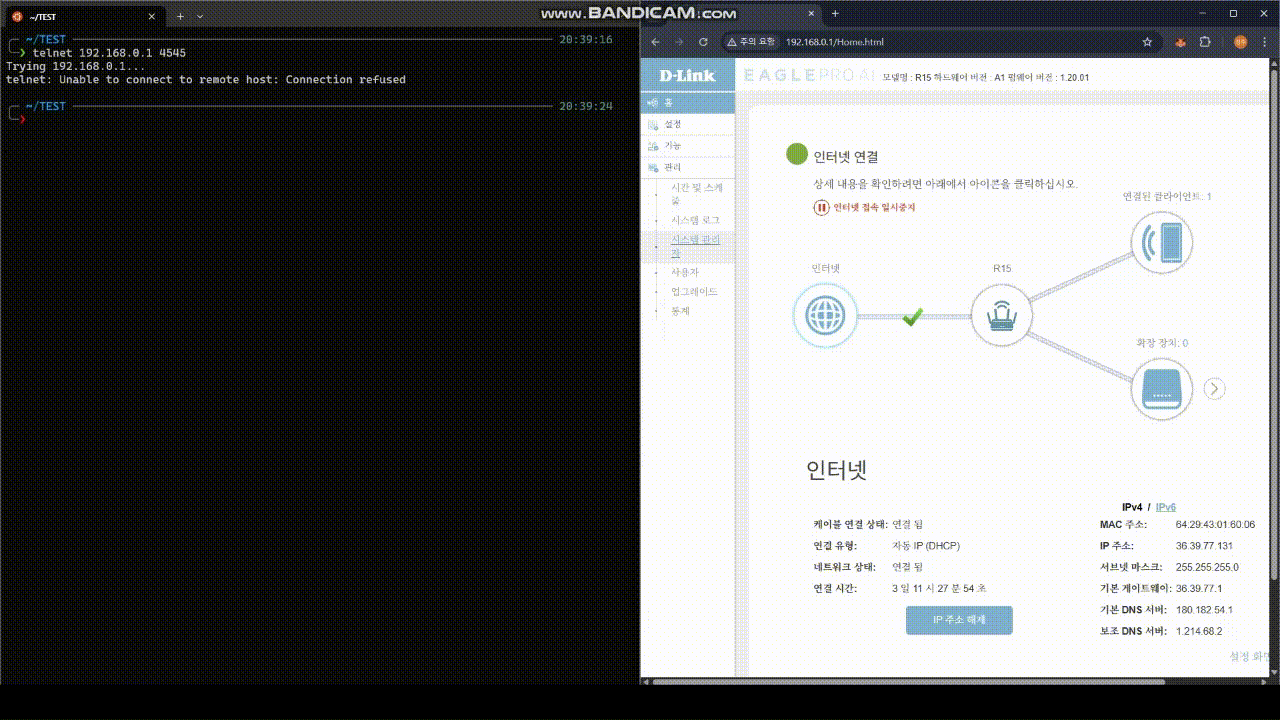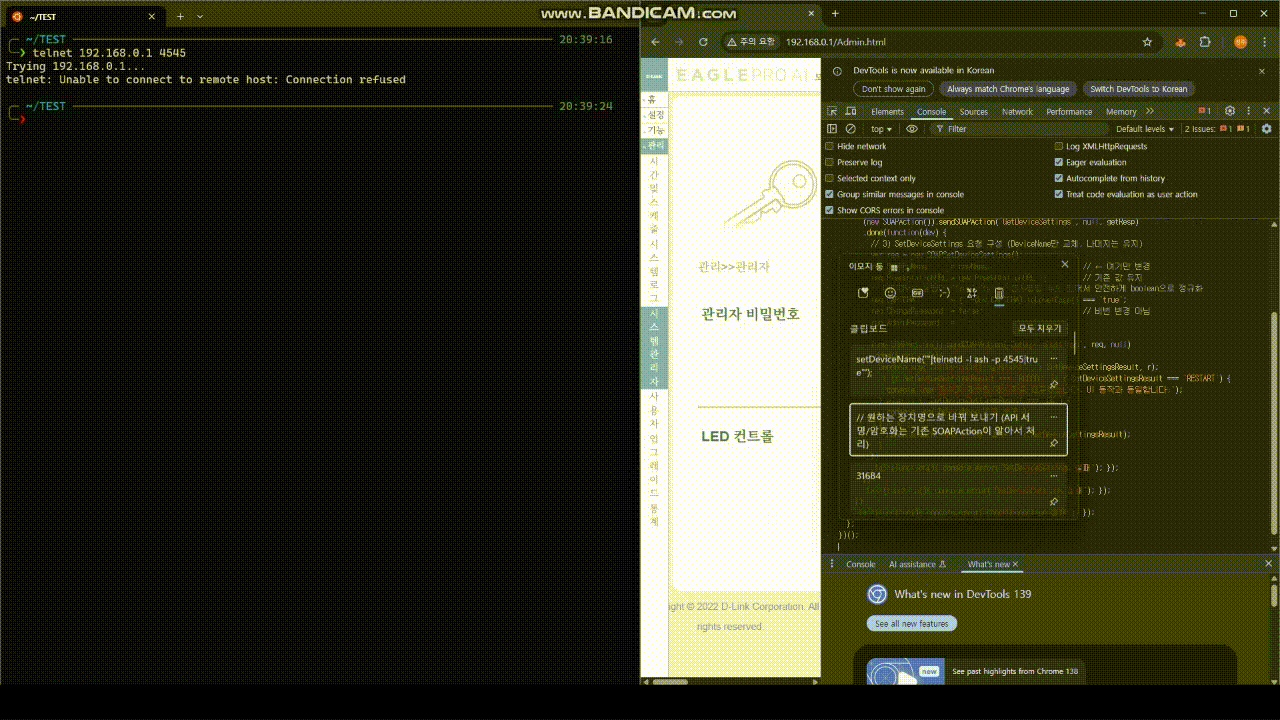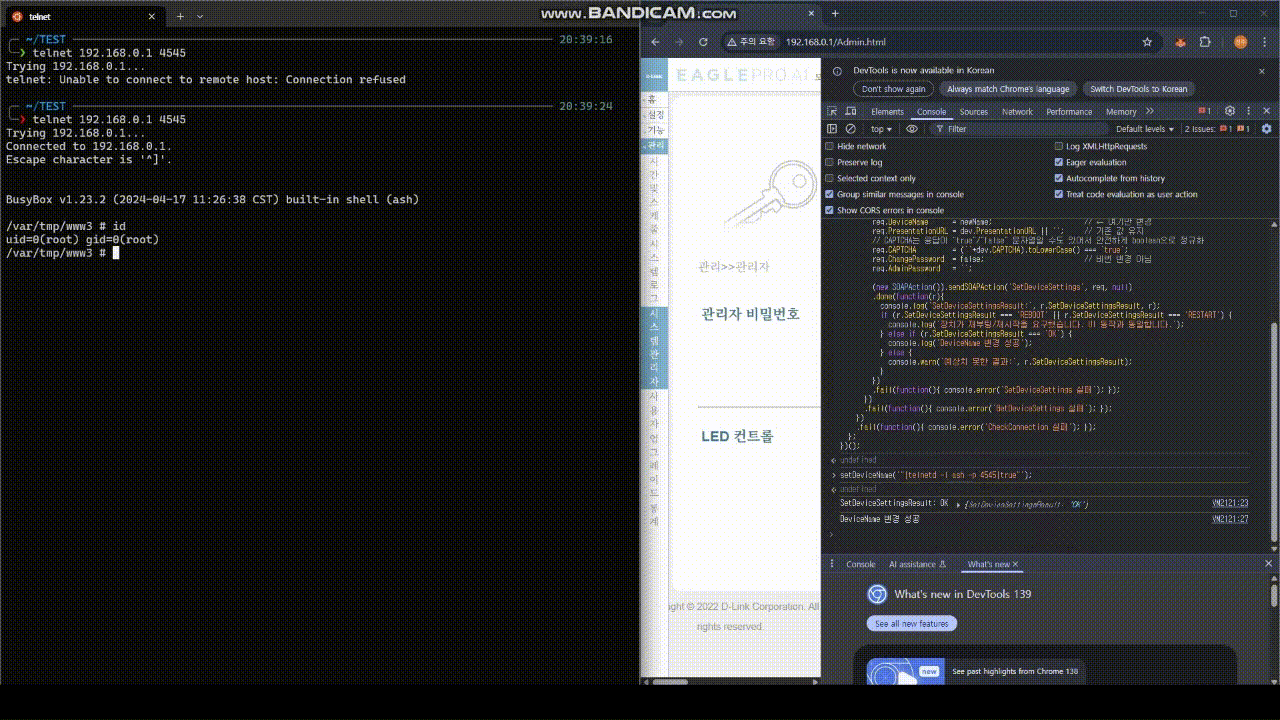 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631