

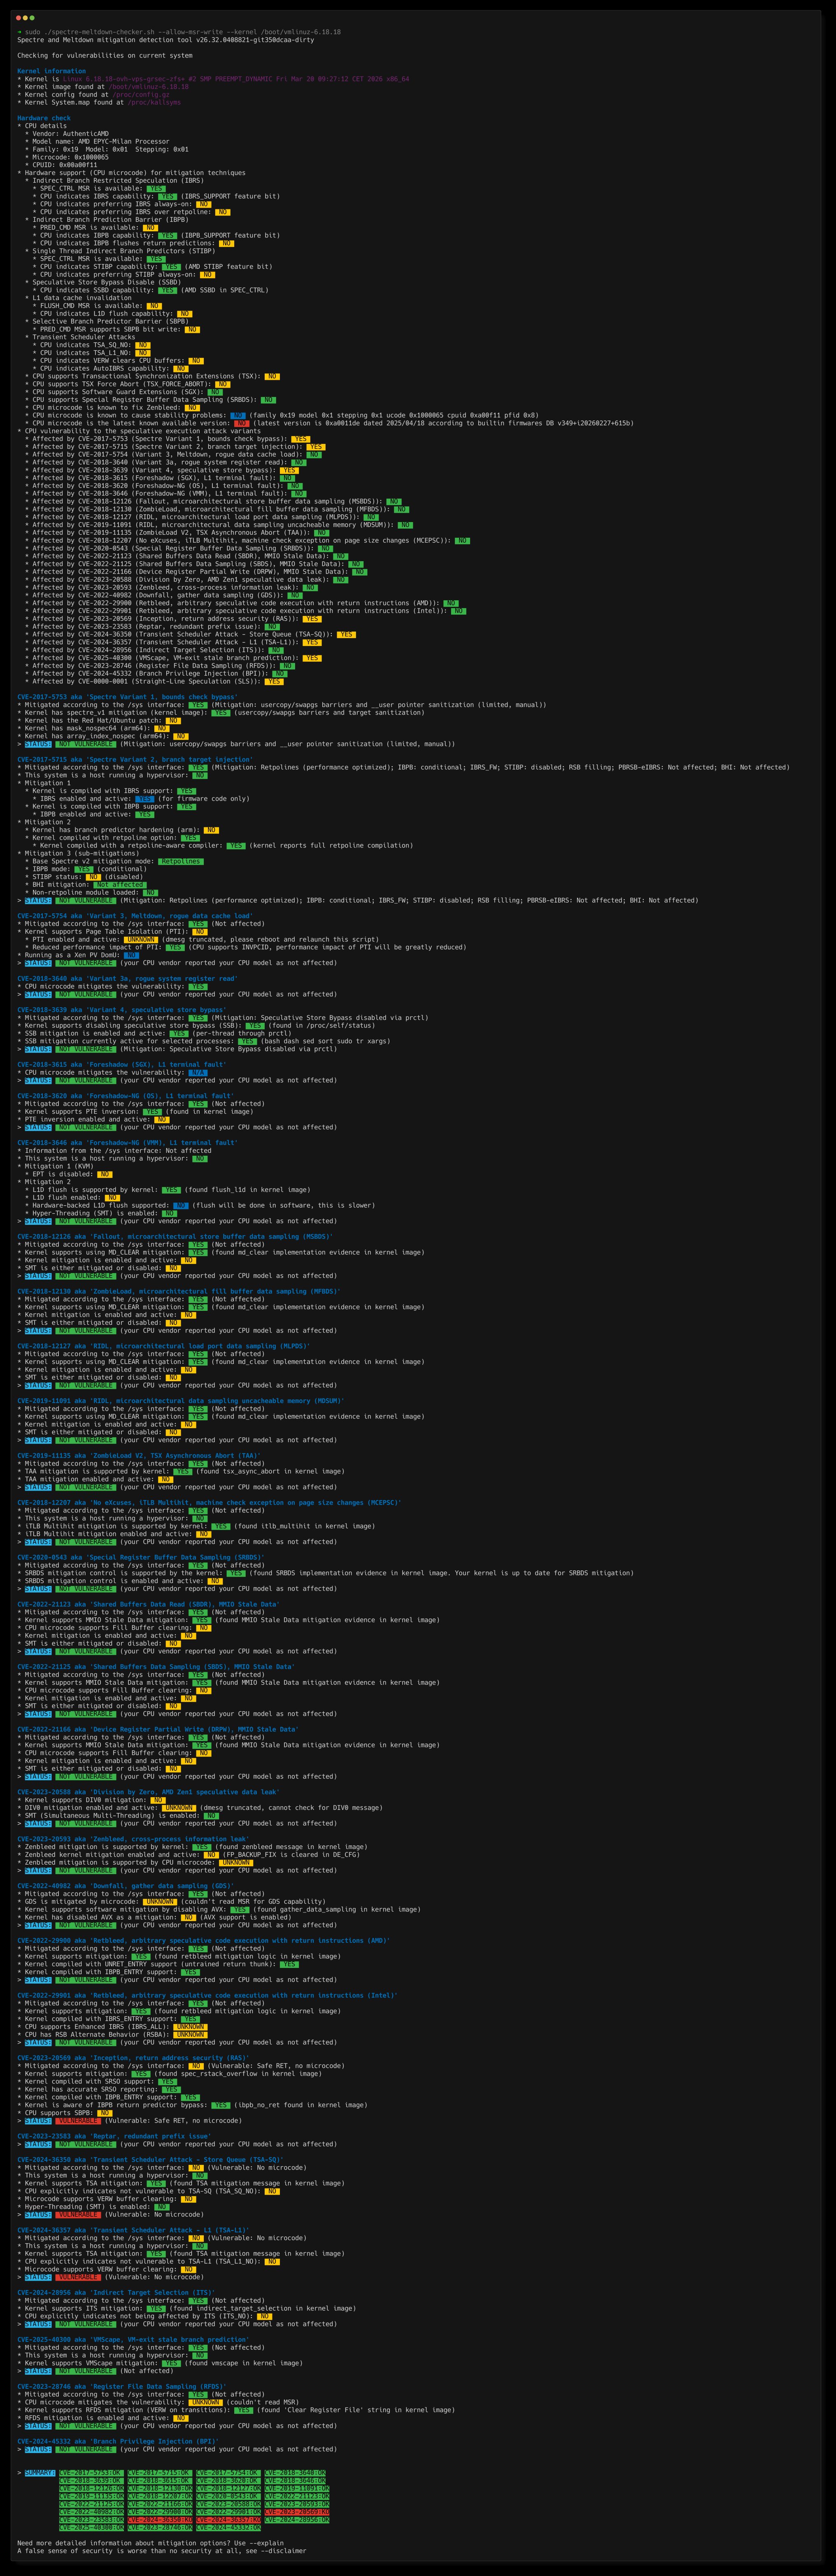
 speed47/spectre-meltdown-checker
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 askyeye/cve-2023-0045
PoC and write-up for CVE-2023-0045: bypasses Linux prctl/seccomp Spectre-BTI mitigations using BTB poisoning and Flush+Reload to leak process secrets.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
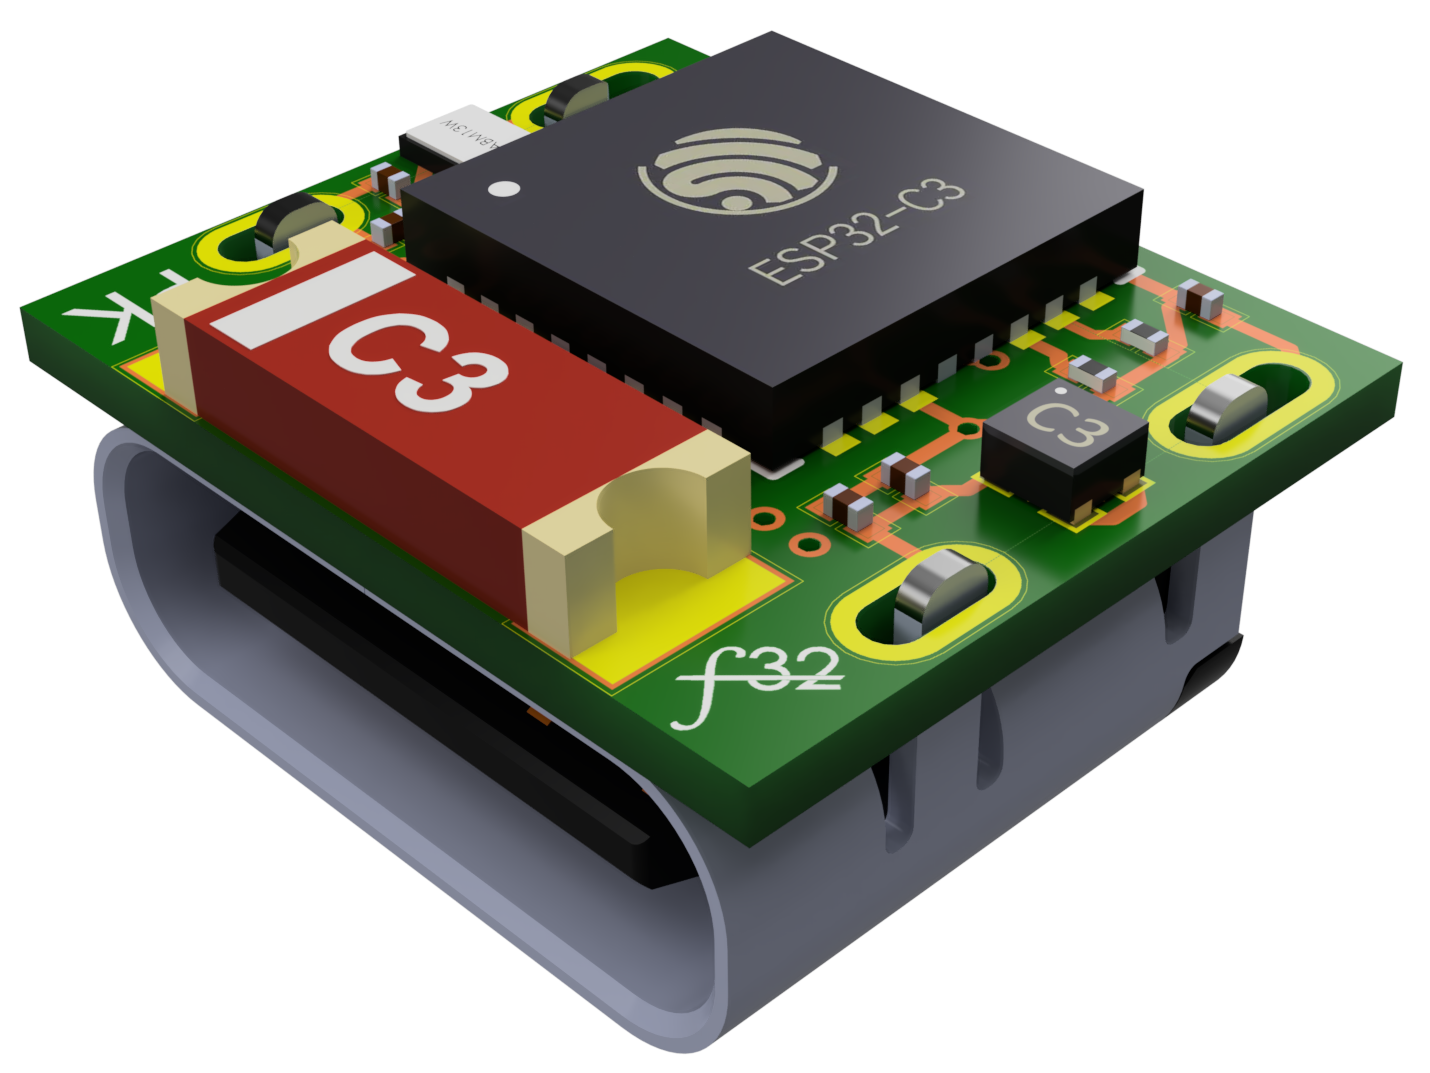 pegork/f32
Ultra-compact ESP32-C3 development board designed for embedded security research, featuring a captive portal example with WiFi scanning and LED…
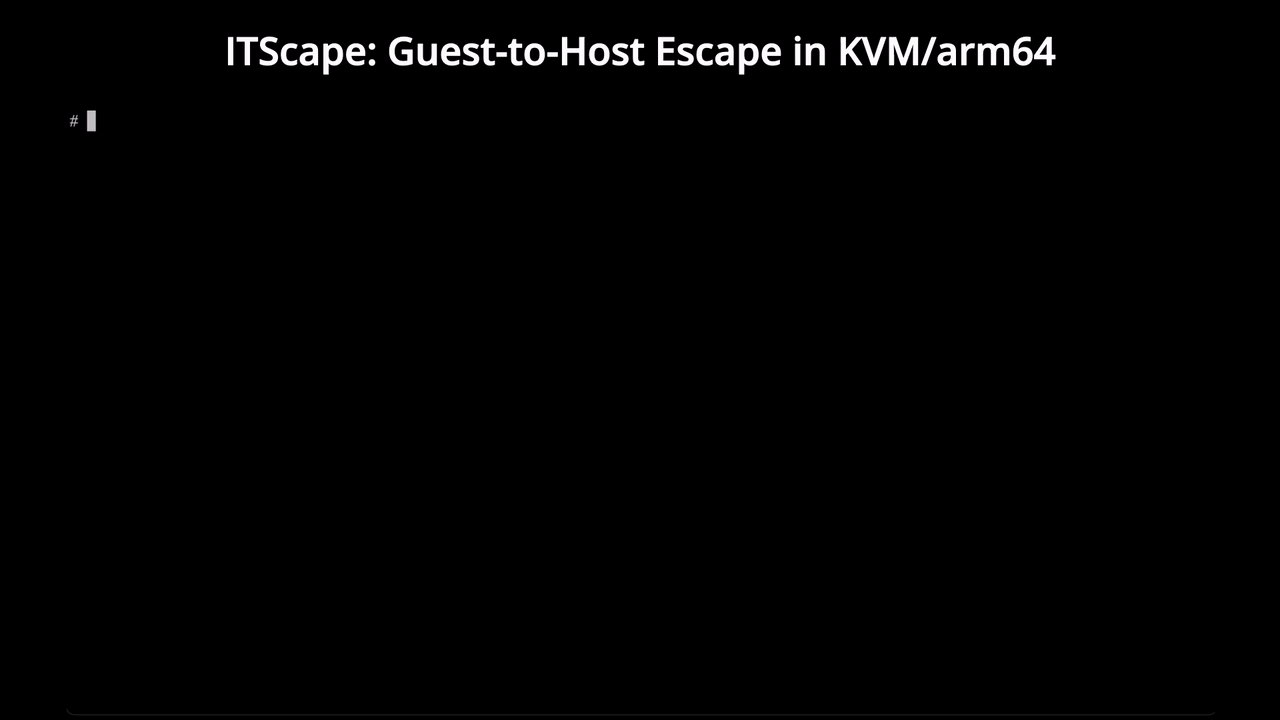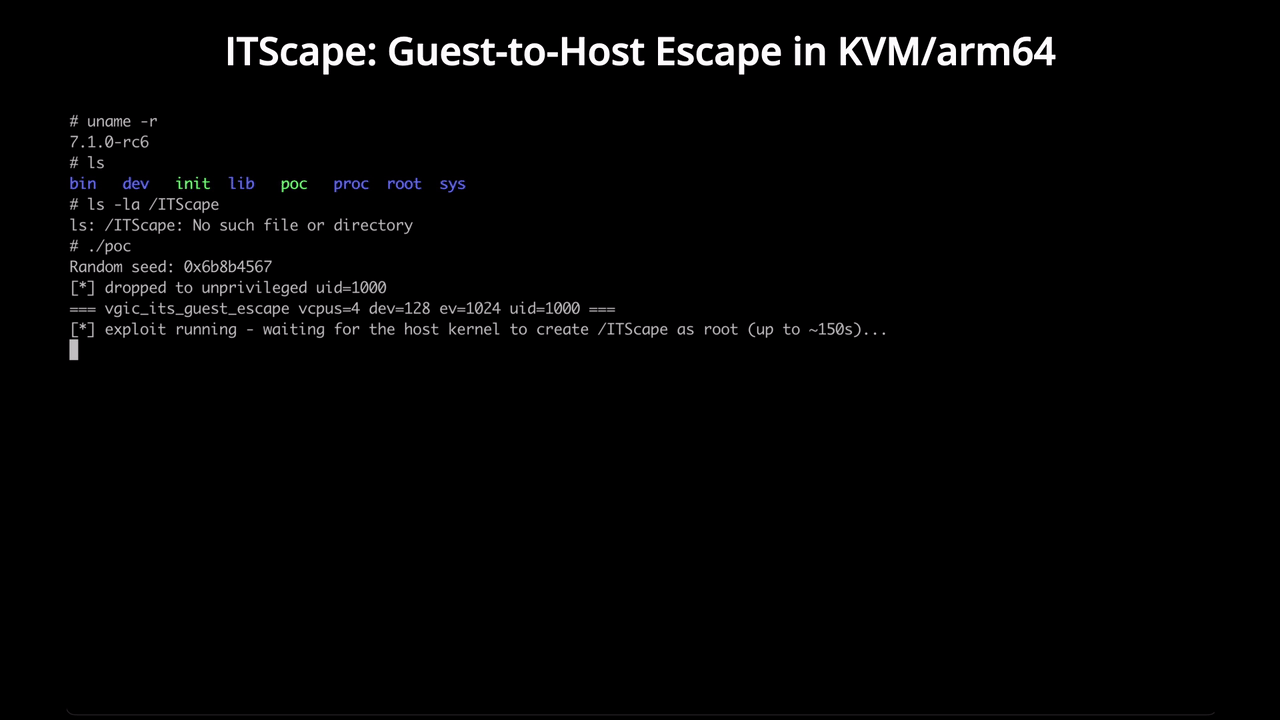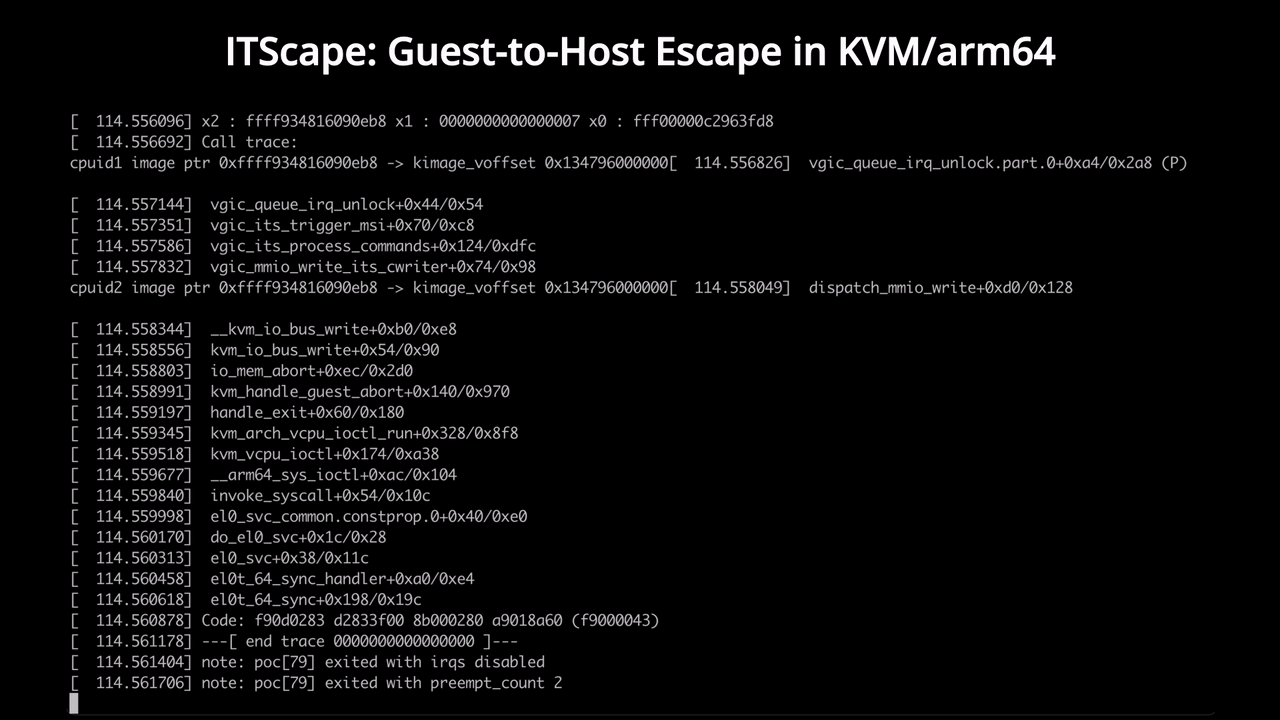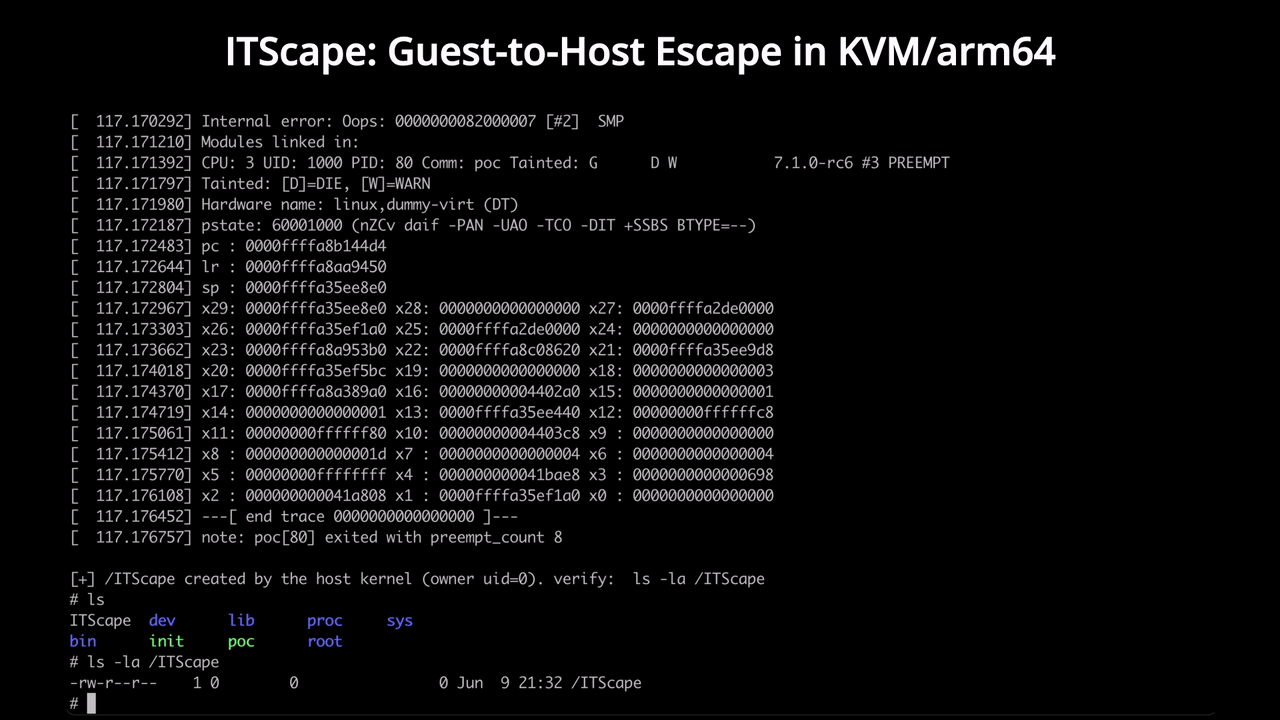 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 nevesnunes/z80-sans
OpenType font that disassembles Z80 instructions
 nishantjoshi00/flipper-template
Zig development template for Flipper Zero with automated build pipeline, SDK integration, and cross-compilation for ARM Cortex-M4. Supports Sub-GHz,…
 msm8916-mainline/cve-2022-22063
Security issue in the hypervisor firmware of some older Qualcomm chipsets
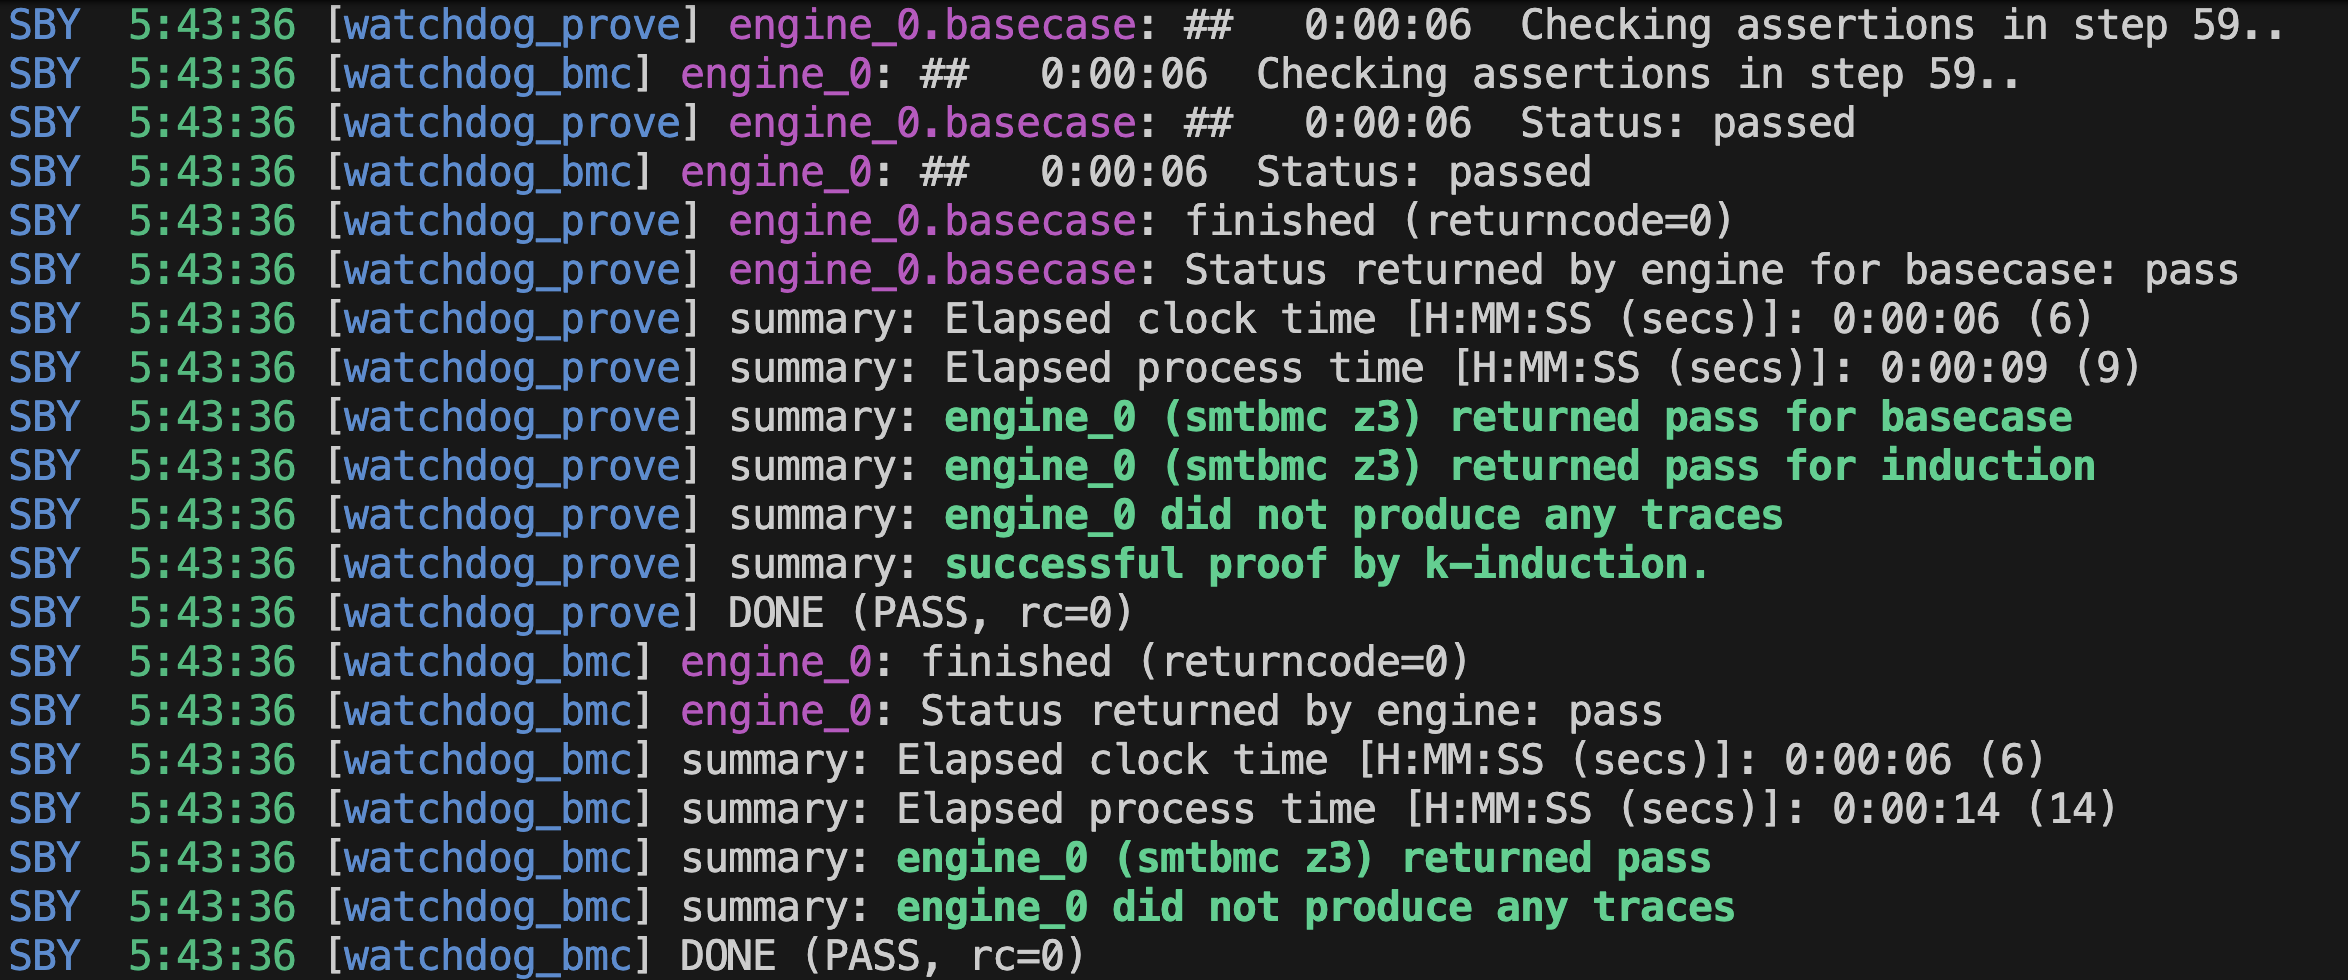 park07/amradio
FPGA-based 12-channel AM radio broadcast system with formal verification of a hardware watchdog for fail-safe emergency alert transmission in…
 hdbreaker/cve-2018-16119
TP-Link TL-WR1043ND - Authenticated Remote Code Execution
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyer
Hardware-level security protocol for mitigating cache-based side-channel attacks.
 saadislamm/spoiler
Speculative Load Hazards Boost Rowhammer and Cache Attacks - CVE-2019-0162 -