
TID-The-Instant-Destroyer
 ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyer
Hardware-level security protocol for mitigating cache-based side-channel attacks.
cryptographydefensive-toolseducation+3
ahmaaaaadbntaaaaa-byte/tid-the-instant-destroyerHardware-level security protocol for mitigating cache-based side-channel attacks.
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…
 dwallener/entropicapublic
Public version of the Entropica repo
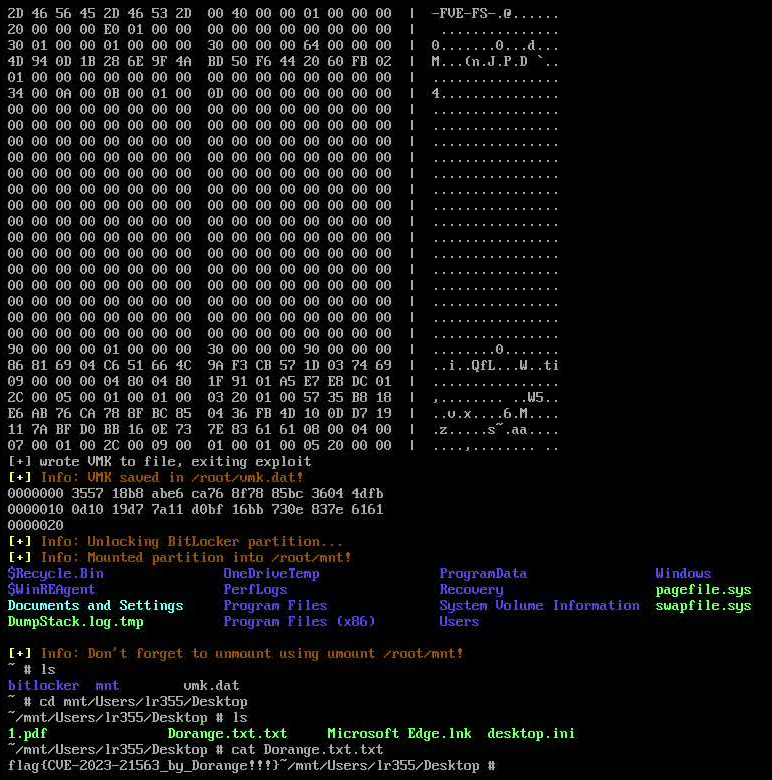 lr2006-robot/bitpixie
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability
 c-sprinks/bitlocker-bypass-research
BitLocker full-disk encryption bypass research using CVE-2023-21563 (BitPixie). Methodology, exploit chain, and defensive recommendations.
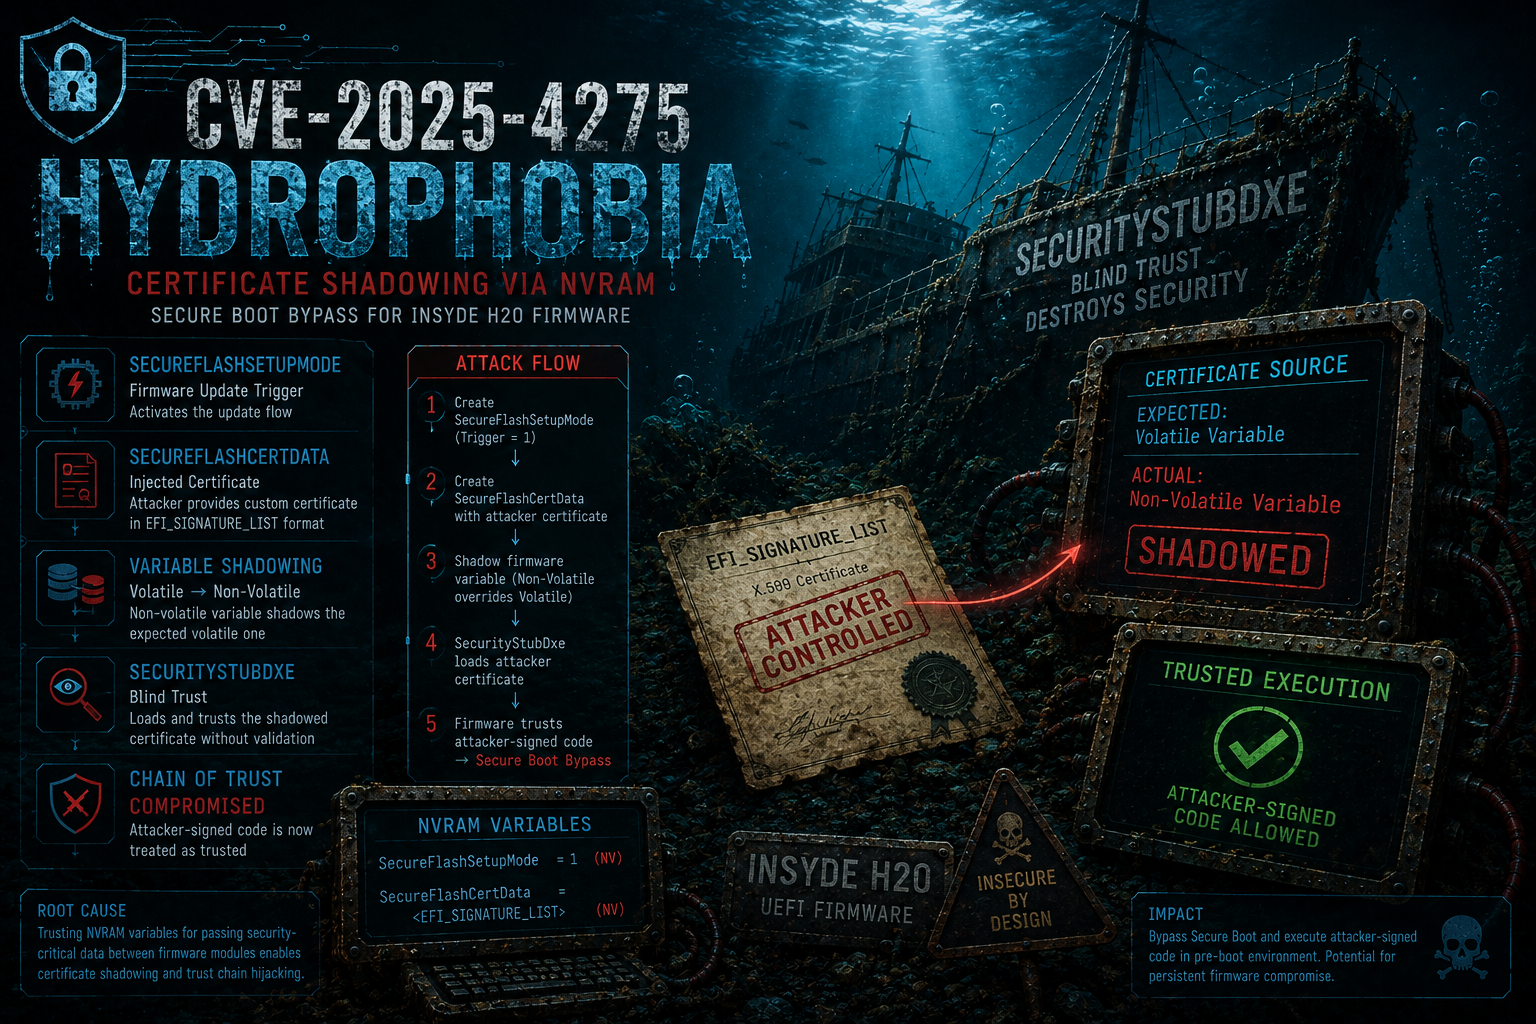 themalwareguardian/cve-2025-4275
Analysis and exploitation of CVE-2025-4275 (Hydr0ph0bia), a Secure Boot trust-chain weakness where firmware variables are used to introduce…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 0xblackash/cve-2026-11499
CVE-2026-11499
 bytereaper77/jump-over-aslr-btb
jump over aslr attacking branch predictors to bypass aslr Technique
 roxanne_ardary/ai-and-the-automobile
Curated collection of open specifications for AI-integrated vehicle systems, covering autonomy, perception, navigation, energy management, safety,…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 cryptoadvocate/cryptohackapp
The mobile engineering home of the Cryptohack Badge project.
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 saadislamm/spoiler
Speculative Load Hazards Boost Rowhammer and Cache Attacks - CVE-2019-0162 -
 synacktiv/lehack-2026-challenge
Sources of Synacktiv's challenge for leHack 2026