
unicorn
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.4k
unicorn-engine/unicornUnicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
 tomking062/cve-2022-38694_unlock_bootloader
This is a one-time signature verification bypass. For persistent signature verification bypass, check…
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
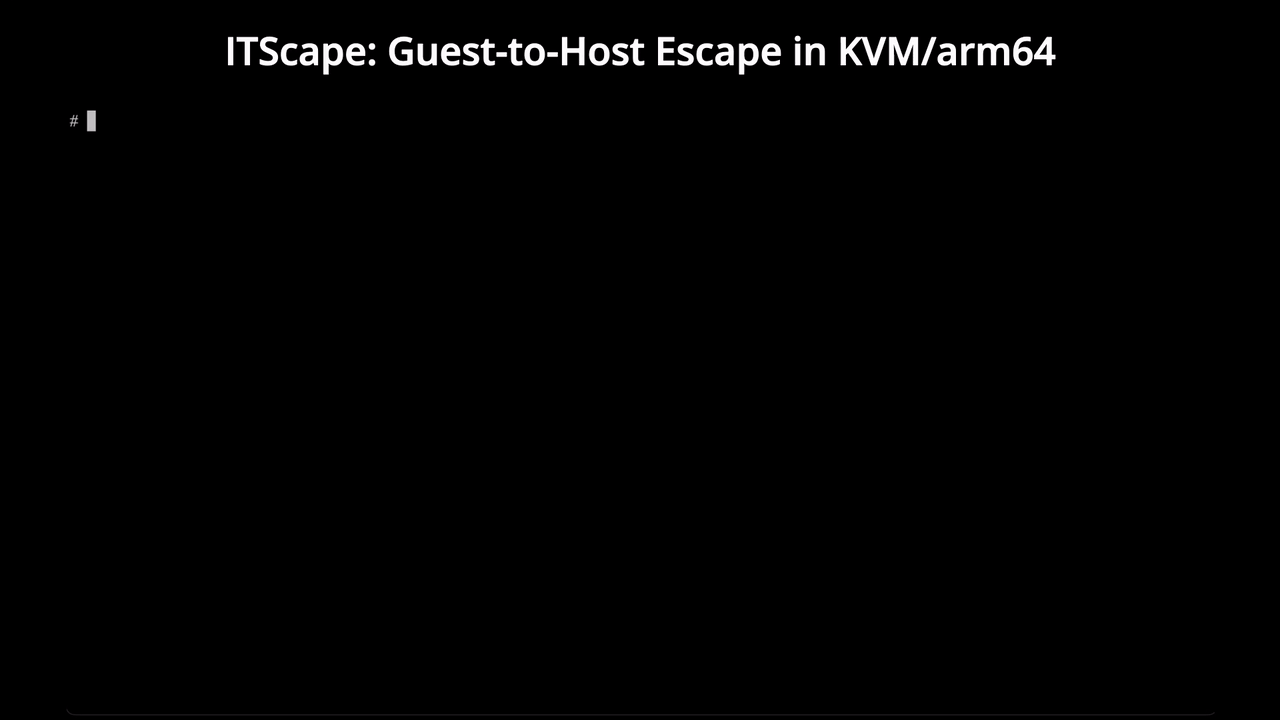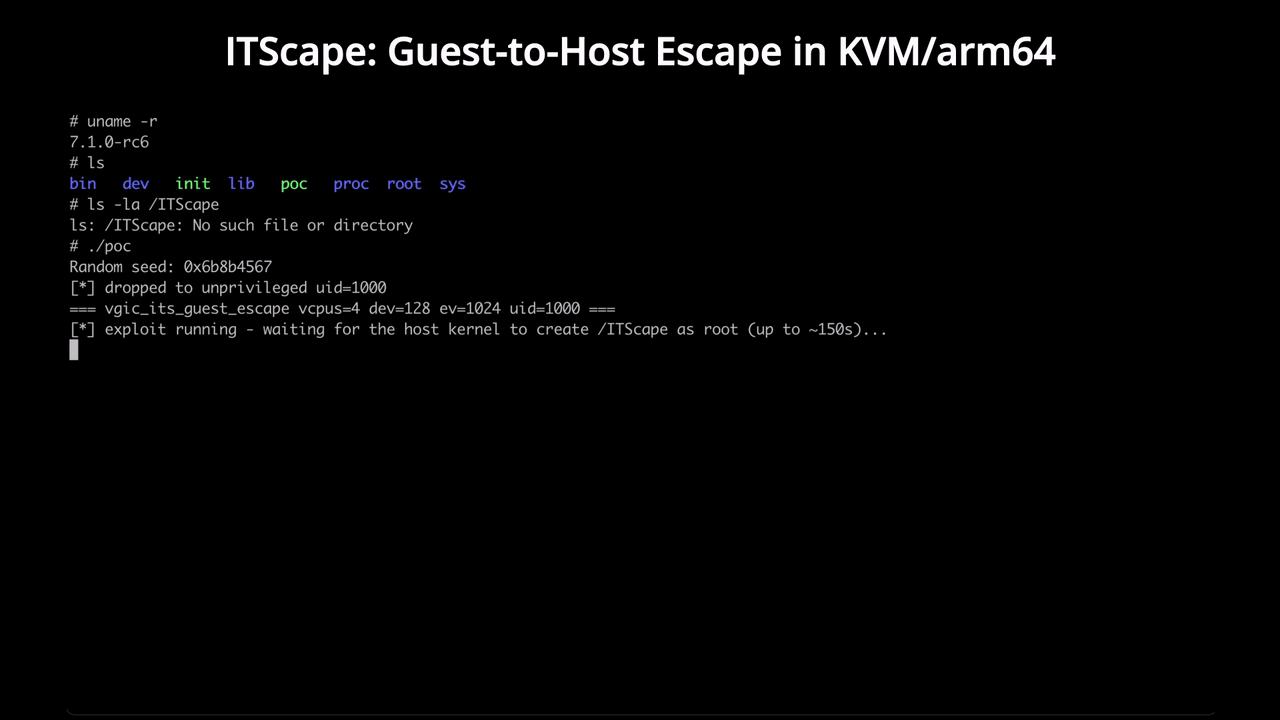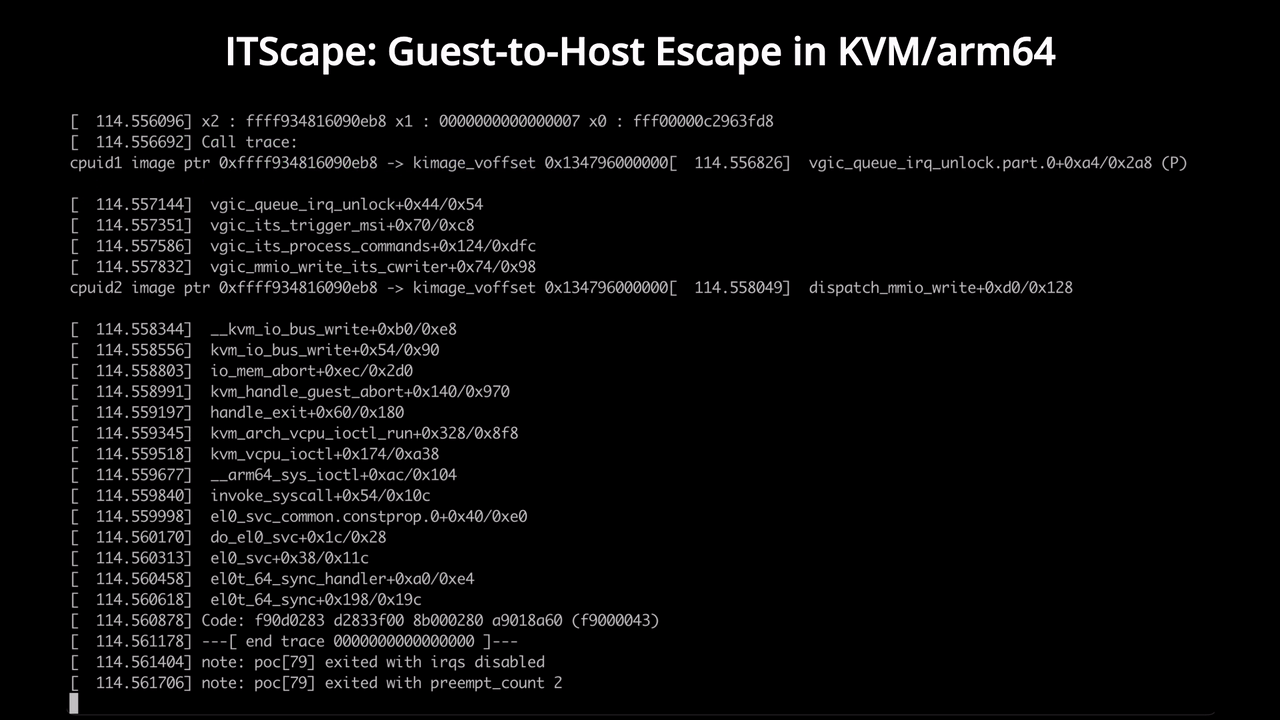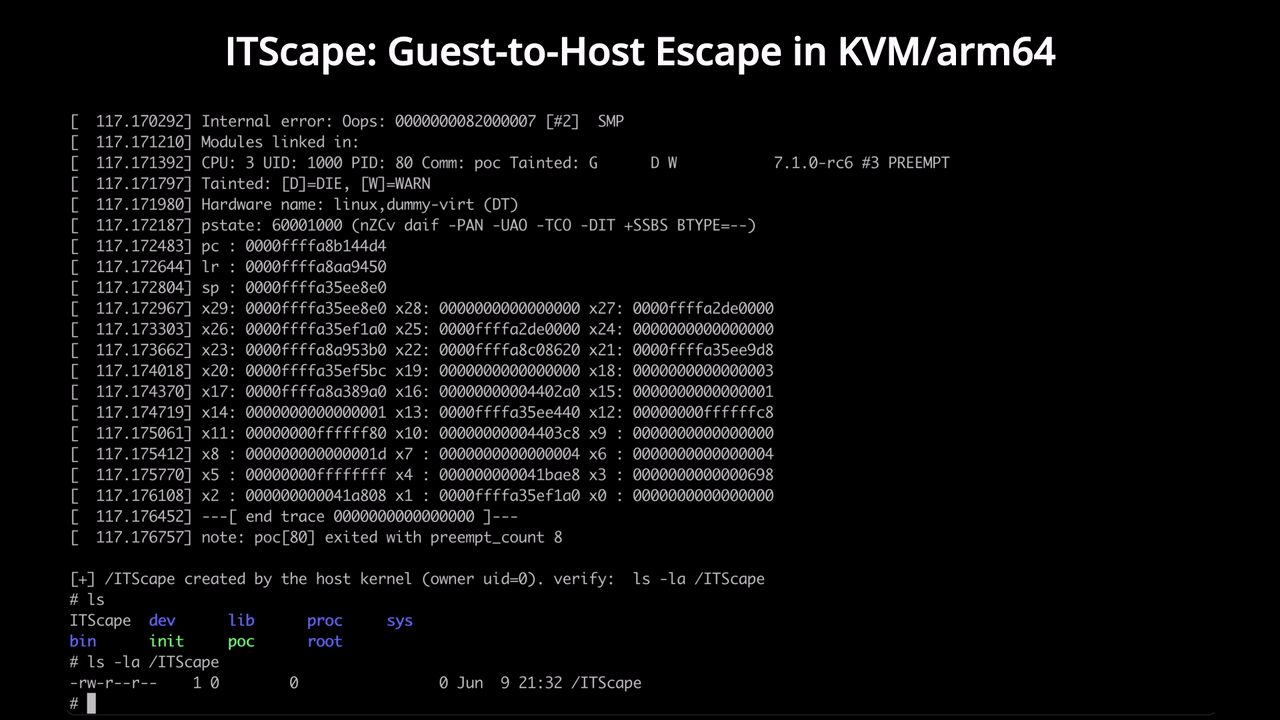 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
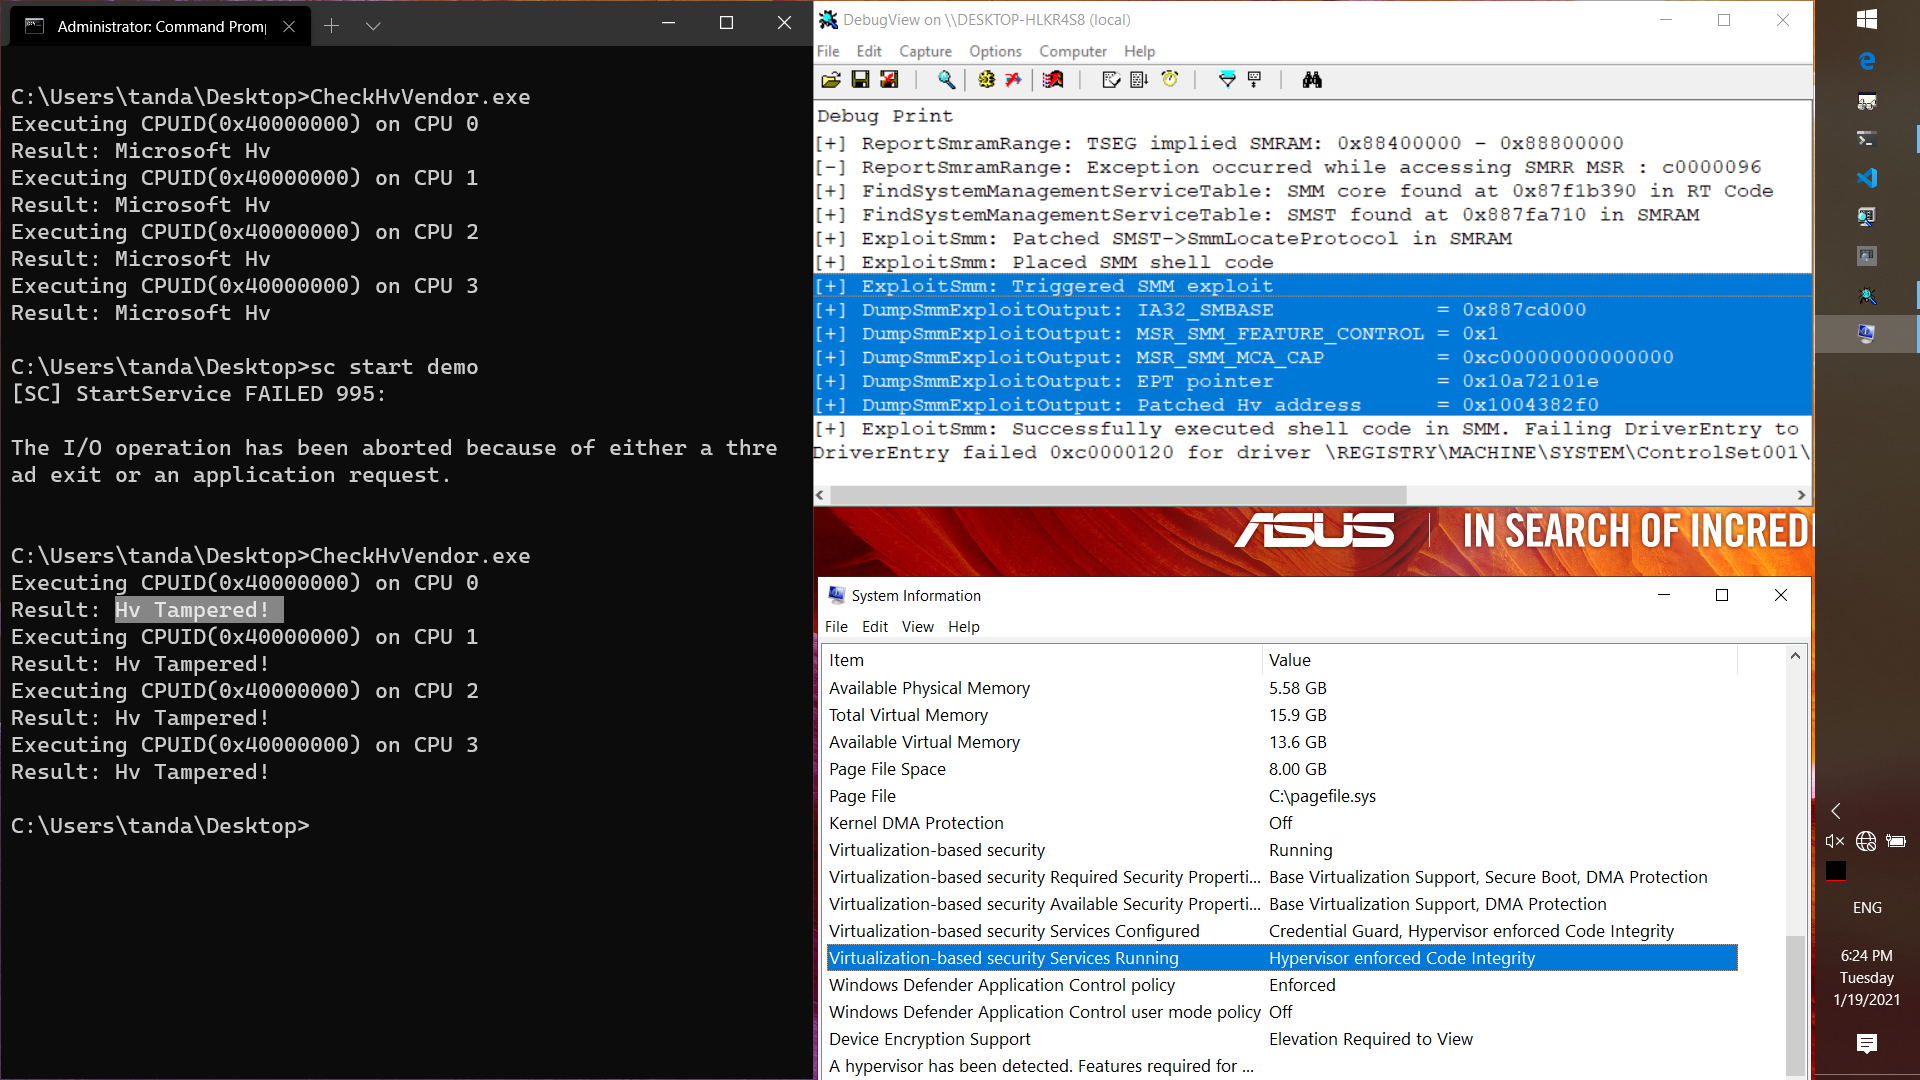 tandasat/smmexploit
The report and the exploit of CVE-2021-26943, the kernel-to-SMM local privilege escalation vulnerability in ASUS UX360CA BIOS version 303.
 tomking062/cve-2022-38691_38692
Let's control Secure Boot Chain ourselves.
 renorobert/virtualbox-cve-2018-2844
C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…
 arthastang/router-exploit-shovel
Automated Application Generation for Stack Overflow Types on Wireless Routers
 m-gsch/s5late
iPod Nano 7G bootrom exploit a bit too late
 giancarlolelli/quantum
This repository contains the code and submission detail for the QDay prize challenge by https://www.projecteleven.com/
 opsxcq/exploit-cve-2017-5715
Spectre exploit
 hacefresko/cve-2025-40634
Exploit for stack-based buffer overflow found in the conn-indicator binary in the TP-Link Archer AX50 router
 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 ch3rn0byl/cve-2021-21551
Proof-of-concept exploit for CVE-2021-21551 targeting Dell's dbutil_2_3 driver to achieve code execution on systems with HVCI disabled.
 bitdefender/lvi-lfb-attack-poc
This repository contains the sources and documentation for the LVI-LFB Control Flow Hijacking attack PoC (CVE-2020-0551)