Extracting-User-credentials-For-Web-portal-and-WiFi-AP-For-Hathway-Router-CVE-2024-44815-

CVE-2024-44815

CVE-2024-44815

Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…

A tiny cpp program to test reading memory using a vulnerable RTCore64.sys driver/device (CVE-2019-16098). It tries to read a "secret" from its own…

IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port

IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control

RowHammer Based-Exploit

CVE-2022-25258 - Demo exploit targeting usb gadget's os descriptor handler

https://www.intel.com/content/www/us/en/security-center/advisory/intel-sa-00338.html

Final OBJECTIVE:BIOS ROOTKIT AND RSHELL USING BIOS NETWORKING STACK

A bunch of routers firmware images. Principally those that are not available and they do need to be extracted via JTAG, UART, desoldering flash or…

CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631

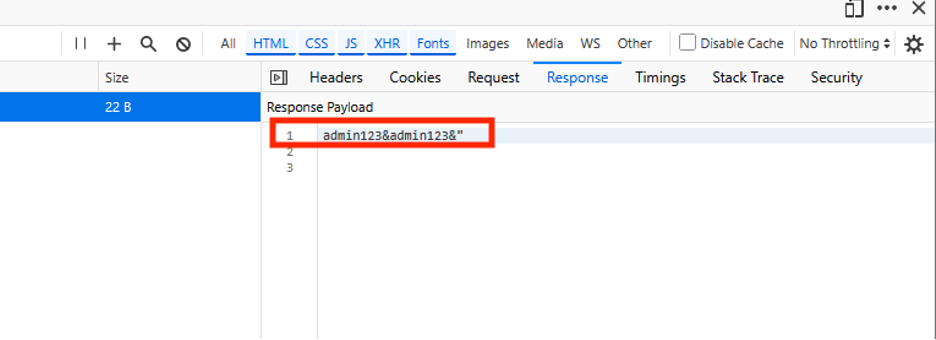
Disclosure of client-side authentication bypass in AVer camera web interface exposing unencrypted credentials via network traffic monitoring.

cve based on vulnerable cisco's Archer A7 routers

Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…

PoC

TP-LINK Multiple HTML Injection Vulnerabilities

个人CVE

Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…