

CVE-2026-79298
 themalwareguardian/cve-2026-79298
Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
binary-analysisexploitationfirmware-analysis+4
2
themalwareguardian/cve-2026-79298Research repository documenting CVE-2026-79298, an incomplete UEFI Secure Boot bypass remediation in Howyar SysReturn's IA-32 boot path, with reverse…
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 d7ead/cve-2025-63602
Disclosure for CVE-2025-63602, including a PoC for use of an insecure driver in Awesome Miner 11.2.4 leading to arbitrary kernel read/write to MSRs,…
 fengjixuchui/cve-2019-18845
The MsIo64.sys and MsIo32.sys drivers in Patriot Viper RGB before 1.1 allow local users (including low integrity processes) to read and write to…
 crackercat/cve-2021-44852
An issue was discovered in BS_RCIO64.sys in Biostar RACING GT Evo 2.1.1905.1700. A low-integrity process can open the driver's device object and…
 gmh5225/driver-hwid-btbd-modified
Modified btbd HWID spoofer kernel driver that can be manually mapped to evade anti-cheat detection on Windows 1909.
 d-raco/cve-2024-31964
Proof-of-concept exploit for CVE-2024-31964, a temporary authentication bypass in Mitel 6900w Series SIP phones allowing unauthenticated POST…
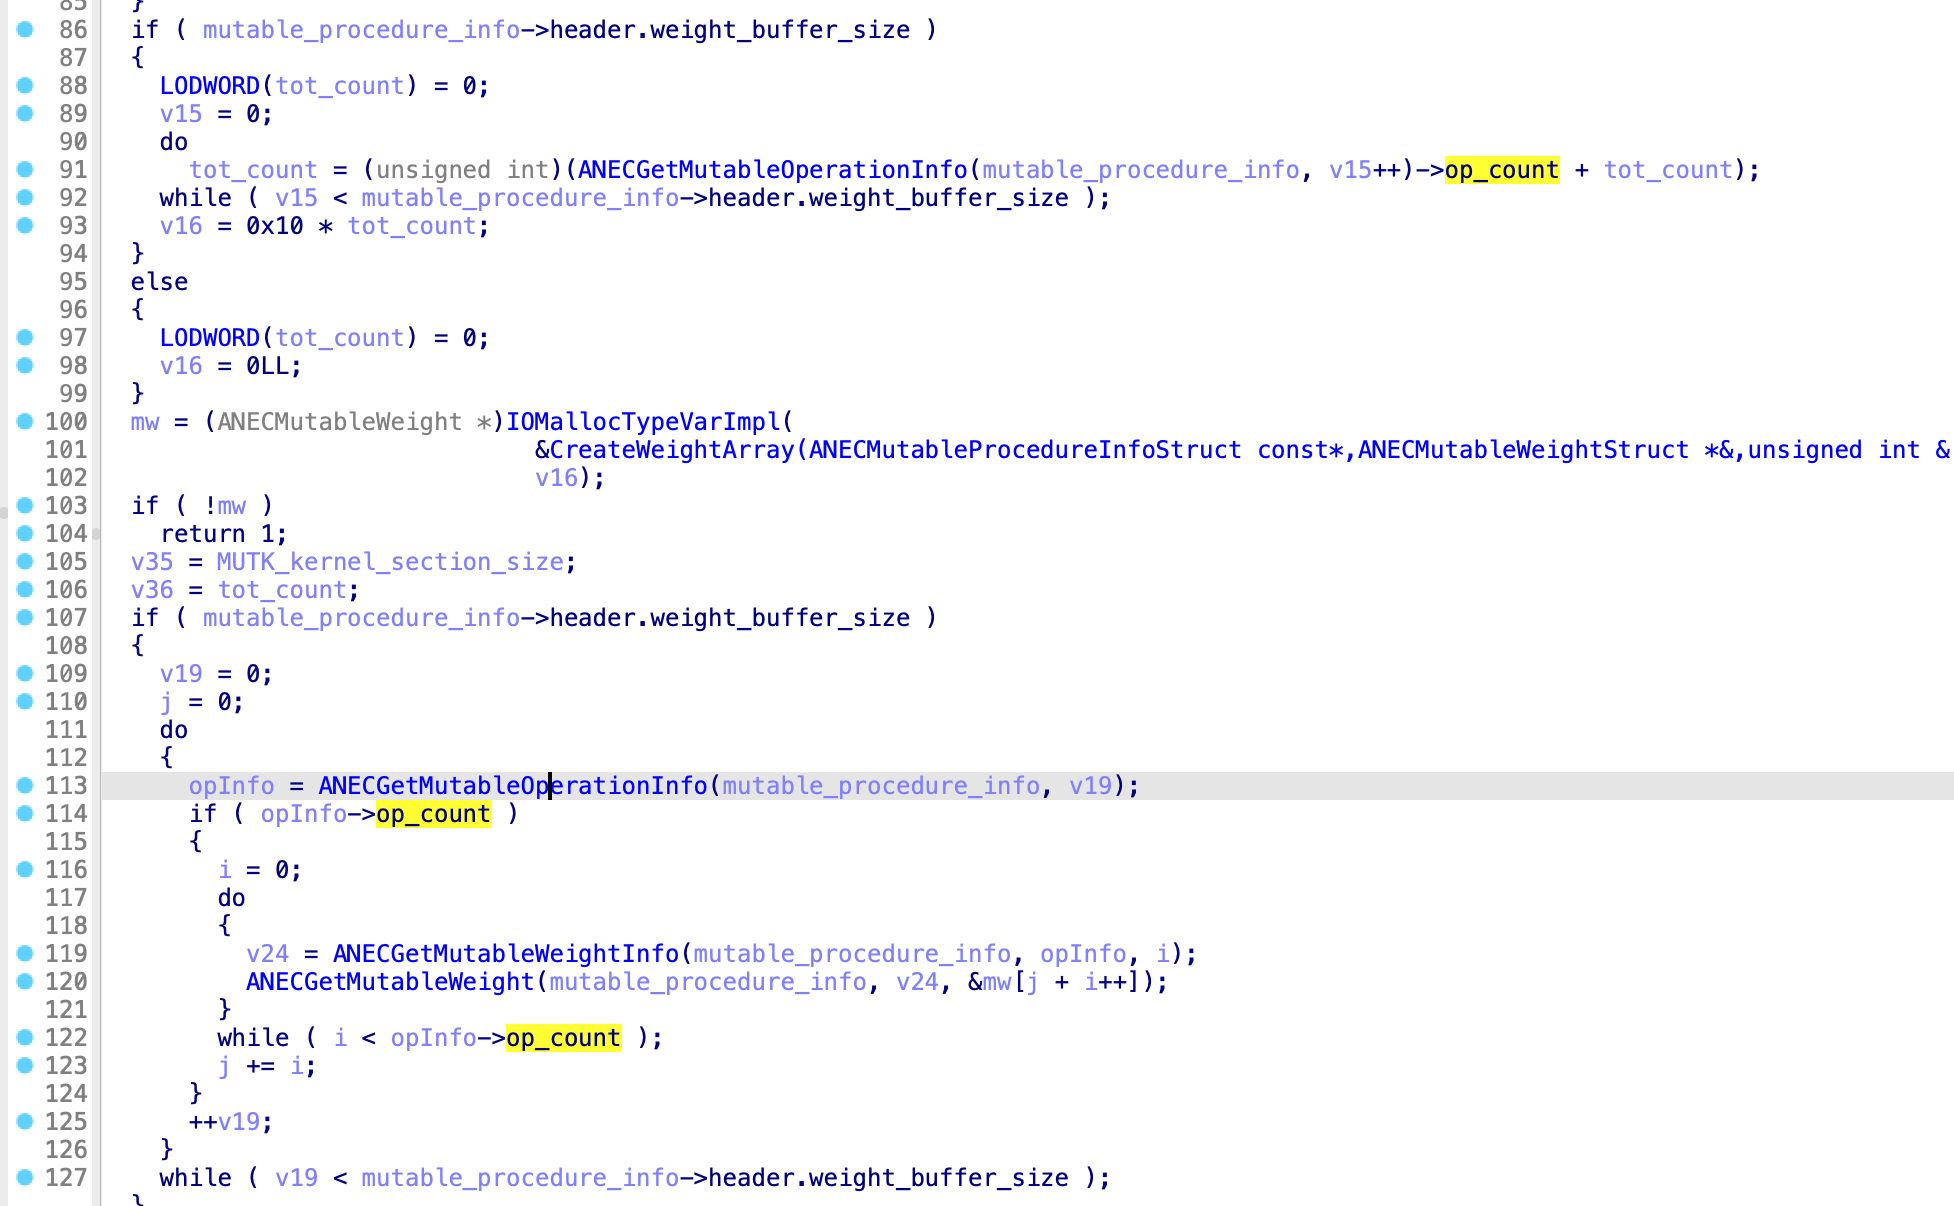 ox1111/cve-2022-32932
Technical analysis and proof-of-concept for CVE-2022-32932, a double fetch vulnerability in Apple's ANE kernel driver leading to out-of-bounds write…
 crackercat/cve-2021-3438
A potential buffer overflow in the software drivers for certain HP LaserJet products and Samsung product printers could lead to an escalation of…
 valium007/cve-2026-56129
Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.
 fevar54/poc_cve-2025-29943_write-what-where-condition
Proof-of-concept for CVE-2025-29943 exploiting an undocumented stack engine bit in AMD Zen CPUs to corrupt the stack pointer in SEV-SNP protected…
 gmh5225/disk-spoofer
Kernel driver based disk size and sector query spoofing program, can evade Windows WMIC query.
 puglia-ryan/s-v-project-implementation-of-cve-2015-3256
Reproducible crash proof-of-concept for CVE-2015-3456 (VENOM) targeting QEMU's virtual floppy disk controller. Demonstrates guest-controlled writes…
 yozarseef95/cve-2023-31595
IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port
 gmh5225/cve-2022-34683
NVIDIA GPU Display Driver for Windows contains a vulnerability in the kernel mode layer (nvlddmkm.sys) handler for DxgkDdiEscape, where a…
 risuxx/cve-2023-34853
Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…
 mav3r1ck0x1/cve-2023-23583-reptar-
This script can help determine the CPU ID for the processor of your system, please note that I have not added every CPU ID to this script, edit as…
 mein-0/knockgiga
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…