
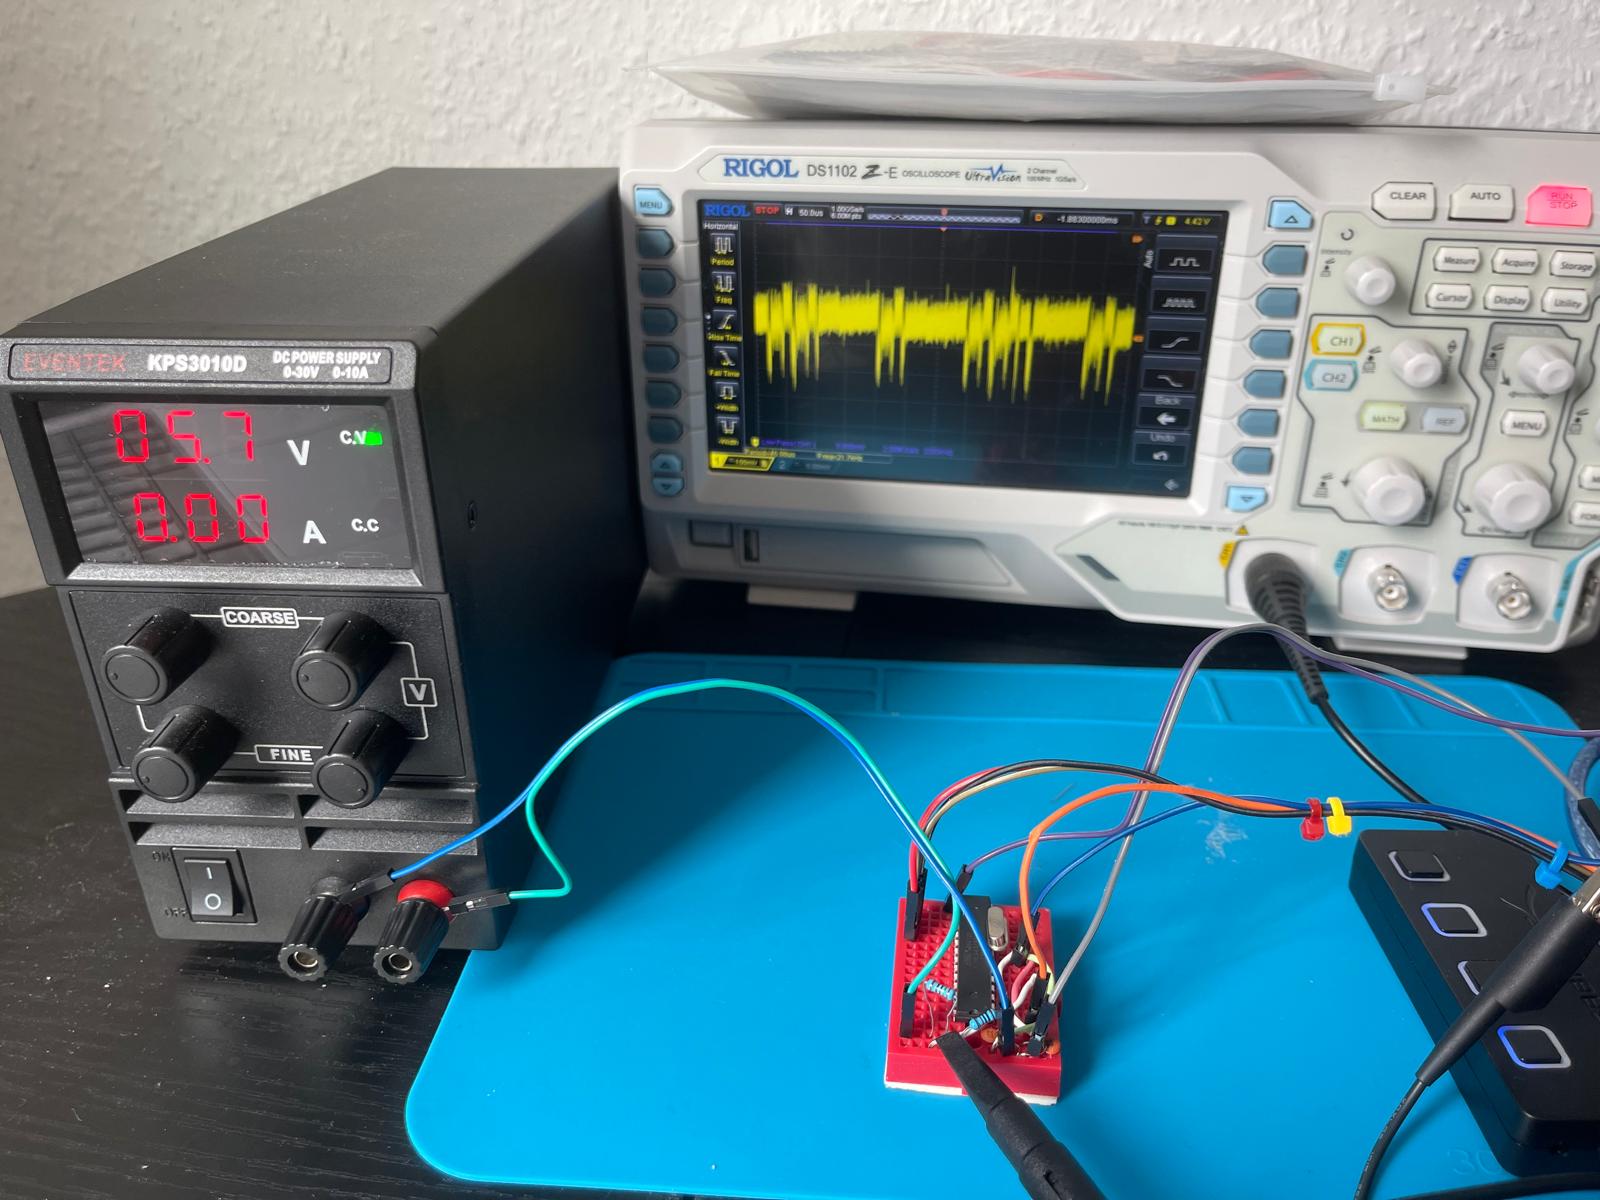
power_analysis
 lord-feistel/power_analysis
Proof-of-concept demonstrating a power analysis side-channel attack against a vulnerable RSA implementation on Arduino (Atmega328P), with detailed…
cryptographyeducationembedded-systems-security+2
32
lord-feistel/power_analysisProof-of-concept demonstrating a power analysis side-channel attack against a vulnerable RSA implementation on Arduino (Atmega328P), with detailed…
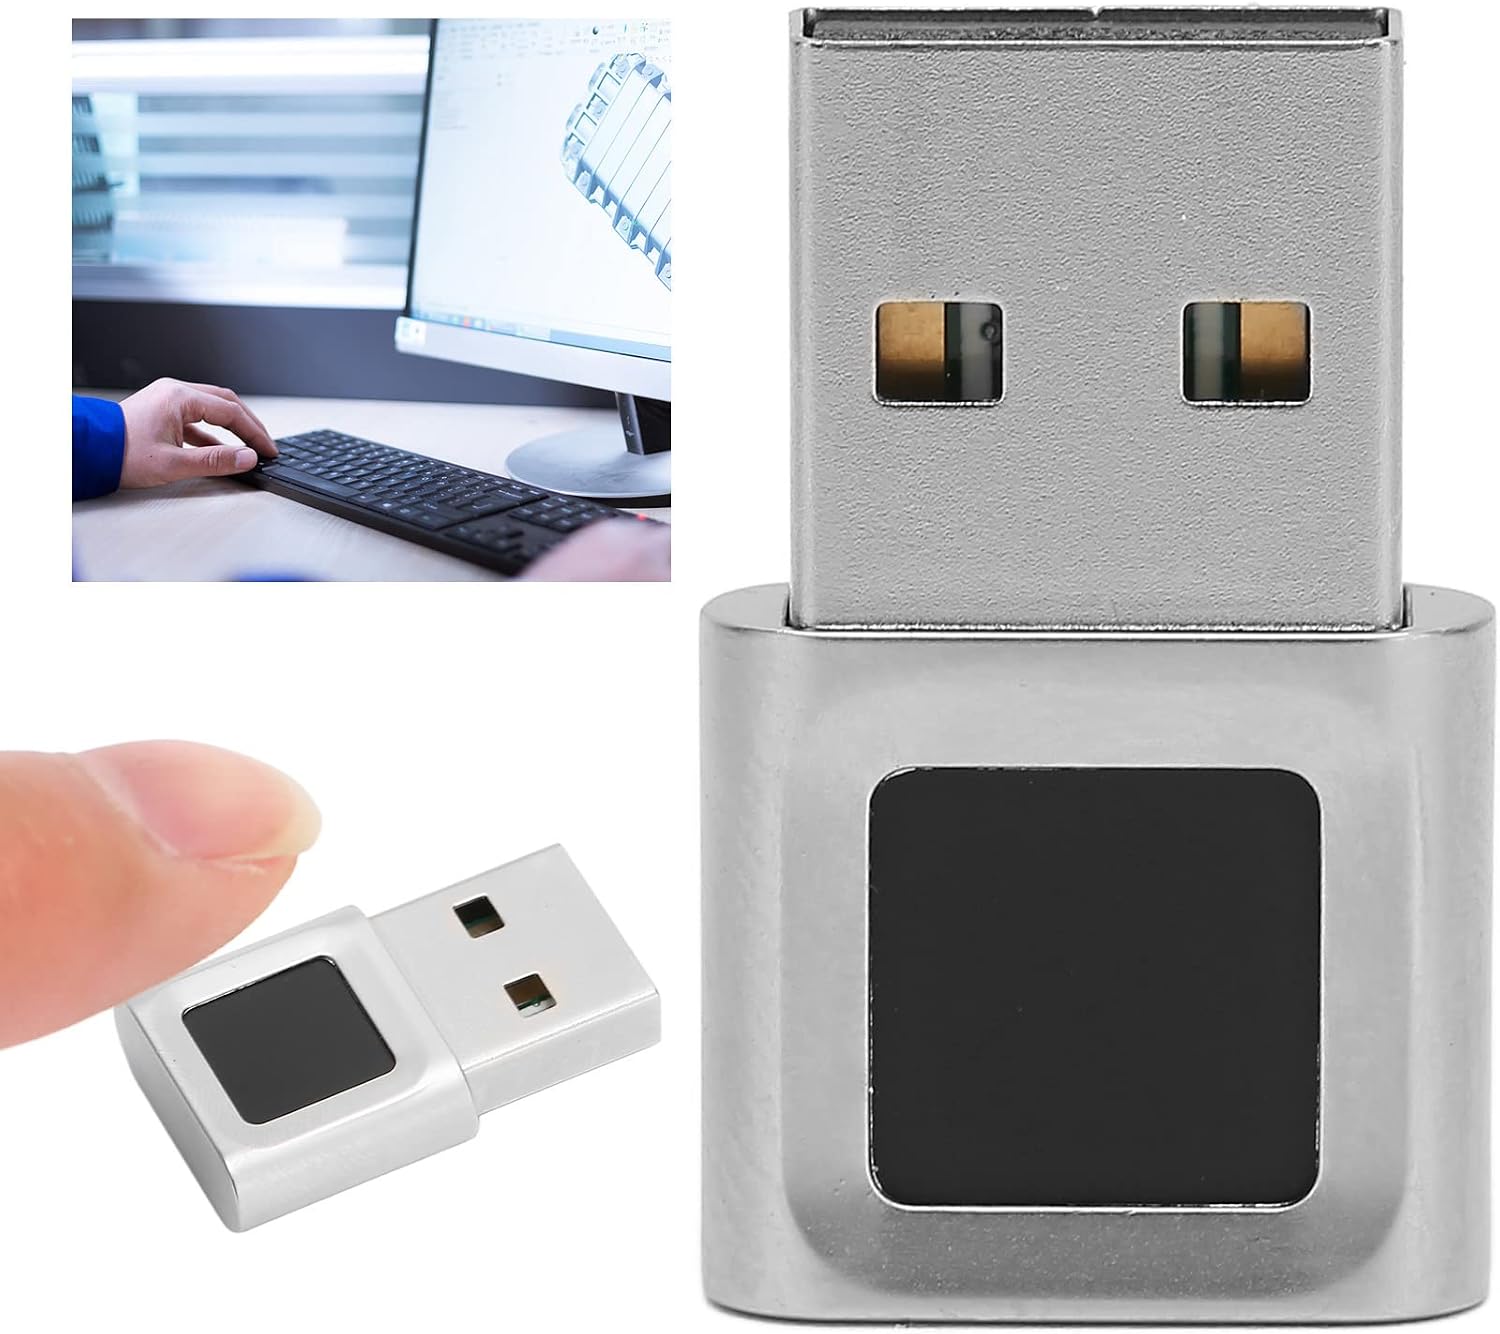 omgrant/ft9201-libfprint
Linux libfprint driver for the Focal-systems FT9201 (2808:93a9) USB fingerprint reader — runs FocalTech's own Windows matching engine natively on…
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…
 badchemical/iot-vulnerability-research-public
Independent IoT security research, vulnerability disclosures, and PoCs focusing on firmware analysis, hardware interfaces, and cryptographic flaws.
 axcheron/crestron_getsudopwd
Tool to exploit CVE-2018-13341 and recover hidden account password on Crestron devices
 userlandkernel/usbusted
Research on Apple's USB protocols
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 264312431/picohaxx
A kernel exploit for Pico 4 devices based on cve-2023-33107.
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
 sbaresearch/stop-zenbleed-win
PowerShell script to apply Zenbleed (CVE-2023-20593) MSR workaround on Windows
 manucuf/cve202015808
A proof of concept of CVE-2020-15808 vulnerability exploit on STM32F4 Discovery board
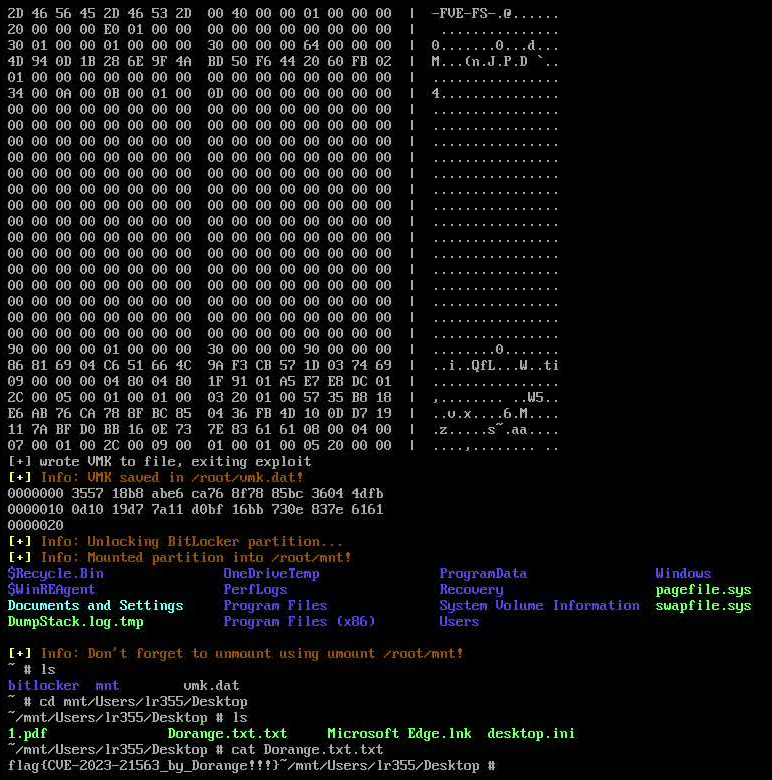 lr2006-robot/bitpixie
Cracking BitLocker encryption based on CVE-2023-21563 vulnerability
 gmh5225/driver-hwid-btbd-modified
Modified btbd HWID spoofer kernel driver that can be manually mapped to evade anti-cheat detection on Windows 1909.
 kh4sh3i/cve-2025-34152
Go-based PoC exploit for unauthenticated remote code execution on Shenzhen Aitemi M300 Wi-Fi repeaters. Includes a scanner and does not reboot the…
 steampunk424/cve-2025-36911-wisper_pair_target_finder
This is not an exploit for CVE-2025-36911!!! This is a detector for finding potentially vulnerable devices! Only use on your own devices! I am not…
 cipherx1802/cve-2025-69821-beat-xp-vega-smartwatch-security-assessment
A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…
 wojkos9/arm-cve-2020-29661
Exploit for ARM-based systems targeting CVE-2020-29661, providing a proof-of-concept for binary exploitation on embedded platforms.