
PcanExploit
 bertoldvdb/pcanexploit
CVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways
command-and-controlembedded-systems-securityexploitation+3
1
bertoldvdb/pcanexploitCVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways
 s-hamann/cve-2023-40289
Exploit for CVE-2023-40289, a command injection vulnerability in several Baseband Management Controllers (BMC) by with firmware by ATEN
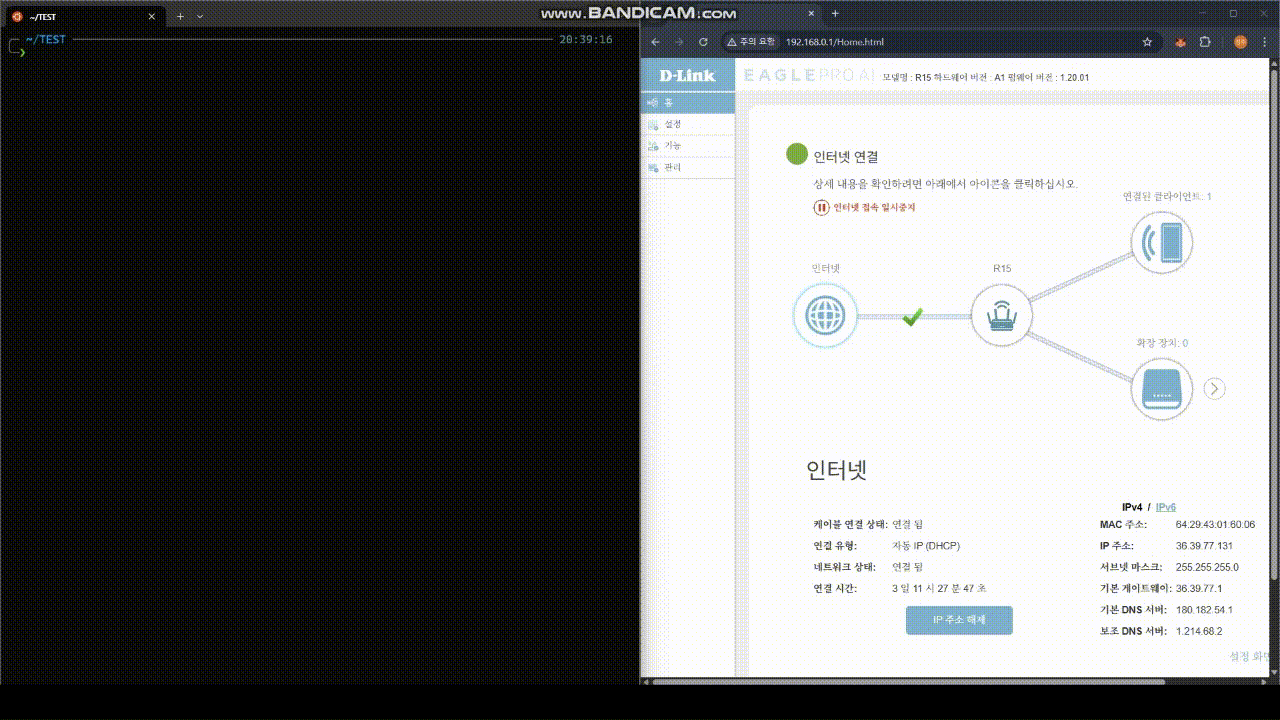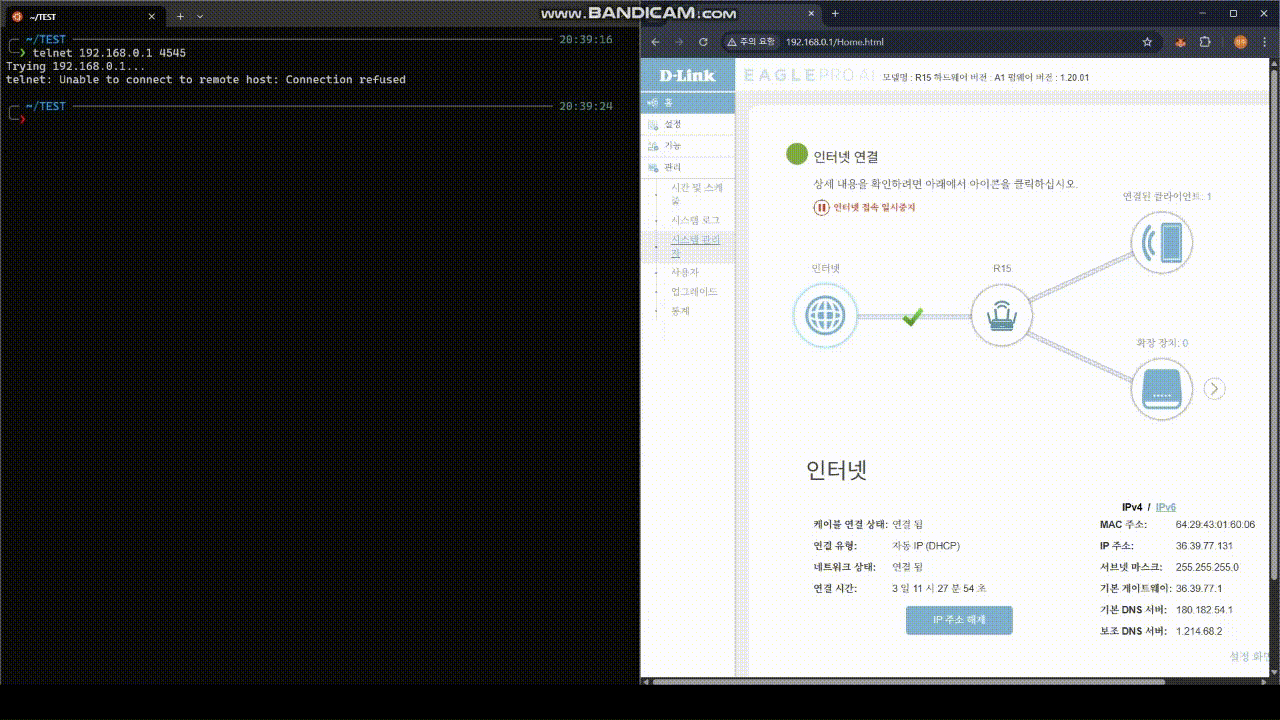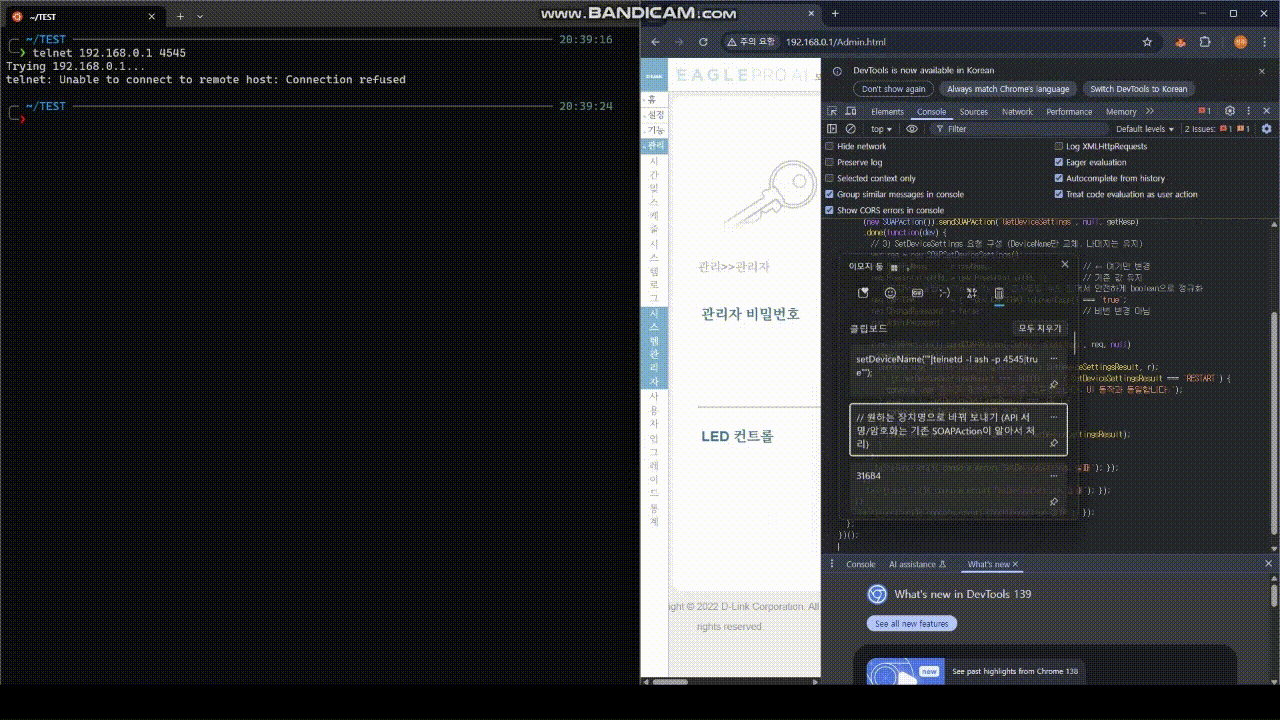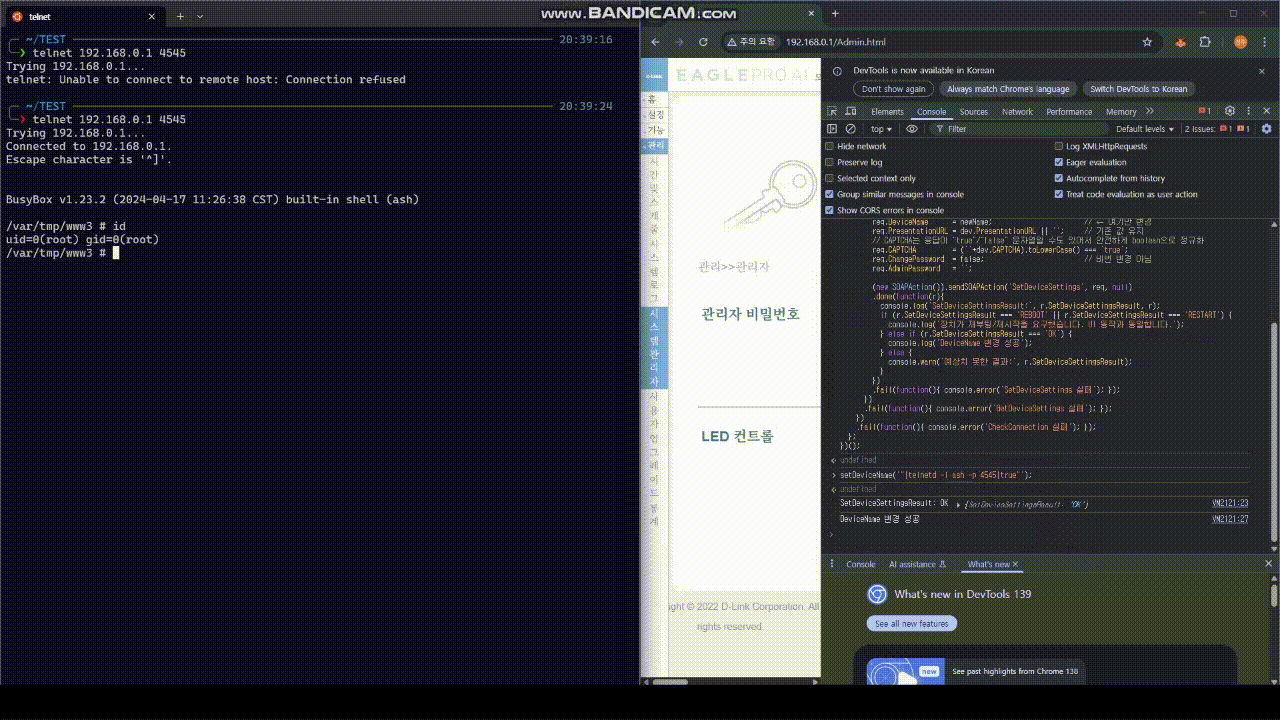 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 kiwidoggie/oni-framework
Embedded systems C2 software written in C/C#