
ThrottleStopPoC
 wqsv/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
binary-exploitationexploitationhardware-security+5
18
wqsv/throttlestoppocCVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 fxrstor/throttlestoppoc
CVE-2025-7771: Arbitrary physical memory and I/O port read/write via ThrottleStop driver
 ntgabrielgomes/cve-2023-20564
Proof-of-concept exploit for CVE-2023-20564 demonstrating arbitrary physical memory read/write via AMD Ryzen Master Driver IOCTL handlers, enabling…
 tc3650/cve-2026-43499-armv7
ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…
 freax13/cve-2024-21980-poc
Exploit for CVE-2024-21980 targeting AMD SEV firmware to decrypt arbitrary memory of decommissioned SEV-SNP guests via a command buffer enforcement…
 freax13/cve-2024-21978-poc
Exploit for AMD SEV-SNP firmware vulnerability CVE-2024-21978, enabling decryption of arbitrary guest memory via memory corruption of context pages.
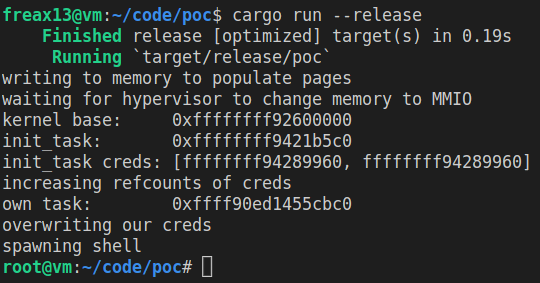 freax13/cve-2023-46813-poc
Proof-of-concept exploit for CVE-2023-46813 targeting AMD SEV-SNP. Escalates privileges by manipulating hypervisor memory type changes to swap task…
 freax13/cve-2023-31355-poc
Exploit for AMD SEV-SNP firmware vulnerability (CVE-2023-31355) that decrypts arbitrary memory of decommissioned guests by corrupting the UMC key…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 imnot-ye/cve-2019-17147
Comprehensive reverse engineering and exploitation of CVE-2019-17147, a stack buffer overflow in TP-Link TL-WR841N routers. Includes firmware…
 fzrsllasher/cve-2026-14960-cve-2026-14961
Technical advisory detailing two privilege escalation vulnerabilities (CVE-2026-14960, CVE-2026-14961) in the Pegatron TdeIo64 driver, enabling…
 fengjixuchui/cve-2019-18845
The MsIo64.sys and MsIo32.sys drivers in Patriot Viper RGB before 1.1 allow local users (including low integrity processes) to read and write to…
 crackercat/cve-2021-44852
An issue was discovered in BS_RCIO64.sys in Biostar RACING GT Evo 2.1.1905.1700. A low-integrity process can open the driver's device object and…
 cwjchoi01/cve-2025-66678
Proof-of-concept exploit for CVE-2025-66678 demonstrating arbitrary MSR and physical memory read/write via a vulnerable hardware utility driver to…
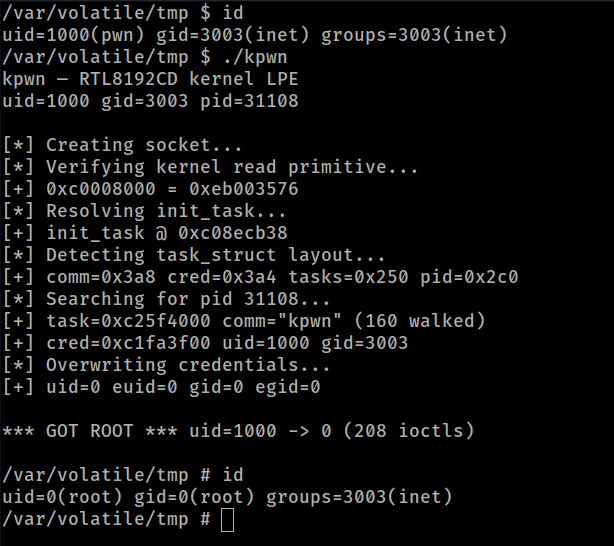 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 puglia-ryan/s-v-project-implementation-of-cve-2015-3256
Reproducible crash proof-of-concept for CVE-2015-3456 (VENOM) targeting QEMU's virtual floppy disk controller. Demonstrates guest-controlled writes…
 christbowel/cve-2026-56111
Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…
 freax13/cve-2023-31346-poc
Proof-of-concept demonstrating memory leaks in AMD SEV-SNP firmware guest message headers and CPUID request, enabling extraction of sensitive guest…