
PoC_CVE-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…

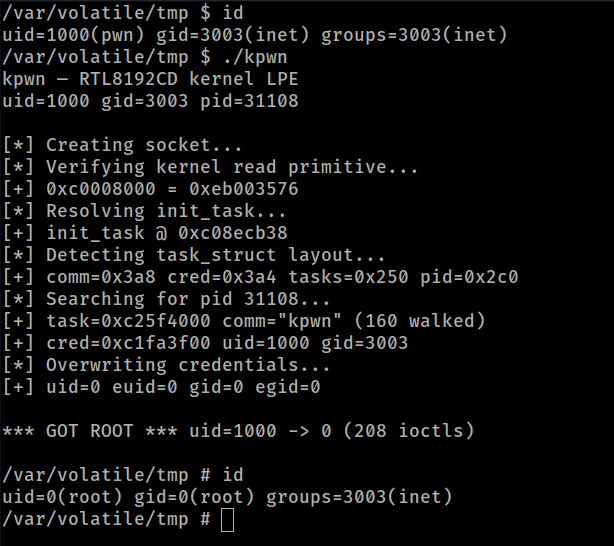
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls

CVE-2026-35904 / CVE-2026-35905 / CVE-2026-35906 — Unauth RCE, Hardcoded Root Creds & Telnet Enable in T3 Technology CPE

Technical details and publication about CVE-2026-38698 and CVE-2026-38699

A security assessment of the Beat XP VEGA Smartwatch (Firmware RB303ATV006229) focused on Bluetooth Low Energy (BLE) connectivity revealed a design…

Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…

Proof-of-concept exploit for a buffer overflow vulnerability in H3C Magic B1STW router's SetAPInfoById function, causing web service crash and…

Exploit for ARM-based systems targeting CVE-2020-29661, providing a proof-of-concept for binary exploitation on embedded platforms.

CVE-2025-57428

CVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways

Exploit for CVE-2023-40289, a command injection vulnerability in several Baseband Management Controllers (BMC) by with firmware by ATEN

Proof-of-concept exploit for CVE-2022-43096, demonstrating local root access via UART port on Mediatrix 4102 devices before v48.5.2718.

Proof-of-concept for CVE-2025-63895: Bluetooth Classic LMP buffer overflow exploitation in JXL 9-inch Android car infotainment systems, enabling…

Proof-of-concept exploit for CVE-2025-45467, demonstrating remote code execution on Unitree Go1 robotic dogs via insecure MD5-based firmware…

Proof-of-Concept for CVE-2025-2082, demonstrating function pointer overwrite via signed-to-unsigned integer conversion bug in Tesla VCSEC, leading to…

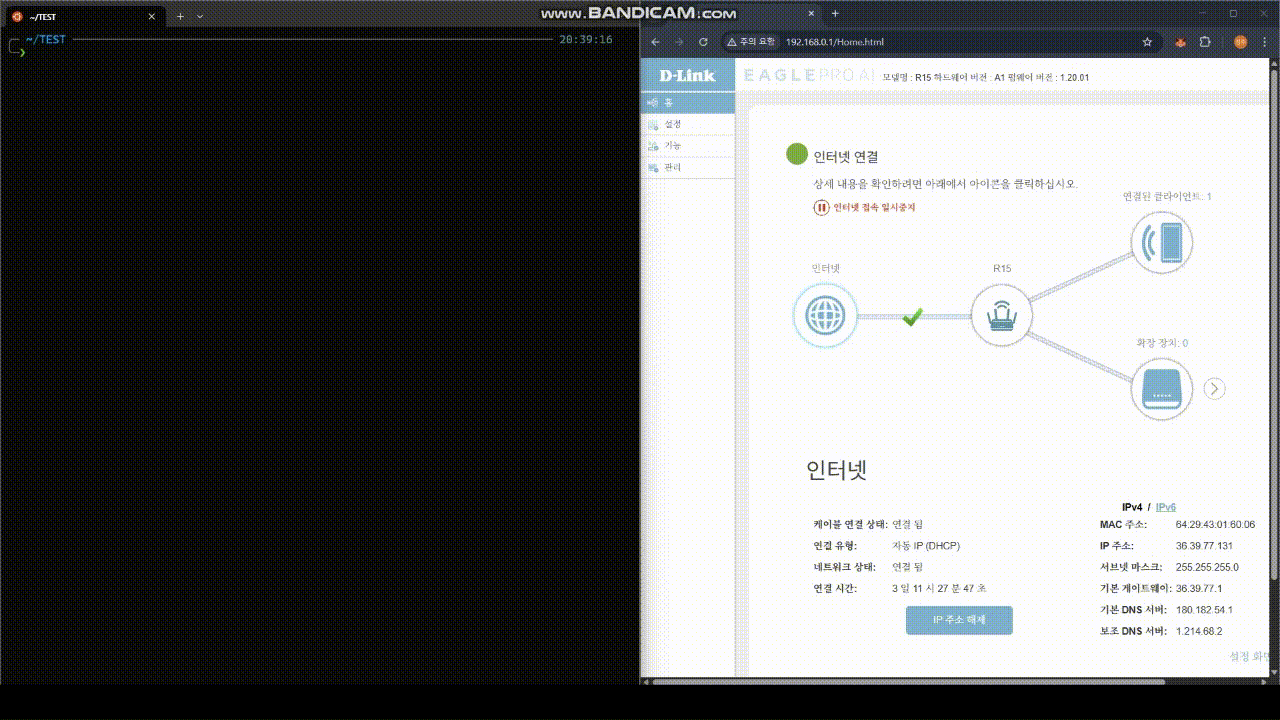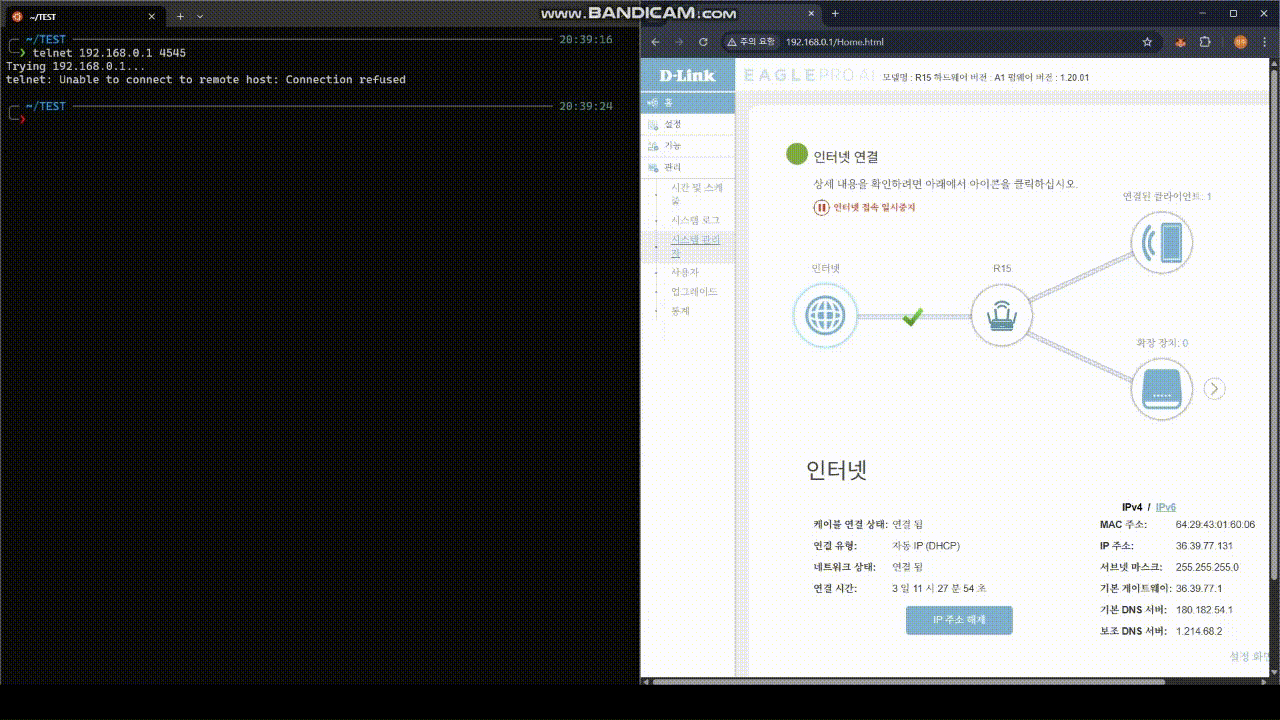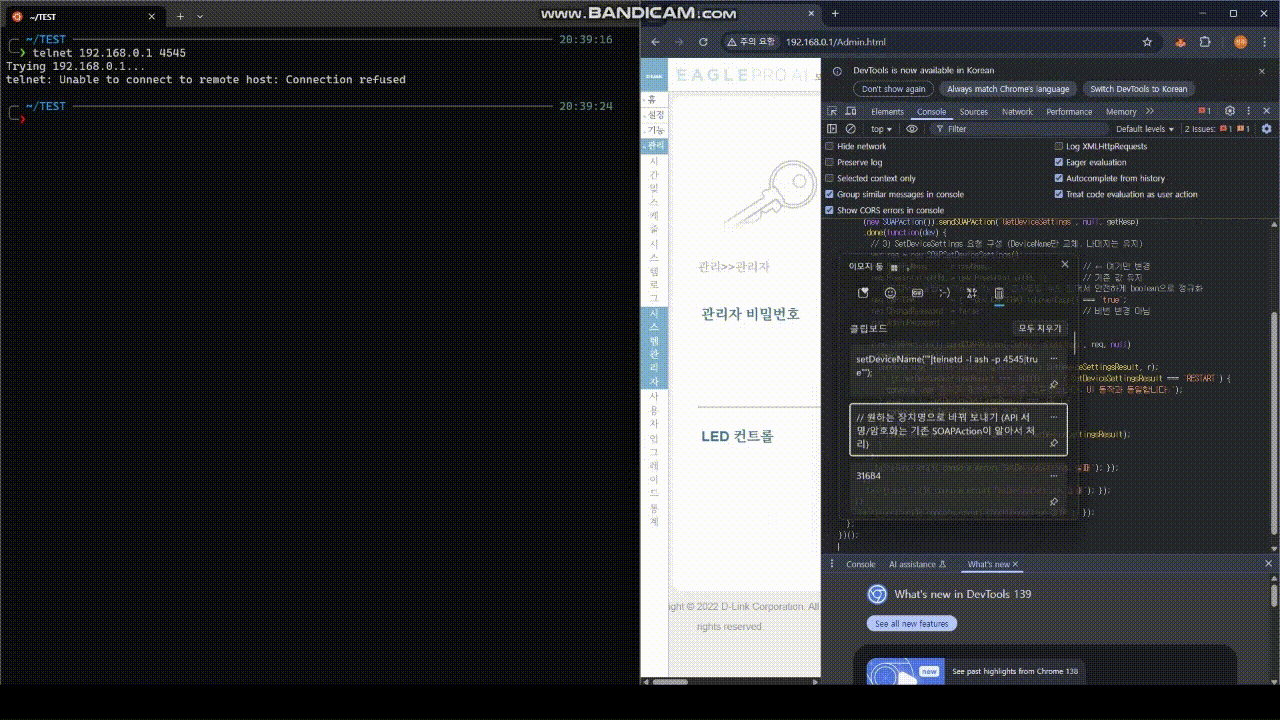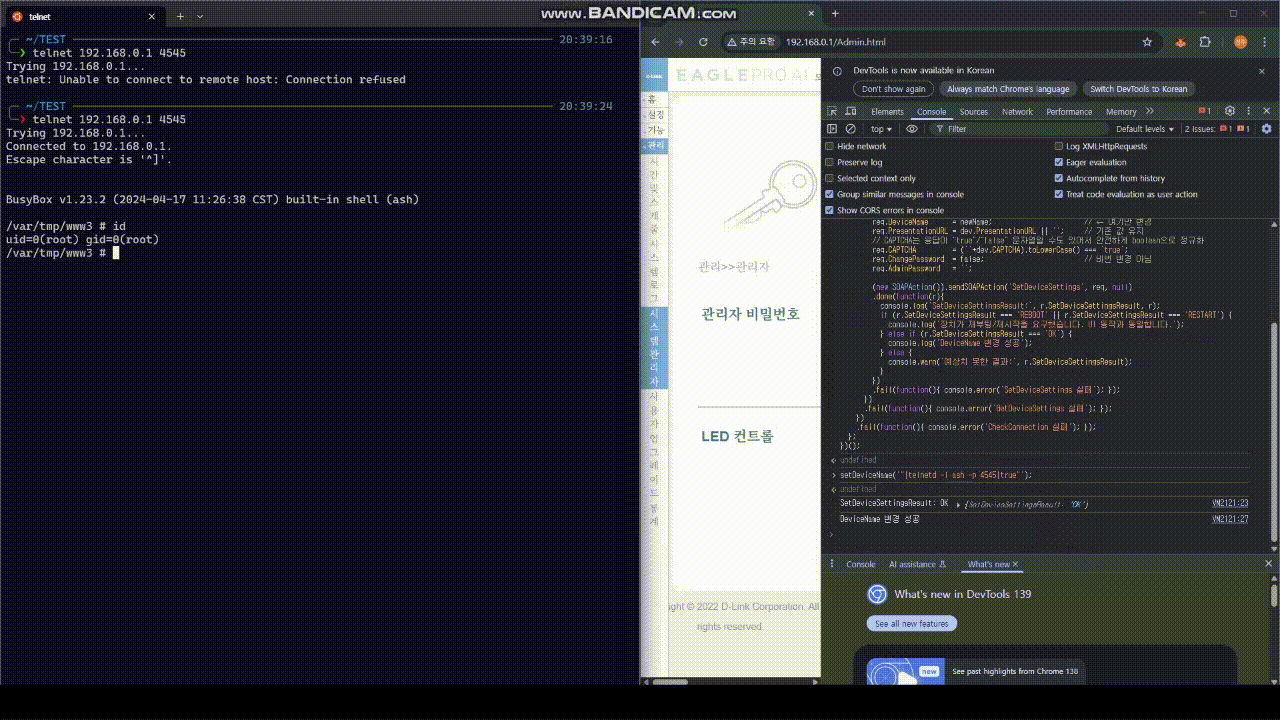
D-link AX1500 Vulnerability

Exploit setup for CVE-2025-7545 targeting vulnerable Binutils in firmware environments, including environment configuration and PDF documentation.

Advisory for CVE-2025-65731