

 a13xp0p0v/kernel-hardening-checker
A tool for checking the security hardening options of the Linux kernel
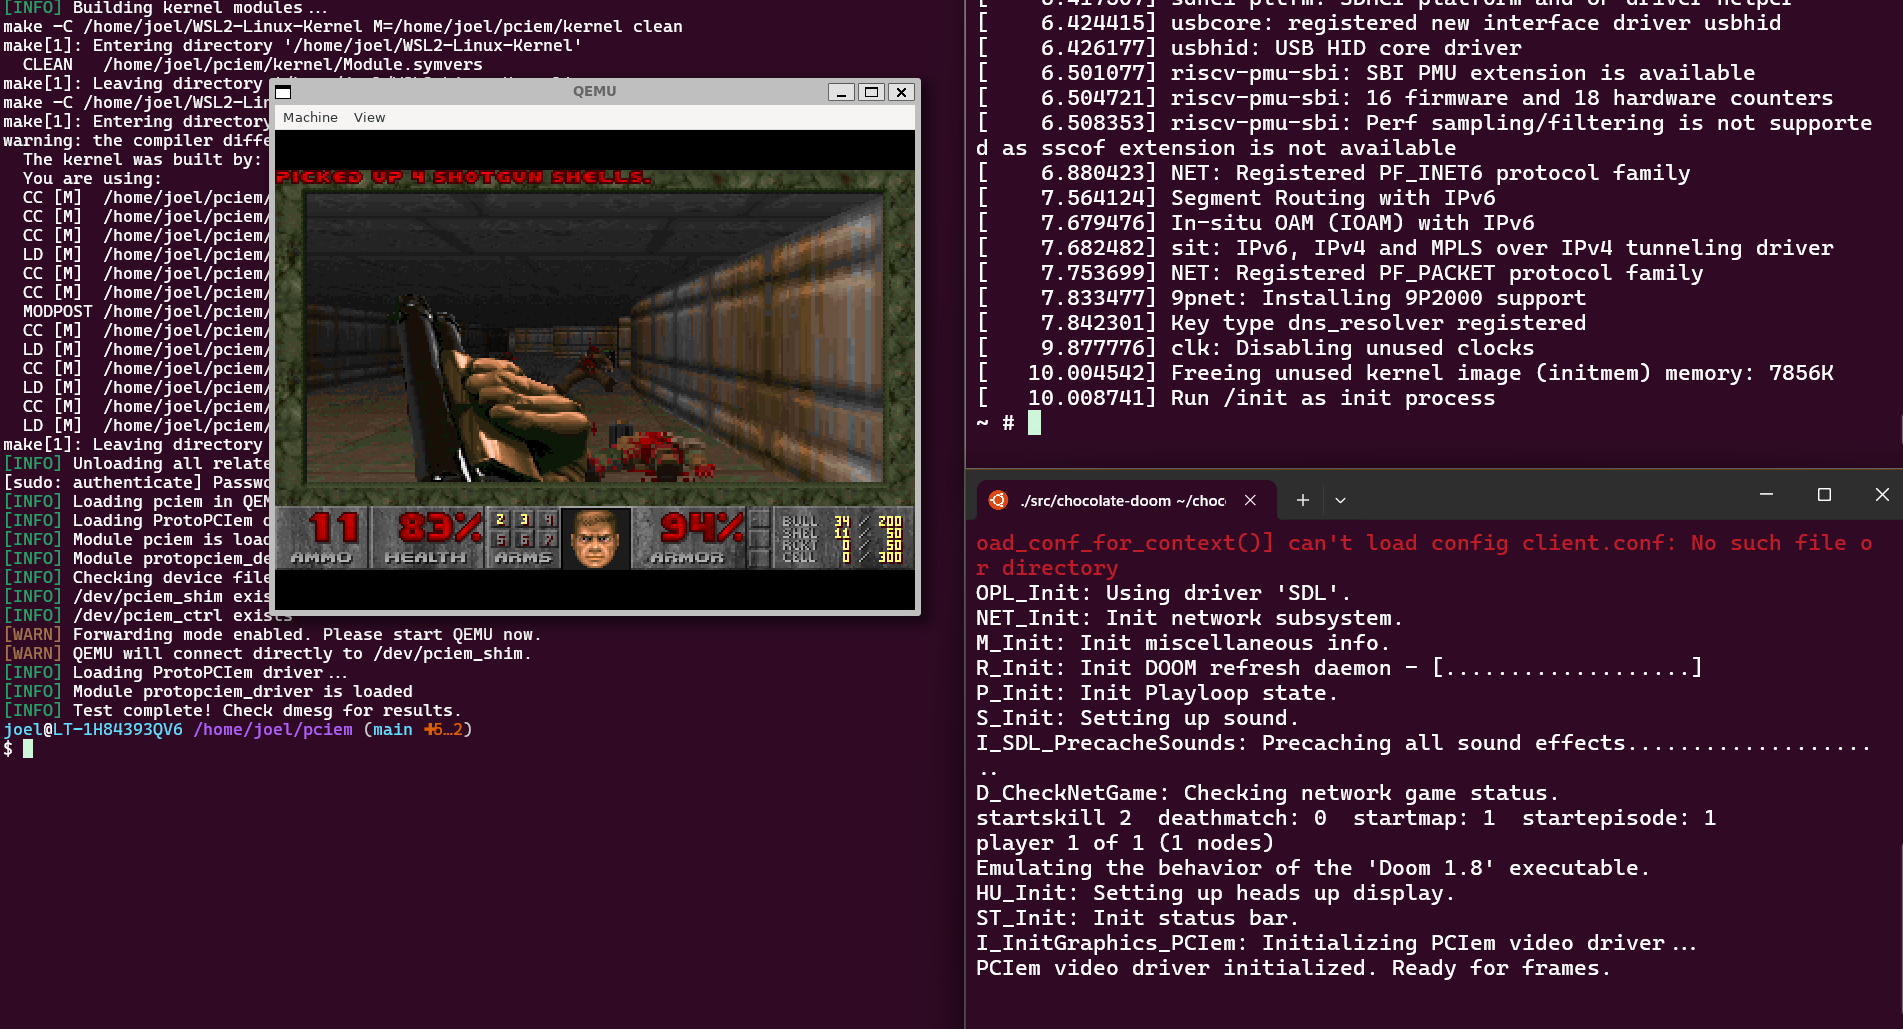 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.

 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
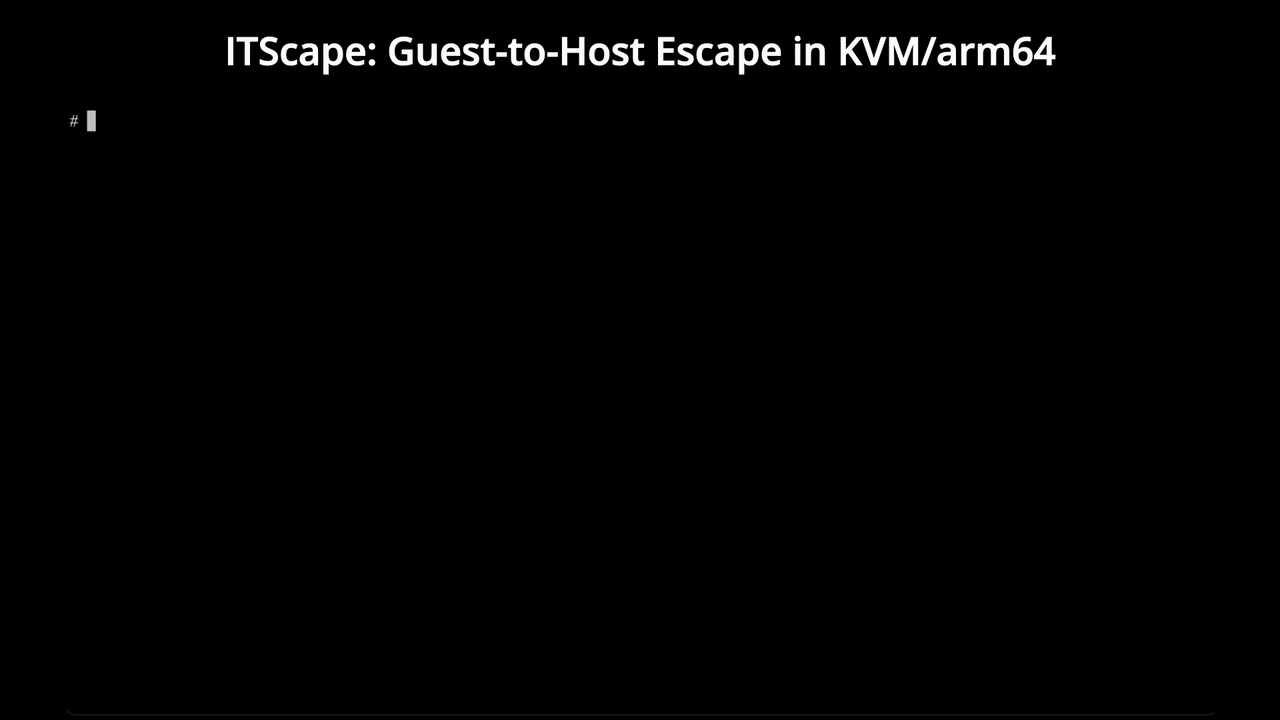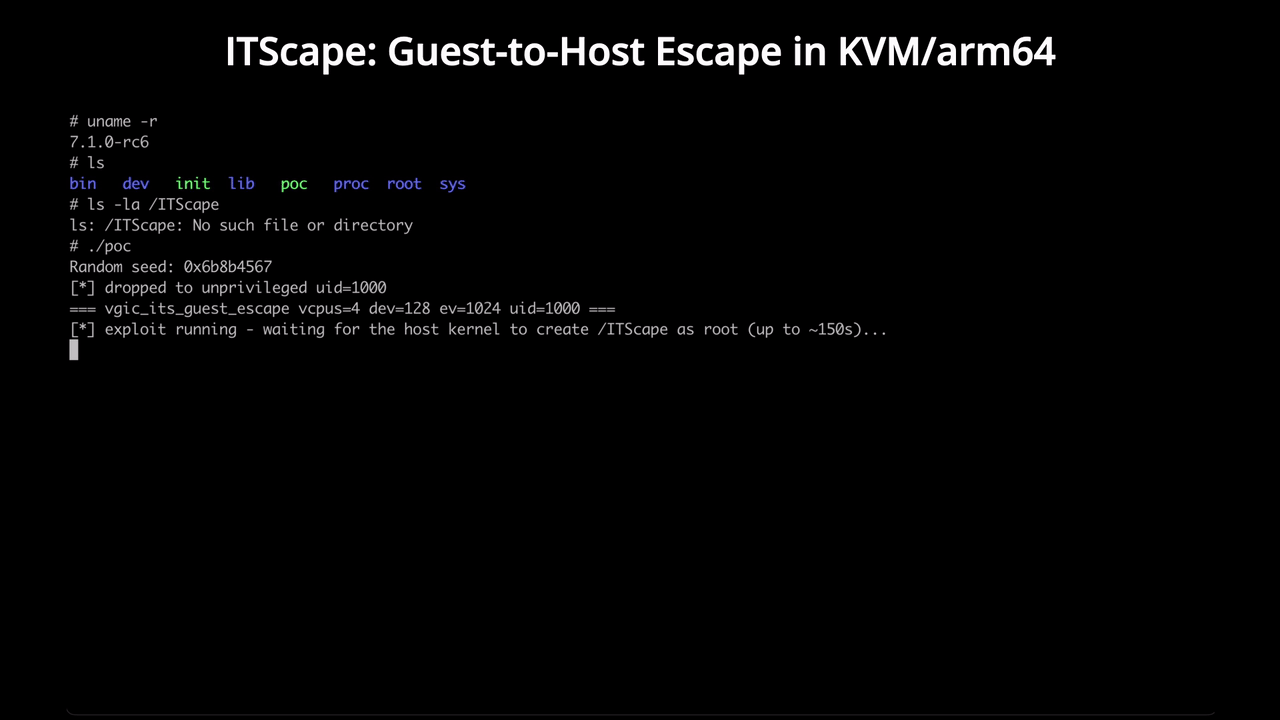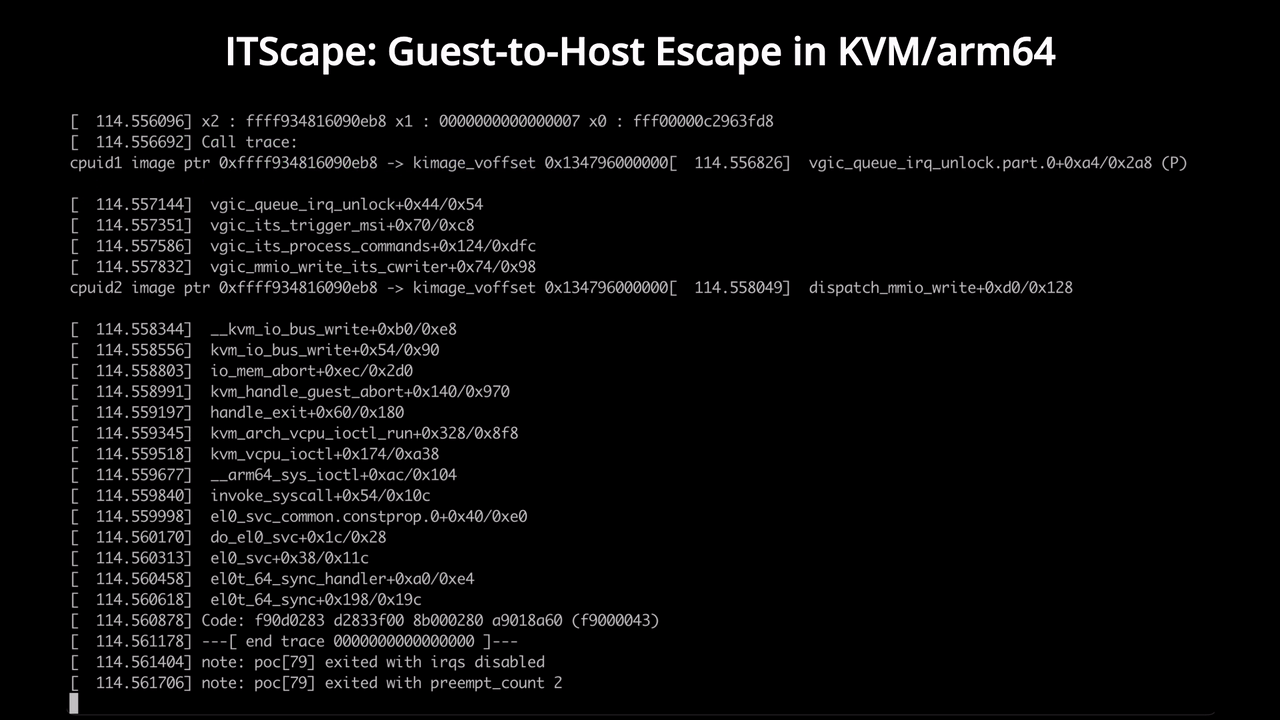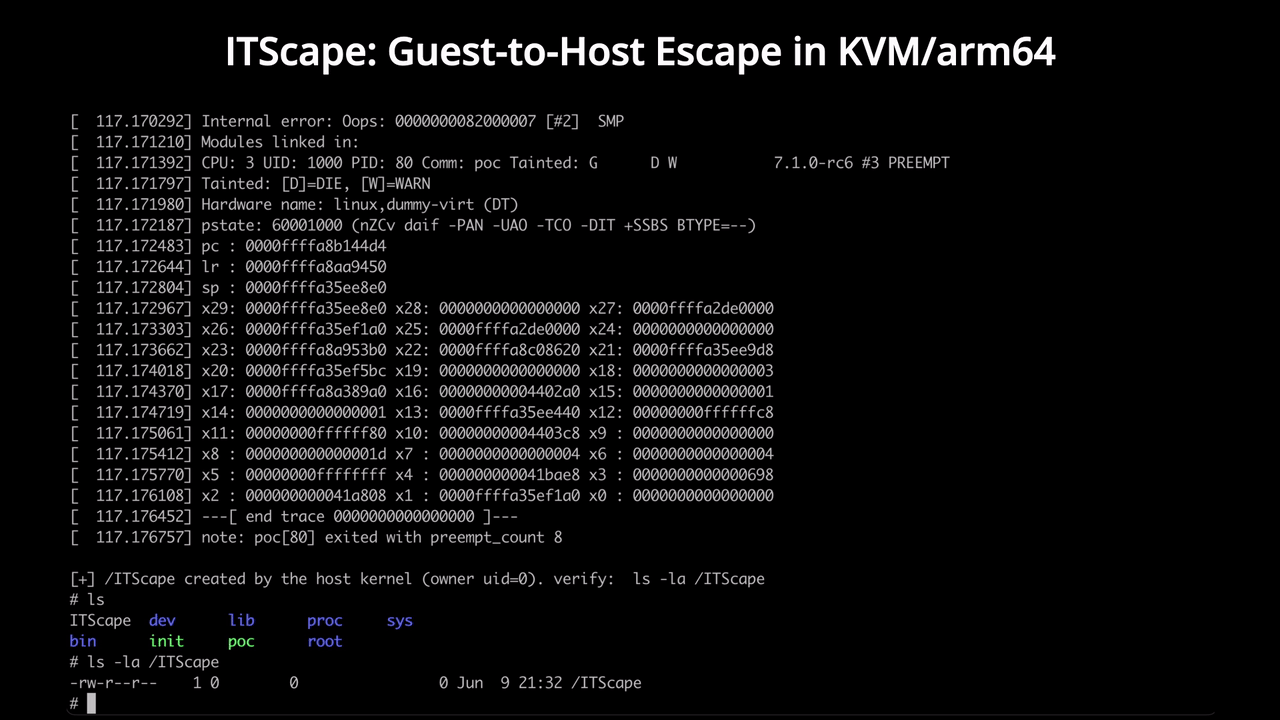 v4bel/itscape
CVE-2026-46316 guest-to-host KVM/arm64 escape exploit exploiting a race condition in vGIC-ITS emulation to achieve host kernel code execution from an…
 tc3650/cve-2026-43499-armv7
ARM32 Linux kernel privilege escalation exploit for CVE-2026-43499 (GhostLock futex UAF) targeting Huawei Watch 4 Pro with multiple exploitation…
 adriancable/eternal
Minimal machine architecture with LLVM compiler backend, Linux port, and virtual machine for creating self-contained software capsules that remain…
 fusion1110/ebpf-hid_guard
Linux kernel-space HID injection attack detector using eBPF. Monitors USB and Bluetooth HID devices for anomalous keystroke timing and automatically…
 analyticeth/chronomaly-webos
CVE-2025-38352 kernel exploit for LG webOS Smart TVs (ARM64). Achieves persistent root on real consumer hardware with novel exploitation techniques.…
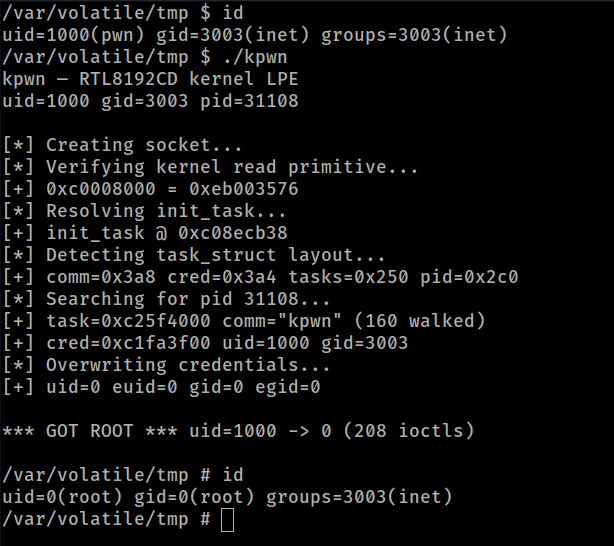 totekuh/cve-2026-36355
CVE-2026-36355: Realtek rtl819x Jungle SDK - Unauthenticated Kernel Memory Read/Write via Debug ioctls
 wkoszek/emuko
RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
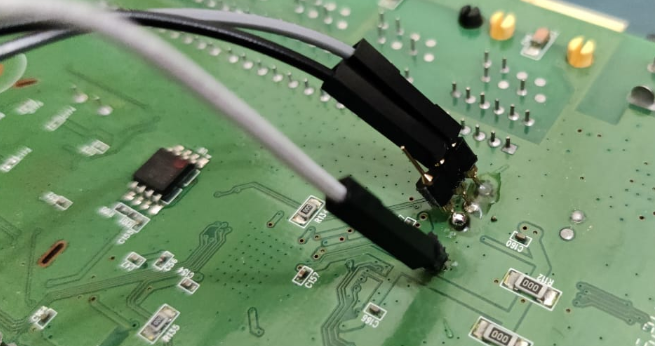 whitej3rry/cve-2025-65731
Advisory for CVE-2025-65731
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
 cryptodev-linux/cryptodev-linux
Linux kernel device driver providing user-space access to hardware cryptographic accelerators, enabling reuse of kernel-space ciphers for accelerated…
 14mb1v45h/cve-2025-38676
Stack buffer overflow during cmdline parsing
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 freax13/cve-2023-20573-poc
Proof-of-concept demonstrating CVE-2023-20573: a hardware vulnerability in AMD SEV-SNP that allows exception reinjection suppression in KVM, enabling…