

OpenSC
 opensc/opensc
Open source smart card tools and middleware. PKCS#11/MiniDriver
authenticationcryptographyencryption-decryption-tools+2
opensc/openscOpen source smart card tools and middleware. PKCS#11/MiniDriver
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 christopher-leese/cve-2015-1187-dir820l-firmware-reverse-engineering
Static firmware reverse engineering of CVE-2015-1187: unauthenticated command injection in D-Link DIR-820L. MIPS root filesystem extraction with…
 christbowel/cve-2026-56111
Proof-of-concept exploit for CVE-2026-56111, an out-of-bounds write in the M421 G-code handler of Marlin Firmware, demonstrating constrained memory…
 cashapp/pivit
Manage x509 certificates on PIV-enabled YubiKeys, generate keys and certificate requests, and sign or verify git commits and files.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 cispa/trevex
Automated Vulnerability Detection Framework for Transient Execution Vulnerabilities (IEEE S&P '26)
 yt2w/cve-2025-9961
Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
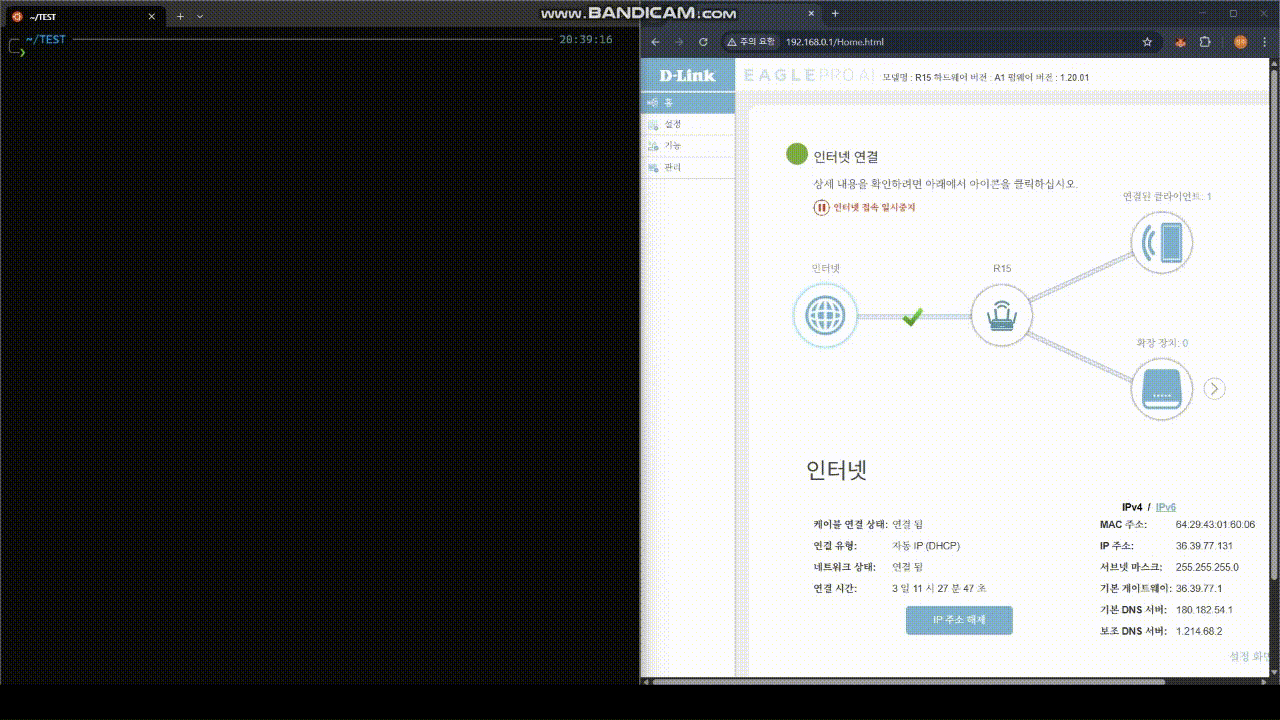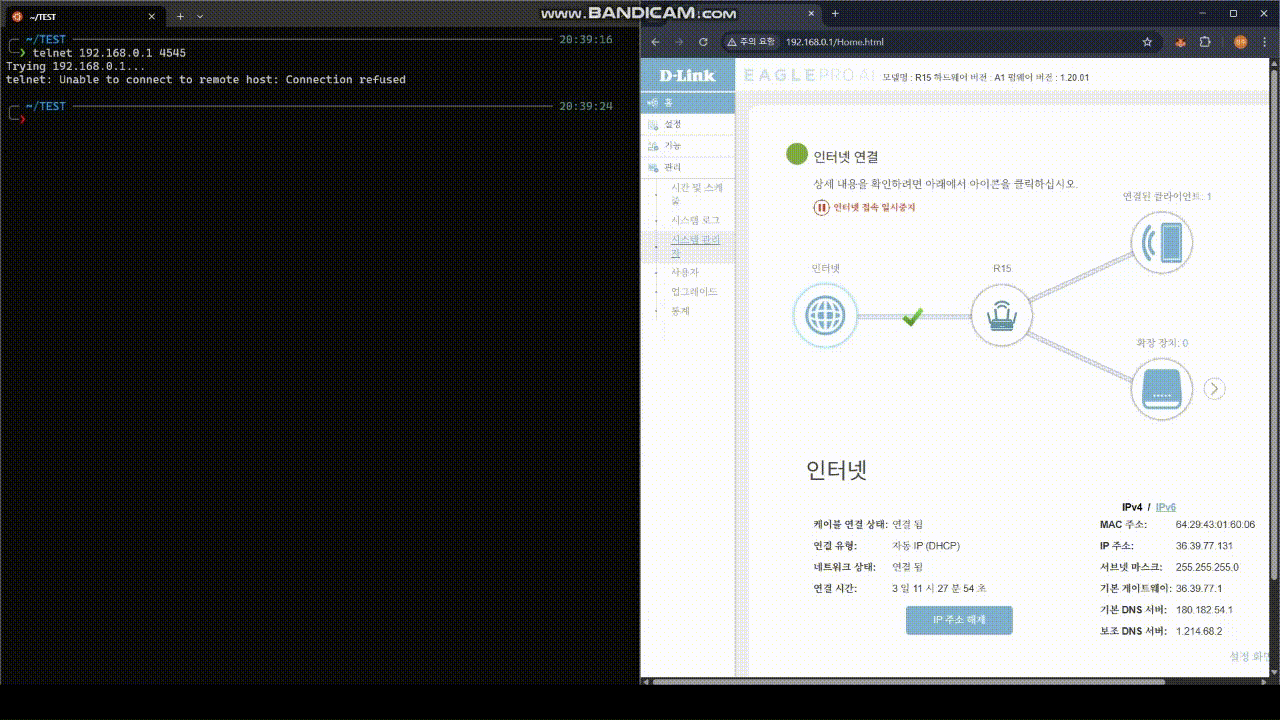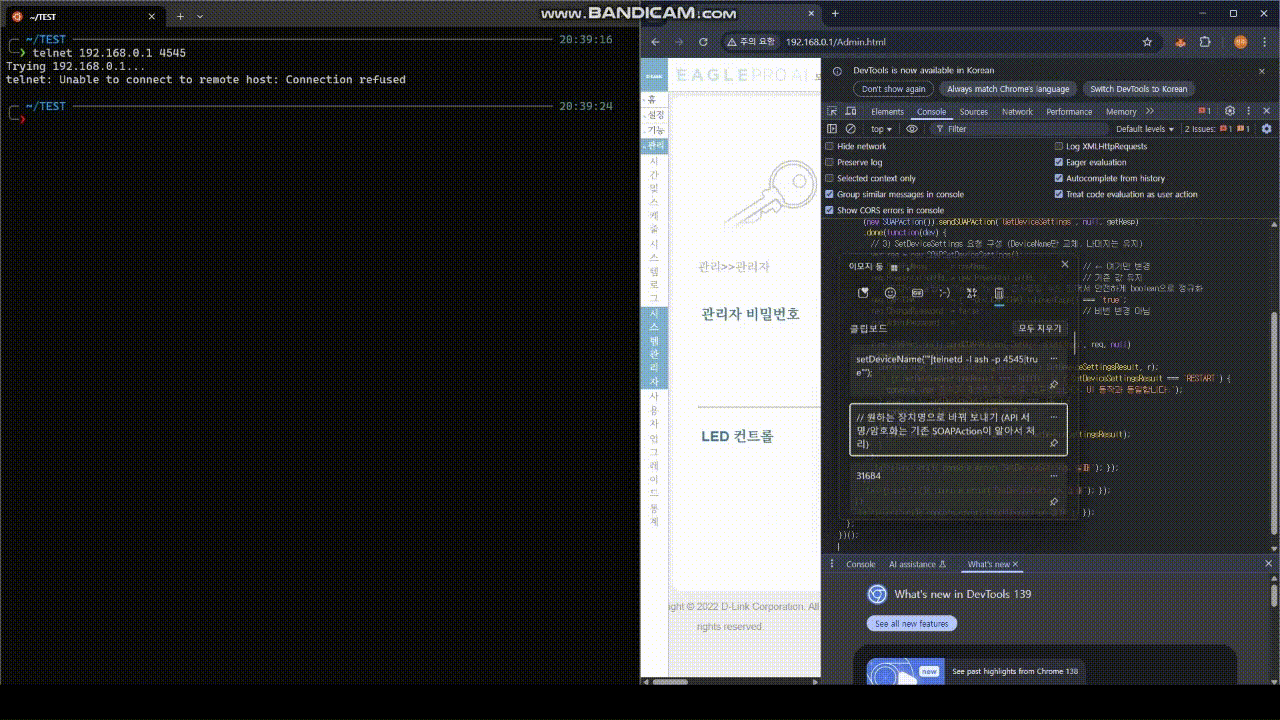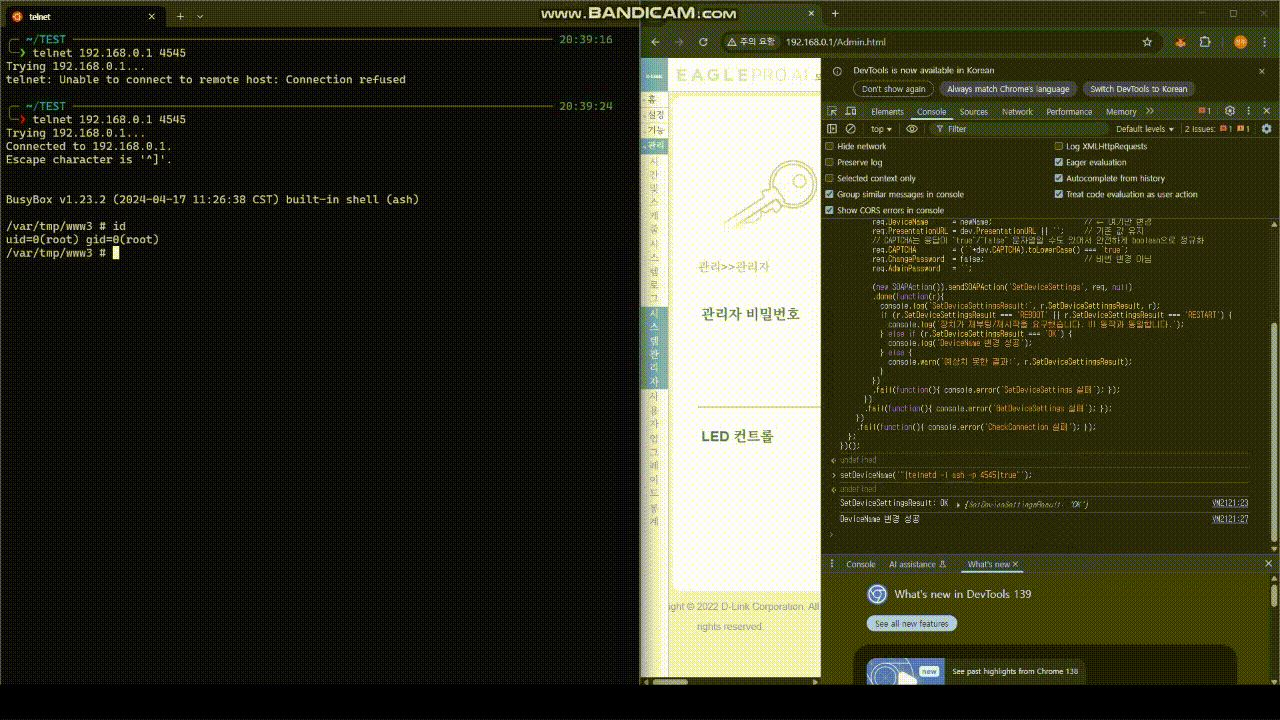 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability
 jaden-bowers/tenda-router-vr-and-exploit
Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.
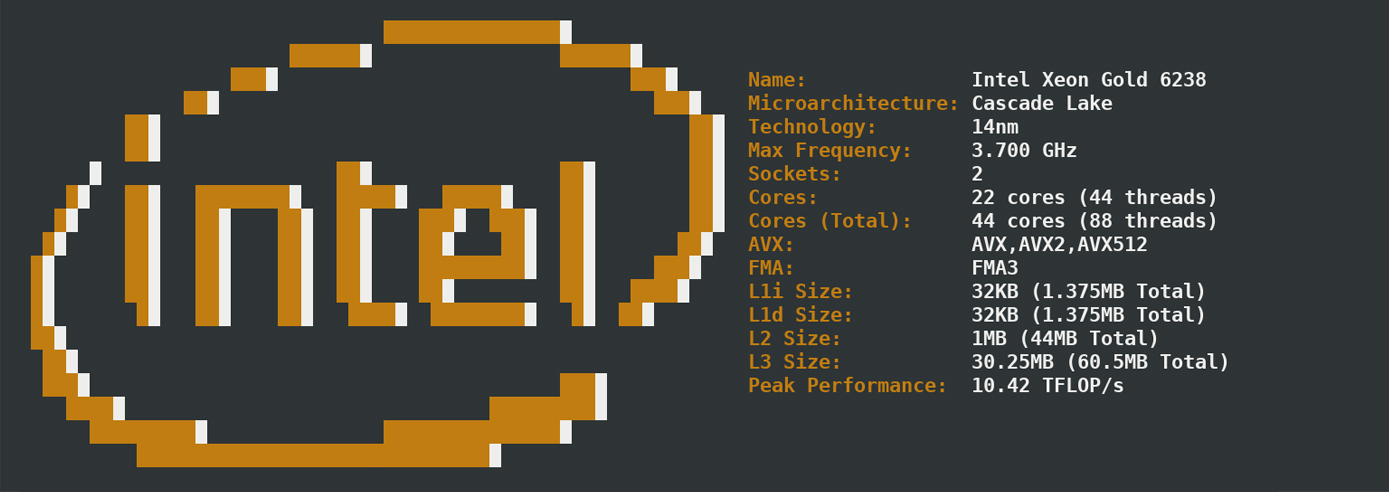 dr-noob/cpufetch
Simple yet fancy CPU architecture fetching tool
 s-hamann/cve-2023-40289
Exploit for CVE-2023-40289, a command injection vulnerability in several Baseband Management Controllers (BMC) by with firmware by ATEN
 kristof-mattei/gardyn-hack
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 mselbrede/gardyn
CVE-2025-29628, CVE-2025-29629, CVE-2025-29630, CVE-2025-29631
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
 bertoldvdb/pcanexploit
CVE-2024-44610: Authenticated remote root exploit in Peak PCAN-Ethernet CAN-(FD) gateways
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…