
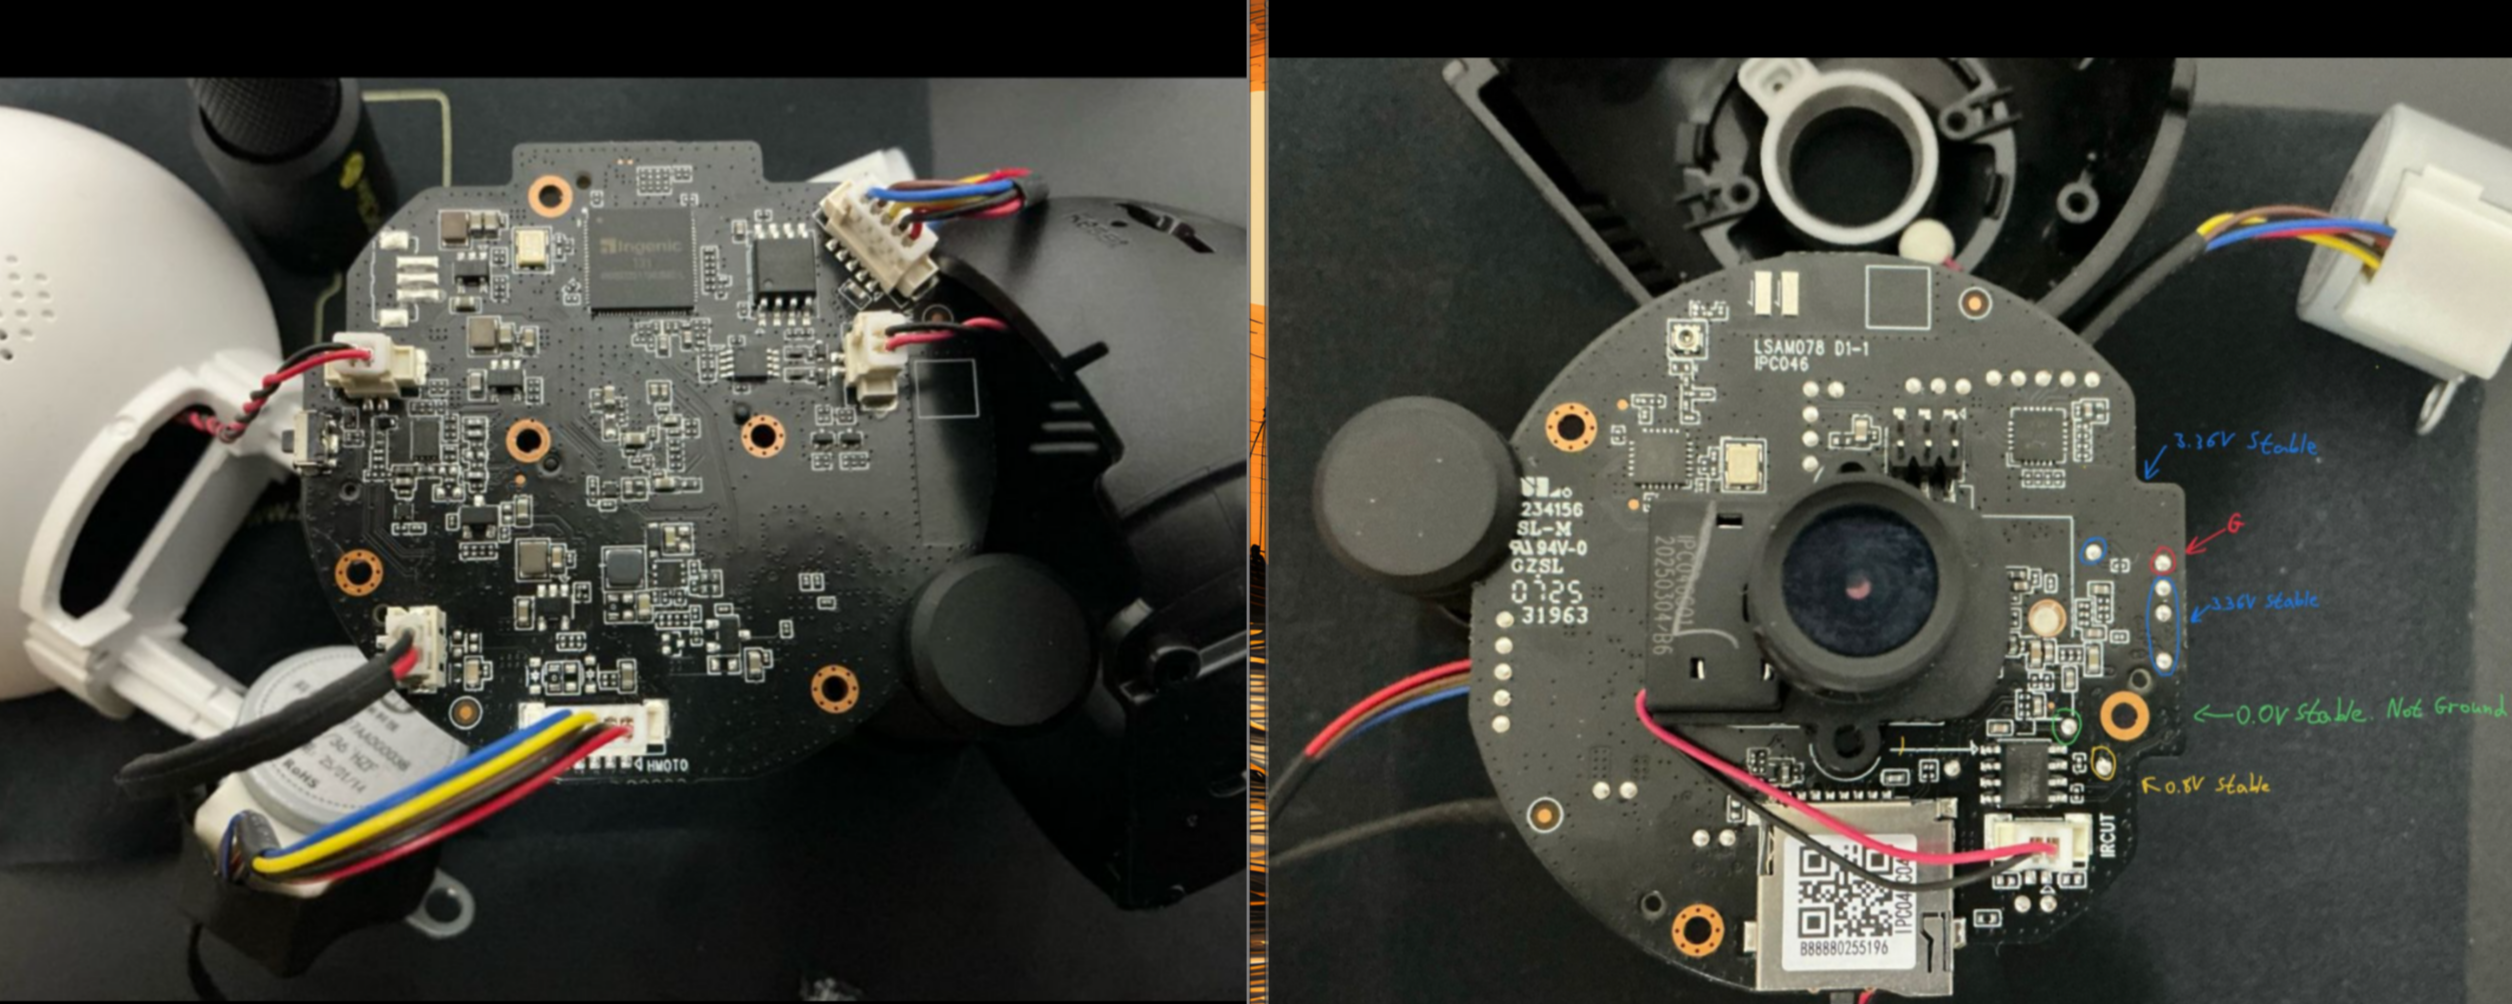
Xiaomi-C200-Firmware-Analysis
 h3xdum/xiaomi-c200-firmware-analysis
From UART to Root: Breaking Into the Xiaomi C200 via U-Boot
data-recoveryembedded-systems-securityexploitation+6
12
h3xdum/xiaomi-c200-firmware-analysisFrom UART to Root: Breaking Into the Xiaomi C200 via U-Boot
 ioallocate/immapper
Demonstration of Abusing the Vulnerable driver AmdTools64.sys for Physical R/W.
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 roxanne_ardary/ai-and-the-automobile
Curated collection of open specifications for AI-integrated vehicle systems, covering autonomy, perception, navigation, energy management, safety,…
 chrisneagu/ftc-skystone-dark-angels-romania-2020
NOTICE This repository contains the public FTC SDK for the SKYSTONE (2019-2020) competition season. If you are looking for the current season's FTC…
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 k3vinlusec/r7000_httpd_bof_cve-2020-15416
Walkthrough of CVE-2020-15416 buffer overflow exploit for Netgear R7000 router, including QEMU user-mode debugging environment setup and detailed…