
Podroid
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
android-securitycontainer-securityhardware-iot-security+3
3.5k19 days ago
extv/podroidA rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 snawoot/hisilicon-dvr-telnet
PoC materials for article https://habr.com/en/post/486856/
 synacktiv/samsung-q60t-exploit
Exploit suite targeting Tizen-based Samsung Q60T TV, including v8 and kernel exploits, firmware decryption, and root shell access via payload…
 fullspectrumdev/rancidcrisco
Proof-of-concept exploit for CVE-2023-20126 targeting Cisco SPA phone adapters. Uploads malicious firmware to gain a root shell on port 23000/tcp via…
 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 analyticeth/tesla-security-research
Vulnerability research on Tesla Model 3/Y infotainment systems. 6 vulnerabilities, 4 CVEs (CVE-2022-42005 through CVE-2022-42008). Root shell,…
 full-disclosure/cve-2021-44827
Proof-of-concept exploit for authenticated remote code execution (CVE-2021-44827) targeting TP-Link Archer C20i routers. Provides post-exploitation…
 jet-pentest/cve-2020-25749
Proof-of-concept exploit for CVE-2020-25749 targeting Rubetek cameras with hardcoded Telnet credentials, enabling remote root shell access and full…
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
 cr0n1c/dlink_shell_poc
Dlink 615/815 shell PoC
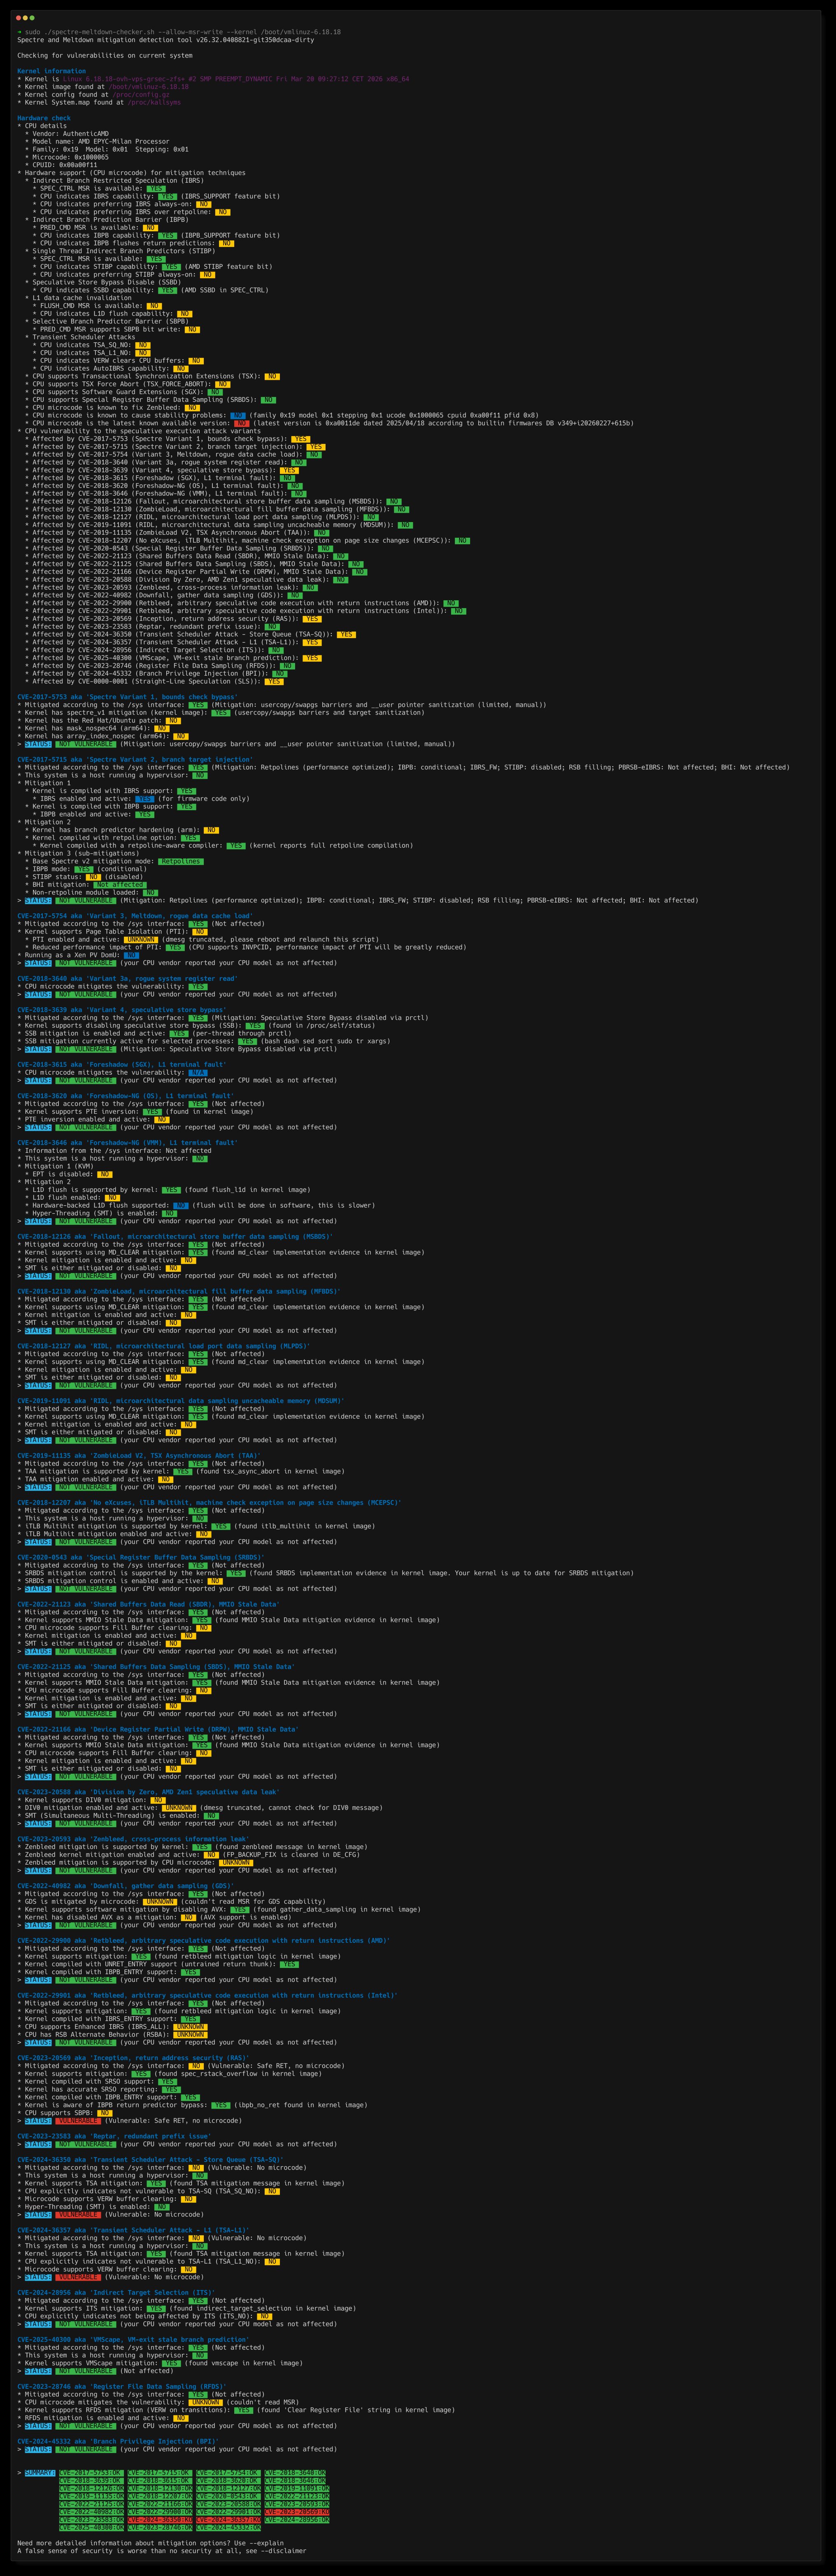 speed47/spectre-meltdown-checker
Reptar, Downfall, Zenbleed, ZombieLoad, RIDL, Fallout, Foreshadow, Spectre, Meltdown vulnerability/mitigation checker for Linux & BSD
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
