
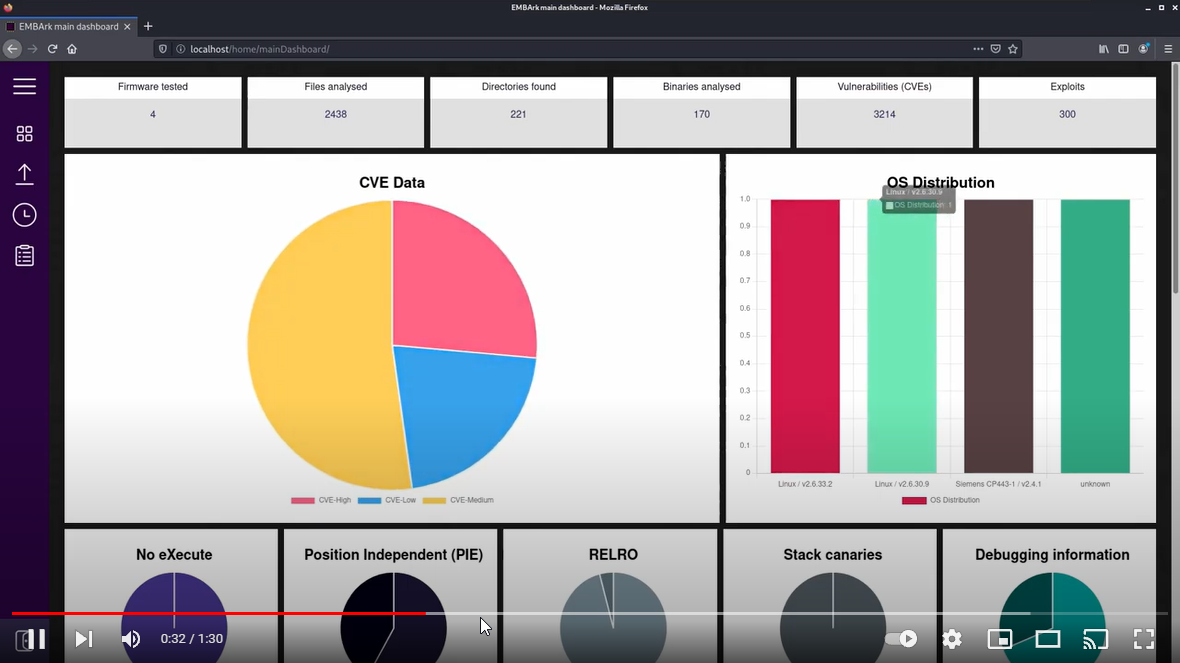
embark
 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
embedded-systems-securityfirmware-analysishardware-iot-security+3
395
e-m-b-a/embarkCentralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 1n3/supermicro-password-scanner
Supermicro IPMI/BMC Cleartext Password Scanner
 lakwsh/cve-2020-8597
Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
 antecursor/antecursor
Autonomous and modular system for network based information gathering and exploitation. WEB interface here: https://antecursor.fr/ More info…
 my0723/cnvd-2022-27366__cve-2023-37621
Exploit for CVE-2023-37621 targeting unauthorized access in Fronius Datalogger Web 2.0.5-4, allowing attackers to retrieve sensitive device…
 yash-chandna/cve-2024-34463
Proof-of-concept exploit for CVE-2024-34463 targeting insufficient Bluetooth security in BPL Smart Weighing Scale PWS-01-BT. Includes BLE scanner and…
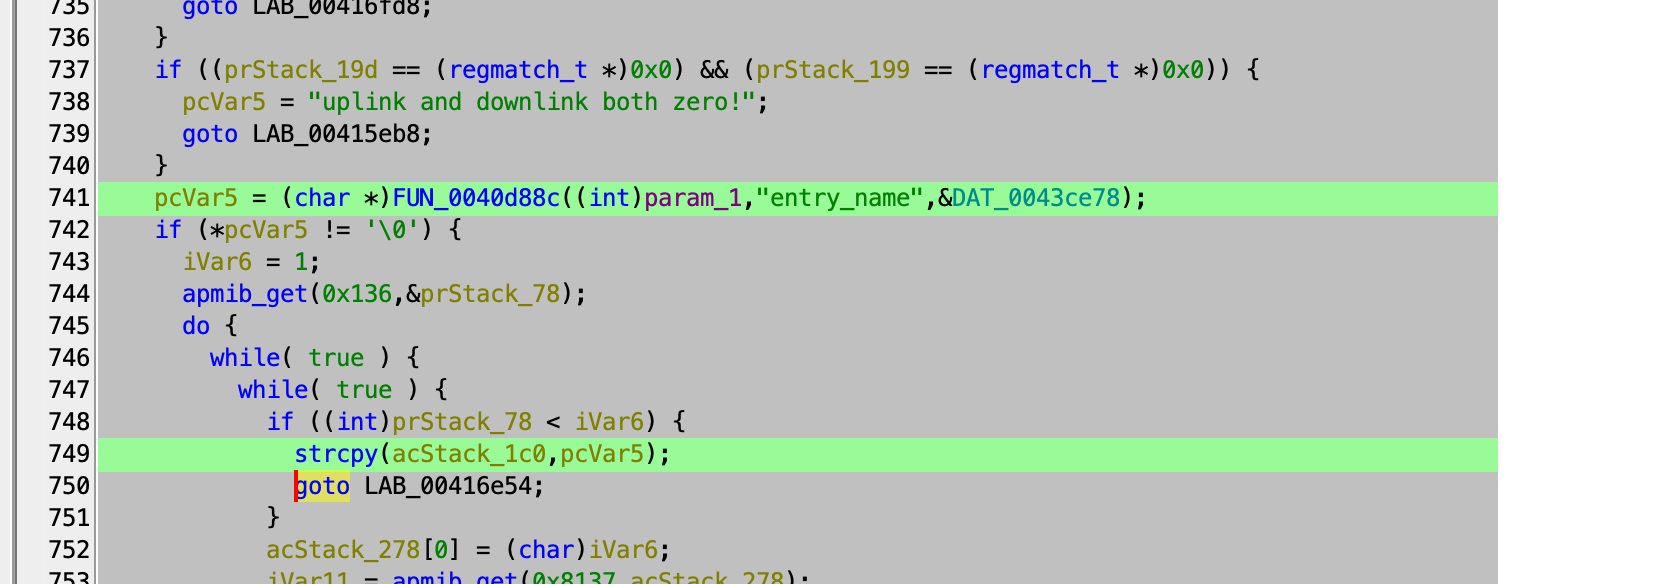 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 smittix/intercept
iNTERCEPT, a free and open-source platform that unites the best signal intelligence tools into a single, accessible interface.
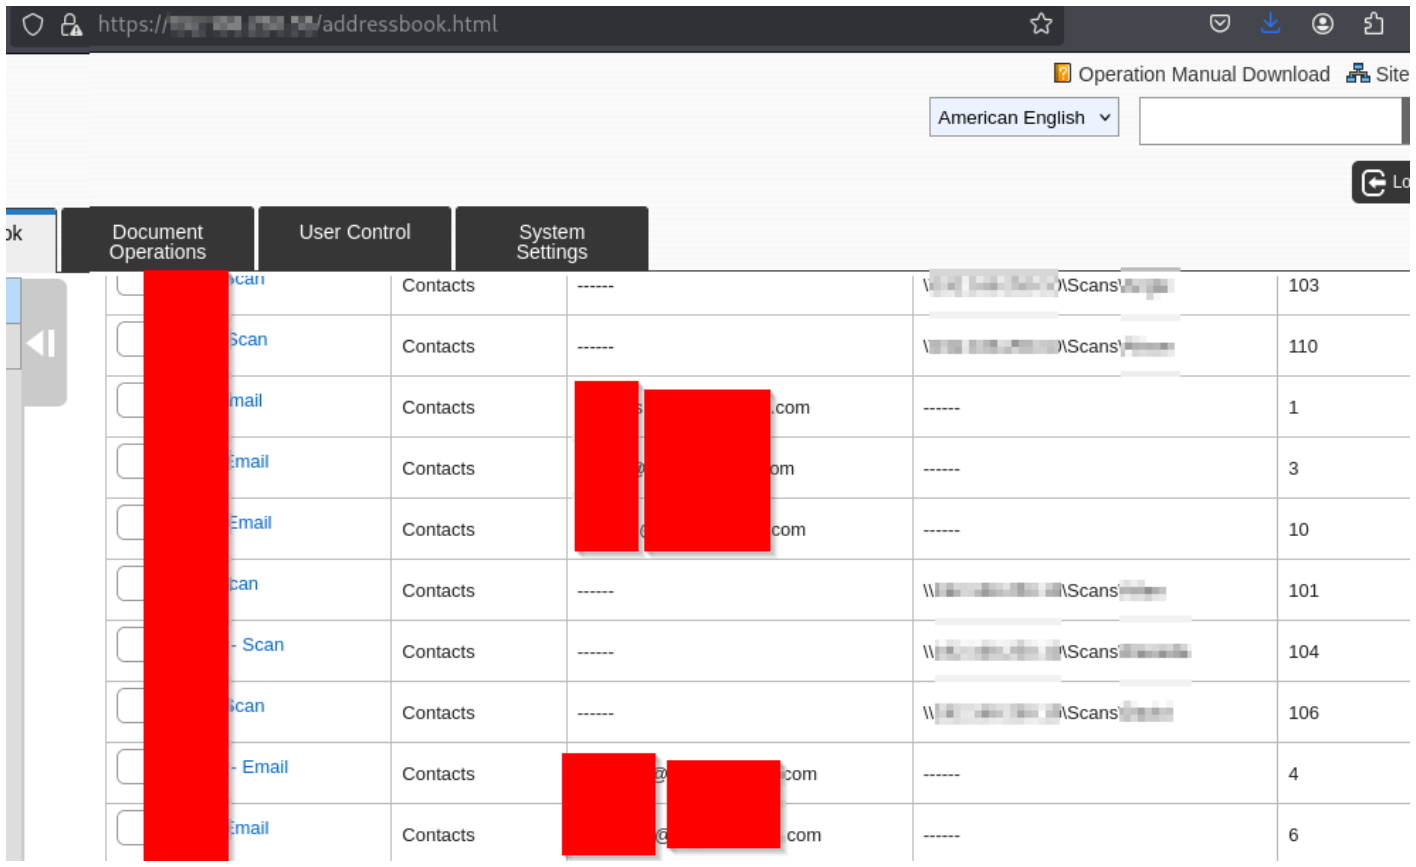 redr0nin/cve-2026-63563
Unauthenticated Address Book Modification on Sharp MX/BP Multifunction Printers
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 joelczk/cve-2025-52688
Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
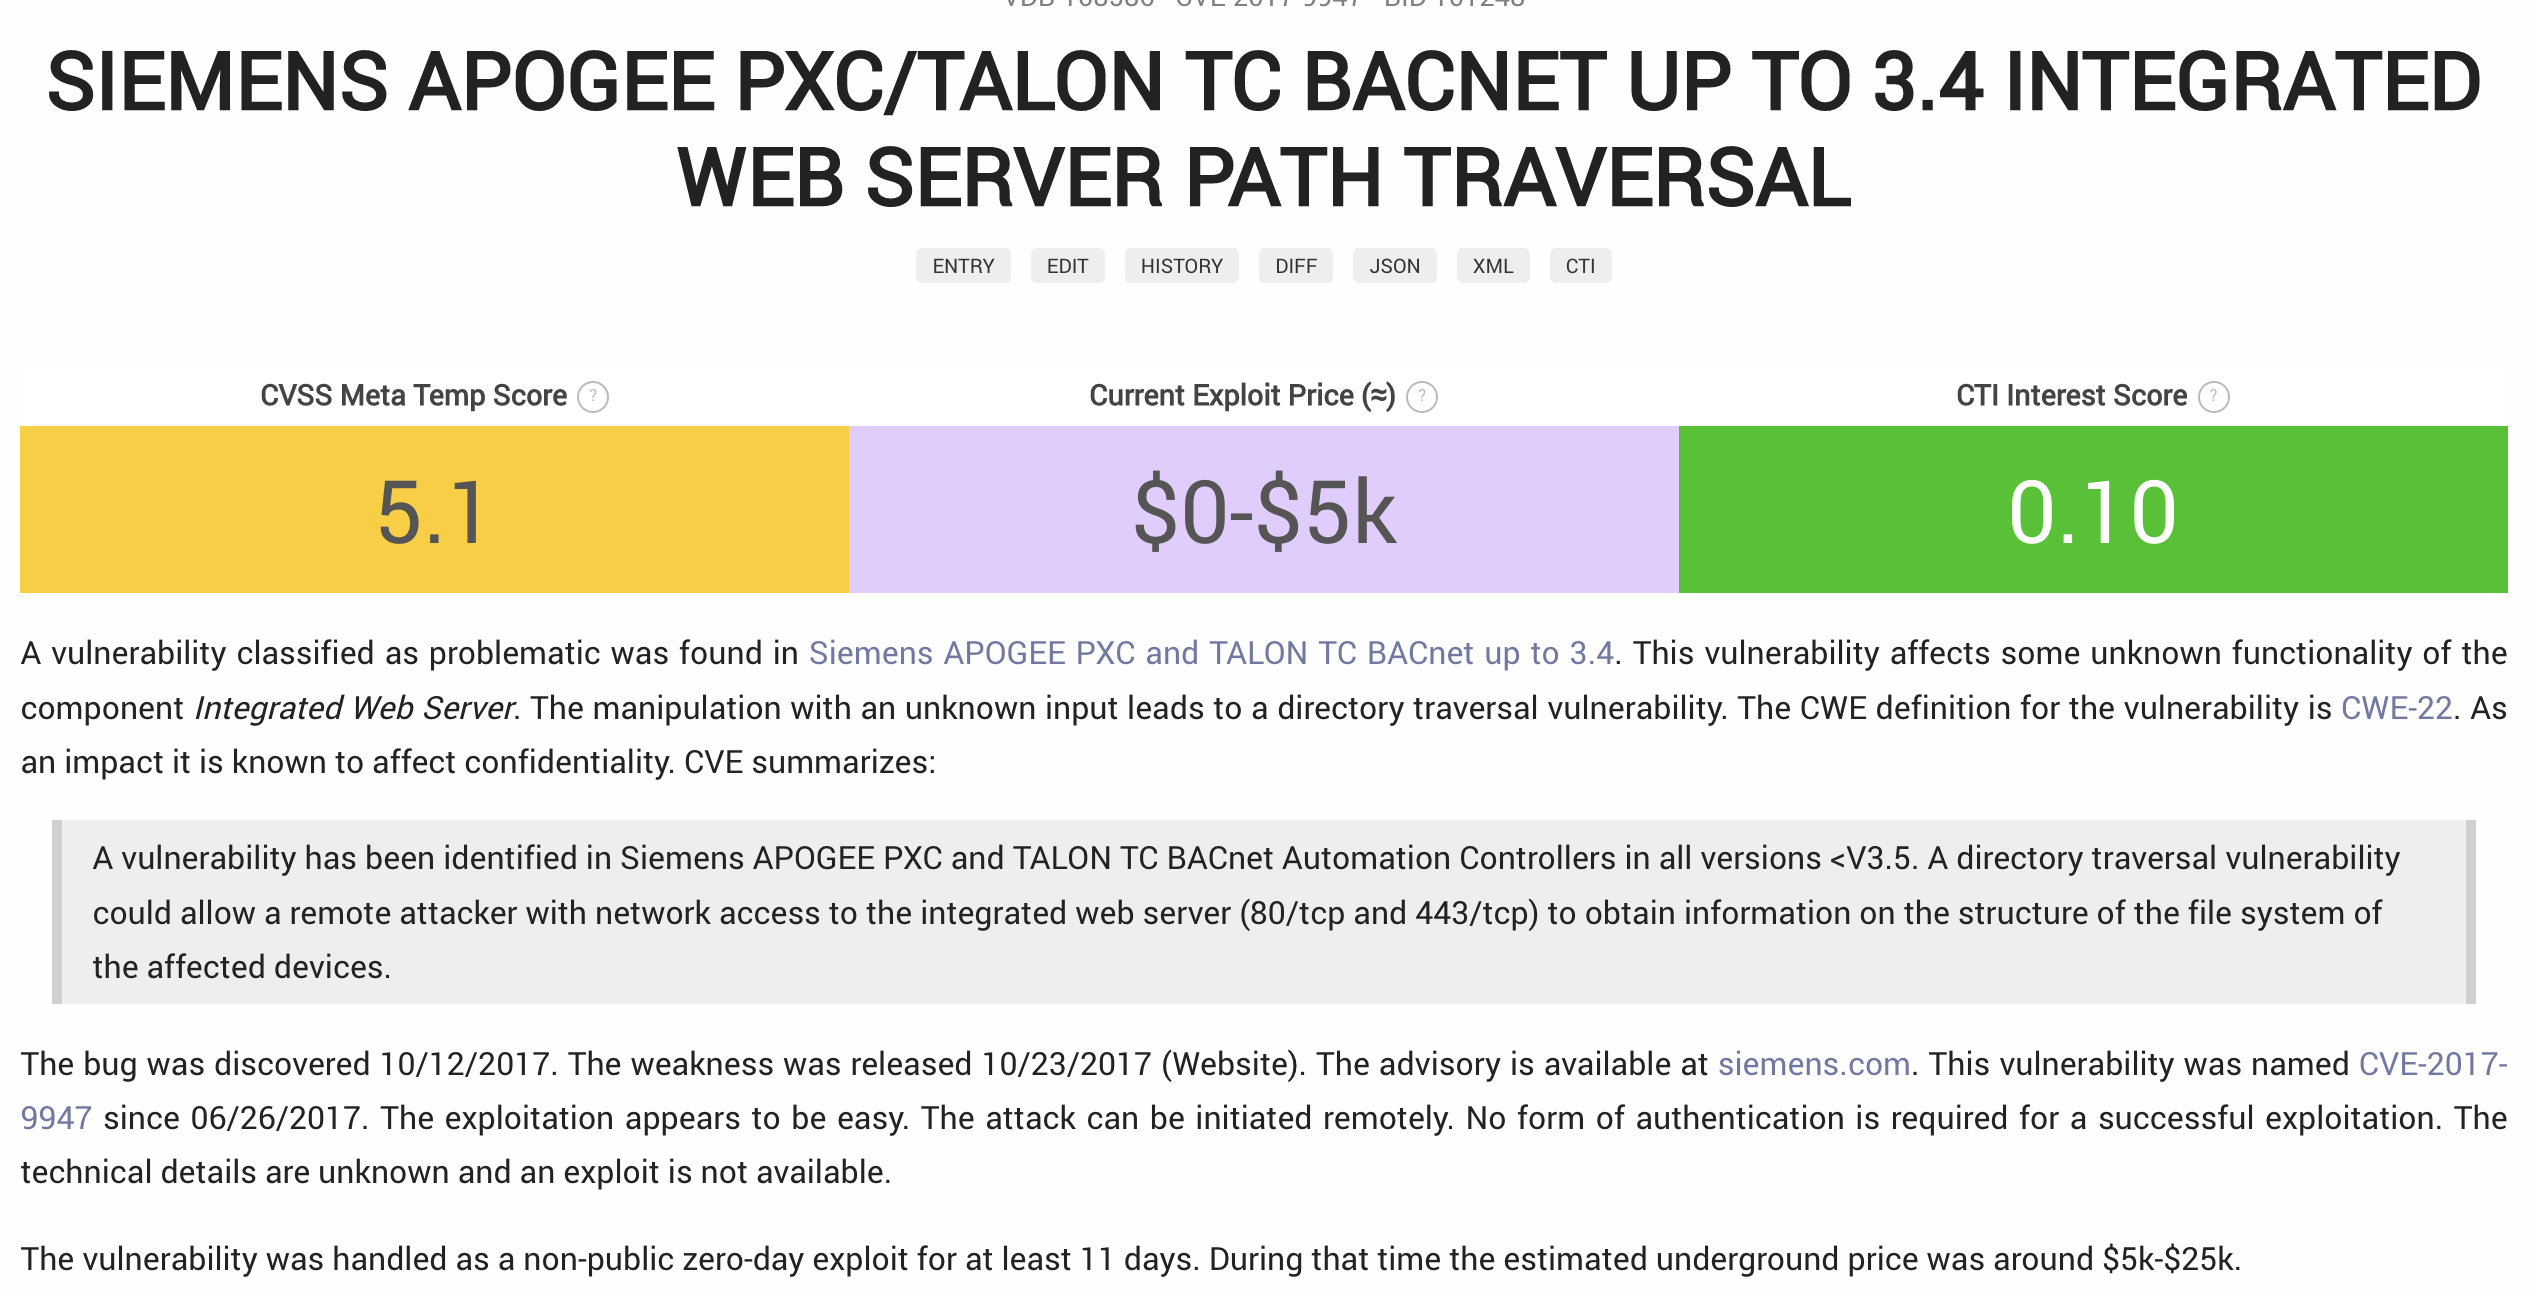 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 traccar/traccar
Traccar GPS Tracking System
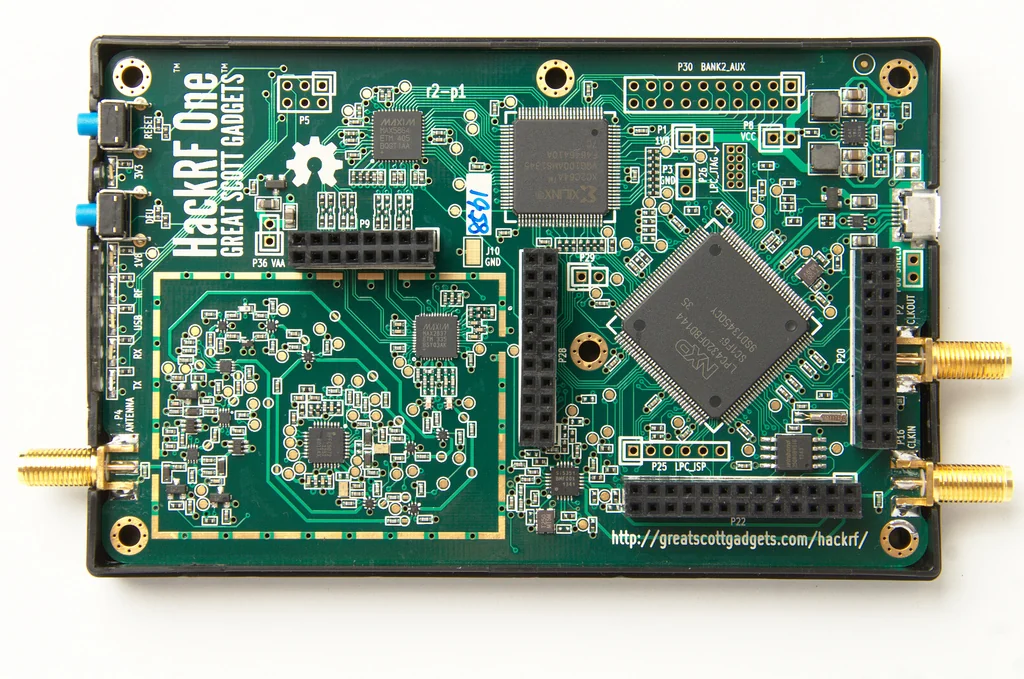 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…