

cve-2022-27255
 infobyte/cve-2022-27255
Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
binary-analysisctfeducation+7
284
infobyte/cve-2022-27255Automated firmware analysis and exploit toolkit for CVE-2022-27255, a Realtek eCos SDK SIP ALG buffer overflow affecting 30+ router models. Includes…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
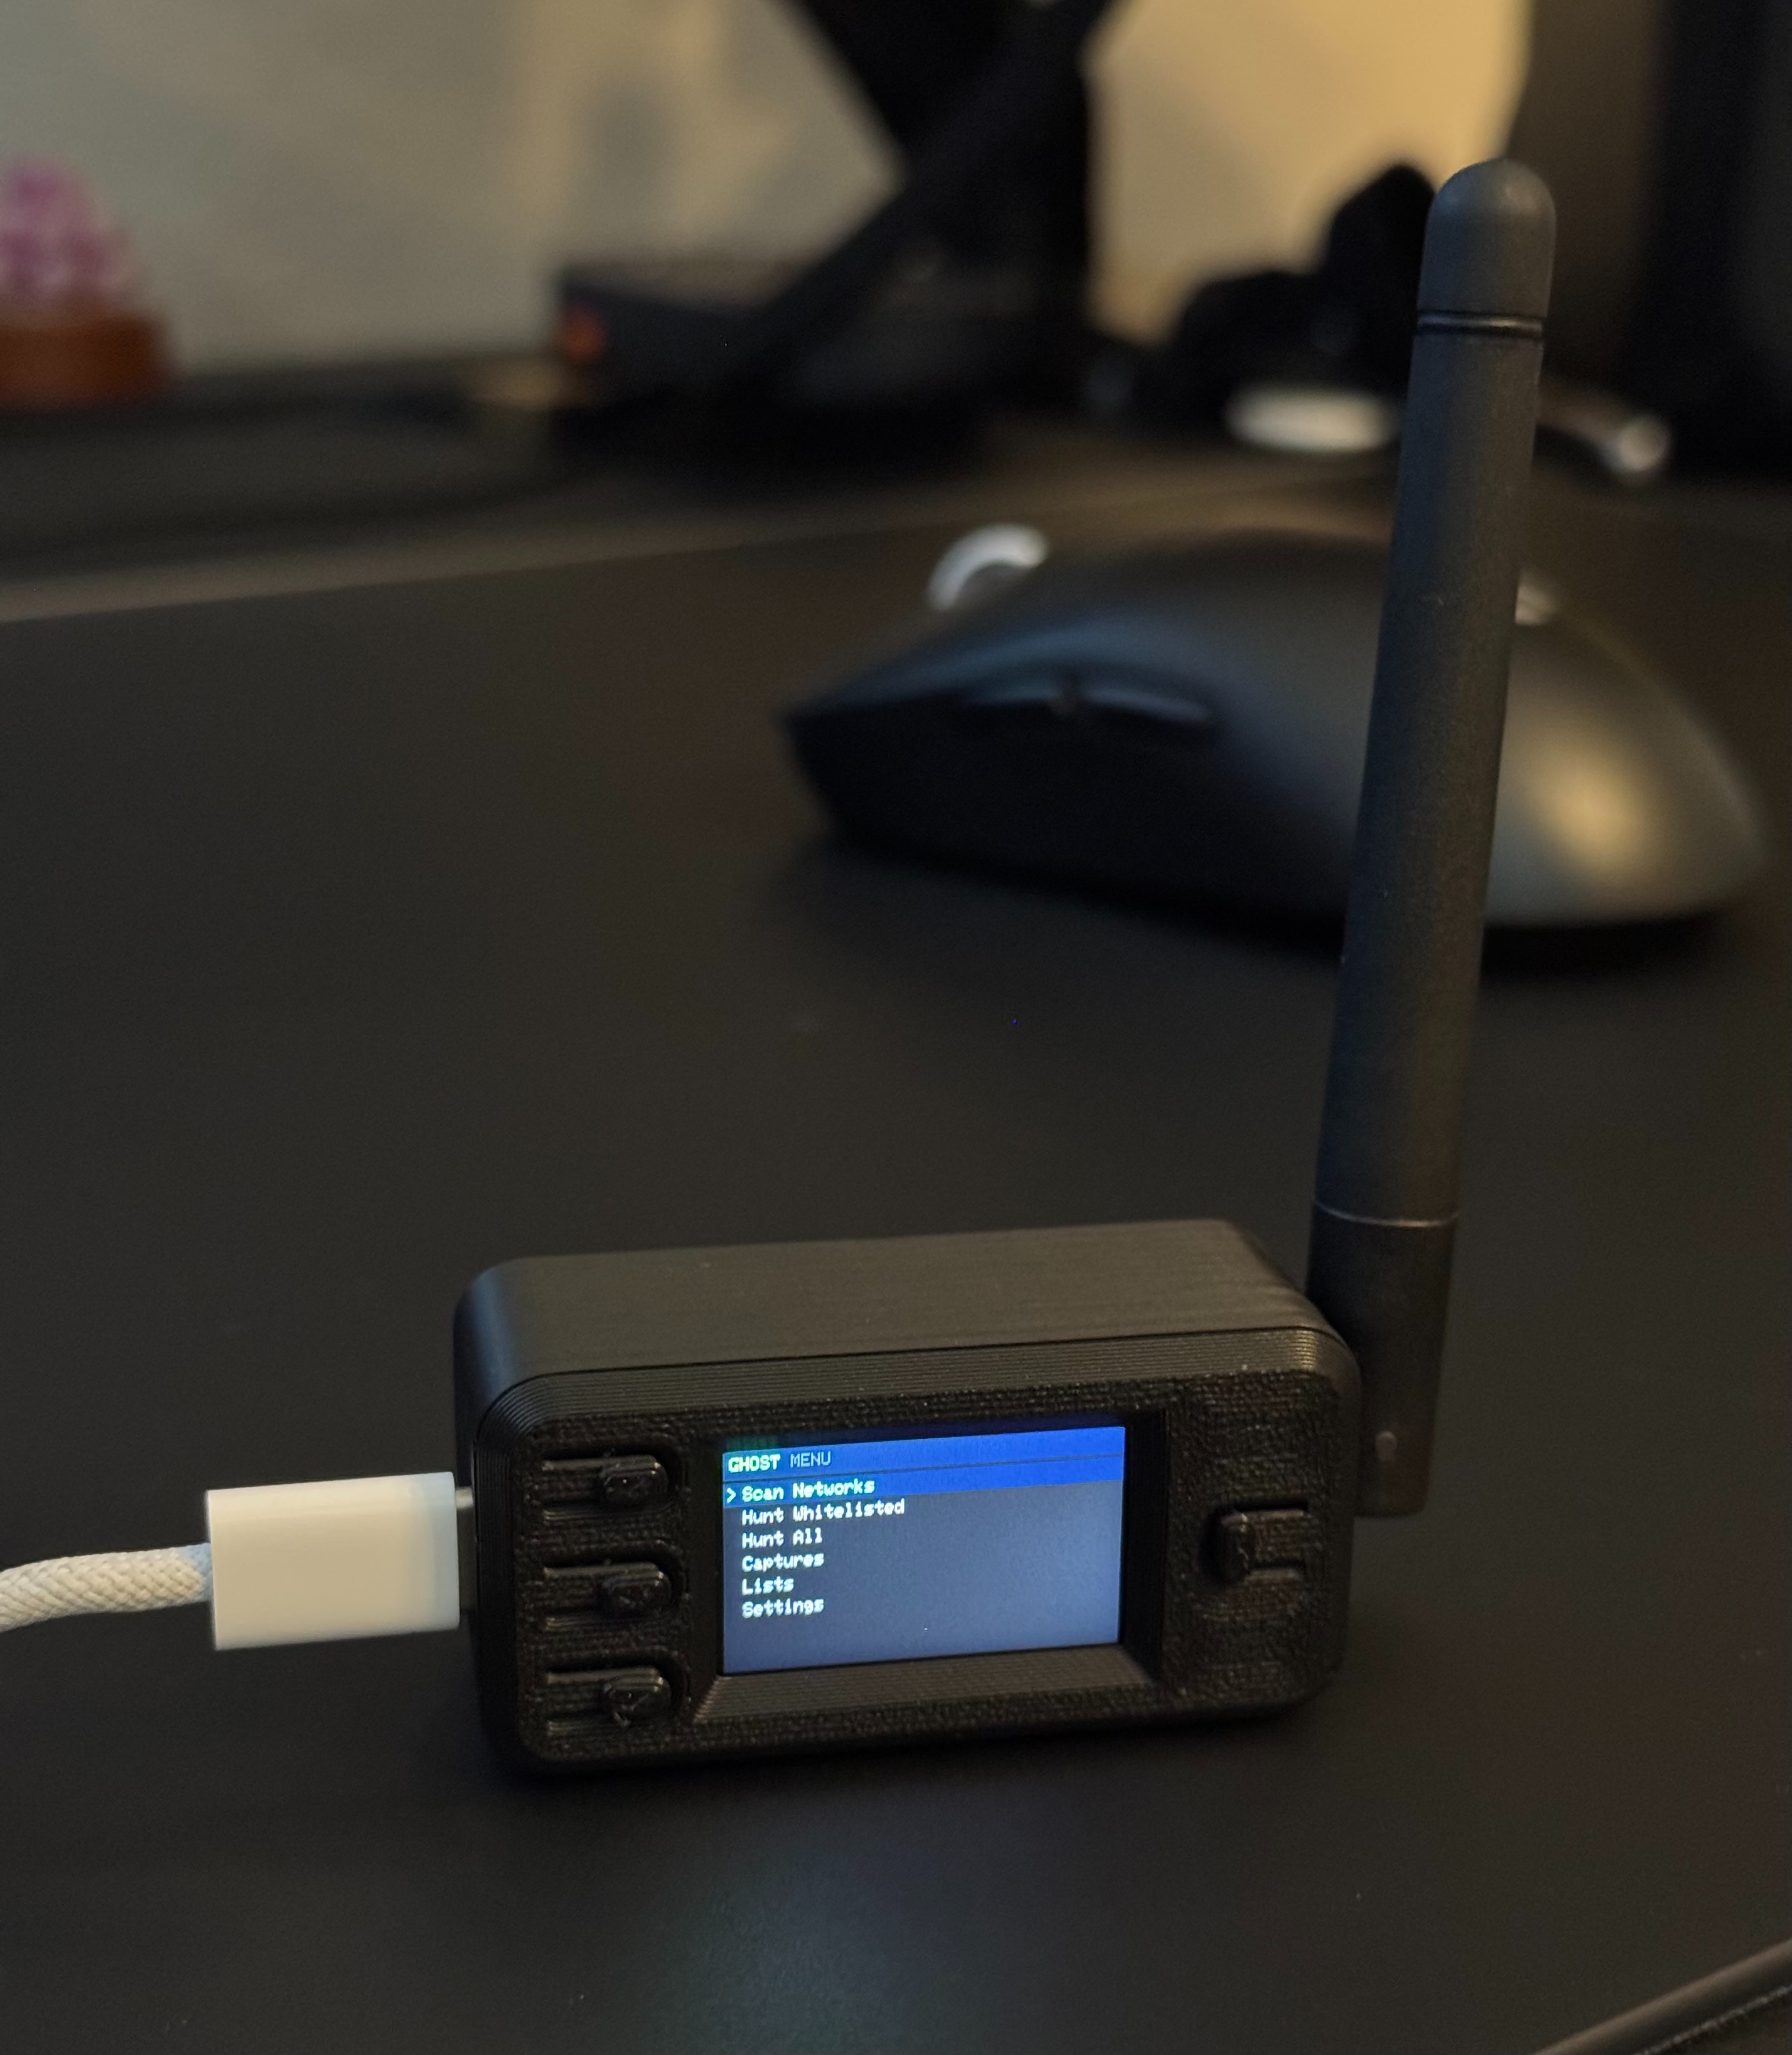 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
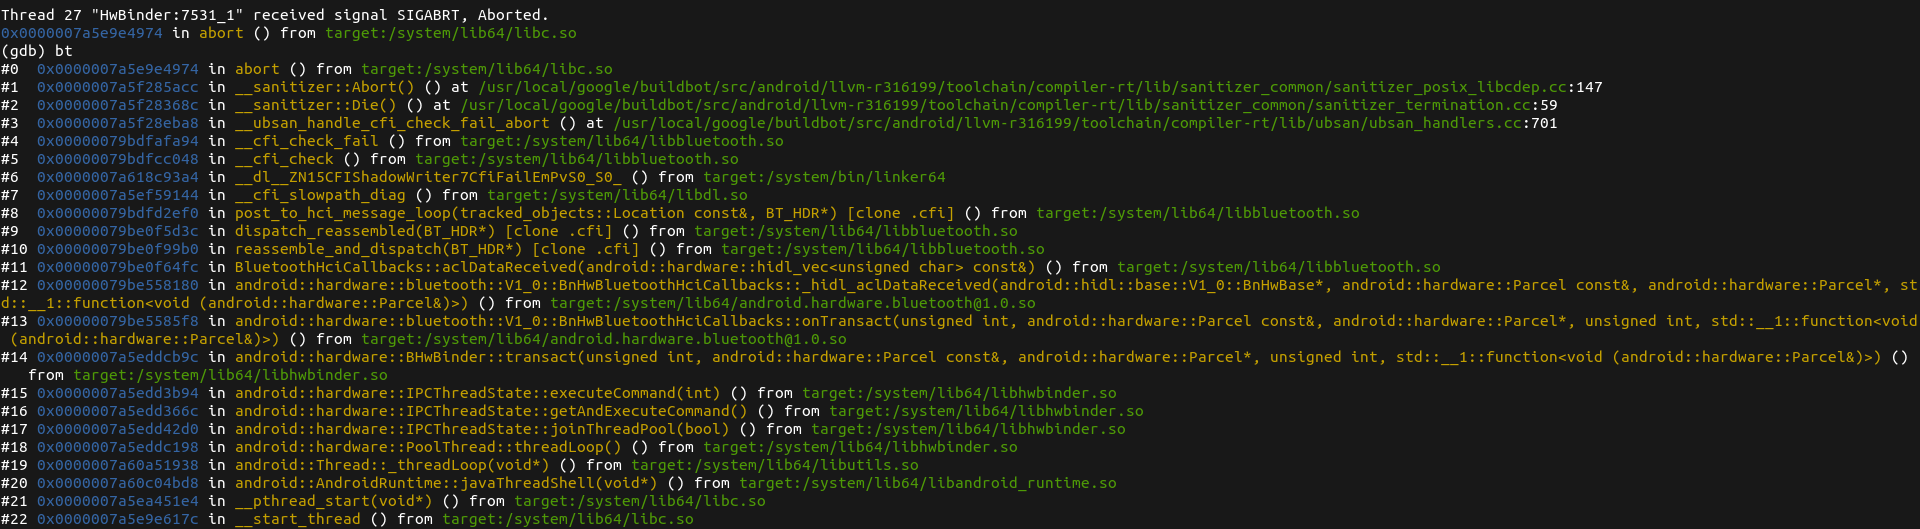 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 nicholasaleks/infected-drones
A collection of vulnerabilities & exploits against modern GCS
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
 yash-chandna/cve-2024-34463
Proof-of-concept exploit for CVE-2024-34463 targeting insufficient Bluetooth security in BPL Smart Weighing Scale PWS-01-BT. Includes BLE scanner and…
 spiralbl0ck/sigint_through_brother_printers
Exploit vulnerable Brother printers via CVE-2017-7588, collect data, and develop custom firmware implants for attack simulation.
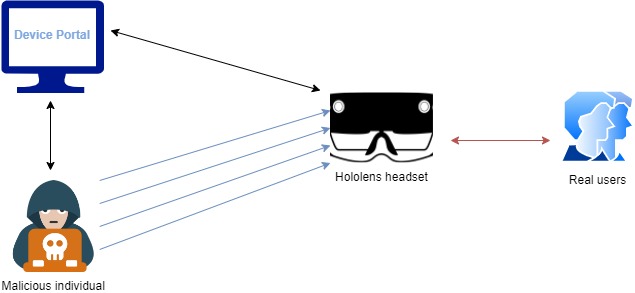 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.
 geeoon/fault-injection-finder
Automatically find and execute fault injection attacks
 spacehuhntech/esp8266_deauther
Affordable WiFi hacking platform for testing and learning
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
 cclabsinc/rfcrack
A Software Defined Radio Attack Tool