
eWeLink-QR-Code
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
cryptographyexploitationhardware-iot-security+3
1
salgio/ewelink-qr-codeThis repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
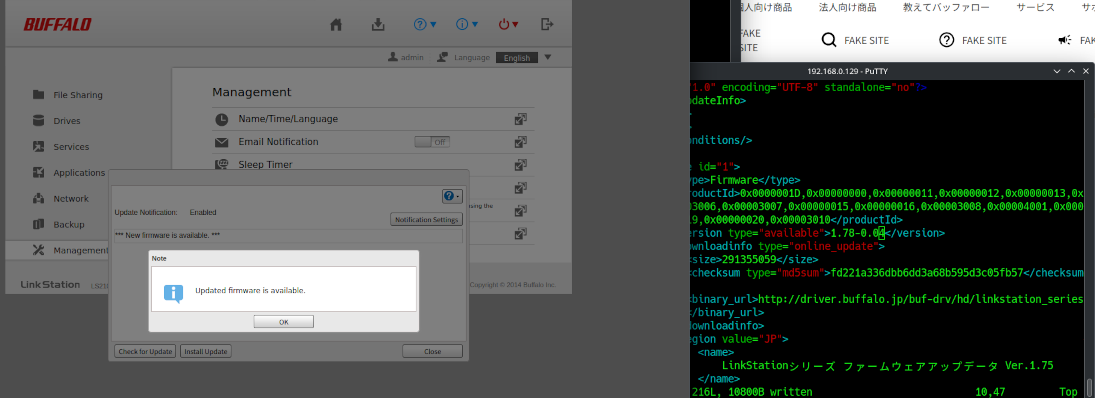 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 traccar/traccar
Traccar GPS Tracking System
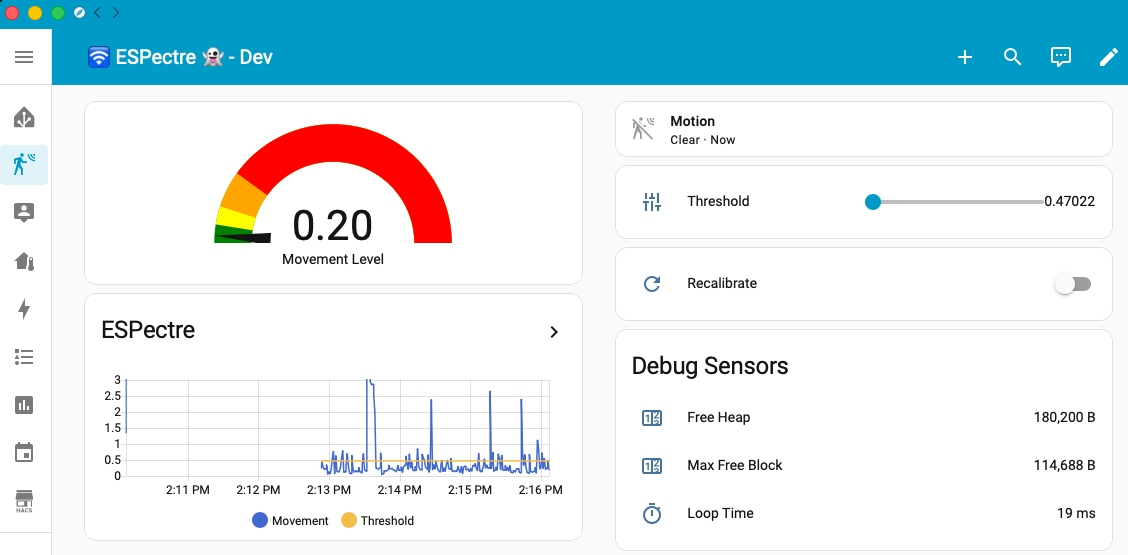 francescopace/espectre
ESPectre - Motion detection system based on Wi-Fi spectre analysis (CSI), with Home Assistant integration.
 efforg/rayhunter
Rust tool to detect cell site simulators on an orbic mobile hotspot
 secgroundzero/warberry
WarBerryPi - Tactical Exploitation
 jduck/asus-cmd
ASUS Router infosvr UDP Broadcast root Command Execution
 baptisterajaut/radmin-vpn-linux
Run Radmin VPN on Linux via Wine — custom driver, TAP bridge, zero packet loss
 insanid/netgear-telenetenable
Telenet Enable for Netgear routers from svn checkout http://netgear-telnetenable.googlecode.com/svn/trunk/ netgear-telnetenable-read-only
 1n3/supermicro-password-scanner
Supermicro IPMI/BMC Cleartext Password Scanner
 saimanish1/logitech-ipc-protocol
Reverse-engineered Logi Options+ agent IPC protocol. Switch Logitech multi-host devices programmatically via Unix socket (macOS) or named pipe…
 tothi/kali-rpi-luks-crypt
Full disk encryption for Kali on Raspberry using LUKS
 h00die/msf-testing-scripts
Metasploit modules in testing
 al1ex/checkpwd
Check the default pwd of product via checklist.
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…