CVE-2018-13341
 rajchowdhury240/cve-2018-13341
This Tool Aims to Exploit the CVE-2018-13341
embedded-systems-securityexploitationhardware-iot-security+3
rajchowdhury240/cve-2018-13341This Tool Aims to Exploit the CVE-2018-13341
yeggor/uefi_retoolA tool for UEFI firmware reverse engineering
 aliasrobotics/aztarna
aztarna, a footprinting tool for robots.
 evilsocket/bleah
This repository is DEPRECATED, please use bettercap as this tool has been ported to its BLE modules.
 renode/renode
Open-source simulation framework for developing, testing, and debugging unmodified software for multi-node embedded and IoT systems, supporting ARM,…
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
 risinek/esp32-wifi-penetration-tool
Exploring possibilities of ESP32 platform to attack on nearby Wi-Fi networks.
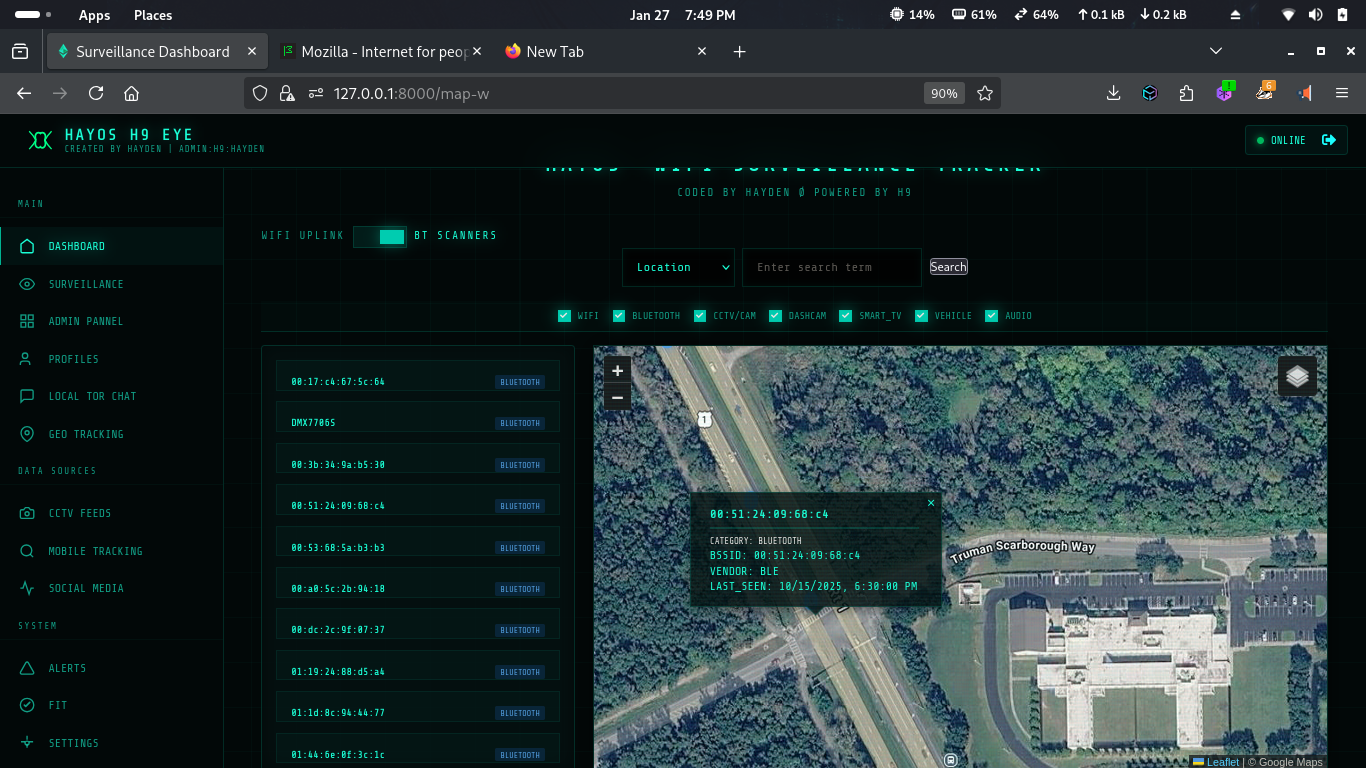 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 e-m-b-a/embark
Centralized firmware scanning and reporting platform with a web UI, REST API, and automated analysis workflows for securing embedded/IoT devices.
 redlectroid/overthruster
HID attack payload generator for Arduinos
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 blasty/sonos
Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…
 ottoyrocky/phantom-brain
Red portatil de reconocimiento inteligente con IA offline
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 atao/raspberrypi-setup
Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 9lyph/cve-2022-43704
Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller
 george0papasotiriou/cve-2026-23004-automotive-uds-authentication-bypass-via-replay-attack
Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.