
UnisocBootROMs
 mutur4/unisocbootroms
This is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694
curated-resourcesembedded-systems-securityfirmware-analysis+3
5
mutur4/unisocbootromsThis is a collection of Unisoc BootROMs dumped from various Unisoc chipsets via CVE-2022-38694
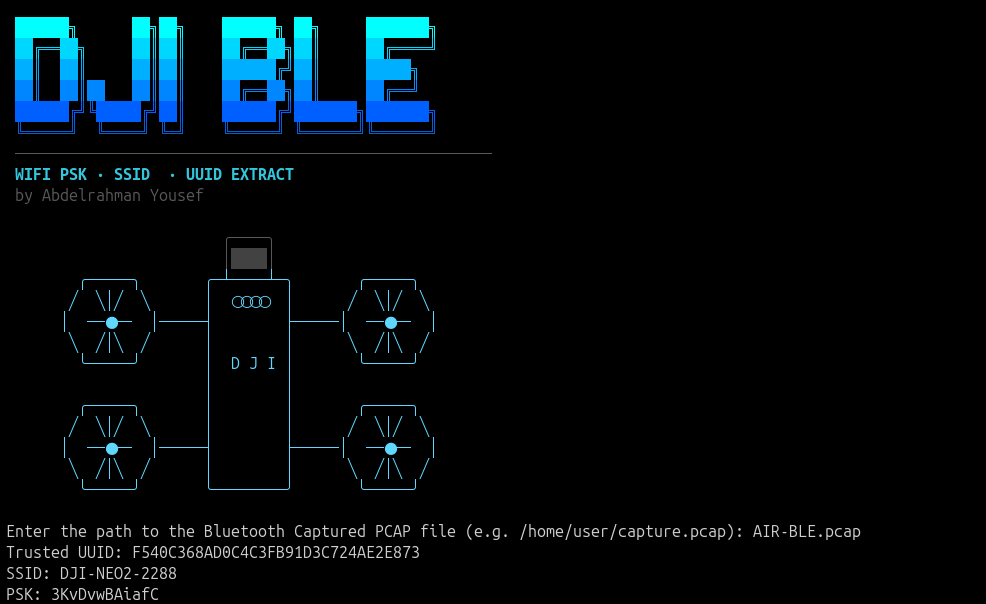 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 turretsec/u3000py
Python client for the Thinkware U3000 dashcam's local WiFi control protocol, reverse-engineered from the official Android app. PoC tooling behind…
 jaarden/cve-2024-22894
Proof-of-concept exploit for CVE-2024-22894, demonstrating 3DES-encrypted root password extraction from Alpha Innotec/Novelan heatpump firmware,…
 c2a2-at-florida-atlantic-university/gr-physec
GNU Radio module for physical layer security using deep learning channel fingerprinting, feature quantization, and SHA3-512 key generation from SDR…
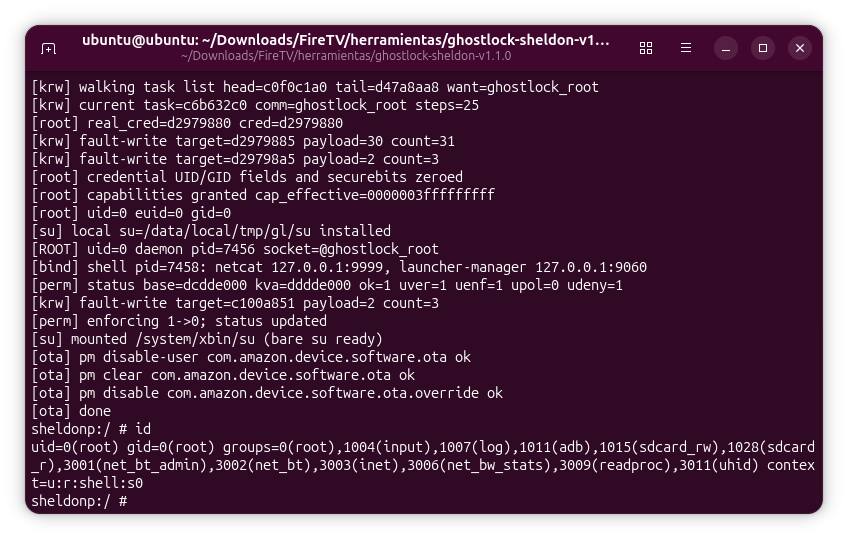 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 x3roxismygood/cve-2012-1803
Critical vulnerability in Siemens RuggedCom ROS devices allowing attackers to derive a hidden factory account password from the device MAC address…
 lycis/cawdog
CAWODOG is a proof-of-concept project demonstrating how to protect Python-based AI models deployed on offline industrial machines. Across three…
 matheus-garbelini/esp32_esp8266_attacks
Proof of Concept of ESP32/8266 Wi-Fi vulnerabilties (CVE-2019-12586, CVE-2019-12587, CVE-2019-12588)
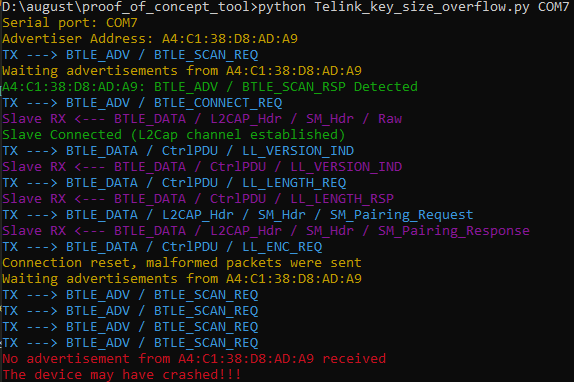 matheus-garbelini/sweyntooth_bluetooth_low_energy_attacks
Proof of Concept of Sweyntooth Bluetooth Low Energy (BLE) vulnerabilities.
 lyrebirds/sagemcom-fast-3890-exploit
Exploit for Sagemcom F@ST 3890 cable modem implementing Cable Haunt vulnerability to achieve remote code execution via WebSocket-based buffer…
 florianmattana/sass-king
Reverse engineering NVIDIA SASS instruction dictionary, kernel audits and pattern recognition across GPU architectures.
 souravbaghz/carpunk
CAN bus injection toolkit for automotive security testing. Performs interface control, sniffing, and CAN injection attacks on vehicle networks,…
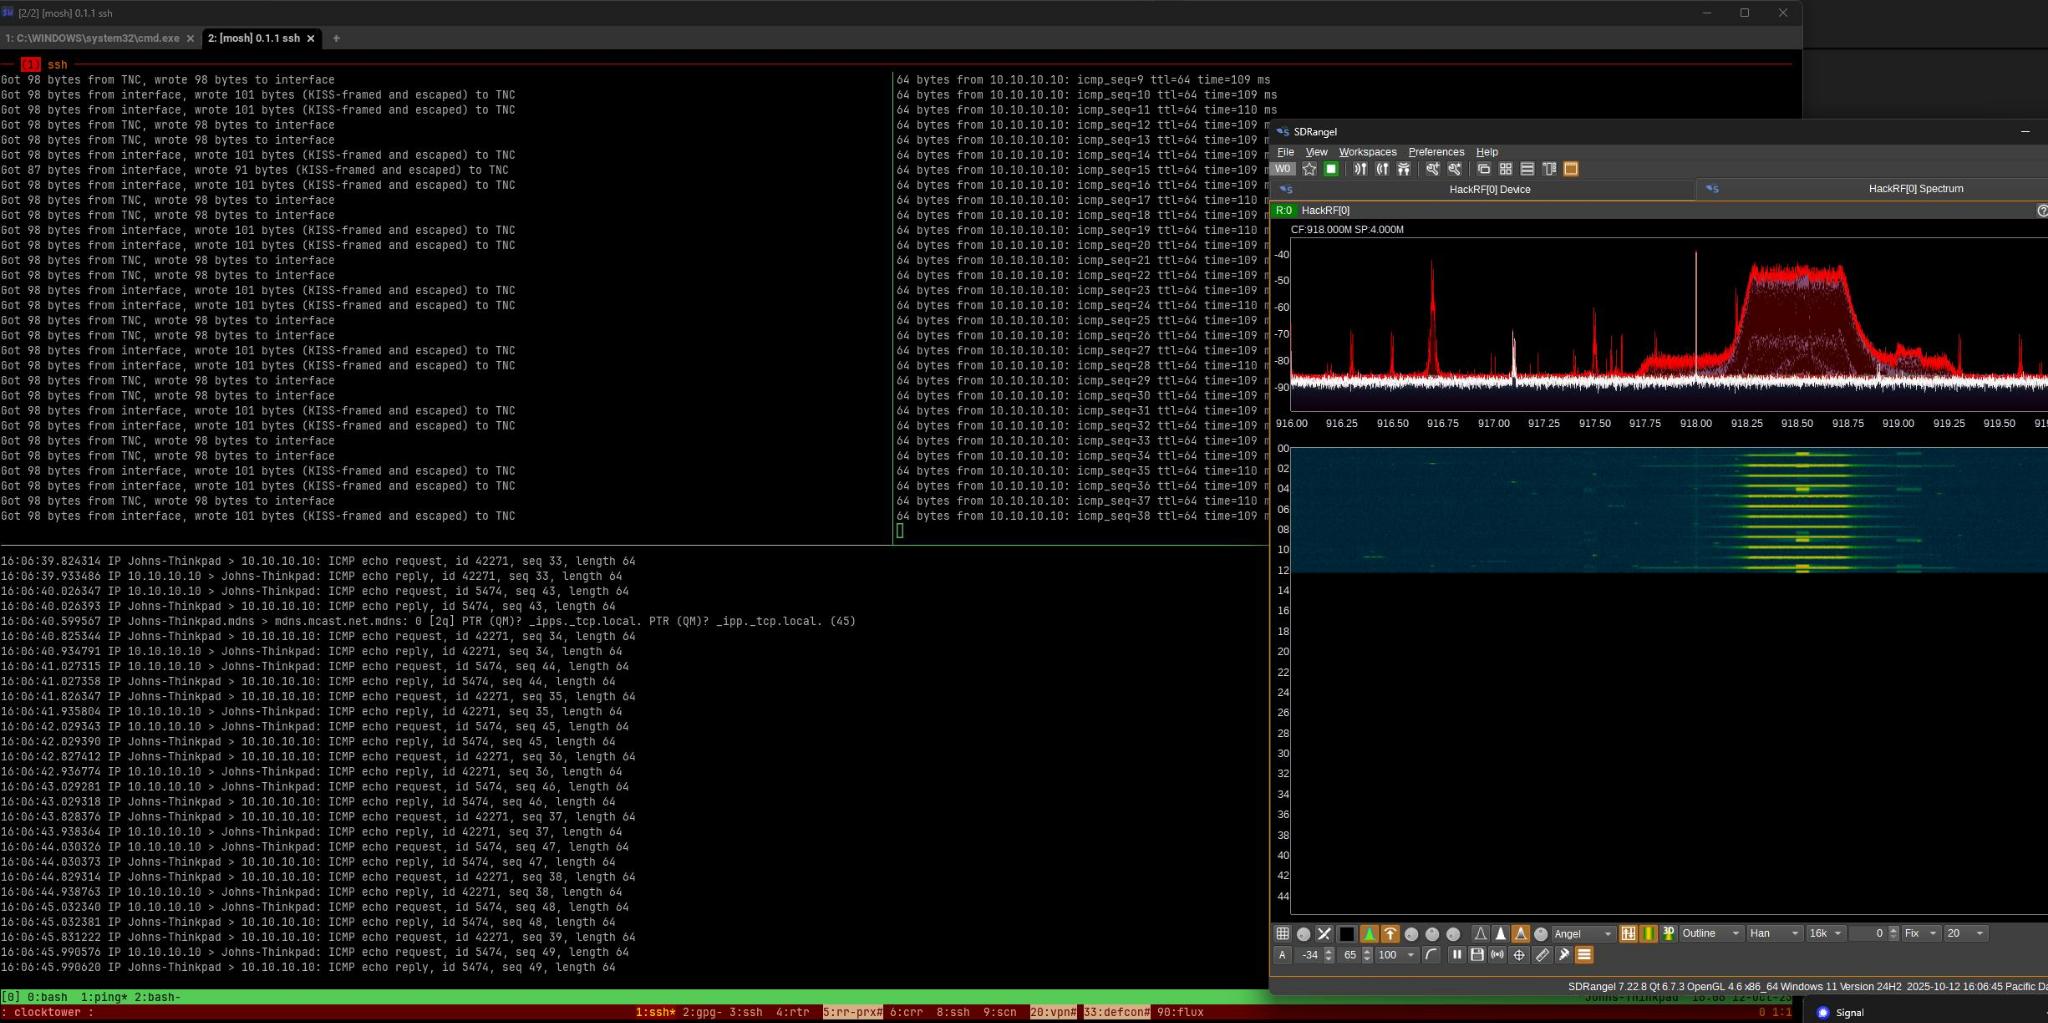 datapartyjs/meshtnc
Firmware for converting consumer LoRa radios into KISS TNC modems with serial CLI, BLE packet sniffing, and APRS/AX.25 compatibility for packet radio…
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 nicholasaleks/infected-drones
A collection of vulnerabilities & exploits against modern GCS
 sfewer-r7/brothervulnerabilities
Multiple Brother Devices: Multiple Vulnerabilities (CVE-2024-51977, CVE-2024-51978, CVE-2024-51979, CVE-2024-51980, CVE-2024-51981, CVE-2024-51982,…
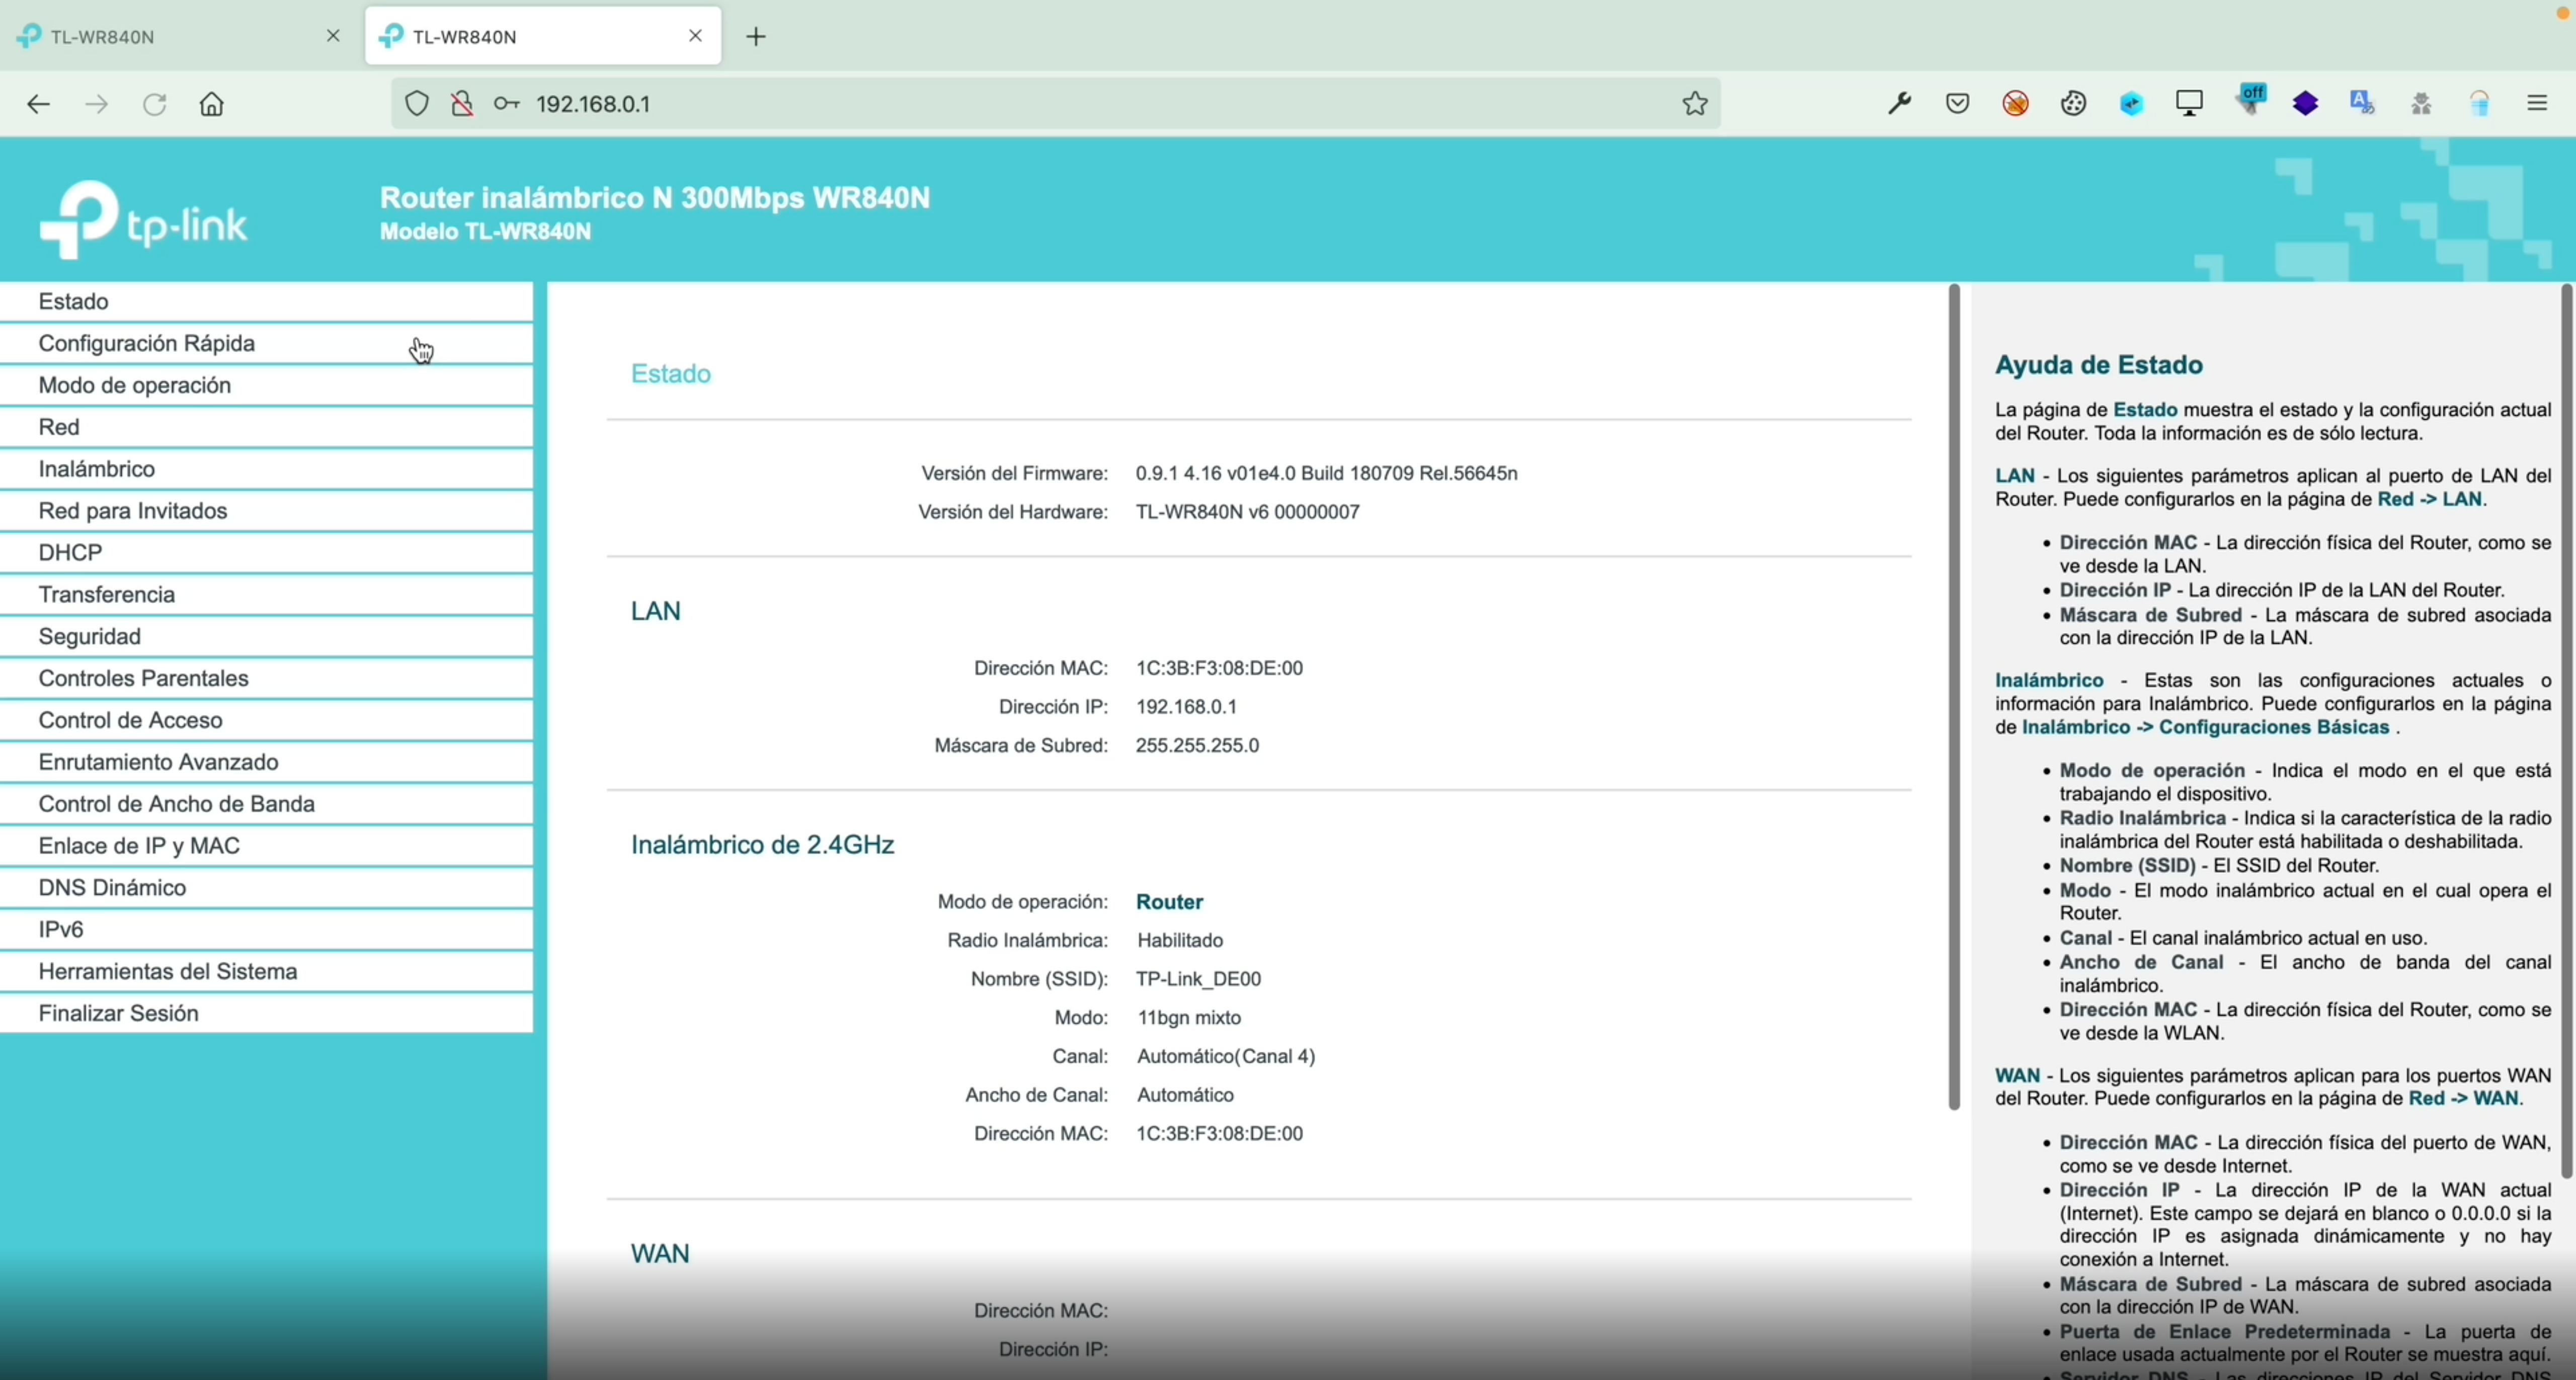 mr-xn/cve-2022-25064
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…