
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Traccar GPS Tracking System

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.

Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…

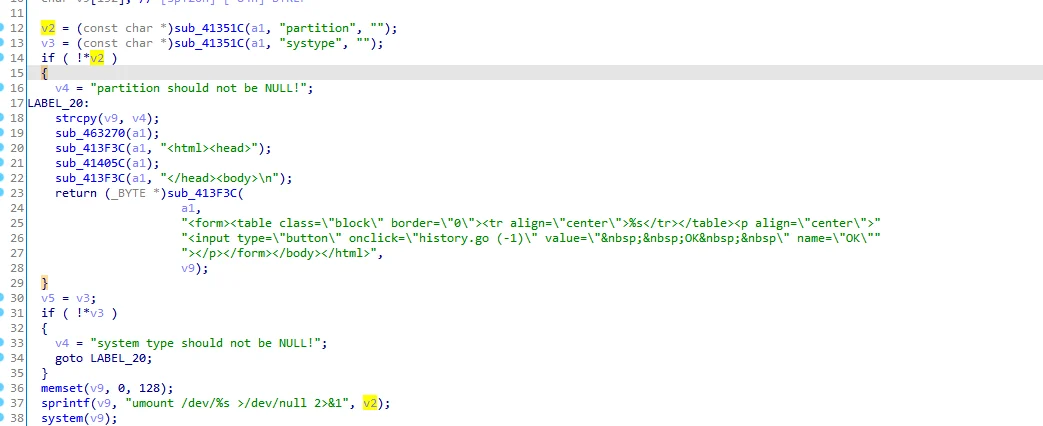
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…

Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…

TP-Link Archer BE800 V1 — Parental Control LAN RCE

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

TypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)

TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…

Proof-of-concept code (Bash and Python) for CVE-2025-65856 where ONVIF implementation in in Xiongmai XM530 IP cameras allows for unauthenticated …

Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…

Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.

Vatilon-based IP camera firmwares issue Session-Id tokens without verifying credentials, allowing attackers to obtain sessions and retrieve plaintext…

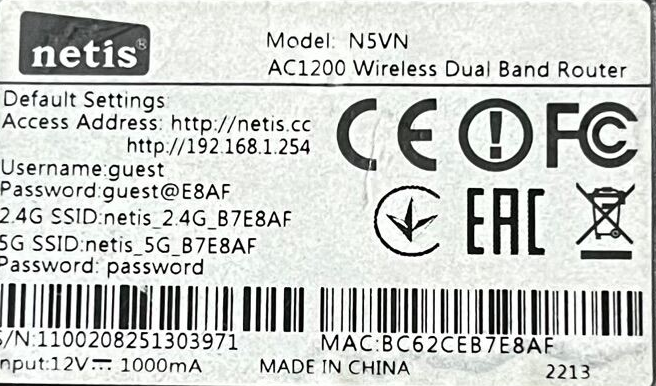
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…

Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)

Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…

Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…