
CVE-2026-2035703-x300
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
binary-analysiseducationexploitation+4
1
danish1162/cve-2026-2035703-x300Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 tangrs/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668.
 murrez/cve-2026-100740
Python PoC for CVE-2026-100740, an L2TP Host Name AVP out-of-bounds write in D-Link DIR-895L A1_102b07 tunnel_set_params. Fingerprints the device and…
 murrez/cve-2026-13249
Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…
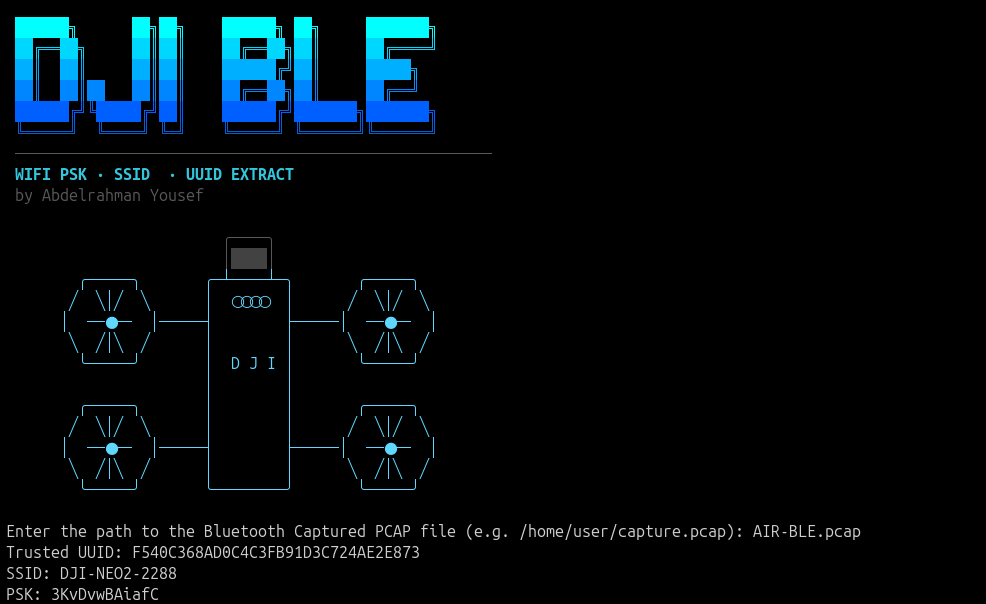 wh02m1/cve-2026-77812
Proof-of-concept that passively sniffs cleartext BLE DUML traffic from DJI drones to recover Wi-Fi PSK and trusted session UUIDs, demonstrating…
 k-o-n-t-o-r/ghostlock-sabrina
CVE-2026-43499 GhostLock root exploit for Chromecast with Google TV (sabrina)
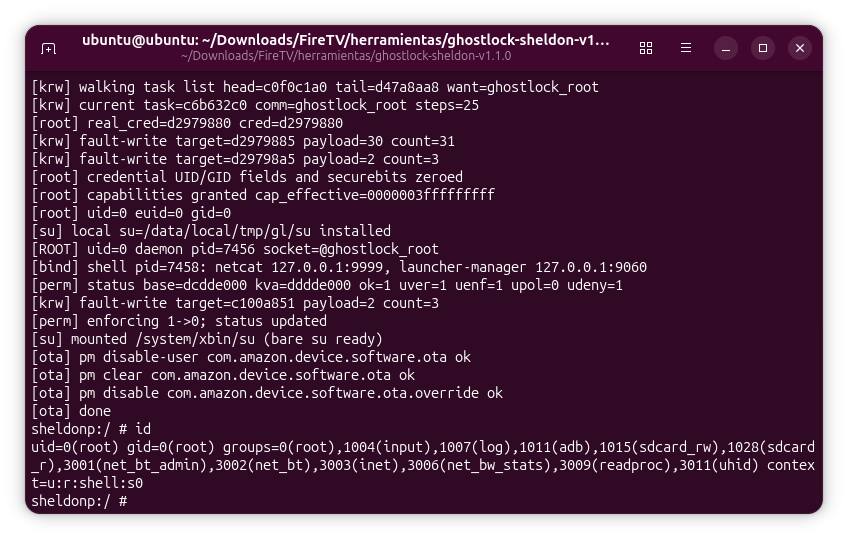 accessmodifier364/cve-2026-43499-firetv-sheldonp-writeup
Security research write-up on exploiting CVE-2026-43499 on the Amazon Fire TV Stick 3rd Gen (sheldonp), from temporary root to bootloader unlock.
 snyi001/cve-2026-79551-tenda
Tenda Technology Co., Ltd NVR_4H: CH3 v2.1.V27.5.58.6 was discovered to contain a hardcoded cryptographic key.
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 poxsky/cve-2026-38577
Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
 rebilibin/ghostlock-oppo-watch3pro
Complete exploit research for CVE-2026-43499 (GhostLock) on OPPO Watch 3 Pro, including kernel UAF analysis, disassembly, and exploit chain…
 olivierlaflamme/unibleed
Unitree G1 RCE PoC & Scripts (CVE-2026-76639 / CVE-2026-76640) technical details at boschko.ca/g1-ble-rce/
 slagzz/cve-2026-9254
TP-Link Archer BE800 V1 — Parental Control LAN RCE
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
 sermikr0/cve-2026-38427
CVE-2026-38427 — Integer Wraparound → Heap Buffer Overflow in Tasmota fetch_jpg() uint16_t (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38426
CVE-2026-38426 — strcpy() Stack Buffer Overflow in Tasmota fetch_jpg() boundary[40] (Tasmota <= 15.3.0.3)
 sermikr0/cve-2026-38422
CVE-2026-38422 — Remote Code Execution via Combined Buffer Overflows in Tasmota fetch_jpg() (Tasmota <= 15.3.0.3)