
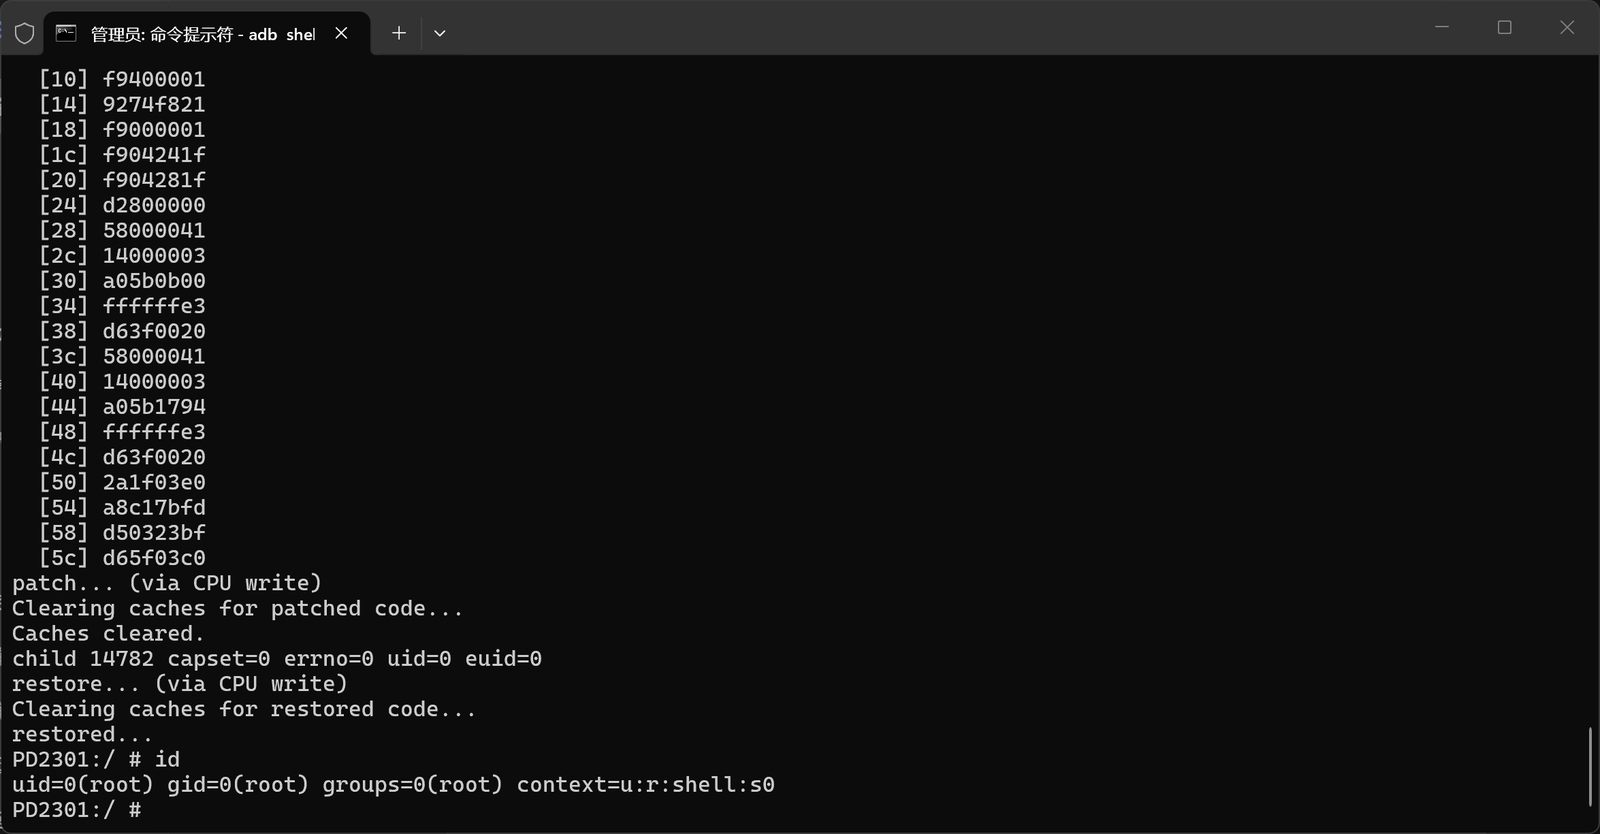
cve-2025-21479_iqooneo8
 qingizi7/cve-2025-21479_iqooneo8
Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
android-securitybinary-exploitationexploitation+6
7
qingizi7/cve-2025-21479_iqooneo8Local root exploit for CVE-2025-21479 (Adreno KGSL) on iQOO Neo8 (SM8475) - physical memory r/w, disables SELinux, spawns root shell
 namaek2/cve-2025-70962
CVE-2025-70962 PoC
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
 fomovet/cve-2025-29384
POC for CVE-2025-29384
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 spectrixdev/diy_whisperpair
Hijacking Bluetooth Accessories Using Google Fast Pair: WhisperPair CVE-2025-36911 Reference Implementation & Vulnerability Verification Toolkit
 kostasereksonas/xm_onvif_auth_bypass
Proof-of-concept code (Bash and Python) for CVE-2025-65856 where ONVIF implementation in in Xiongmai XM530 IP cameras allows for unauthenticated …
 pivotchip/frostedfastpair
WhisperPair (CVE-2025-36911) POC for ESP32 device
 steveakawlabs/marmalade-2-cve-2025-67780-exploit
Exploit PoCs for MARMALDE 2 (CVE-2025-67780) vulnerability in Starlink Dishes
 c0nyy/iot_vuln
Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
 otsmane-ahmed/cve-2025-29384-poc
Proof-of-concept exploit for CVE-2025-29384, a critical stack-based buffer overflow in Tenda AC9 routers. Includes Python and Metasploit modules for…