
flipper-mcp
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
ai-securitybluetooth-securitycommand-and-control+9
22
roostercoopllc/flipper-mcpAI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
 khaleedbt/netis-cve-2026-36539
Python script that checks Netis routers for CVE-2026-36539, detecting vulnerable devices on a network.
 v3ilsm1th/cve-2025-27840-wip
Work-in-progress PoC for CVE-2025-27840, an ESP32 Bluetooth vulnerability involving undocumented HCI commands enabling memory access and device…
 hackerest/pwneye
Your ONVIF and RTSP camera companion for discovering and hacking real-world security cameras 🎥
 withsecurelabs/usb-ninja-detection-poc
Detects USB Ninja keystroke injection attacks by logging keystrokes and application events, providing a proof-of-concept for defensive monitoring.
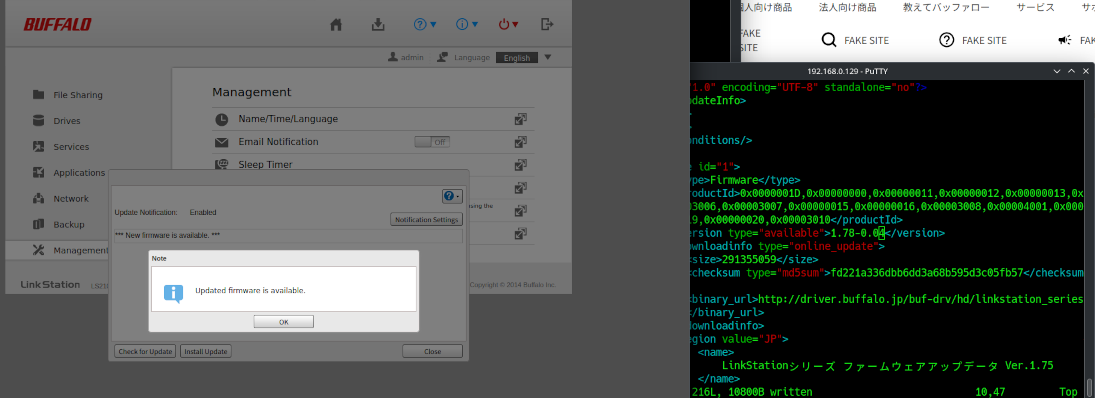 christopher-pace/cve-2023-51073
Firmware Update Server Verification Vulnerability on Buffalo LS210D Version 1.78-0.03
 bluez/bluez
Linux Bluetooth protocol stack with daemons, command-line clients, HCI monitor, and support for BR/EDR, LE, Mesh, audio profiles, providing device…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 jduck/asus-cmd
ASUS Router infosvr UDP Broadcast root Command Execution
 h00die/msf-testing-scripts
Metasploit modules in testing
 al1ex/checkpwd
Check the default pwd of product via checklist.
 nccgroup/upnp-pentest-toolkit
UPnP Pentest Toolkit for Windows
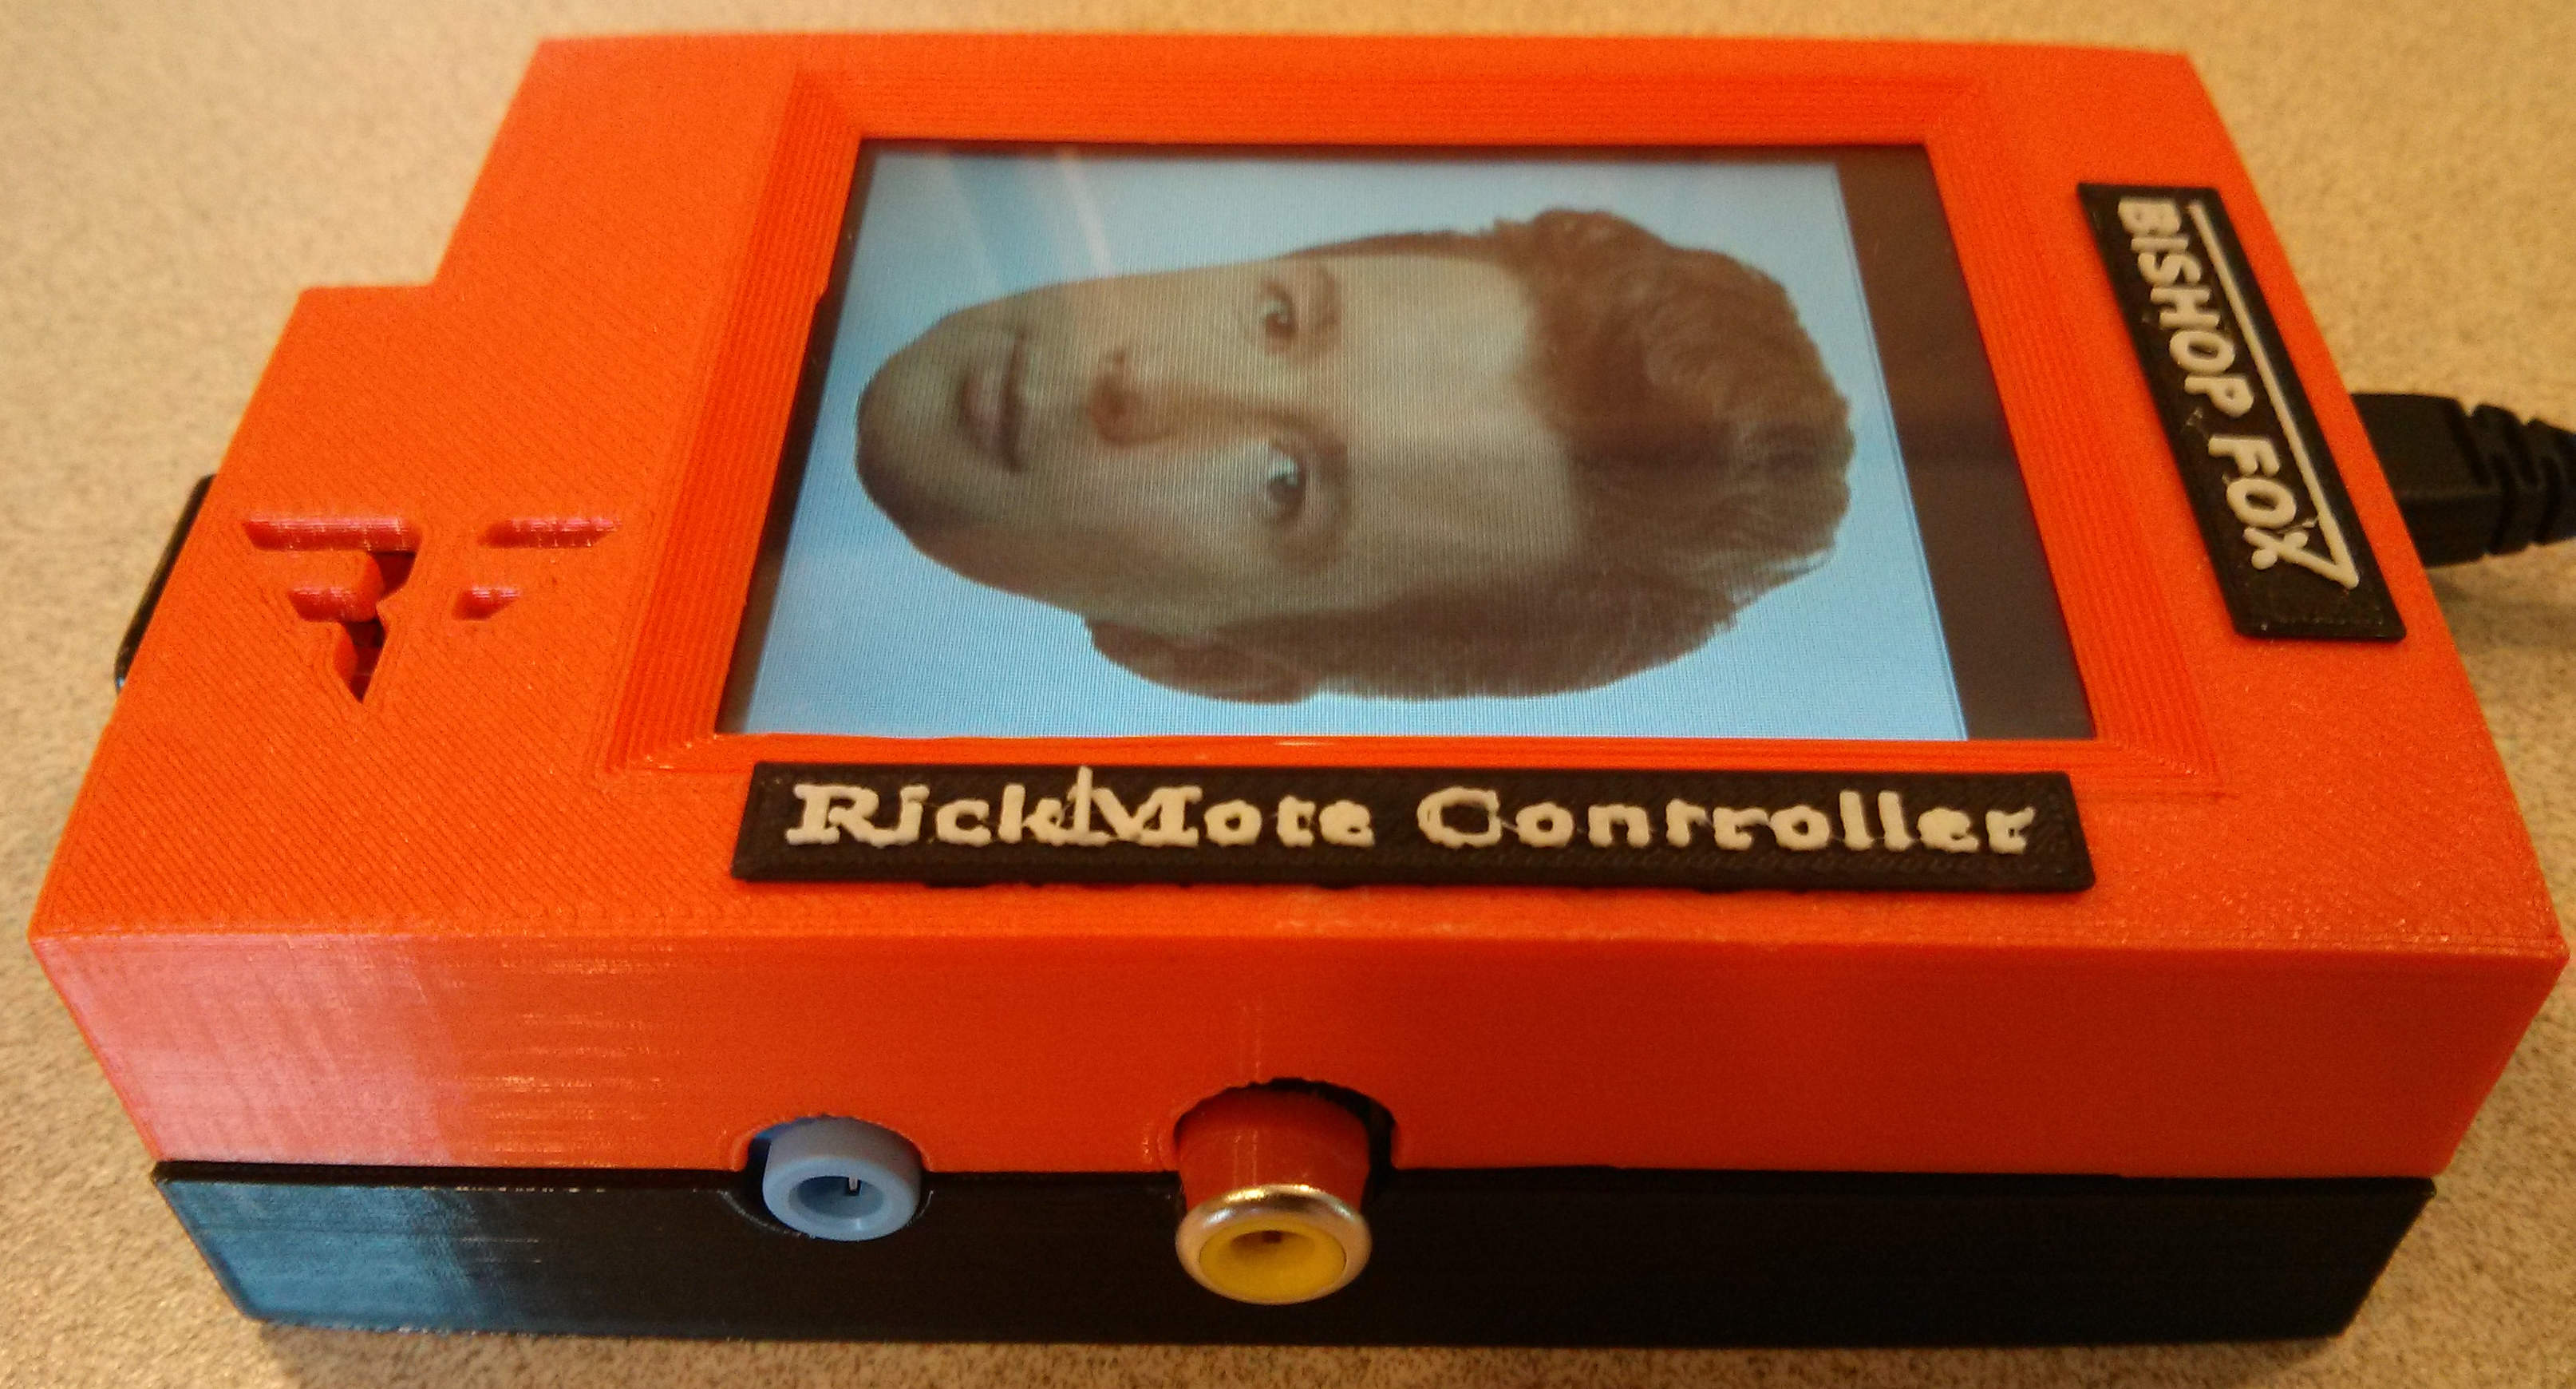 bishopfox/rickmote
The Rickmote Controller: Hijack TVs using Google Chromecast
 rdomanski/exploits_and_advisories
Repository that tracks public exploits, vulnerabilities and advisories that I [co-]discovered or [co-]authored.
 insanid/netgear-telenetenable
Telenet Enable for Netgear routers from svn checkout http://netgear-telnetenable.googlecode.com/svn/trunk/ netgear-telnetenable-read-only
 cybervinner/cp-plus-ez-p21-cve-2026-65893-65894
Documents CP PLUS EZ-P21 IP camera CVEs: arbitrary code execution via debug feature and improper authentication of HTTP endpoints, with responsible…
 itres-labs/usbcoercer
USBCoercer turns an ESP32 development board with native USB-OTG into an Ethernet-over-USB gadget capable of coercing proxy configuration via WPAD.