
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
9 results
CVE-2026-94095 preview

CVE-2026-94095

GitHubhackspeak/cve-2026-94095

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.
embedded-systems-securityexploitationhardware-iot-security+5
1
1 month ago
CVE-2026-38577 preview

CVE-2026-38577

GitHubpoxsky/cve-2026-38577

Proof-of-concept demonstrating hardcoded root credentials (admin/system) in Tenda HG21 XPON modem firmware, enabling unauthorized root access via…
embedded-systems-securityexploitationfirmware-analysis+5
1 month ago
CVE-2026-82592 preview

CVE-2026-82592

GitHubhackspeak/cve-2026-82592

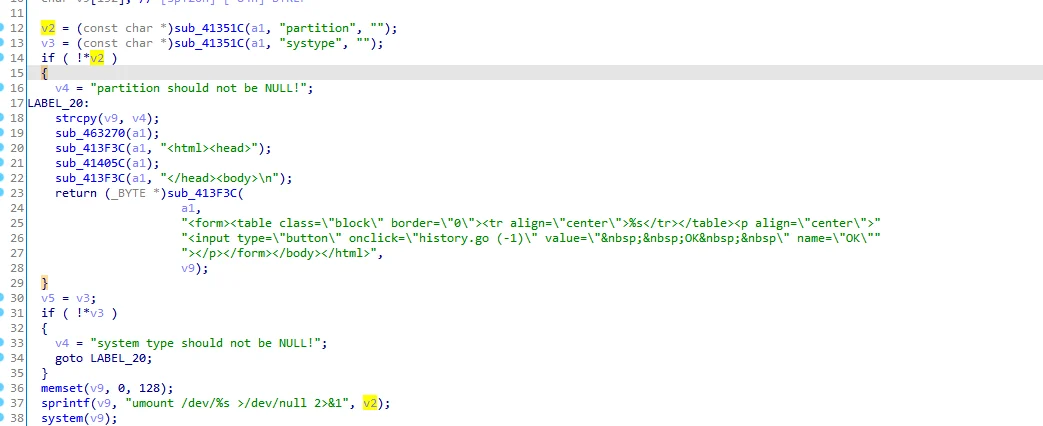
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
binary-exploitationexploitationhardware-iot-security+4
21 month ago
libnfc preview

libnfc

GitHubnfc-tools/libnfc

Platform independent Near Field Communication (NFC) library
hardware-hackinghardware-iot-securityhardware-security+2
2.0k1 year ago
CVE-2025-70962 preview

CVE-2025-70962

GitHubnamaek2/cve-2025-70962

CVE-2025-70962 PoC
exploitationfirmware-analysishardware-iot-security+3
2 months ago
CVE-2025-10681 preview

CVE-2025-10681

GitHubmichaeladamgroberman/cve-2025-10681

CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
cloud-securitydata-exfiltrationembedded-systems-security+8
4 months ago
CVE-2022-25064 preview

CVE-2022-25064

GitHubmr-xn/cve-2022-25064

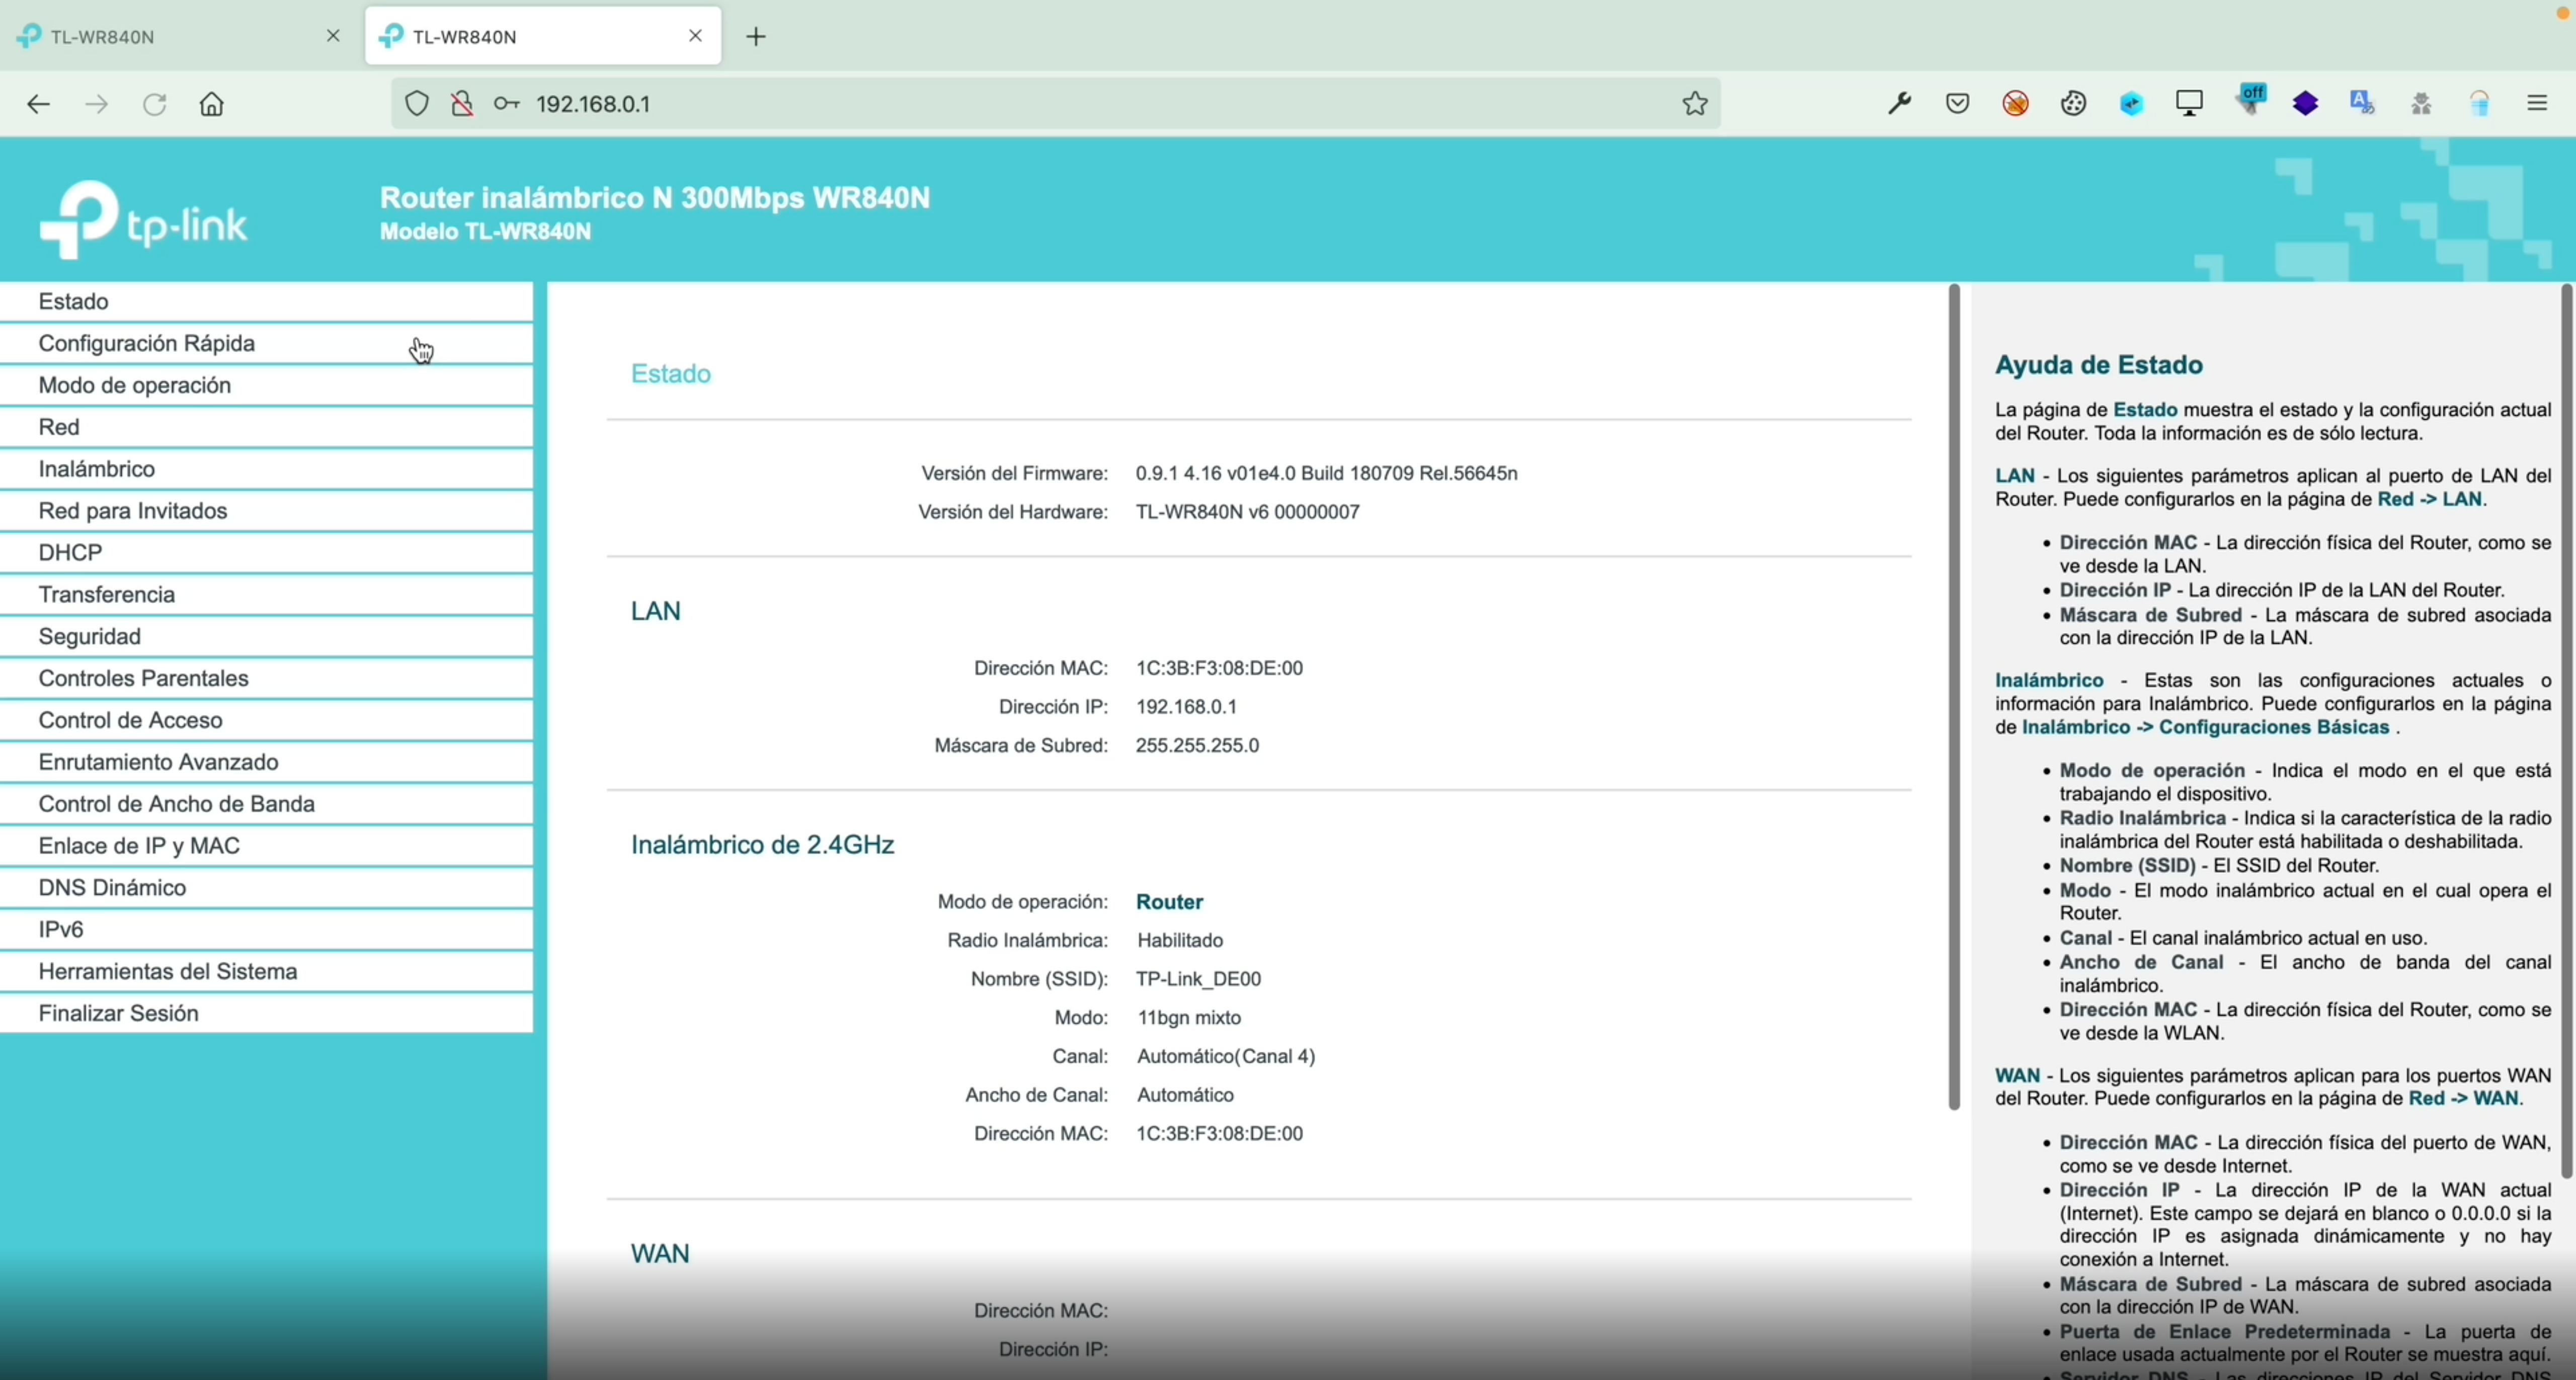
Python exploit for TP-Link TL-WR840N RCE (CVE-2022-25064) via crafted IPv6 address payload in the router's CGI interface, enabling remote command…
exploitationhardware-iot-securityiot-security+4
224 years ago
cve-2020-9375 preview

cve-2020-9375

GitHubthewhiteh4t/cve-2020-9375

TP-Link Archer C50 V3 devices before Build 200318 Rel. 62209 allows remote attackers to cause a denial of service via a crafted HTTP Header…
exploitationhardware-iot-securityiot-security+2
206 years ago
CVE-2022-25062 preview

CVE-2022-25062

GitHubexploitwritter/cve-2022-25062

This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.

exploitationhardware-iot-securityiot-security+3
4 years ago