
unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.

Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…

PoC for CVE-2026-94095, a traceroute command injection in Netcore NBR200V2 firmware via ubus JSON-RPC, enabling root RCE for authorized testing.

Traccar GPS Tracking System

Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.

This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).

infosec enthusiast and madman

Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…

Proof-of-concept demonstrating CVE-2021-30731, allowing unauthorized USB webcam access on macOS. Built with libuvc, it previews connected webcams on…

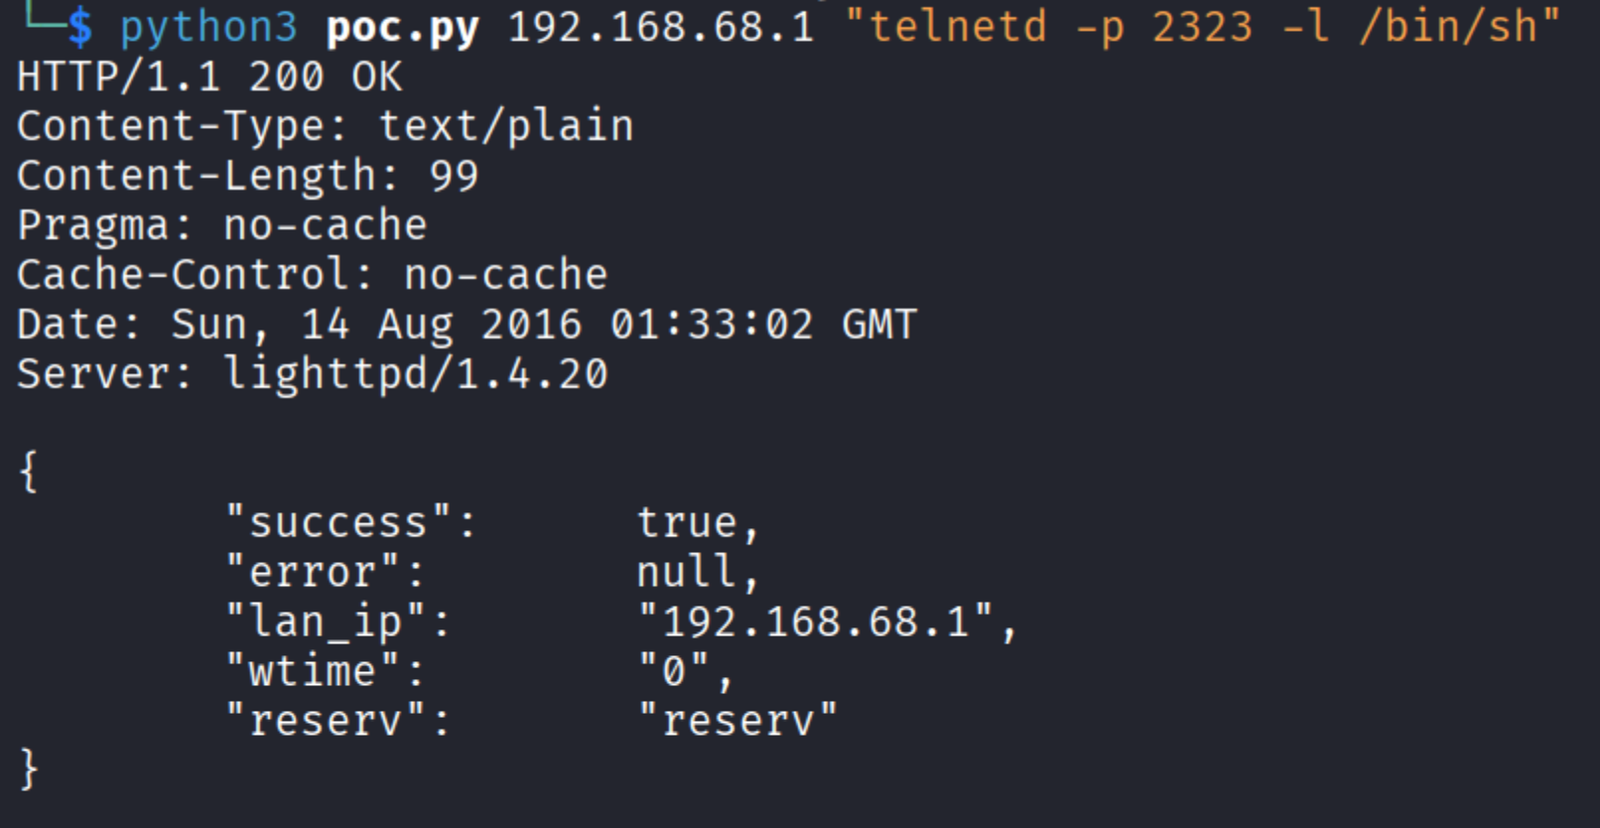
Dlink 615/815 shell PoC

Proof-of-concept exploit for authentication bypass via capture-replay in Dingtian DT-R002 relay, allowing unauthorized control of relays through HTTP…

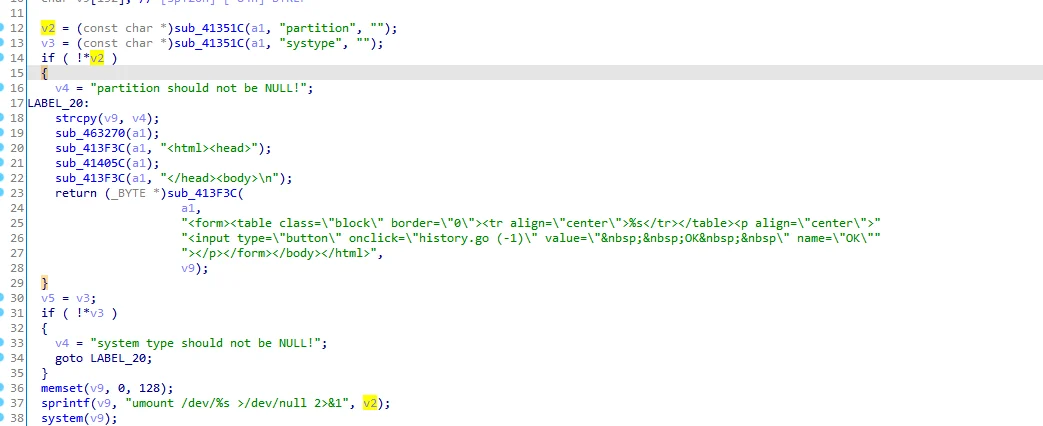
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…

TP-Link Archer BE800 V1 — Parental Control LAN RCE

Python proof-of-concept for unauthenticated OS command injection in TOTOLINK N600R, exploiting the langType parameter to execute arbitrary commands…

CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS

Proof-of-concept exploits for IoT device vulnerabilities, including TOTOLINK login bypass CVEs, with detailed technical analysis and reproduction…

This script exploits a vulnerability (IoF) in the TPLink WR840N router, using a field for injecting code in the module DNS.

Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)