

Sniffle
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
bluetooth-securityembedded-systems-securityhardware-hacking+5
1.2k
nccgroup/sniffleBluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 seemoo-lab/internalblue
Bluetooth experimentation framework for Broadcom and Cypress chips.
 qengineering/rk35xx-copyfail-hotfix
Provides a pre-compiled kernel patch for CVE-2026-31431 (Copy Fail) on RK35xx SBCs running Ubuntu 24.04, with installation instructions and build…
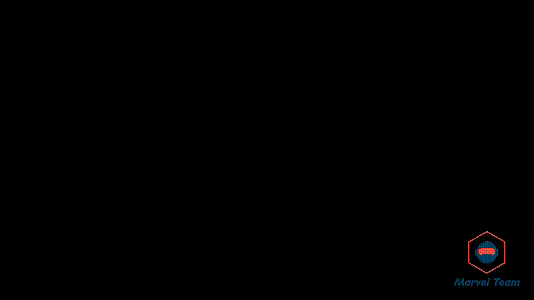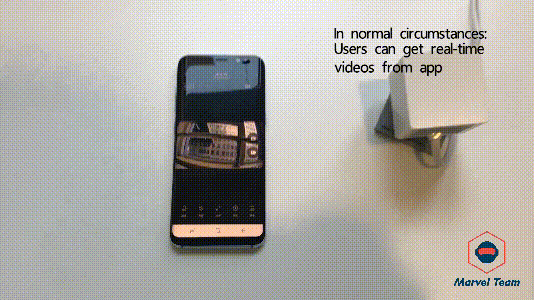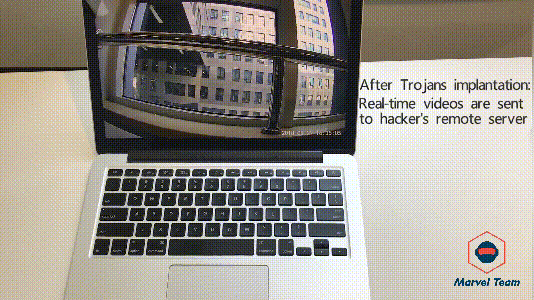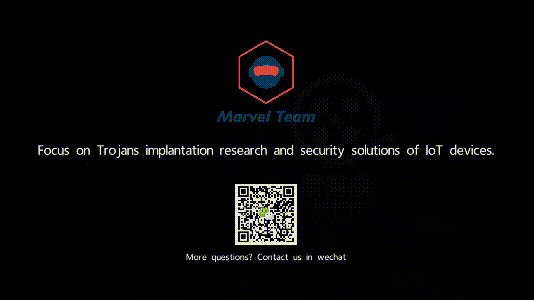 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices
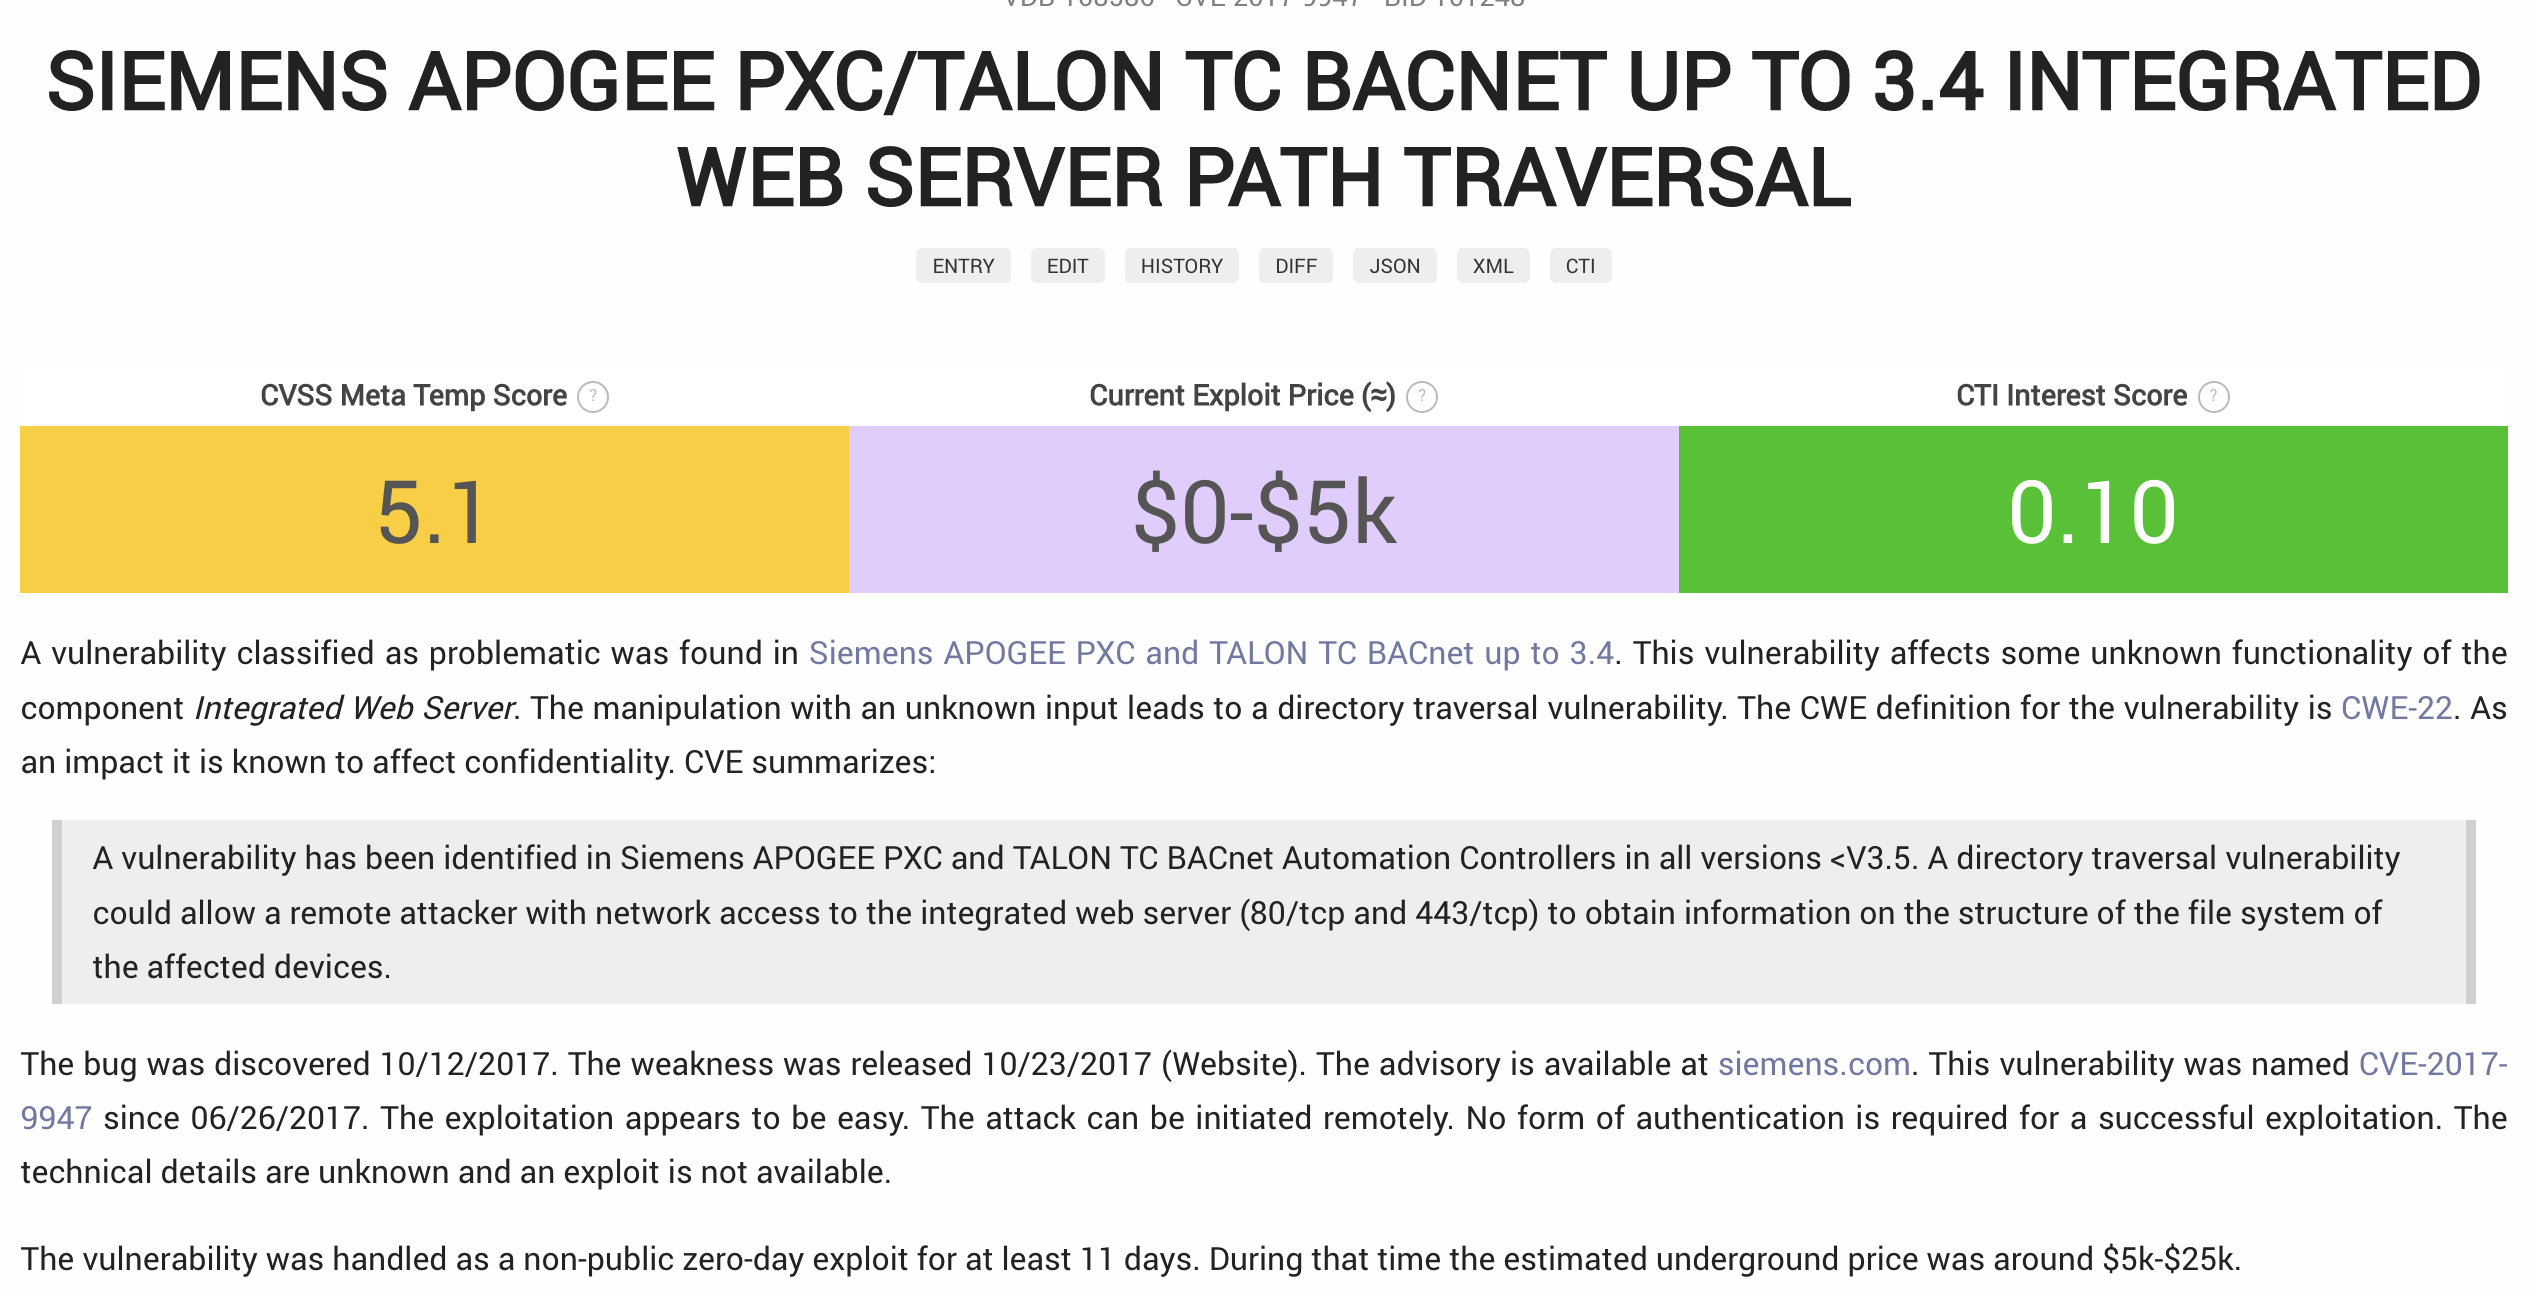 rosesecurity/apologee
APOLOGEE is a Python script and Metasploit module that enumerates a hidden directory on Siemens APOGEE PXC BACnet Automation Controllers (all…
 ebux/cable-modems
Black-box security evaluation of five ISP cable modem/router gateways, analyzing firmware images and documenting 35+ vulnerabilities including…
 alt3kx/papers
A handy collection of my public papers, all in one place.
 mathse/meltdown-spectre-bios-list
a list of BIOS/Firmware fixes adressing CVE-2017-5715, CVE-2017-5753, CVE-2017-5754
 0xbinder/cve-2021-4045
🔐 "PWNTAPO: Unveiling Command Injection in TP-Link Tapo C200 Cameras (<= v1.1.16 Build 211209)" 🔓
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
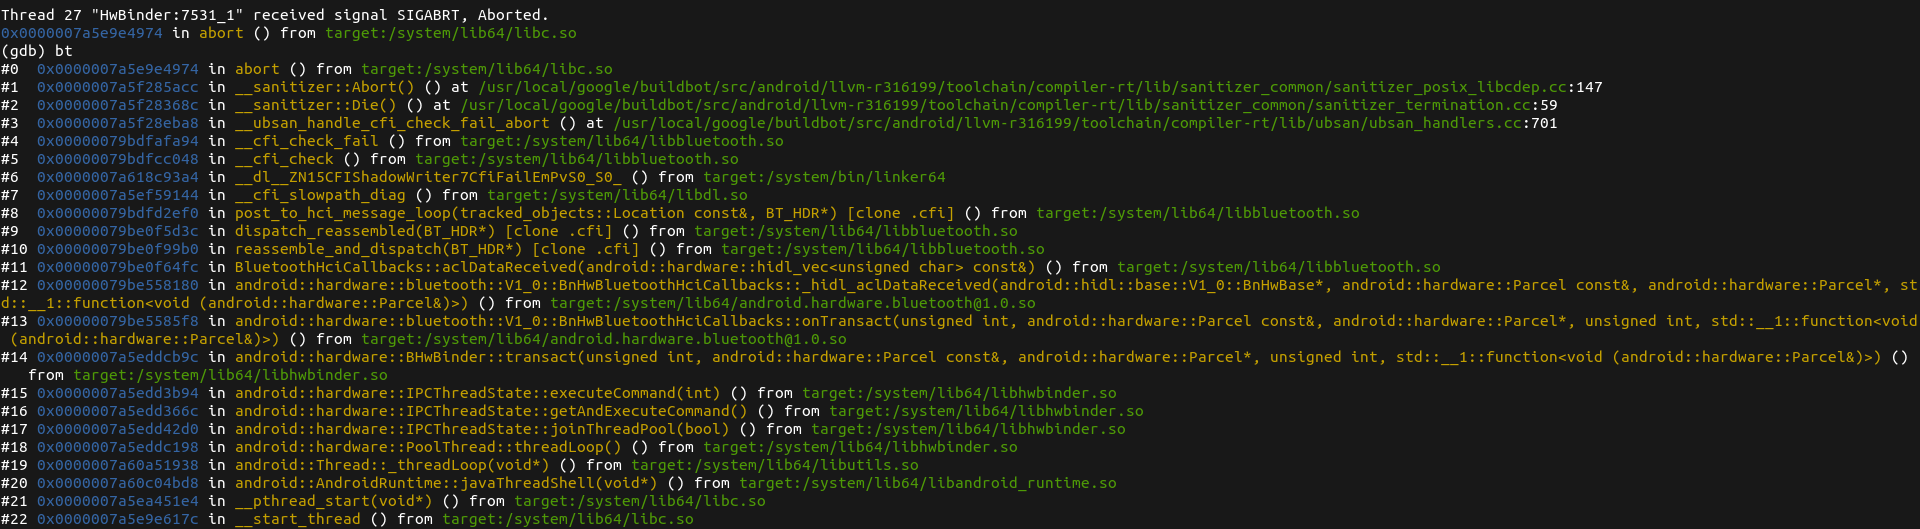 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
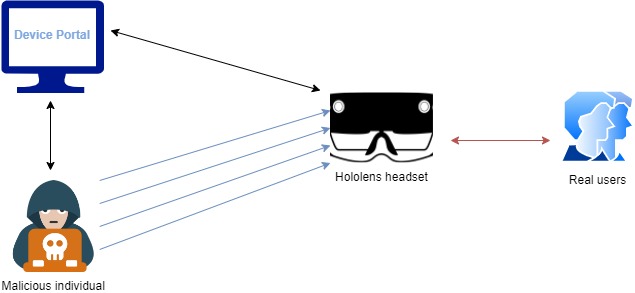 tania-silva/cve-2024-57972
Denial of Service exploit for Microsoft HoloLens Device Portal via repeated API pairing requests, causing CPU overload and system unresponsiveness.