

radio-hackbox
 syss-research/radio-hackbox
PoC tool to demonstrate vulnerabilities in wireless input devices
exploitationhardware-iot-securitywireless-security
syss-research/radio-hackboxPoC tool to demonstrate vulnerabilities in wireless input devices
 praetorian-inc/caeruleus
Single Go binary for Bluetooth Low Energy security testing on Linux/BlueZ: scan, enumerate GATT, read/write/notify, fuzz characteristics, and run…
 elevenpaths/devicepairedtool
Tool for testing and auditing Bluetooth device pairing security, identifying vulnerabilities in wireless pairing protocols and hardware IoT…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 nccgroup/blesuite
BLESuite is a Python package that provides an easier way to test Bluetooth Low Energy (BLE) device
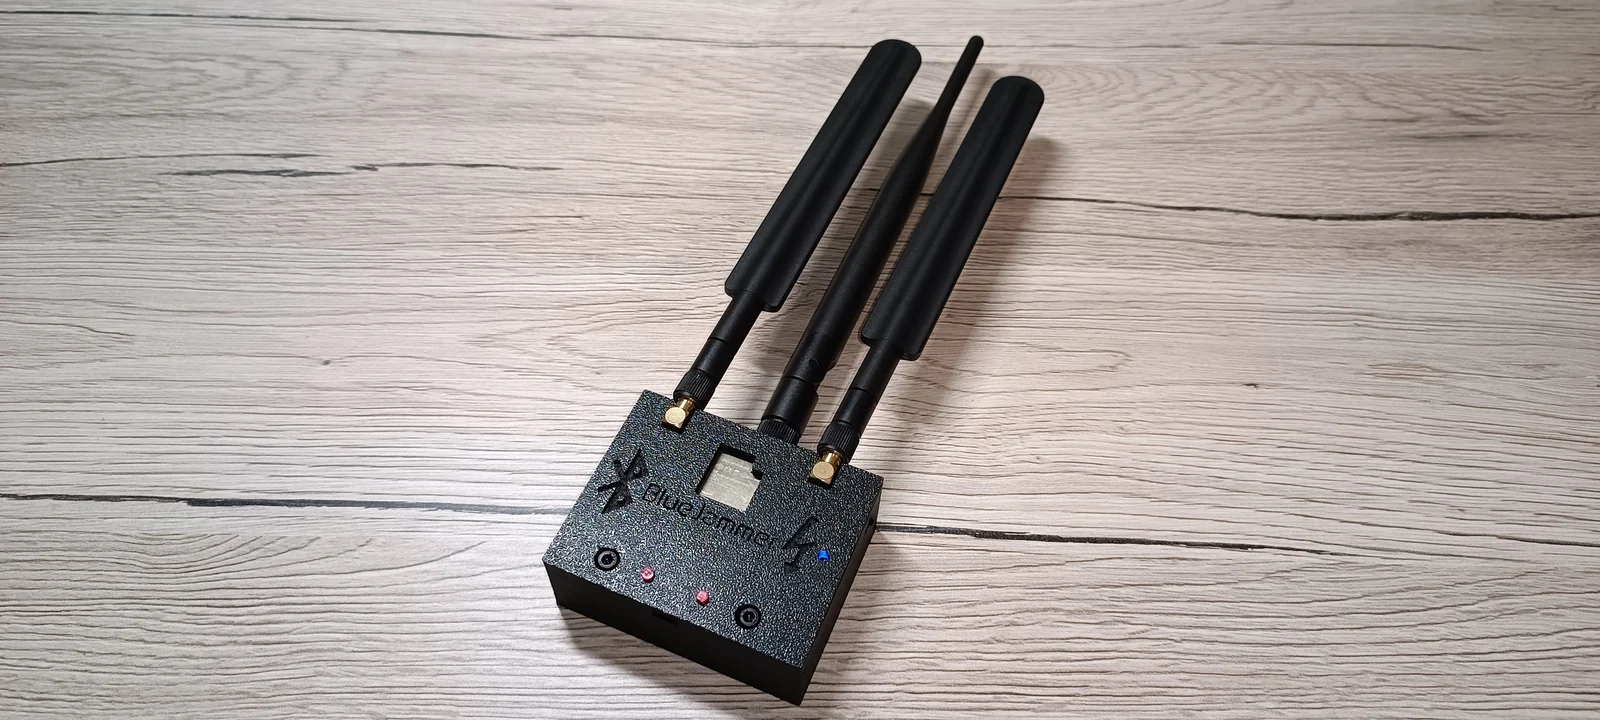 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 marcnewlin/hi_my_name_is_keyboard
Bluetooth keystroke injection exploit PoCs for CVE-2023-45866, CVE-2024-21306, and CVE-2024-0230 targeting Android, Linux, macOS, and iOS via…
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 jopohl/urh
Universal Radio Hacker: Investigate Wireless Protocols Like A Boss
 v3ilsm1th/cve-2023-45866_wip
Simulates a Bluetooth keyboard to exploit CVE-2023-45866, injecting keystrokes via DuckyScript on vulnerable Android, iOS, macOS, and Linux devices…
 telefonica/homepwn
HomePwn - Swiss Army Knife for Pentesting of IoT Devices
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
 ap425q/whisper-pair
Scans Bluetooth Low Energy devices for Fast Pair vulnerabilities (CVE-2025-36911), testing if accessories accept unencrypted Key-Based Pairing…
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)