
CVE-2025-45512
 azhariramadhan/cve-2025-45512
Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
embedded-systems-securityexploitationfirmware-analysis+5
2
azhariramadhan/cve-2025-45512Proof-of-concept exploit suite for U-Boot bootloader vulnerabilities, including insecure update mechanisms, hardcoded credentials, debugging…
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 sigrokproject/libsigrok
C library providing a portable API for acquiring signals from logic analyzers, oscilloscopes, multimeters, and other test instruments, with…
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 l0lsec/tapo-c260-rce
PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.
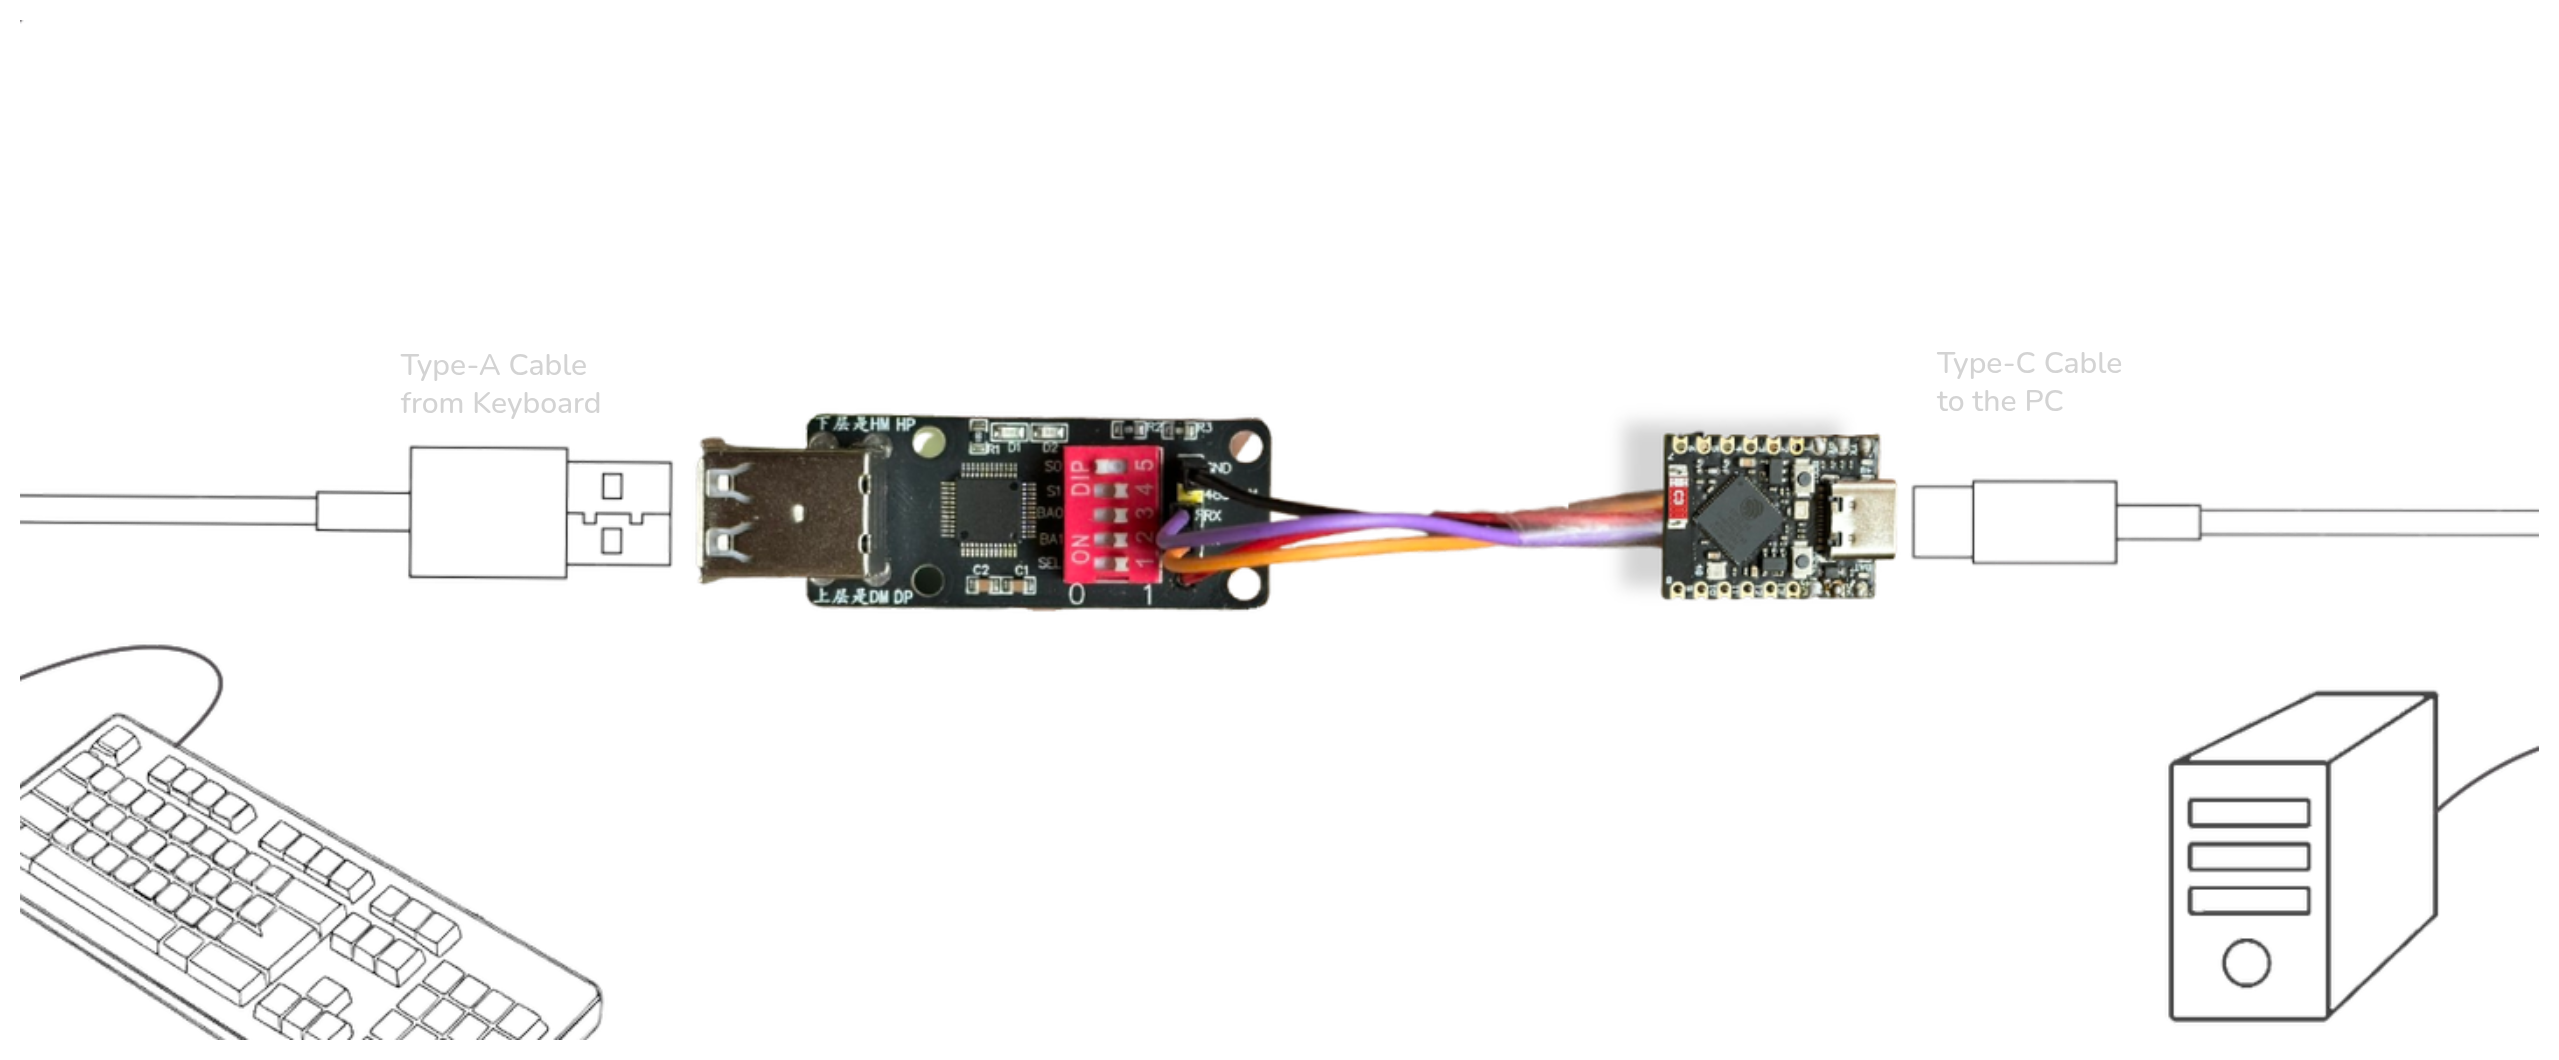 itsmmdoha/ducklogger
A ESP32-S3–based usb keylogger with wifi, easy DIY-able with widely available hardware.
 darkflippers/unleashed-firmware
Custom firmware for Flipper Zero enabling Sub-GHz radio, NFC/RFID emulation, infrared, and BadUSB attack features for hardware security testing.
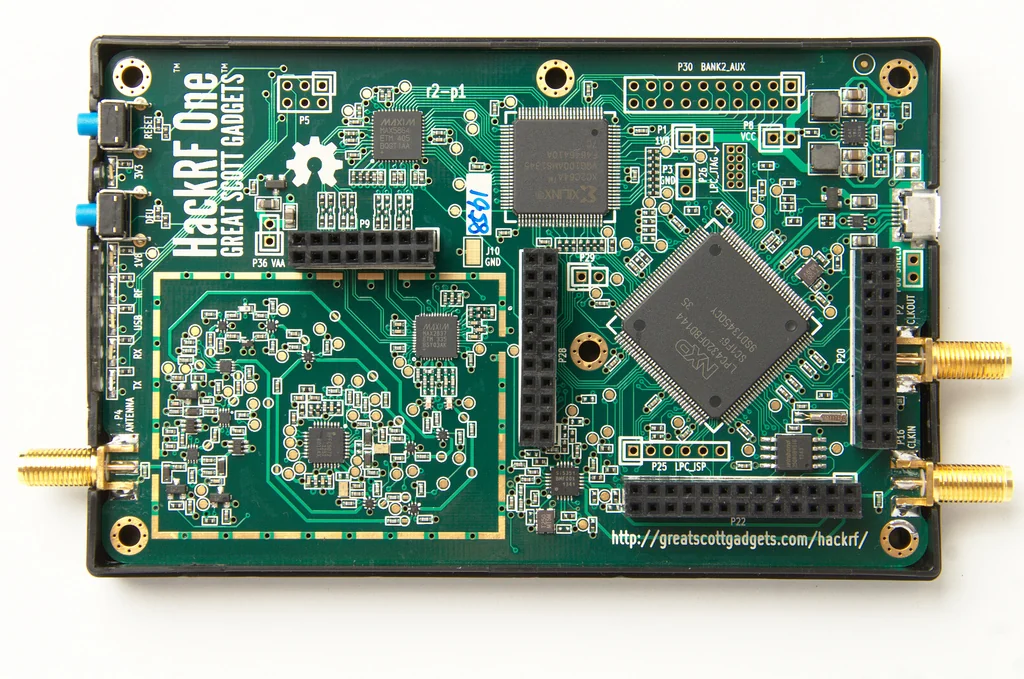 greatscottgadgets/hackrf
Low-cost open-source software-defined radio platform with hardware designs and firmware for RF transmission, reception, and signal analysis from 1…
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
 mister-devel/main_mister
FPGA-based hardware emulation platform main binary and documentation for retro system development, firmware compilation, and hardware security…
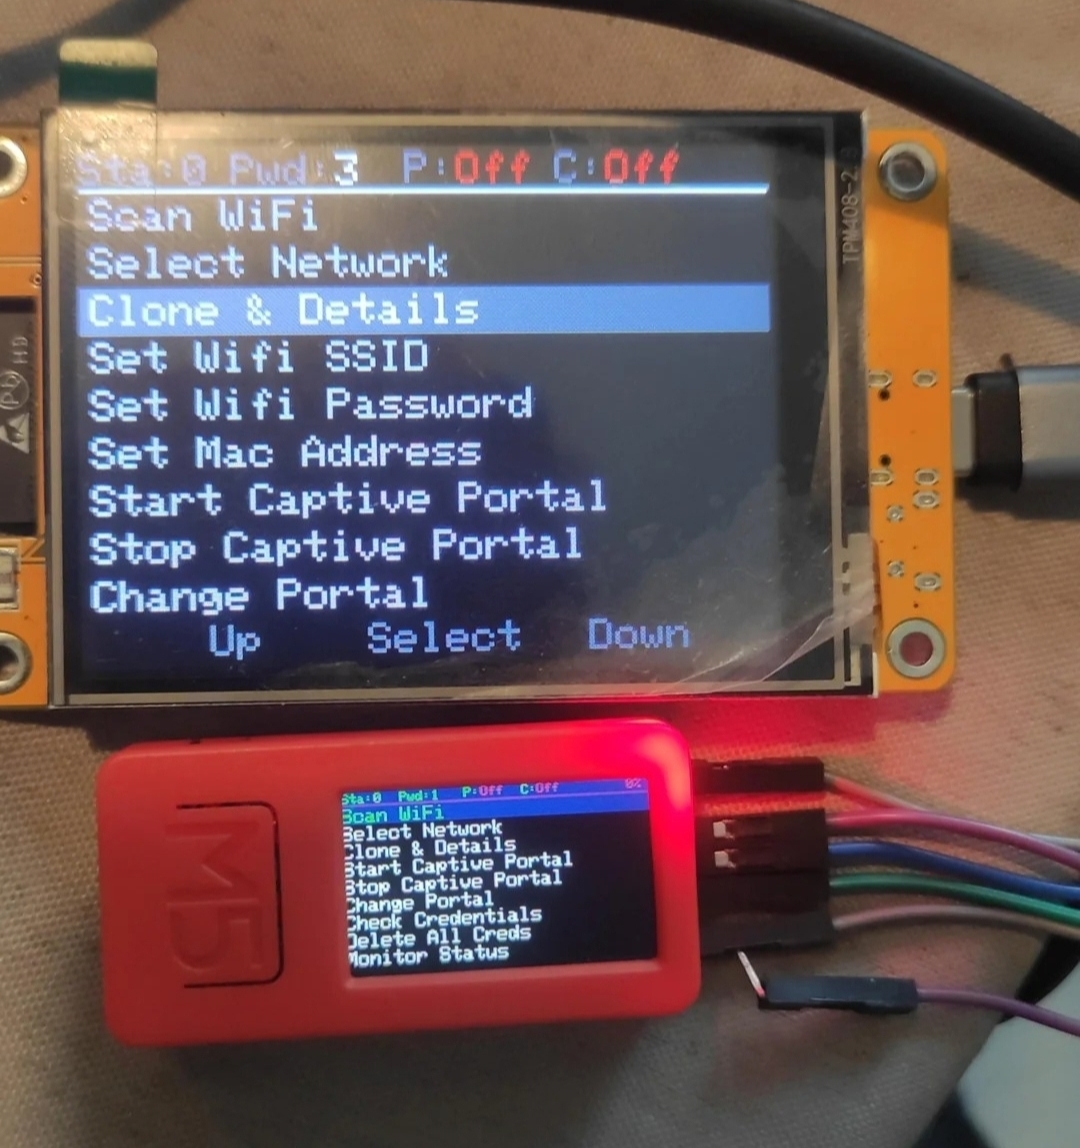 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
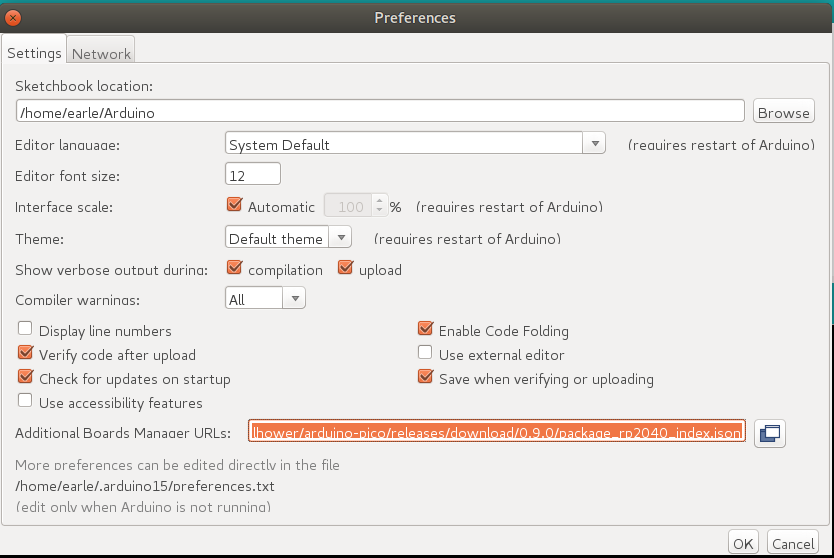 earlephilhower/arduino-pico
Raspberry Pi Pico Arduino core, for all RP2040 and RP2350 boards
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 newaetech/chipwhisperer
Open-source hardware security toolchain for power trace capture, side-channel analysis, and glitching/fault-injection attacks on embedded devices and…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.