

bad_ducky
 mharjac/bad_ducky
Rubber Ducky compatible clone based on CJMCU BadUSB HW.
hardware-hackingids-ips-evasionimpersonation-tools+5
mharjac/bad_duckyRubber Ducky compatible clone based on CJMCU BadUSB HW.
 iotsrg/iot-pentest-devices-and-purpose
Curated guide to IoT penetration testing hardware and software tools for 2025, covering Bluetooth, Zigbee, Z-Wave, WiFi, RFID, automotive, and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
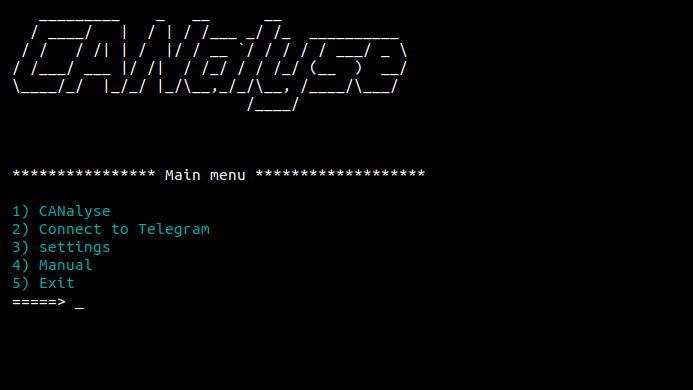 kartheeklade/canalyse
A vehicle network analysis and attack tool.
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 idoka/awesome-canbus
:articulated_lorry: Awesome CAN bus tools, hardware and resources for Cyber Security Researchers, Reverse Engineers, and Automotive Electronics…
 gmh5225/memtools
Windows Linux DMA、Dump 、Direct、inject 内存读取、写入工具
 sacriphanius/zhilly
🛡️ AI-powered portable cybersecurity & pentesting assistant built on ESP32-S3 (LilyGO T-Embed CC1101 & T-Watch S3). Features voice-controlled RF…
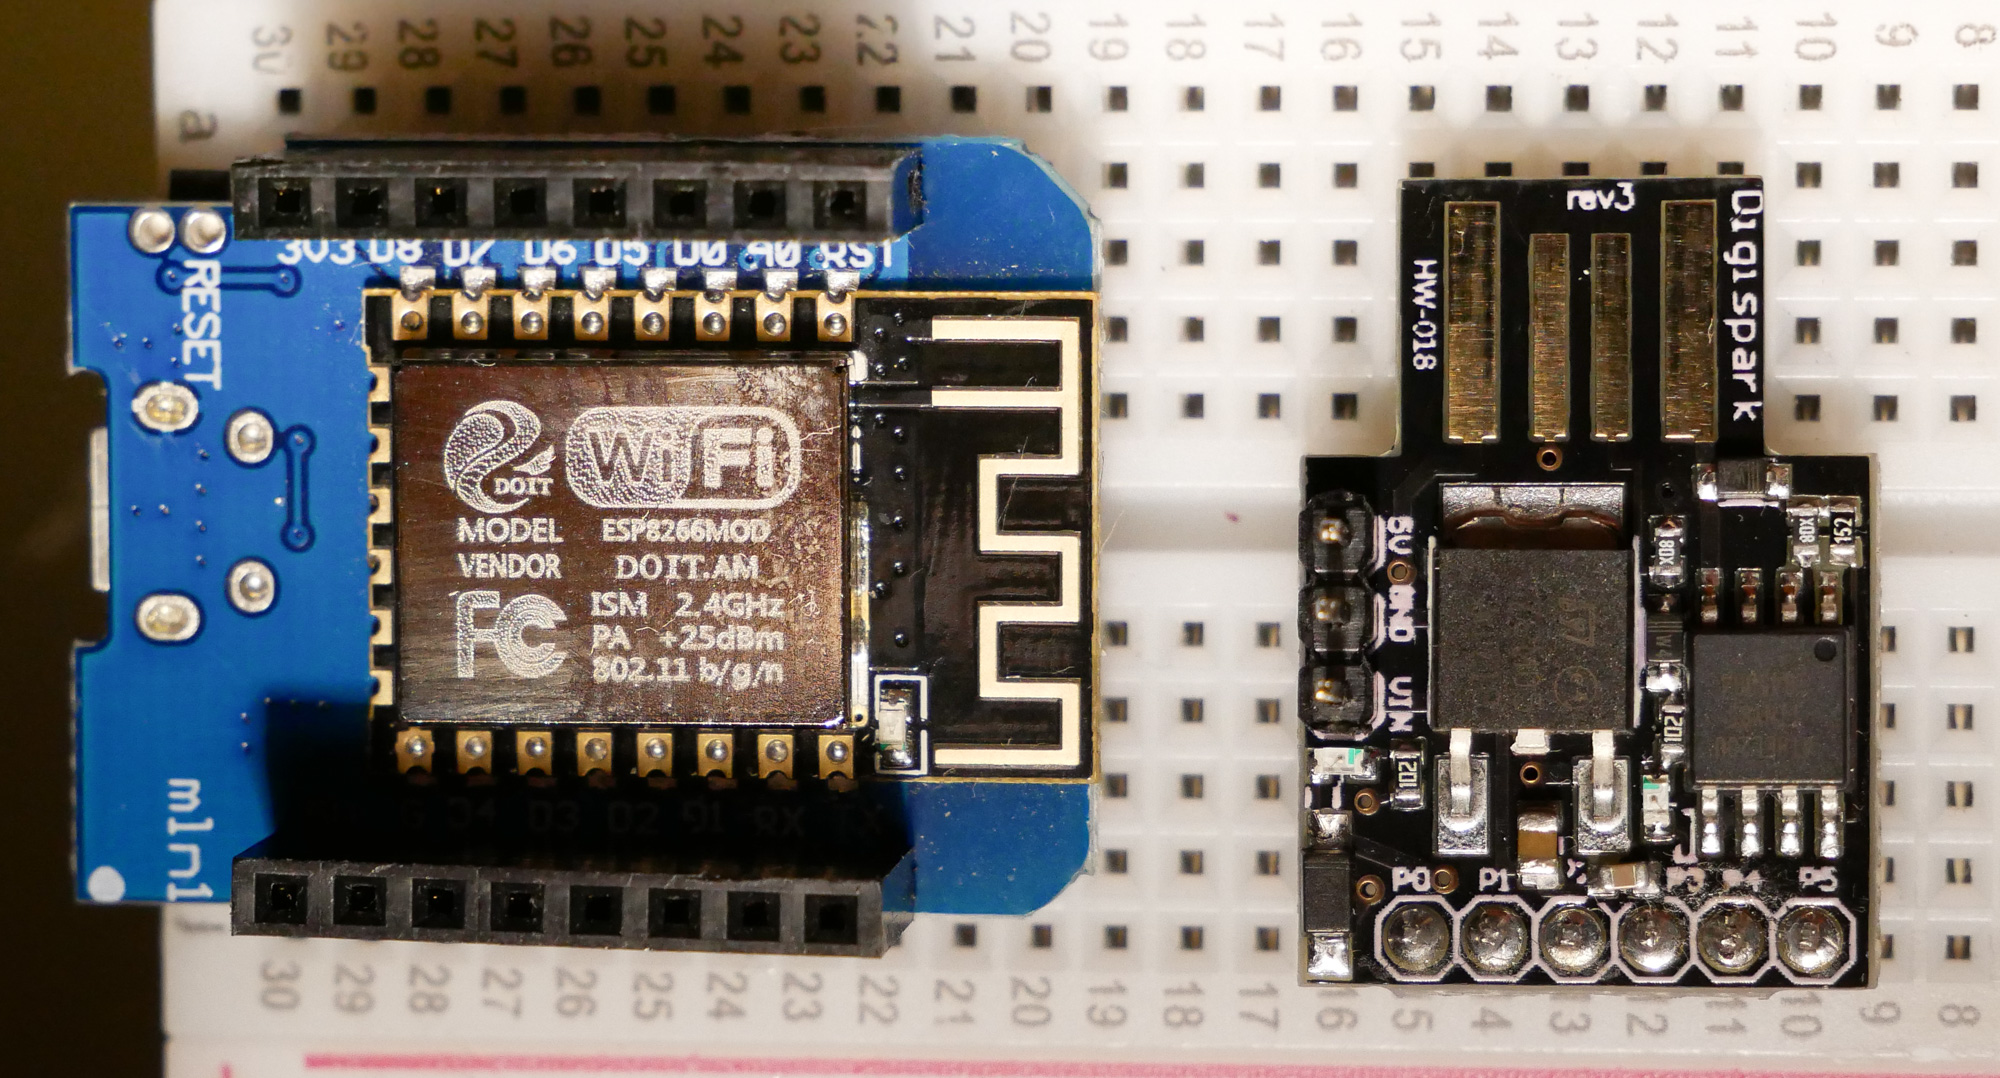 skickar/digitrack
Attacks for $5 or less using Arduino
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 rfidresearchgroup/proxmark3
Hardware tool for RFID analysis, emulation, and penetration testing. Supports 125kHz, 13.56MHz protocols (MIFARE, iClass, ISO14443/15693) with key…
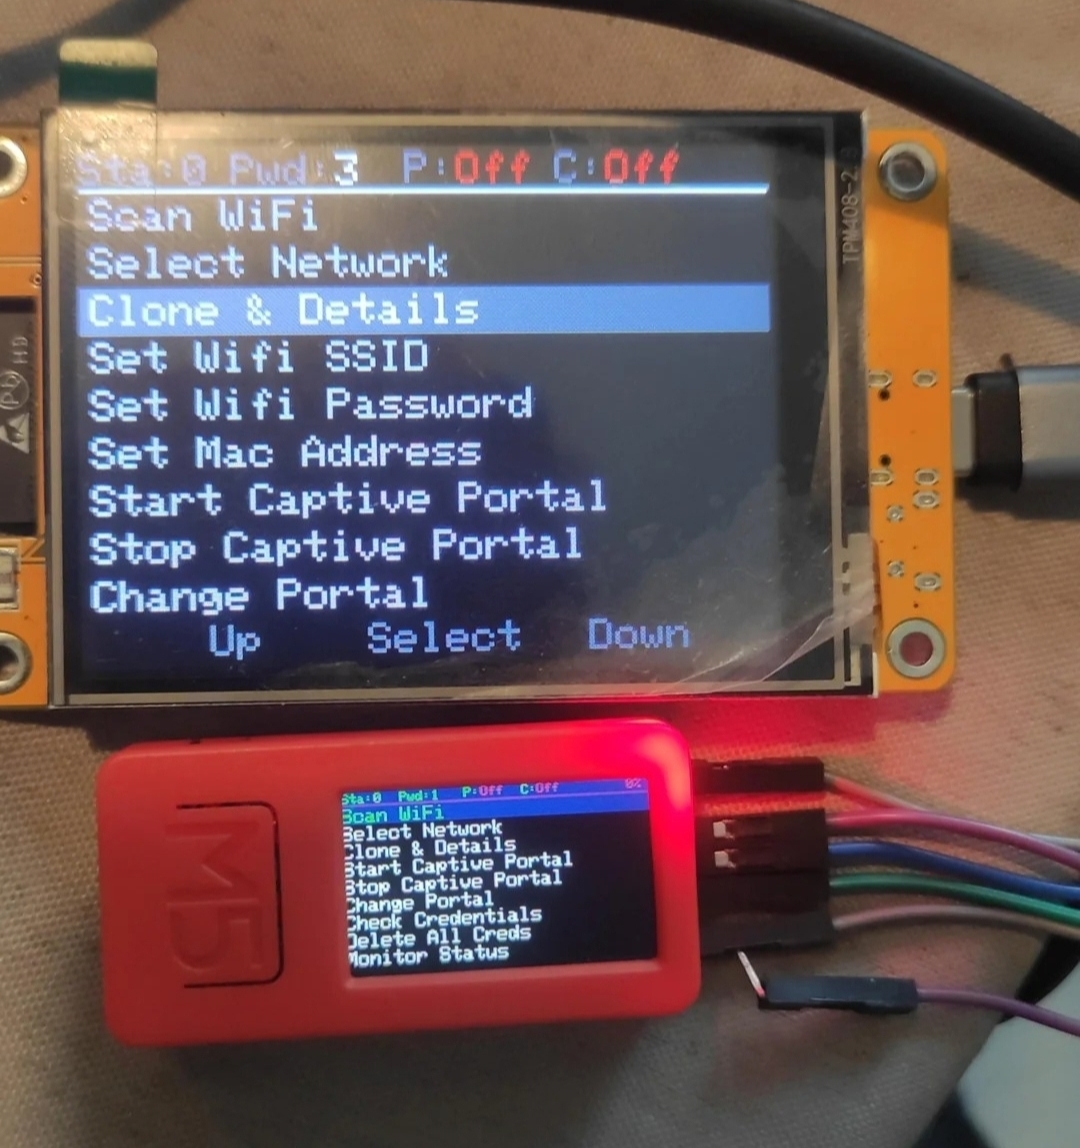 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
 emenstanougat/esp32-bluejammer
ESP32 and nRF24 based 2.4GHz jammer that disrupts Bluetooth, BLE, WiFi, and RC channels via noise and packet flooding for controlled security testing.
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.