

Flipper
 uberguidoz/flipper
Playground (and dump) of stuff I make or modify for the Flipper Zero
curated-resourceseducationembedded-systems-security+3
17.3k3 months ago
uberguidoz/flipperPlayground (and dump) of stuff I make or modify for the Flipper Zero
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 justcallmekoko/esp32marauder
A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32
 rfidresearchgroup/chameleonultra
The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…
 e-m-b-a/emba
EMBA - The firmware security analyzer
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 seemoo-lab/nexmon
The C-based Firmware Patching Framework for Broadcom/Cypress WiFi Chips that enables Monitor Mode, Frame Injection and much more
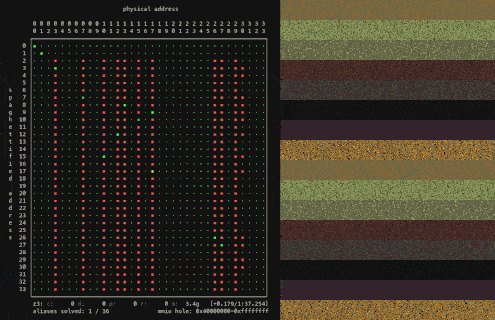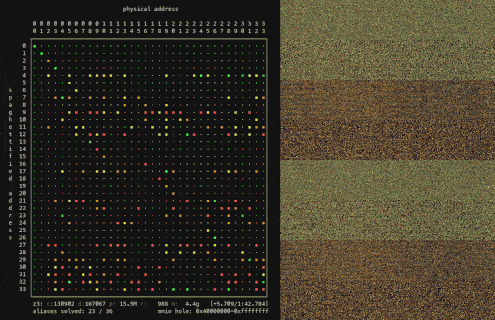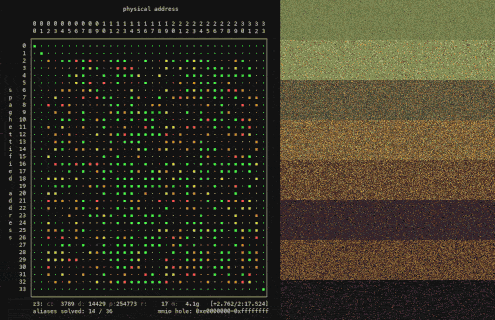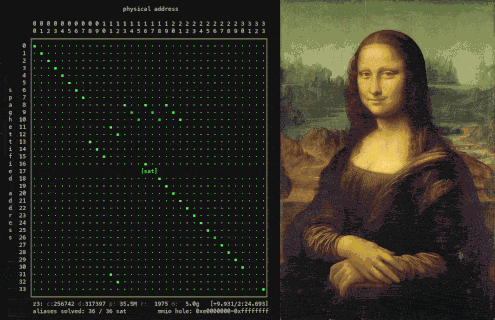 xoreaxeaxeax/skitter-creek-bath-salts
Unlocking _everything_ on the CPU with DRAM scrambling
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 emsec/chameleonmini
The ChameleonMini is a versatile contactless smartcard emulator compliant to NFC. The ChameleonMini was developed by https://kasper-oswald.de. The…
 samyk/keysweeper
KeySweeper is a stealthy Arduino-based device, camouflaged as a functioning USB wall charger, that wirelessly and passively sniffs, decrypts, logs…
 iceman1001/chameleonmini-rebooted
Chameleon Mini revE rebooted - Iceman Fork, the ChameleonMini is a versatile contactless smartcard emulator (NFC/RFID)
 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 davidprobinsky/redteam-physical-tools
Red Team Toolkit - A curated list of tools that are commonly used in the field for Physical Security, Red Teaming, and Tactical Covert Entry.
 pepsipu/ns2jb
Console jailbreak demo that executes native functions inside the Switch 2 filesystem process via SmileBASIC, verifies results, and restores original…
 owasp/owasp-istg
The IoT Security Testing Guide (ISTG) provides a comprehensive methodology for penetration tests in the IoT field, offering flexibility to adapt…
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)